

Safeguard on social
Every post we have published on our social profiles, newest first, with the copy exactly as posted. Each card links to the original post.
Latest posts
RSS feed Facebook
Two separate exposures at Amadeus, the airline booking technology provider, surfaced in October 2026. Korean Air and Asiana say booking data leaked through misuse of a login for an Amadeus system account. Separately, heise online found passenger records behind an unauthenticated…
Read the full postHide the full post
Two separate exposures at Amadeus, the airline booking technology provider, surfaced in October 2026. Korean Air and Asiana say booking data leaked through misuse of a login for an Amadeus system account. Separately, heise online found passenger records behind an unauthenticated Spring Boot heap dump, including Lufthansa and Condor flights; Amadeus says it is fixed. No source links the two. If you buy from a booking or SaaS vendor, ask which of their system accounts can read your data, how credentials rotate, and how many hours until they tell you after unauthorized access. https://na2.hubs.ly/H08CDSQ0
- LinkedIn
Two separate exposures at Amadeus, the airline booking technology provider, surfaced in October 2026. Korean Air and Asiana say booking data leaked through unauthorized use of login credentials assigned to an Amadeus system account, in an estimated window from August 2023 to Sep…
Read the full postHide the full post
Two separate exposures at Amadeus, the airline booking technology provider, surfaced in October 2026. Korean Air and Asiana say booking data leaked through unauthorized use of login credentials assigned to an Amadeus system account, in an estimated window from August 2023 to September 2026. Separately, heise online found a Spring Boot heap dump reachable without authentication, holding credentials and tokens, with passenger records searchable by last name, many on Lufthansa and Condor flights. Amadeus told heise it learned of that on 21 September and that it is fixed. No source links the two events. No affected counts are published. Neither has a CVE. Both are vendor-side identity and configuration failures that customers learn about from the vendor. Five questions to put to any booking, payroll or SaaS vendor this week: 1. Which of your system accounts can read our data, and how are their credentials issued and rotated? 2. Do non-production environments hold our real data? 3. How many days of access logs do you keep for our data? 4. After you confirm unauthorized access, how many hours until you tell us? 5. Which services expose management or debugging endpoints, and how are they restricted? On your own side, list every service that includes Spring Boot Actuator and check what it exposes. Safeguard's dependency and image scanning gives you that list across repositories and container images. Full read, with the checks: https://lnkd.in/g7pGW3hR Sources: Korean Air and Asiana statements as reported by Korean outlets on 23 Oct 2026; heise online, 13 Oct 2026. As read on 26 Oct 2026. #VendorRisk #ThirdPartyRisk #AppSec
- X
Amadeus, Oct 2026: Korean Air and Asiana cite misuse of an Amadeus system account login; heise found an unauthenticated Spring Boot heap dump. No source links them. Ask your vendors which system accounts reach your data and how credentials rotate. https://t.co/SNKF0W3NP8 https:/…
Read the full postHide the full post
Amadeus, Oct 2026: Korean Air and Asiana cite misuse of an Amadeus system account login; heise found an unauthenticated Spring Boot heap dump. No source links them. Ask your vendors which system accounts reach your data and how credentials rotate. https://t.co/SNKF0W3NP8 https://t.co/PTQljXSY9A
 LinkedInVideo
The Fix Window, Ep 5 is live: Three days: how fast to patch a bug that is already being used. CISA's BOD 26-04 replaced one patch deadline with four facts. Is the asset exposed to the internet? Is the flaw on the KEV catalog? Can an attacker automate the exploit? Does it give pa…
Read the full postHide the full post
The Fix Window, Ep 5 is live: Three days: how fast to patch a bug that is already being used. CISA's BOD 26-04 replaced one patch deadline with four facts. Is the asset exposed to the internet? Is the flaw on the KEV catalog? Can an attacker automate the exploit? Does it give partial or total control? Mira, Cal and Theo walk through forensic triage, a fast lane for exploited flaws on exposed assets, a CI gate on known exploited CVEs, and what to say to a customer who asks about your patch SLA. It ends with six things to do this week. Mira, Cal and Theo are AI voices. The script is written by the Safeguard team and checked against our published research. Listen: https://lnkd.in/gsz3zvsJ #SecurityPodcast #AppSec #VulnerabilityManagement
- InstagramVideo
The Fix Window, Ep 5 is live: Three days: how fast to patch a bug that is already being used. Four facts from CISA's BOD 26-04 decide the clock: exposed or not, on the KEV catalog or not, automatable or not, partial or total control. Then a fast lane, a CI gate on known exploite…
Read the full postHide the full post
The Fix Window, Ep 5 is live: Three days: how fast to patch a bug that is already being used. Four facts from CISA's BOD 26-04 decide the clock: exposed or not, on the KEV catalog or not, automatable or not, partial or total control. Then a fast lane, a CI gate on known exploited CVEs, and six things to do this week. Mira, Cal and Theo are AI voices. The script is written by the Safeguard team. Link in bio: http://safeguard.sh/podcast #securitypodcast #appsec #vulnerabilitymanagement #devsecops
- XVideo
The Fix Window, Ep 5 is live: how fast to patch a bug that is already being used. Four facts from CISA's BOD 26-04, and six things to do this week. AI voices. https://t.co/l6T3vu3hVs https://t.co/fl2vzPurB3
- FacebookVideo
The Fix Window, Ep 5 is live: Three days: how fast to patch a bug that is already being used. How CISA's BOD 26-04 turned one patch deadline into four facts, and how a private team can borrow the idea: a fast lane for exploited flaws on exposed assets, a CI gate on known exploit…
Read the full postHide the full post
The Fix Window, Ep 5 is live: Three days: how fast to patch a bug that is already being used. How CISA's BOD 26-04 turned one patch deadline into four facts, and how a private team can borrow the idea: a fast lane for exploited flaws on exposed assets, a CI gate on known exploited CVEs, and honest risk acceptance. Mira, Cal and Theo are AI voices; the script is written by the Safeguard team. Listen: https://na2.hubs.ly/H08Jbb_0
 YouTubeVideo
A message lands on a Monday: a flaw in something you run has just been added to the known exploited list. You used to have three weeks. Now you may have three days. Mira and Cal explain how CISA's BOD 26-04, issued in June 2026, replaced one patch deadline with four facts: is th…
Read the full postHide the full post
A message lands on a Monday: a flaw in something you run has just been added to the known exploited list. You used to have three weeks. Now you may have three days. Mira and Cal explain how CISA's BOD 26-04, issued in June 2026, replaced one patch deadline with four facts: is the asset exposed to the internet, is the flaw on the KEV catalog, can an attacker automate the exploit, and does it give partial or total control. They cover what forensic triage means, the permission to wait at the bottom of the table, and how a private team can borrow the idea for vulnerability prioritisation: a fast lane for exploited flaws on exposed assets, a CI gate on known exploited CVEs, and honest risk acceptance. It is a practical episode on vulnerability management and patch management for AppSec and DevSecOps teams: how CVSS, EPSS and KEV fit together, why reachability and a software inventory (an SBOM) decide how fast you can do remediation, and what to say to a federal customer who asks about your patch SLA. In the news, in October: two exploited flaws added to the KEV catalog on 27 October, PolyShell in Adobe Commerce and Magento and a Brotli decoder flaw bundled in Node.js, and why their federal due date was fourteen days when two PHP flaws added the day before got three days plus a compromise check. Theo explains why to keep your old deadlines as a baseline, and the episode ends with six things to do this week. Topics: BOD 26-04, CISA KEV, forensic triage, CVSS, EPSS, CVE, exploit, Node.js, Brotli, Adobe Commerce, Magento, PolyShell, PHP, vulnerability prioritisation, CI gate, software supply chain security, open source security Chapters • 00:00 Cold open • 00:36 Intro • 01:00 News: two exploited flaws, two due dates • 03:41 What changed: the day the 21 day clock went away • 06:03 Deep dive: four facts, a fast lane and a floor • 09:32 Practitioner corner (Theo) • 10:23 Fix it this week • 11:35 Outro Links • Safeguard (https://safeguard.sh/?utm_source=podcast&utm_medium=audio&utm_campaign=the-fix-window&utm_content=ep05) • BOD 26-04: the deadlines and forensic triage, explained (https://safeguard.sh/resources/blog/cisa-bod-26-04-kev-remediation-timelines-forensic-triage?utm_source=podcast&utm_medium=audio&utm_campaign=the-fix-window&utm_content=ep05) • Should a CI gate block on known exploited vulnerabilities? (https://safeguard.sh/resources/blog/should-a-ci-gate-block-on-known-exploited-vulnerabilities?utm_source=podcast&utm_medium=audio&utm_campaign=the-fix-window&utm_content=ep05) • Can you accept risk on a known exploited vulnerability? (https://safeguard.sh/resources/blog/can-you-accept-risk-on-a-known-exploited-vulnerability?utm_source=podcast&utm_medium=audio&utm_campaign=the-fix-window&utm_content=ep05) • Free scan (Gold Open Source, no login) (https://gold.safeguard.sh/scan?utm_source=podcast&utm_medium=audio&utm_campaign=the-fix-window&utm_content=ep05) Full dated source list: see the show notes.
 YouTubeVideo
A message lands on a Monday: a flaw in something you run has just been added to the known exploited list. You used to have three weeks. Now you may have three days. Mira and Cal explain how CISA's BOD 26-04, issued in June 2026, replaced one patch deadline with four facts: is th…
Read the full postHide the full post
A message lands on a Monday: a flaw in something you run has just been added to the known exploited list. You used to have three weeks. Now you may have three days. Mira and Cal explain how CISA's BOD 26-04, issued in June 2026, replaced one patch deadline with four facts: is the asset exposed to the internet, is the flaw on the KEV catalog, can an attacker automate the exploit, and does it give partial or total control. They cover what forensic triage means, the permission to wait at the bottom of the table, and how a private team can borrow the idea for vulnerability prioritisation: a fast lane for exploited flaws on exposed assets, a CI gate on known exploited CVEs, and honest risk acceptance. It is a practical episode on vulnerability management and patch management for AppSec and DevSecOps teams: how CVSS, EPSS and KEV fit together, why reachability and a software inventory (an SBOM) decide how fast you can do remediation, and what to say to a federal customer who asks about your patch SLA. In the news, in October: two exploited flaws added to the KEV catalog on 27 October, PolyShell in Adobe Commerce and Magento and a Brotli decoder flaw bundled in Node.js, and why their federal due date was fourteen days when two PHP flaws added the day before got three days plus a compromise check. Theo explains why to keep your old deadlines as a baseline, and the episode ends with six things to do this week. Topics: BOD 26-04, CISA KEV, forensic triage, CVSS, EPSS, CVE, exploit, Node.js, Brotli, Adobe Commerce, Magento, PolyShell, PHP, vulnerability prioritisation, CI gate, software supply chain security, open source security Chapters: 00:00 Cold open 00:36 Intro 01:00 News: two exploited flaws, two due dates 03:41 What changed: the day the 21 day clock went away 06:03 Deep dive: four facts, a fast lane and a floor 09:32 Practitioner corner (Theo) 10:23 Fix it this week 11:35 Outro Links: Safeguard: https://safeguard.sh/?utm_source=podcast&utm_medium=video&utm_campaign=the-fix-window&utm_content=ep05 BOD 26-04: the deadlines and forensic triage, explained: https://safeguard.sh/resources/blog/cisa-bod-26-04-kev-remediation-timelines-forensic-triage?utm_source=podcast&utm_medium=video&utm_campaign=the-fix-window&utm_content=ep05 Should a CI gate block on known exploited vulnerabilities?: https://safeguard.sh/resources/blog/should-a-ci-gate-block-on-known-exploited-vulnerabilities?utm_source=podcast&utm_medium=video&utm_campaign=the-fix-window&utm_content=ep05 Can you accept risk on a known exploited vulnerability?: https://safeguard.sh/resources/blog/can-you-accept-risk-on-a-known-exploited-vulnerability?utm_source=podcast&utm_medium=video&utm_campaign=the-fix-window&utm_content=ep05 Free scan (Gold Open Source, no login): https://gold.safeguard.sh/scan?utm_source=podcast&utm_medium=video&utm_campaign=the-fix-window&utm_content=ep05 More episodes: https://safeguard.sh/podcast?utm_source=podcast&utm_medium=video&utm_campaign=the-fix-window&utm_content=ep05 Listen on Spotify: https://open.spotify.com/show/03400iIvo19RZbfRDfPECc?utm_source=podcast&utm_medium=video&utm_campaign=the-fix-window&utm_content=ep05
 LinkedInVideo
One mistyped package name should not be able to reach your build. Typosquatted packages bet on a tired finger. Dependency confusion bets that your installer picks the wrong source. Either way, the bad package is already in your tree before anyone looks. Safeguard's Package Firew…
Read the full postHide the full post
One mistyped package name should not be able to reach your build. Typosquatted packages bet on a tired finger. Dependency confusion bets that your installer picks the wrong source. Either way, the bad package is already in your tree before anyone looks. Safeguard's Package Firewall moves that check to install time. It runs as a proxy between your developers, your CI and the public registries for npm and pip, so every fetch is evaluated before the package reaches a laptop or a build, transitive dependencies included. It blocks malicious, typosquatted and dependency confusion packages at install time. In the video you can see the real CLI answer for a misspelled "requests": flagged as a typosquat, one edit away, and held. Rollout that works: an admin turns it on, you start the proxy locally or in CI with the Safeguard CLI, run audit mode first to see what it would stop, then move to warn and block one rule at a time with an exception path that has an owner and an expiry. Full walkthrough, with the policy table and the CLI commands: https://lnkd.in/g_NjpNtf #SupplyChainSecurity #AppSec #DevSecOps
 InstagramVideo
One mistyped package name, stopped before it lands. Safeguard's Package Firewall sits between your developers, your CI and the public registries for npm and pip, and blocks malicious, typosquatted and dependency confusion packages at install time. Start in audit mode, then enfor…
Read the full postHide the full post
One mistyped package name, stopped before it lands. Safeguard's Package Firewall sits between your developers, your CI and the public registries for npm and pip, and blocks malicious, typosquatted and dependency confusion packages at install time. Start in audit mode, then enforce. Walkthrough and CLI commands: link in bio (http://safeguard.sh/resources/blog) #SupplyChainSecurity #AppSec #DevSecOps #npm #pip
- FacebookVideo
One mistyped package name, stopped before it lands. Safeguard's Package Firewall sits between your developers, your CI and the public registries for npm and pip, and blocks malicious, typosquatted and dependency confusion packages at install time. Start in audit mode, then enfor…
Read the full postHide the full post
One mistyped package name, stopped before it lands. Safeguard's Package Firewall sits between your developers, your CI and the public registries for npm and pip, and blocks malicious, typosquatted and dependency confusion packages at install time. Start in audit mode, then enforce. Walkthrough and CLI commands: https://na2.hubs.ly/H08Cv4m0
 YouTubeVideo
Safeguard's Package Firewall is an install-time proxy for npm and pip. It sits between developers, CI and the public registries and blocks malicious, typosquatted and dependency confusion packages at install time. In the video: the real Safeguard CLI answer for a misspelled "req…
Read the full postHide the full post
Safeguard's Package Firewall is an install-time proxy for npm and pip. It sits between developers, CI and the public registries and blocks malicious, typosquatted and dependency confusion packages at install time. In the video: the real Safeguard CLI answer for a misspelled "requests". Walkthrough and CLI commands: https://na2.hubs.ly/H08Cv4p0 #SupplyChainSecurity #AppSec #Shorts
- XVideo
One mistyped package name, stopped before it lands. Safeguard's Package Firewall sits between devs, CI and the public registries for npm and pip and blocks malicious, typosquatted and dependency confusion packages at install time. https://t.co/aTgnUYr1eN https://t.co/PhTySVLHFR
- TikTokVideo
One mistyped package name, stopped before it lands. Package Firewall blocks malicious, typosquatted and dependency confusion packages at install time for npm and pip. Walkthrough: https://na2.hubs.ly/H08Cvl00 (link in bio) #supplychainsecurity #appsec #devsecops
 Instagram
Running Adobe Commerce or Magento Open Source? Patch CVE-2026-48356 (unrestricted file upload, CVSS 9.3) with Adobe's fix in APSB26-73. Then check pub/media/custom_options/ for files that are not real images, review admin users and rotate credentials if you find anything. Patchi…
Read the full postHide the full post
Running Adobe Commerce or Magento Open Source? Patch CVE-2026-48356 (unrestricted file upload, CVSS 9.3) with Adobe's fix in APSB26-73. Then check pub/media/custom_options/ for files that are not real images, review admin users and rotate credentials if you find anything. Patching does not remove what an attacker already left behind. Safeguard inventories each store from its lock file and puts KEV listed findings first. Link in bio: safeguard.sh/resources/blog/adobe-commerce-magento-cve-2026-48356-kev-unrestricted-file-upload-what-to-patch-and-check
 InstagramVideo
Don't let your security program depend on one model vendor. Whether your team standardised on Anthropic's Claude or OpenAI's ChatGPT, the risk is any single provider. In Safeguard you pick the model per task: one OpenAI-compatible endpoint, change the id, not the integration. Br…
Read the full postHide the full post
Don't let your security program depend on one model vendor. Whether your team standardised on Anthropic's Claude or OpenAI's ChatGPT, the risk is any single provider. In Safeguard you pick the model per task: one OpenAI-compatible endpoint, change the id, not the integration. Bring your own model for Safeguard's AI features, or run Zero AI. Your model, your call (1/3). Link in bio: http://safeguard.sh/models/compare Claude is a product of Anthropic. ChatGPT is a product of OpenAI. #appsec #aisecurity #supplychainsecurity #devsecops
 LinkedInVideo
Whether your team standardised on Anthropic's Claude or OpenAI's ChatGPT, the risk is the same: one provider, one dependency. In Safeguard you pick the model per task, and switching does not mean re-platforming. - One OpenAI-compatible endpoint. Model ids look like provider/mode…
Read the full postHide the full post
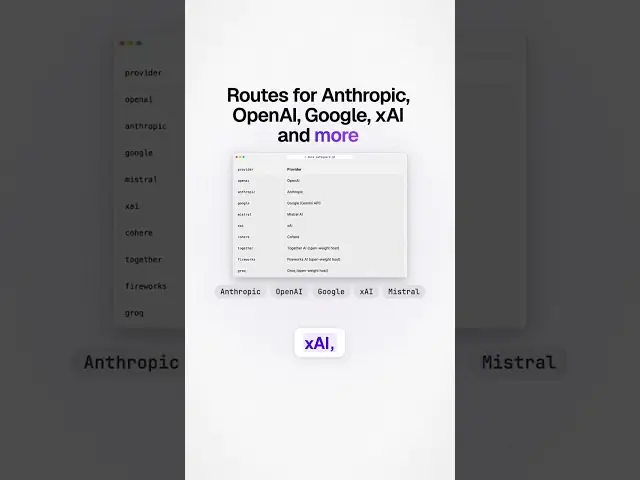
Whether your team standardised on Anthropic's Claude or OpenAI's ChatGPT, the risk is the same: one provider, one dependency. In Safeguard you pick the model per task, and switching does not mean re-platforming. - One OpenAI-compatible endpoint. Model ids look like provider/model, so you change the id, not the integration. - Provider routes for Anthropic, OpenAI, Google, xAI, Mistral, Cohere and open-weight hosts. - The Workbench runs your own prompts through two or three candidates and shows tokens, cost, latency and time to first token for each run. - Bring your own model for Safeguard's AI features, such as search and chat, or run Zero AI: no LLM anywhere, every scanner still works. Use either, use both, or use your own. Your model, your call. Compare models: https://lnkd.in/ee4XCQmT Claude is a product of Anthropic. ChatGPT is a product of OpenAI. No endorsement implied. #AppSec #AISecurity #SupplyChainSecurity
 YouTubeVideo
Your model, your call (1/3). Whether your team standardised on Anthropic's Claude or OpenAI's ChatGPT, the risk is depending on any single provider. In Safeguard you pick the model per task through one OpenAI-compatible endpoint with provider/model ids, so you change the id, not…
Read the full postHide the full post
Your model, your call (1/3). Whether your team standardised on Anthropic's Claude or OpenAI's ChatGPT, the risk is depending on any single provider. In Safeguard you pick the model per task through one OpenAI-compatible endpoint with provider/model ids, so you change the id, not the integration. There are provider routes for Anthropic, OpenAI, Google, xAI, Mistral, Cohere and open-weight hosts. Compare candidates on your own prompts in the Workbench, bring your own model for Safeguard's AI features such as search and chat, or run Zero AI with no LLM anywhere. Footage: Mixkit stock (free license), read-only recordings of Safeguard docs and https://na2.hubs.ly/H08Fyr40, a terminal demo with a placeholder key. Compare models: https://na2.hubs.ly/H08Fyr50 Claude is a product of Anthropic. ChatGPT is a product of OpenAI. #AppSec #AISecurity #Shorts
- Facebook
Running Adobe Commerce or Magento Open Source? Apply the fix for CVE-2026-48356 (unrestricted file upload, CVSS 9.3) from Adobe bulletin APSB26-73, then check pub/media/custom_options/ for uploaded files, review admin users and rotate credentials if you find anything. Patching d…
Read the full postHide the full post
Running Adobe Commerce or Magento Open Source? Apply the fix for CVE-2026-48356 (unrestricted file upload, CVSS 9.3) from Adobe bulletin APSB26-73, then check pub/media/custom_options/ for uploaded files, review admin users and rotate credentials if you find anything. Patching does not remove what an attacker already left behind. Safeguard inventories each store from its lock file and puts KEV listed findings first. The full checklist: https://na2.hubs.ly/H08J3KV0
- XVideo
Whether your team standardised on Anthropic's Claude or OpenAI's ChatGPT, the risk is one provider (1/3). In Safeguard you pick the model per task: one OpenAI-compatible endpoint, change the id, not the integration. https://t.co/V4OX8DPS18 https://t.co/S7HrD6wMYc
- FacebookVideo
Whether your team standardised on Anthropic's Claude or OpenAI's ChatGPT, the risk is depending on any single provider. In Safeguard you pick the model per task: one OpenAI-compatible endpoint, provider/model ids, and you change the id, not the integration. Routes for Anthropic,…
Read the full postHide the full post
Whether your team standardised on Anthropic's Claude or OpenAI's ChatGPT, the risk is depending on any single provider. In Safeguard you pick the model per task: one OpenAI-compatible endpoint, provider/model ids, and you change the id, not the integration. Routes for Anthropic, OpenAI, Google, xAI, Mistral, Cohere and open-weight hosts. Bring your own model for Safeguard's AI features such as search and chat, or run Zero AI with no LLM anywhere. Your model, your call (1/3): https://na2.hubs.ly/H08FyrB0 Claude is a product of Anthropic. ChatGPT is a product of OpenAI.
- LinkedIn
Adobe Commerce and Magento Open Source: patch CVE-2026-48356, then check the store. It is an unrestricted file upload flaw (CWE-434), scored CVSS 3.1 9.3 Critical. Adobe's fix is in security bulletin APSB26-73. It affects Adobe Commerce, Adobe Commerce B2B, Magento Open Source a…
Read the full postHide the full post
Adobe Commerce and Magento Open Source: patch CVE-2026-48356, then check the store. It is an unrestricted file upload flaw (CWE-434), scored CVSS 3.1 9.3 Critical. Adobe's fix is in security bulletin APSB26-73. It affects Adobe Commerce, Adobe Commerce B2B, Magento Open Source and the Adobe Commerce Events module, so read the exact builds from the bulletin before you change anything. Then check, because patching does not remove what an attacker already left behind: - look in pub/media/custom_options/ for files that are not real images - search CMS blocks and pages for injected scripts - review admin users and integrations, and rotate credentials if you find anything - compare your web server config with Magento's http://nginx.conf.sample, which denies web access to /media/custom_options/ CISA added it to the KEV catalog on 27 October 2026 with a due date of 10 November 2026. How Safeguard helps: it inventories each store from its lock file, puts KEV listed findings first, and can gate the build on the fixed release. Full checklist: https://lnkd.in/eeD8PVR7
- X
Adobe Commerce/Magento CVE-2026-48356 (CVSS 9.3, file upload): apply Adobe's fix in APSB26-73, then check pub/media/custom_options/ for uploaded files and review admin users. Patching removes nothing already left behind. https://t.co/6WEAkn2pa0 https://t.co/I58Kd7CZpG
Follow Safeguard

Self-healing security runs on Safeguard.
Your first fix PR is minutes away.
No sales call required, even your agent can complete the purchase over MCP.