 Interactive
Platform
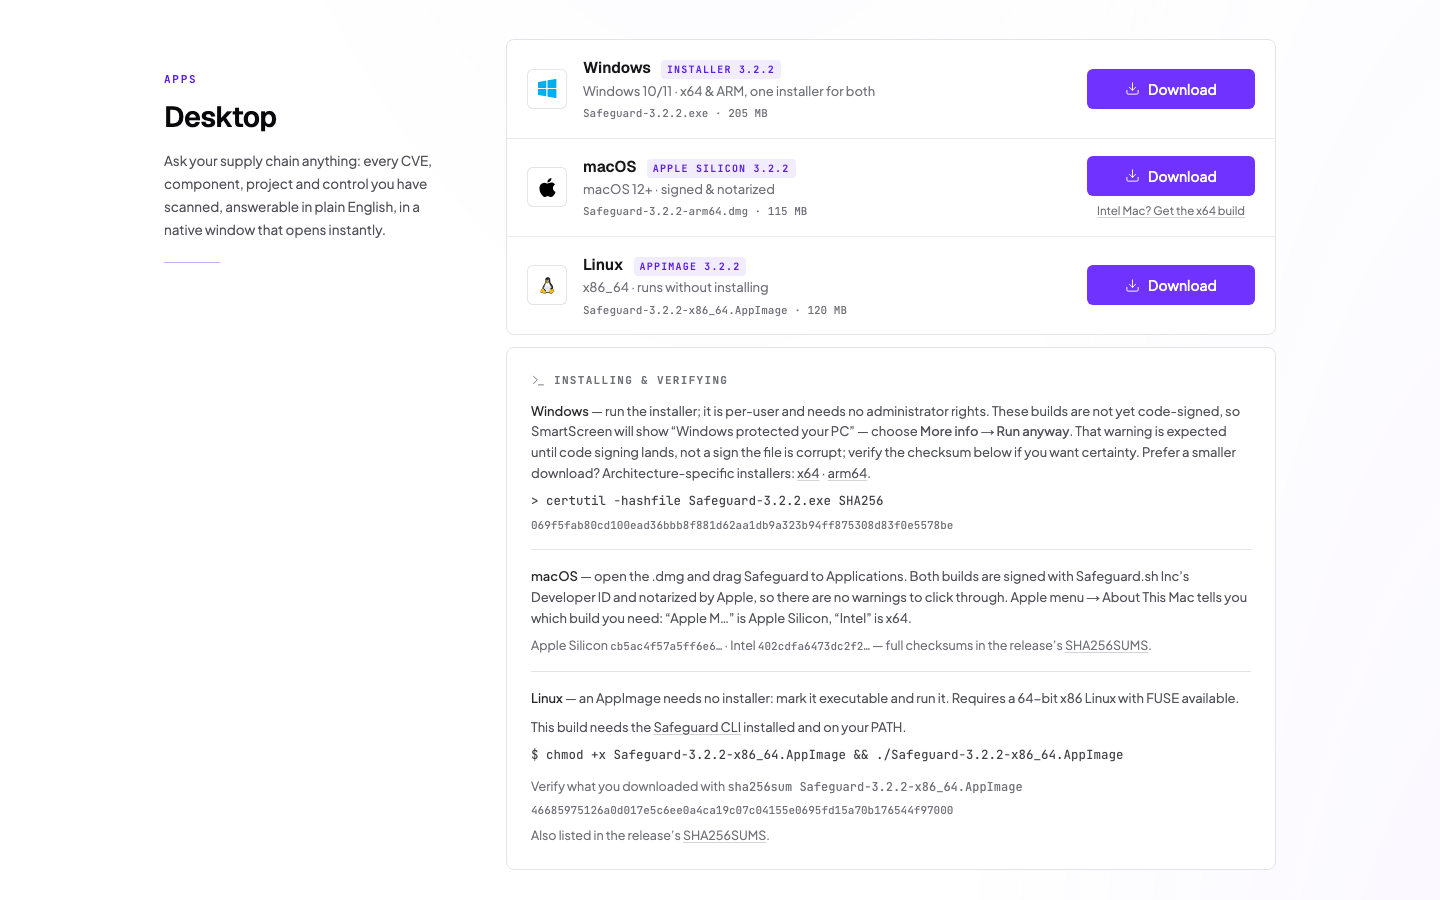
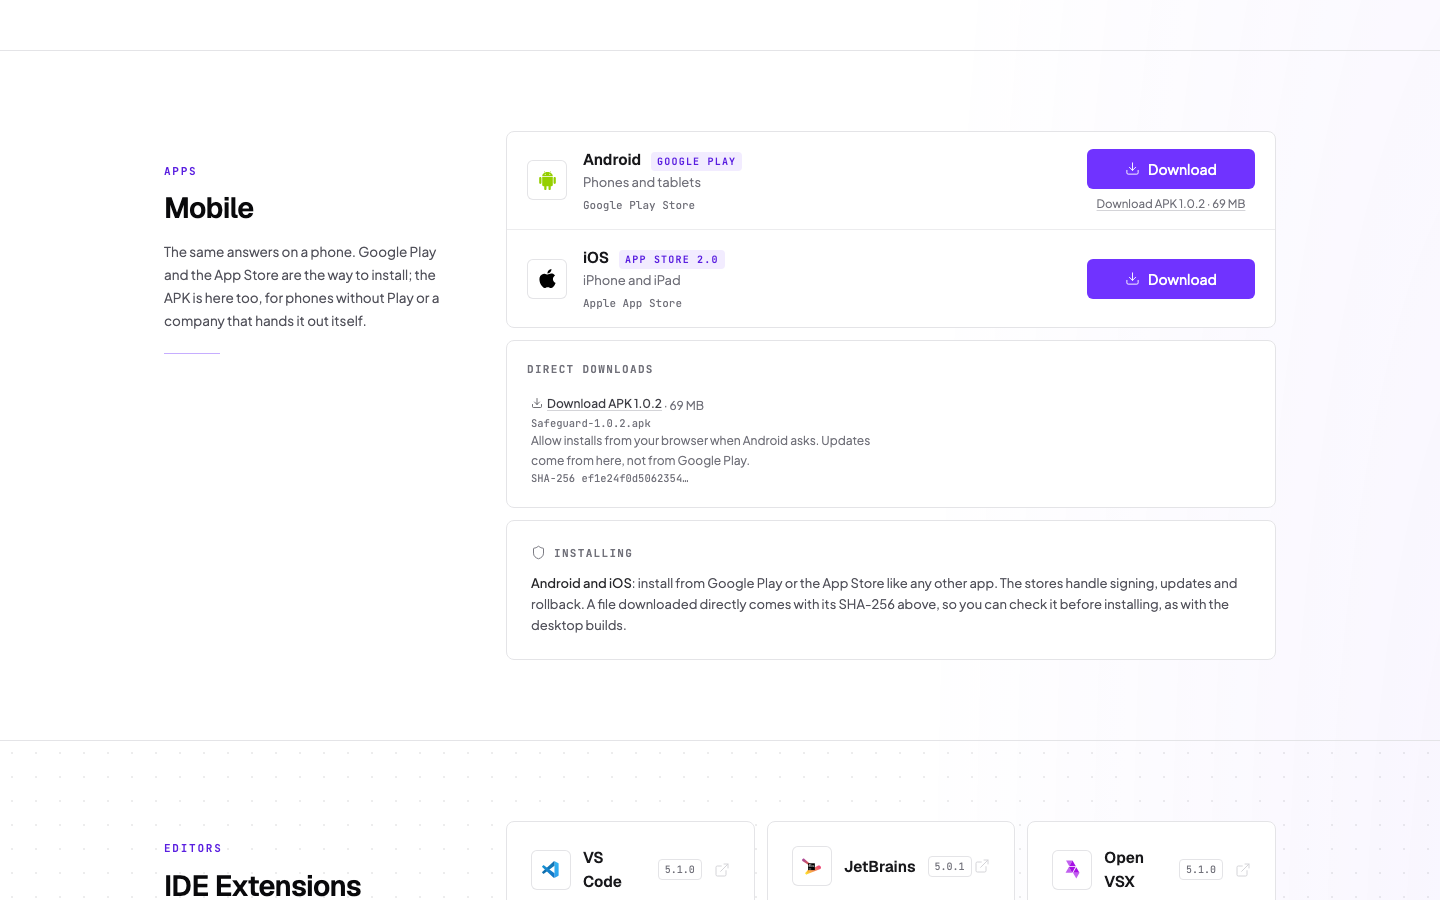
Safeguard on Huawei devices
Use Safeguard on a Huawei MateBook running Windows with the desktop app and the CLI, and on a Huawei phone or tablet through the direct Android APK or the browser.
3 min14 steps
See how Safeguard works before you sign up. Click through an interactive demo at your own pace, or watch a short video walkthrough.
Try it on your own code
Create a workspace and connect a repository. Plans start at $0.
Talk to an engineer
Book a 30-minute call and walk through your own stack with our team.
121 demos
InteractivePlatform
Use Safeguard on a Huawei MateBook running Windows with the desktop app and the CLI, and on a Huawei phone or tablet through the direct Android APK or the browser.
3 min14 steps
 Interactive
Platform
Use Safeguard on a Galaxy phone or tablet with the Android app from Google Play, and on a Galaxy Book with the Windows desktop app, the CLI and the browser extension.
3 min14 steps
InteractivePlatform
Install Safeguard across Mac, iPhone and iPad: the desktop app and the CLI on your Mac, the iOS app, and the Safari extension, all on one account.
3 min15 steps
 Interactive
Platform
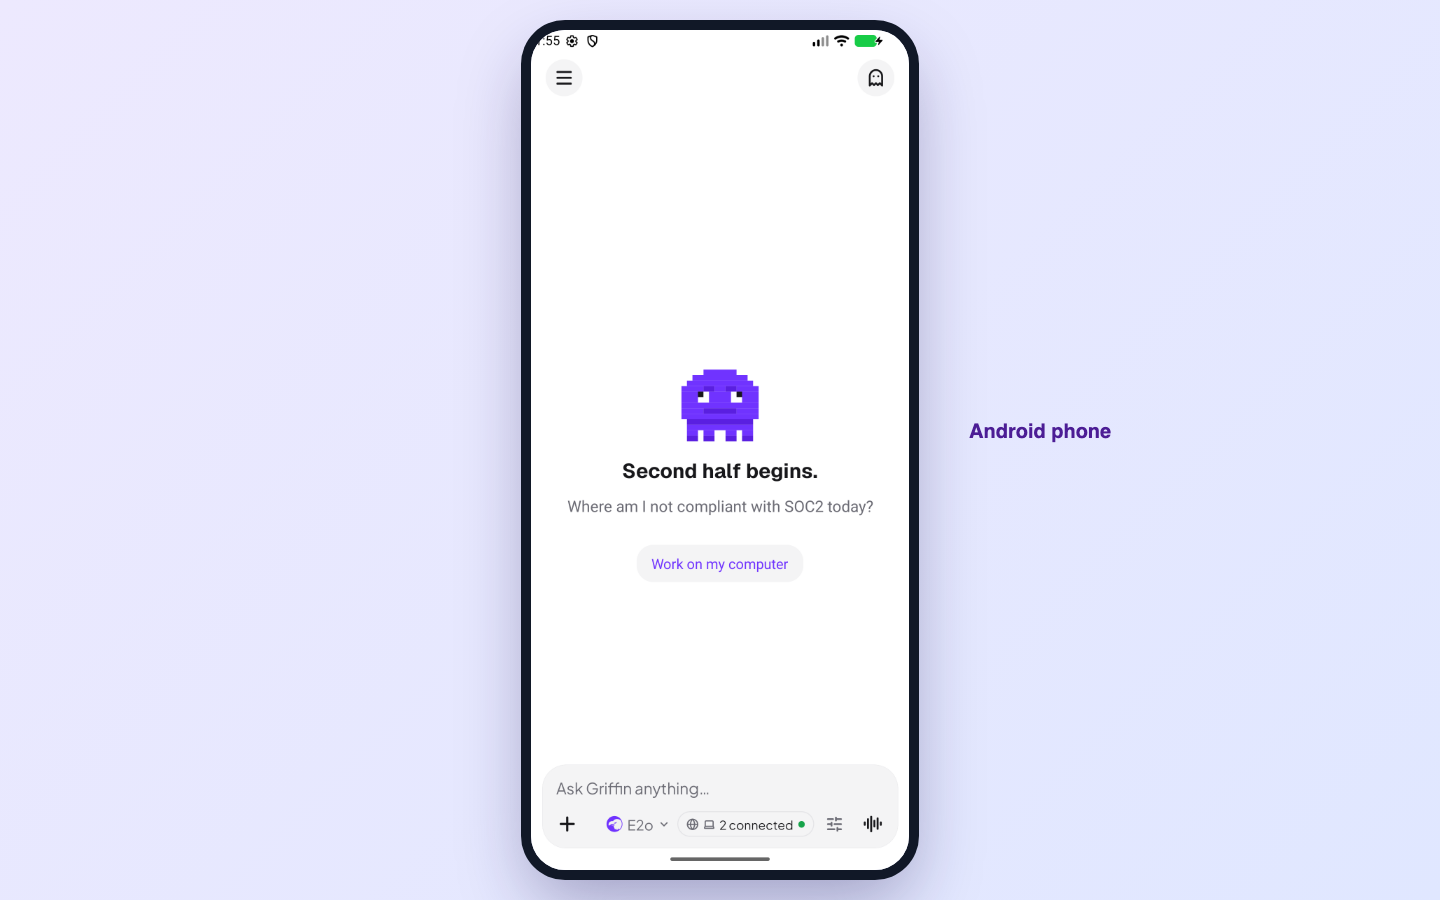
A real Android app session: see your desktop and CLI work, send a task to your computer and approve it from the phone.
2 min10 steps
 Interactive
Platform
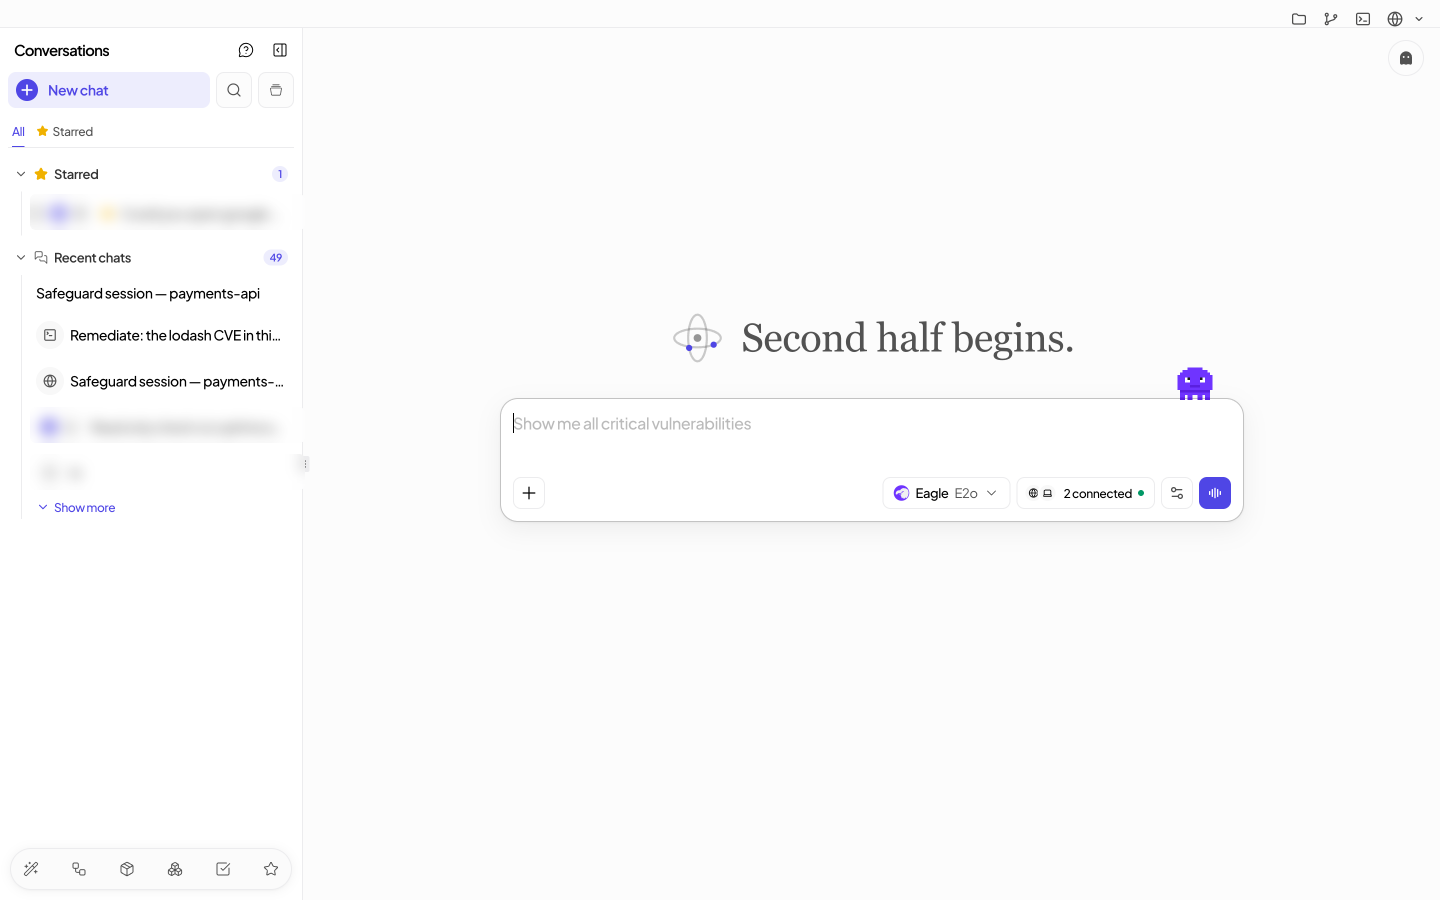
A real desktop app session: see the CLI run, pick a computer and folder, approve each step and get the result.
3 min12 steps
 Interactive
Platform
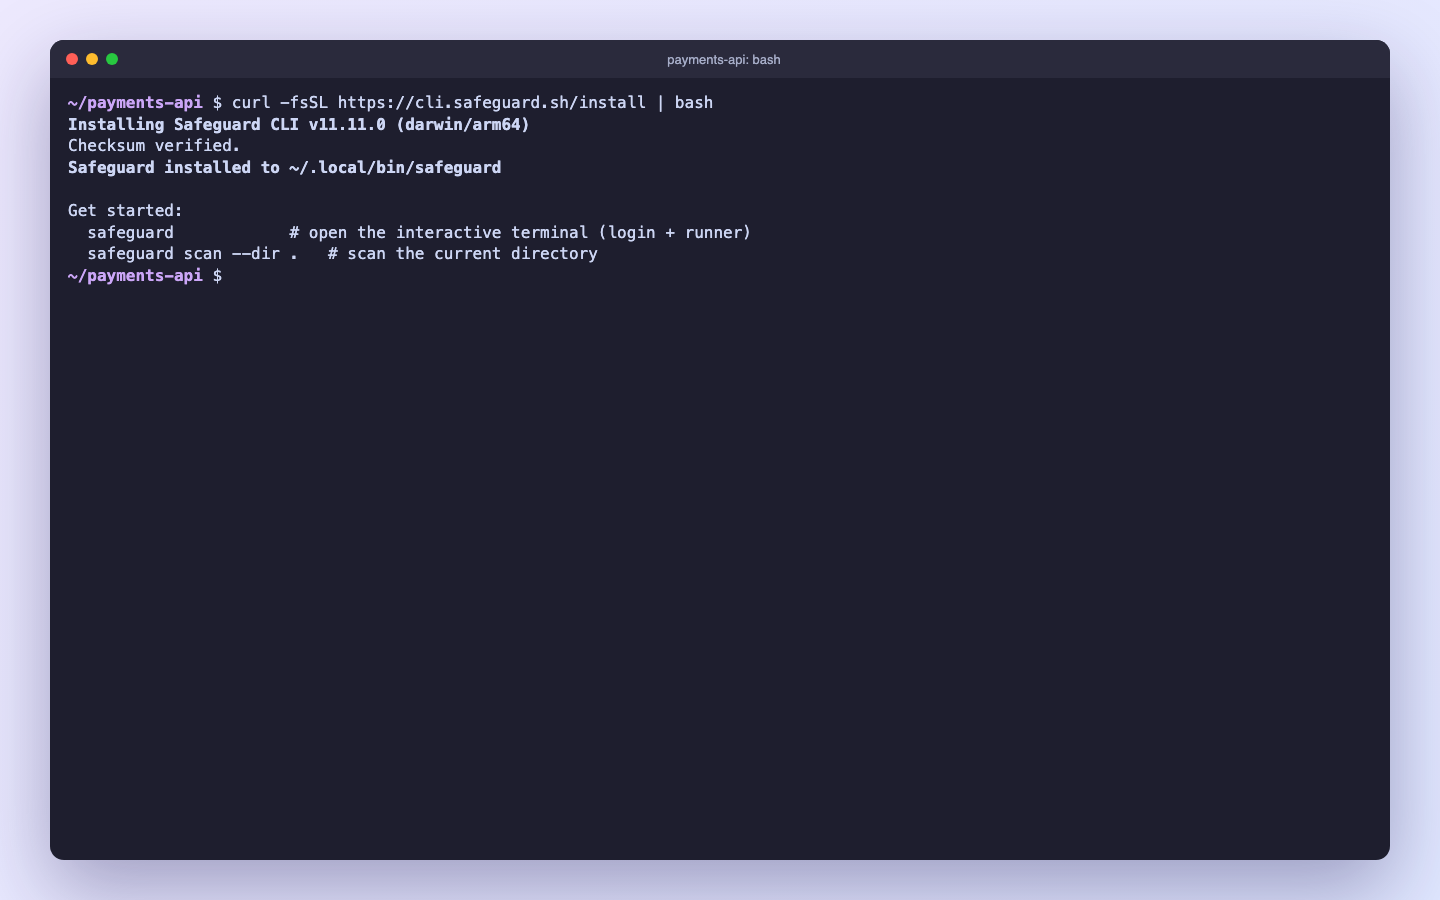
A real CLI session on a Mac: install, ask for a fix, approve each command, check the result and scan the folder.
3 min13 steps
 Interactive
Search
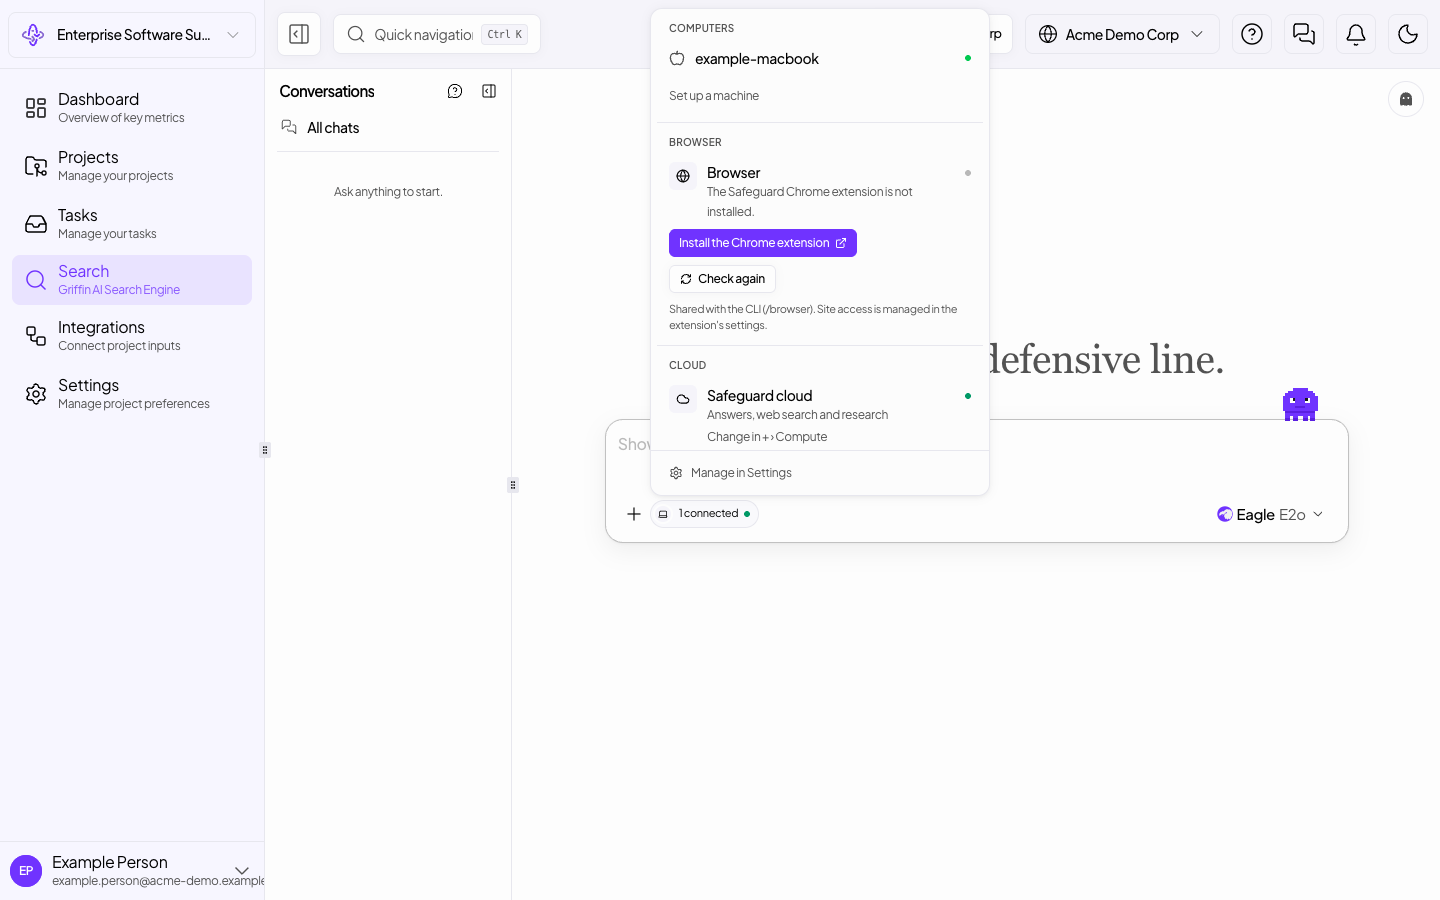
Attach a computer running the Safeguard CLI and a folder, ask for a fix, review the diff and approve the command before it runs.
2 min8 steps
 Interactive
Search
Hand Search a Chrome tab through the Safeguard extension, choose Ask, Auto or Yolo, and answer its questions before risky steps.
2 min7 steps
 Interactive
Platform
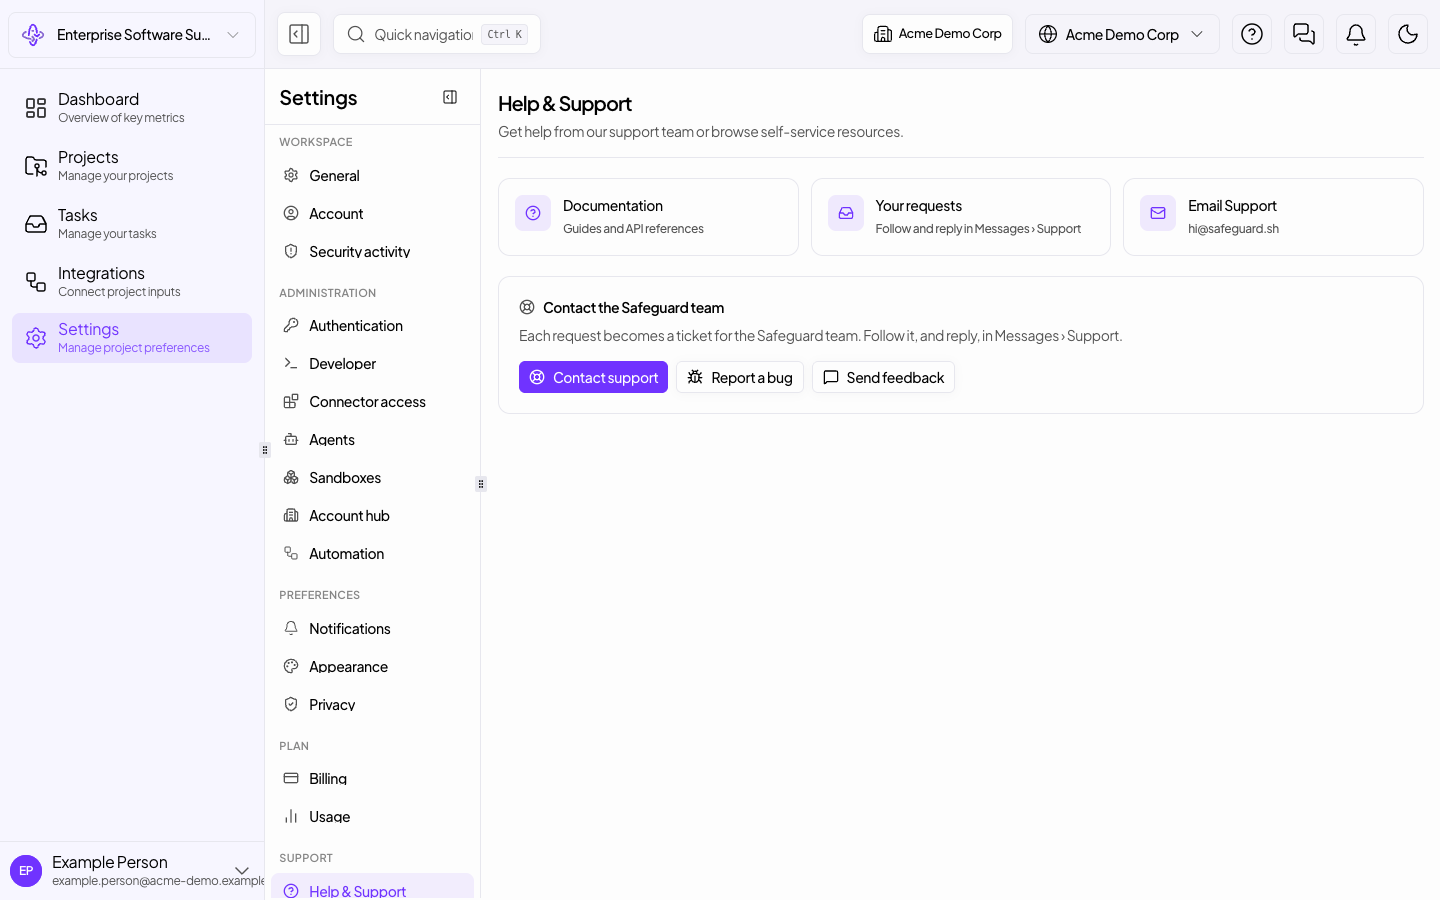
See where to get help in Safeguard, follow your requests, escalate one that is waiting on the team with the reply time the app states, and rate a resolved request.
2 min8 steps
 Interactive
Platform
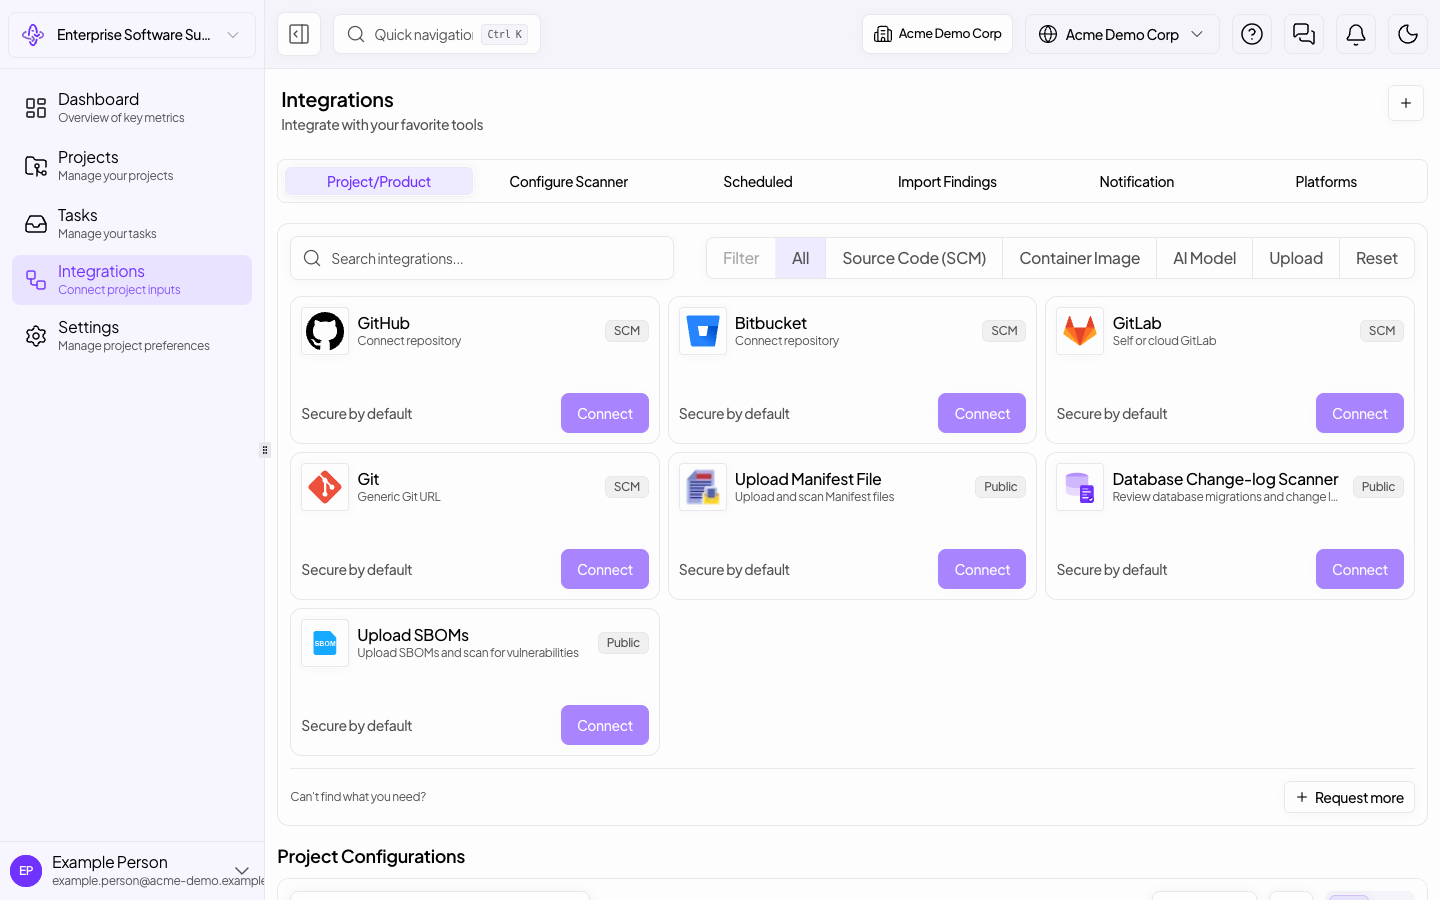
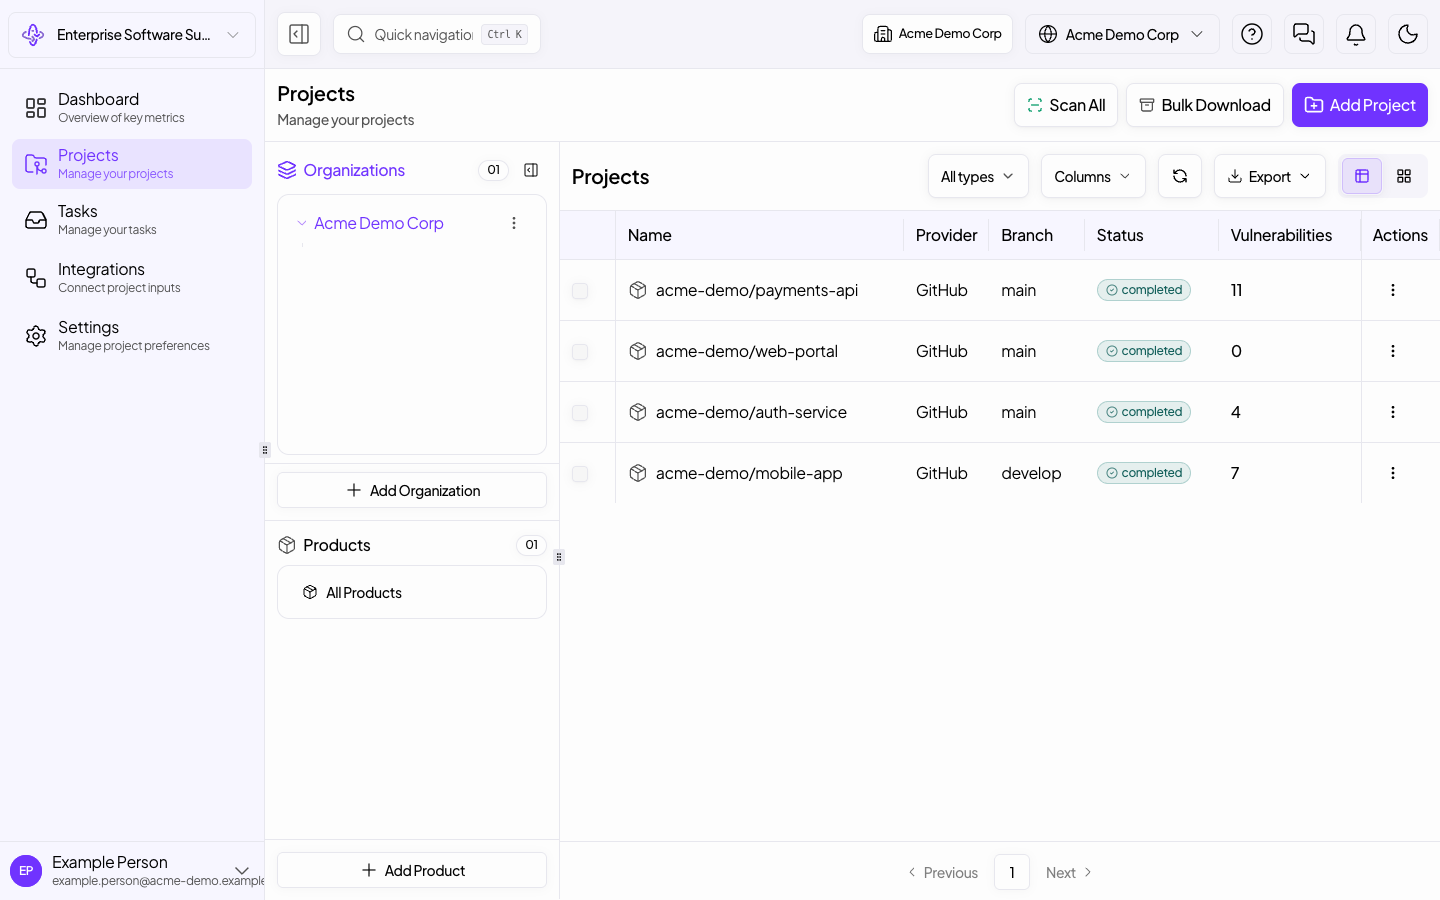
Report a bug with its severity, steps and an optional screen recording, then ask for an integration you need with the + request on the Integrations page. Both become tickets you can follow.
2 min9 steps
 Interactive
Platform
Send a support request from Help & Feedback with an urgency and optional screenshot or recording, keep the ticket reference, then follow the reply and answer it in Messages, Support.
2 min9 steps
 Interactive
Platform
Open Help & Feedback from any page, search the help articles your support team publishes, read one in place, and see matching articles suggested while you type a question.
2 min8 steps
 Interactive
Search
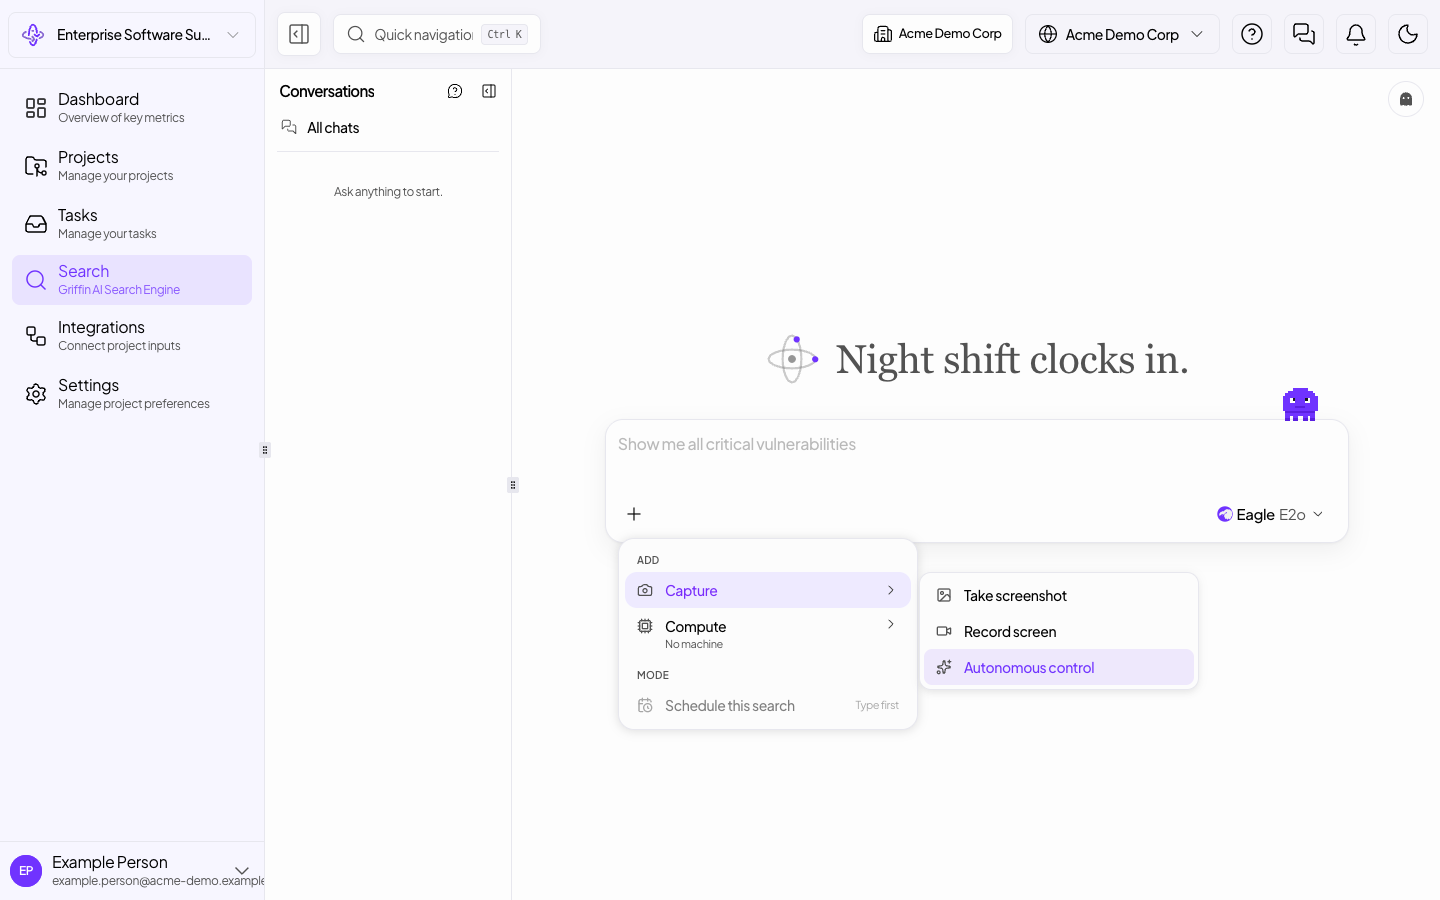
Autonomous control lets Search operate the Safeguard app for you. It reads each page, asks before anything high-risk, and stores the run in the conversation.
2 min8 steps
 Interactive
Search
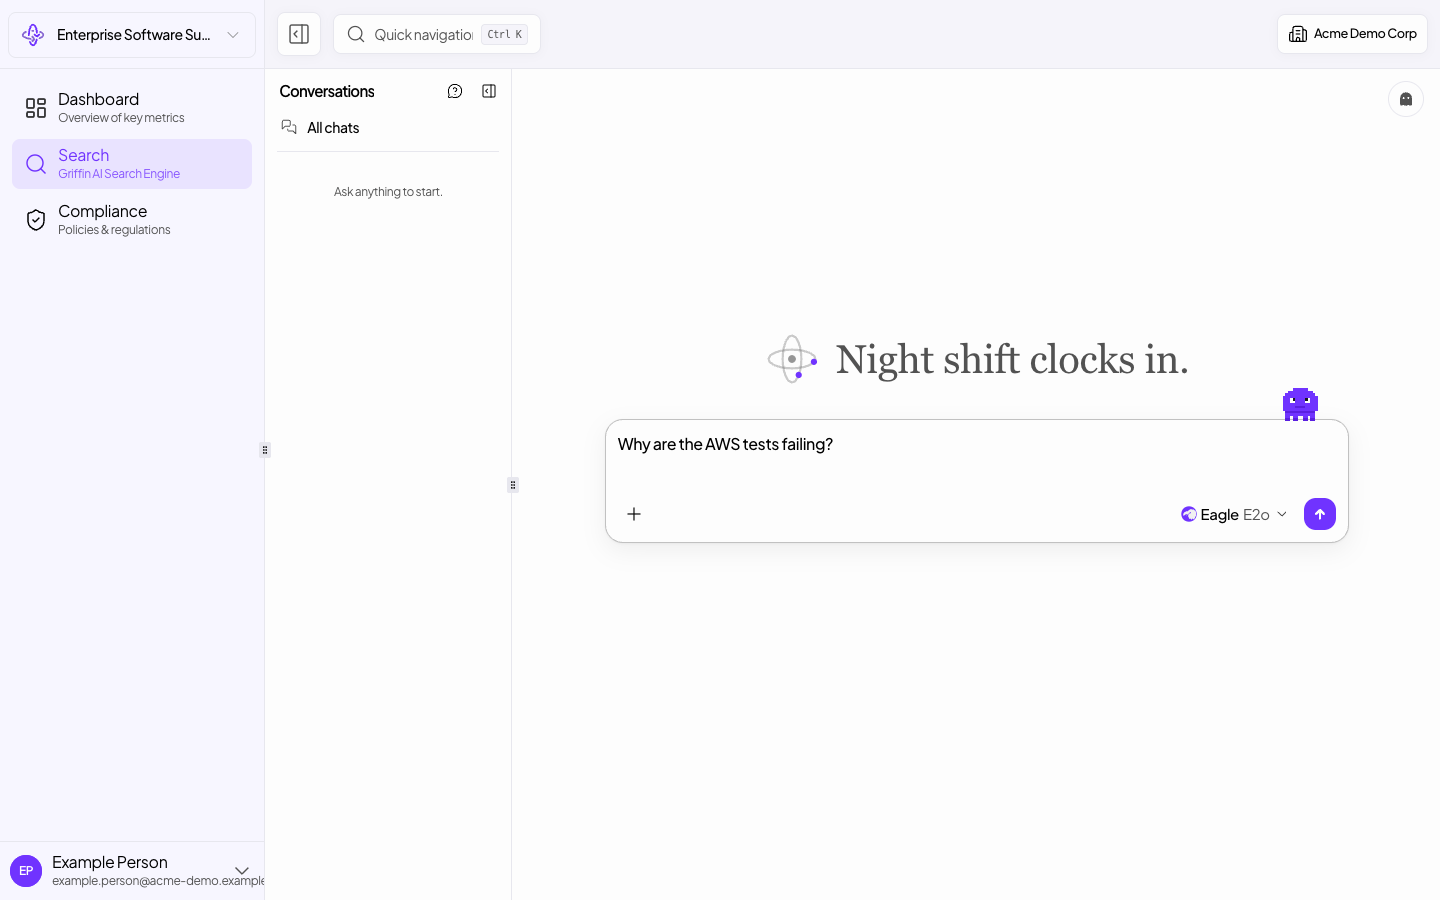
Ask Search why your AWS tests fail, then have Griffin prepare the follow-up task. The change waits for your Confirm and runs once, as you.
2 min7 steps
 Interactive
Compliance
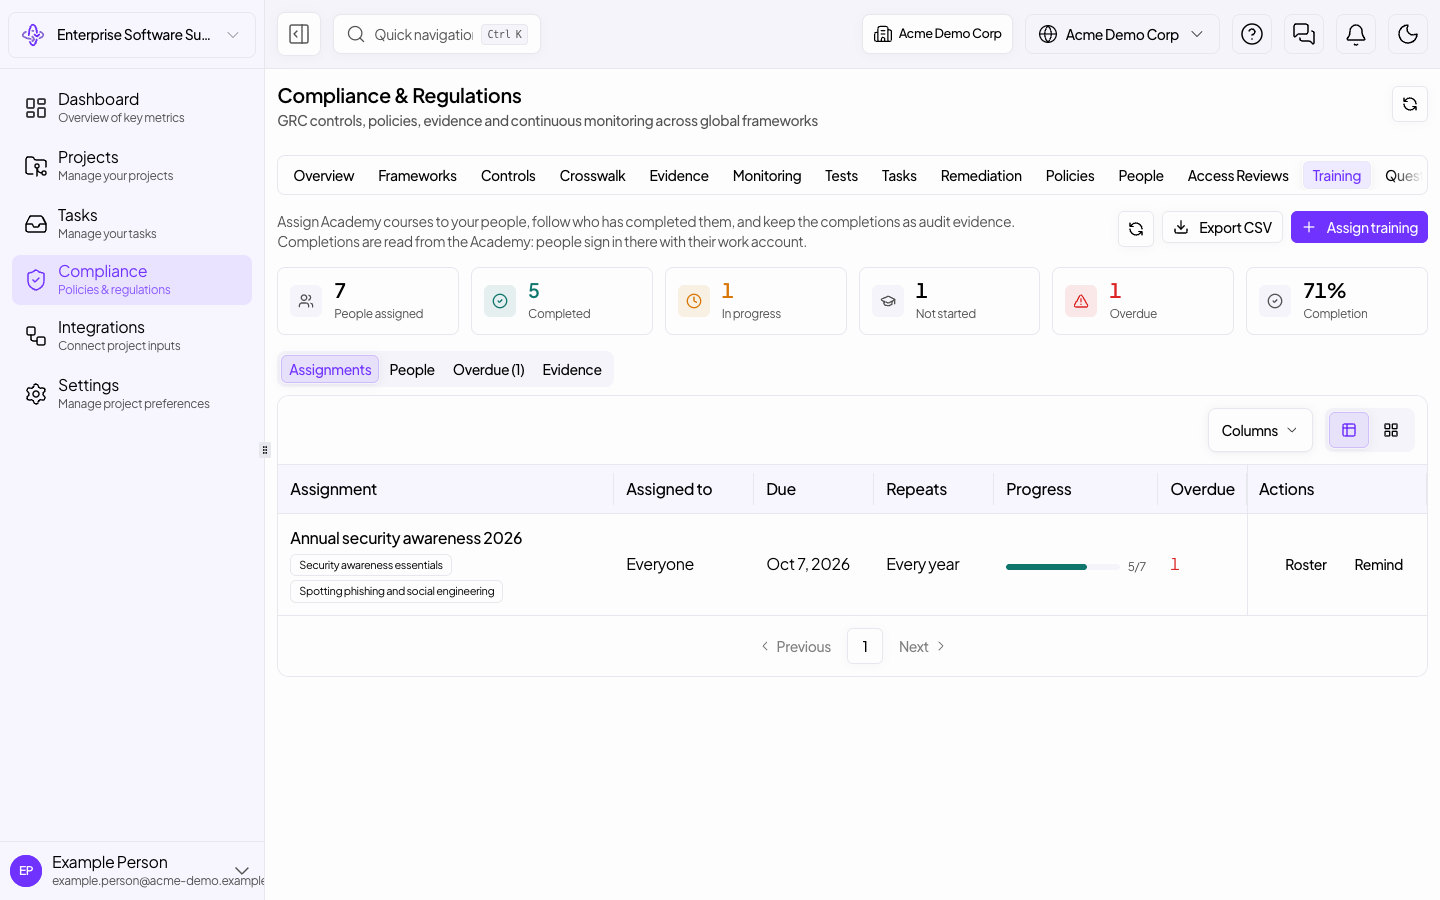
Assign Safeguard Academy courses, follow who has completed them and who is overdue, and turn completion into evidence for the controls that ask for training.
1 min8 steps
 Interactive
Compliance
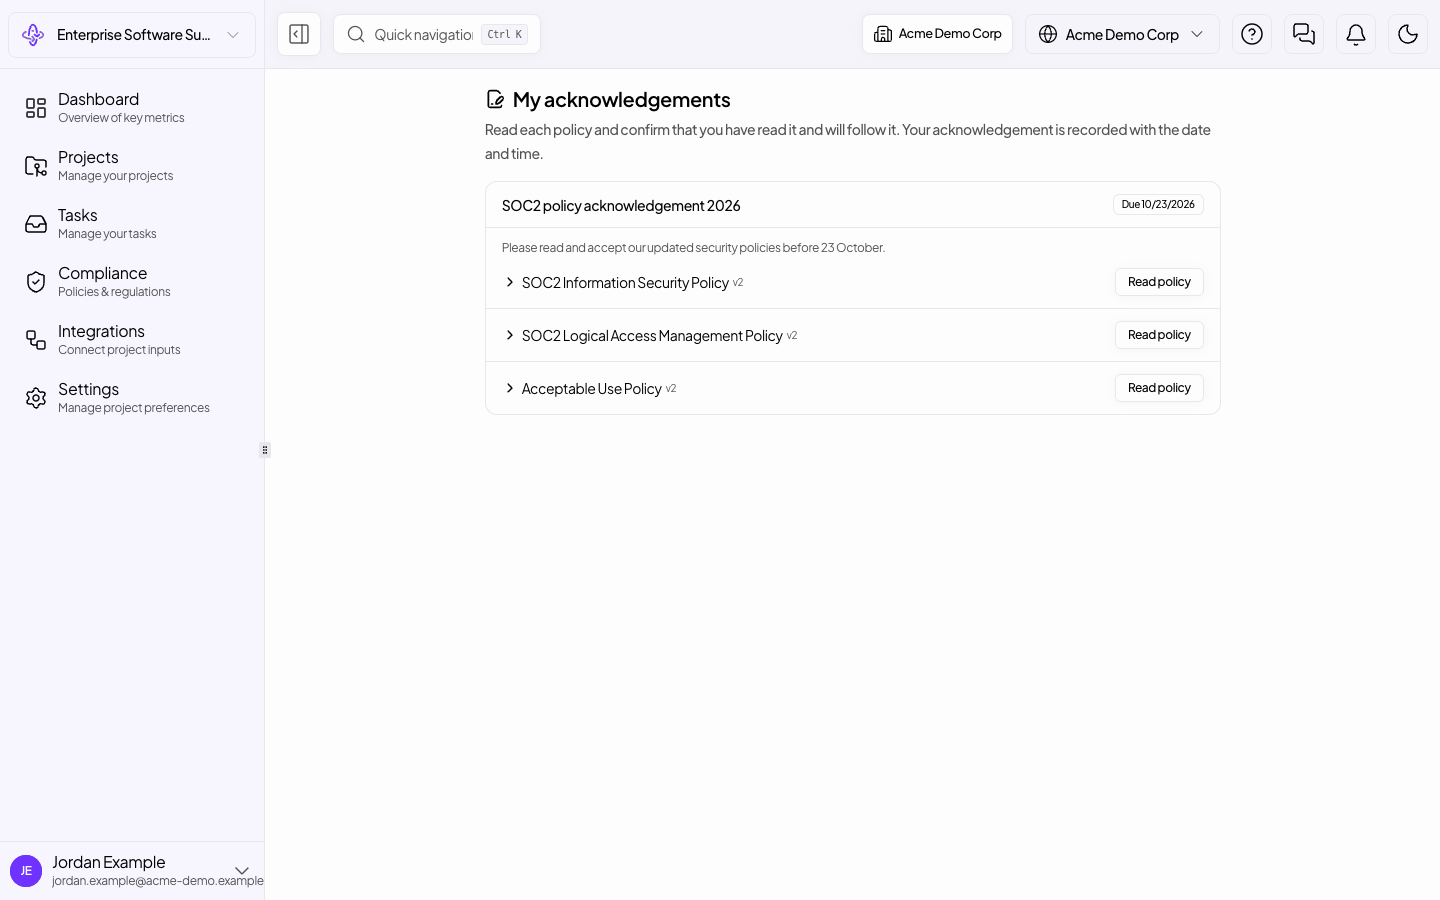
An employee reads and accepts each policy version in My acknowledgements; the compliance lead then sees the record per person, reminds whoever is pending, and follows the rate on the people register.
1 min7 steps
 Interactive
Compliance
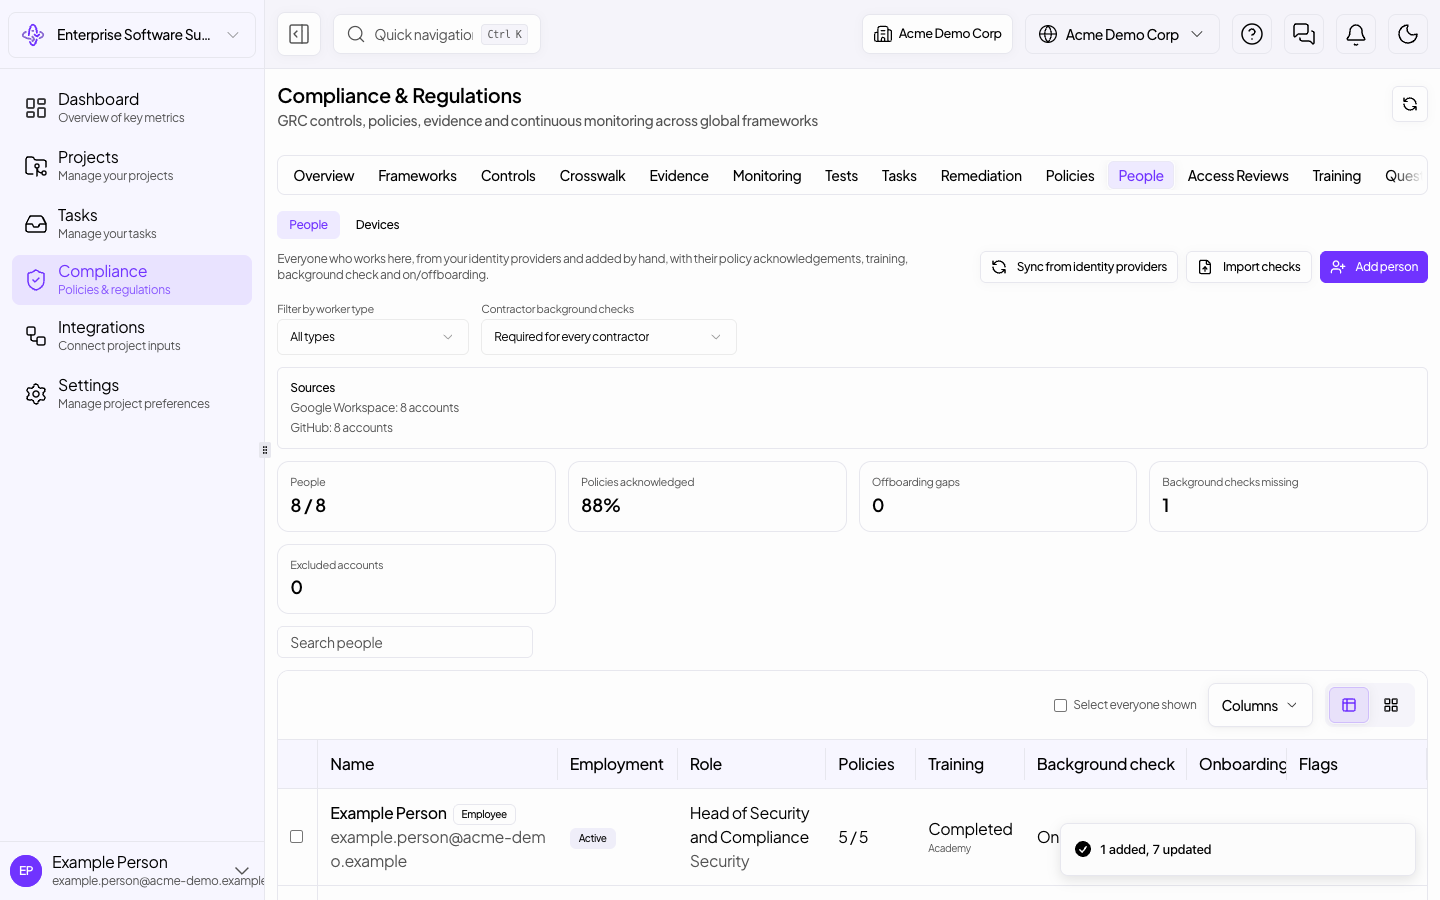
A new joiner arrives from the identity providers, their background check is recorded with the report, and their onboarding checklist, training and accounts sit on one record.
1 min8 steps
 Interactive
Compliance
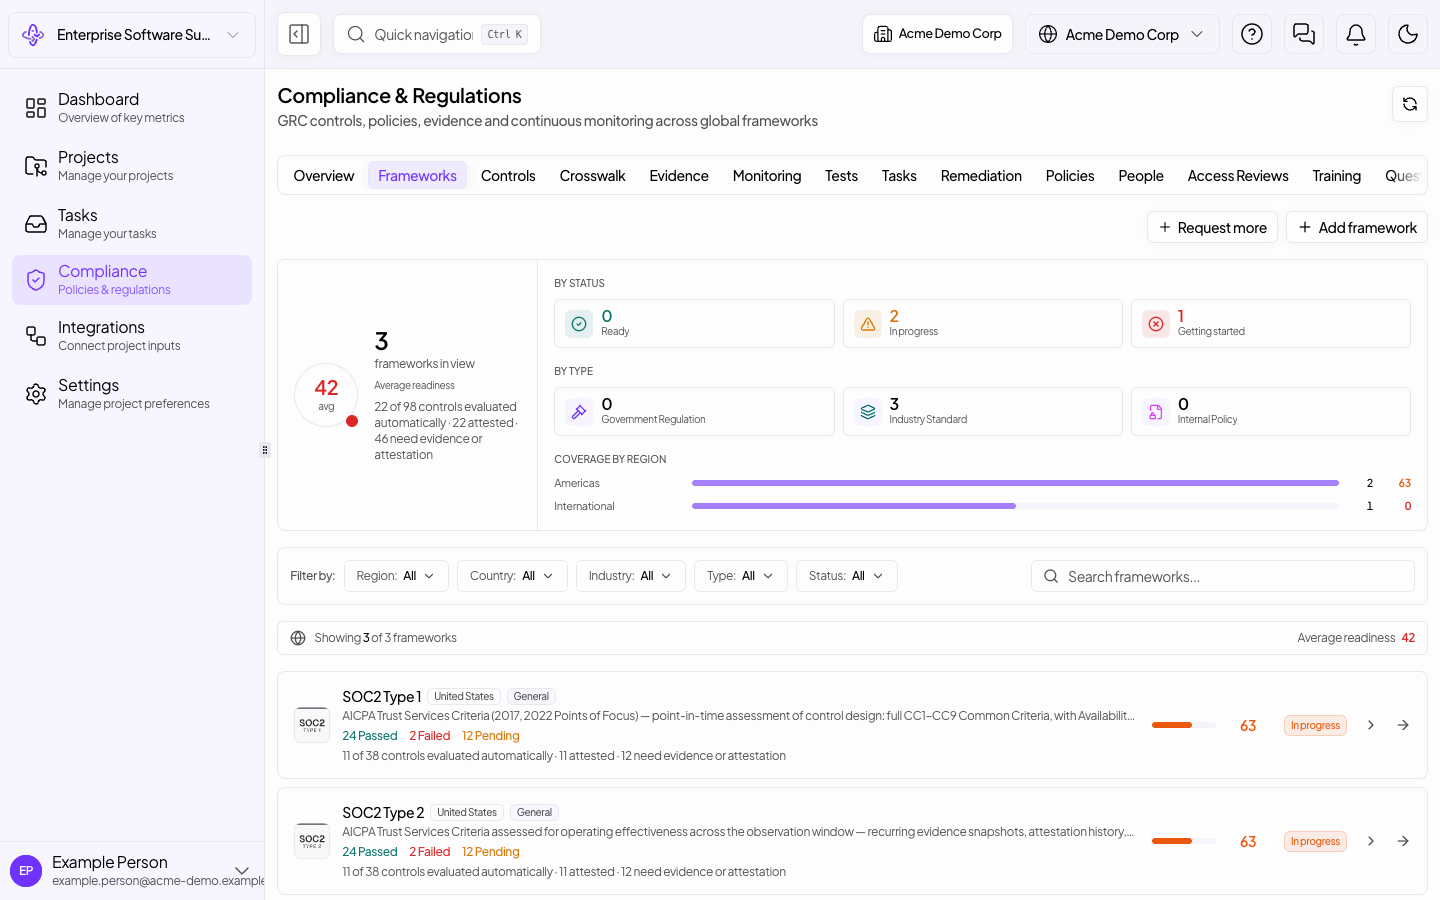
Create a custom framework for your own baseline or a customer's requirements, add its controls, and track it beside SOC2 with the same score and evidence.
1 min7 steps
 Interactive
Compliance
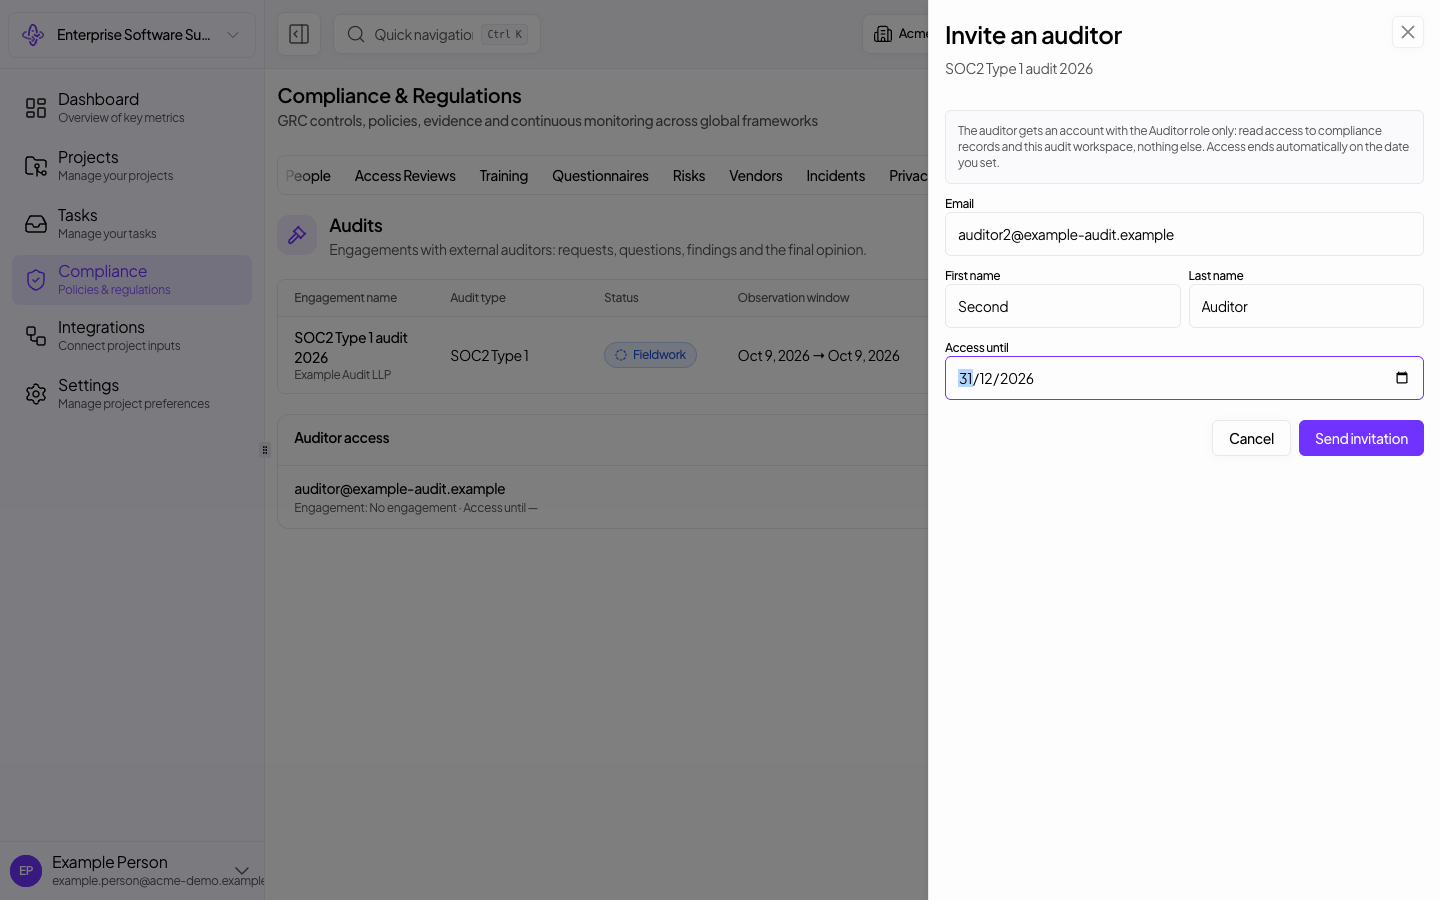
Invite the auditor, answer an open evidence request with evidence you already hold, respond to a finding, and keep the engagement's progress and audit package in one place.
2 min8 steps
 Interactive
Compliance
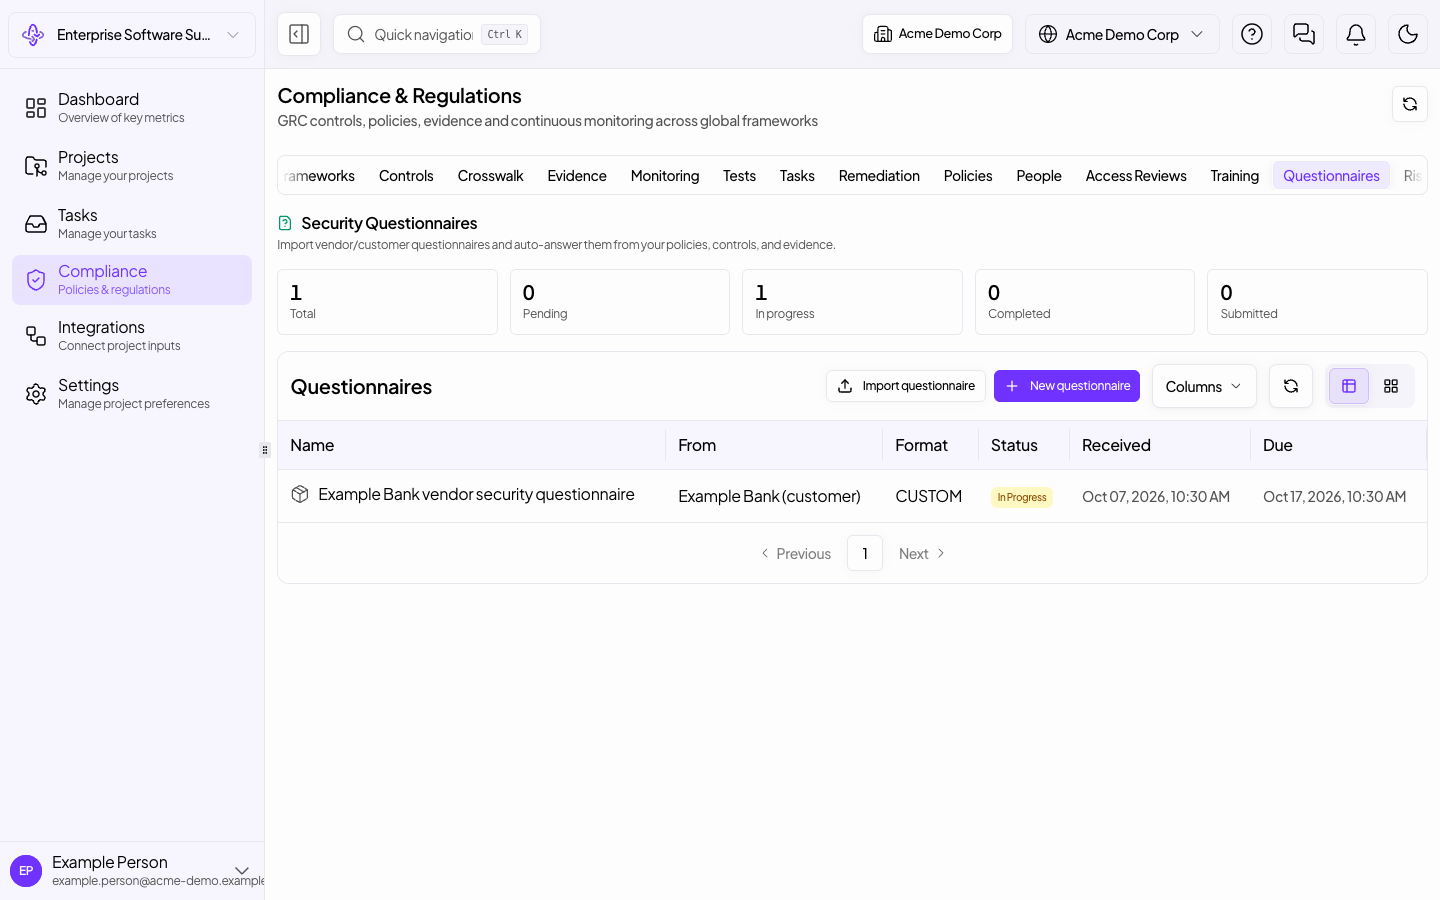
Open a customer's security questionnaire, draft answers grounded on your approved policies and evidence with their sources, review and approve each answer, and export it.
1 min7 steps
 Interactive
Compliance
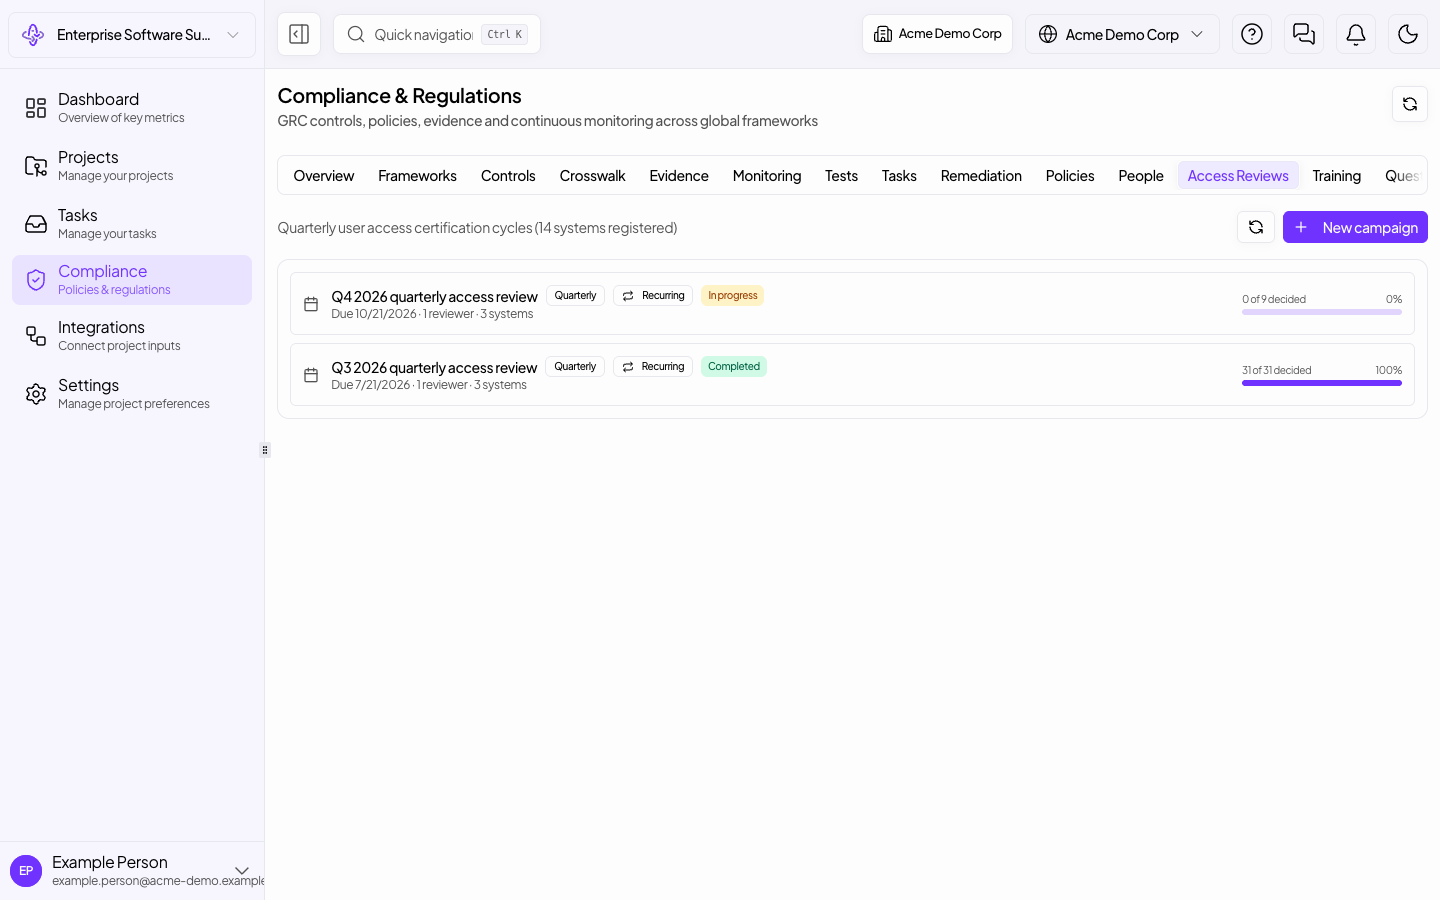
Open the quarter's access review, see every account pulled from the connected systems, revoke one with a reason, and follow the campaign to completion.
1 min6 steps
 Interactive
Compliance
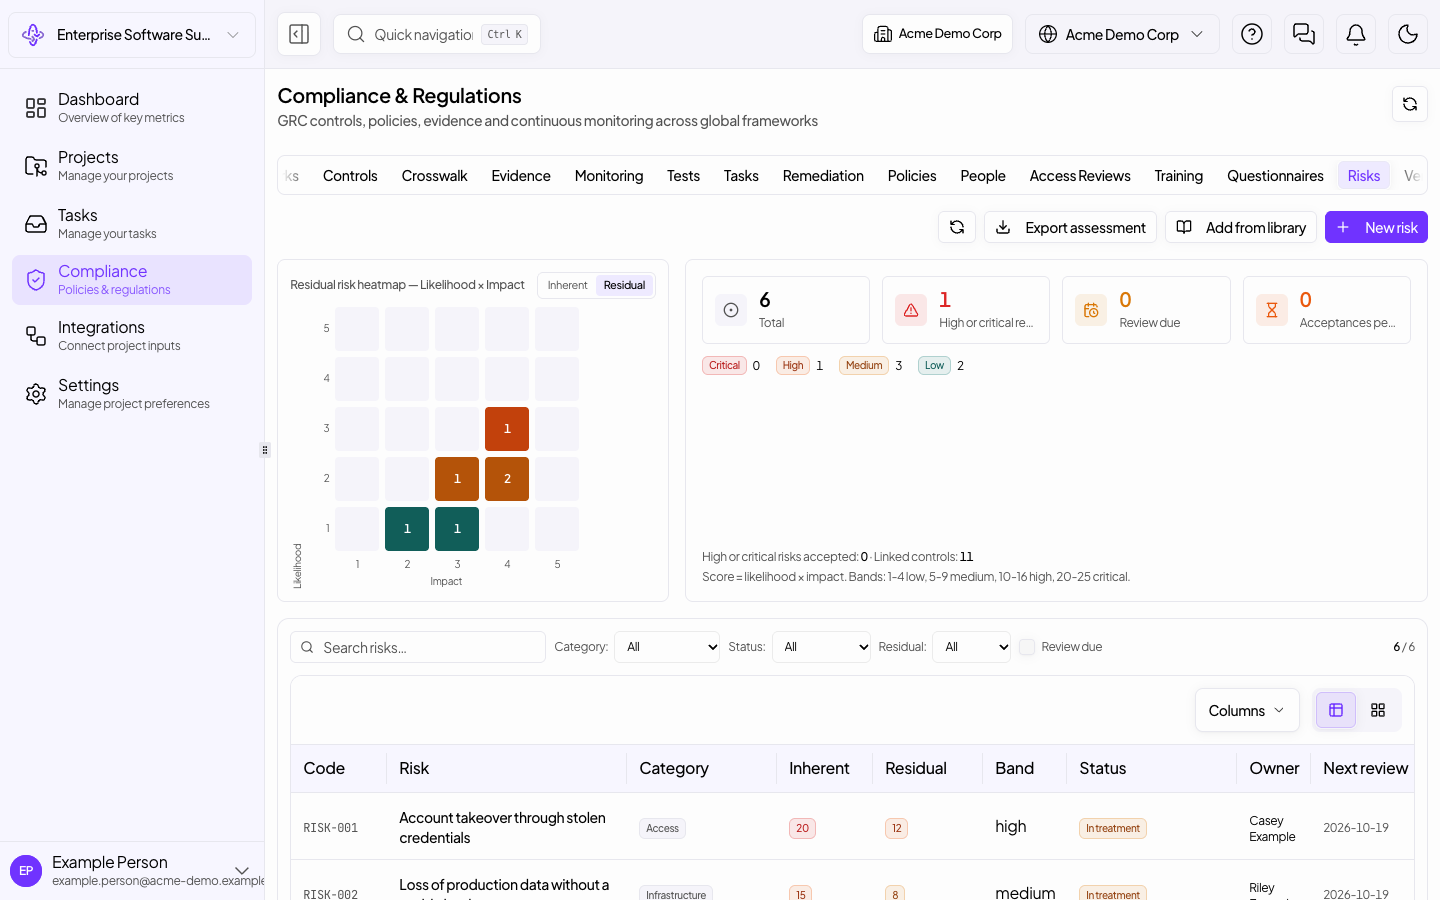
Score risks for likelihood and impact, see the inherent and residual heat maps, read how linked controls lower a risk, and record a review.
1 min7 steps
 Interactive
Compliance
Keep data subject requests in one register with their 30-day deadlines, record a new request, and complete a deletion request on time.
1 min7 steps
 Interactive
Compliance
Record a security incident in the register, see which major incidents still owe a post-mortem and by when, and record the post-mortem with root cause and actions.
1 min8 steps
 Interactive
Compliance
Collect evidence from every connected system at once, see it land in the evidence register with its source, and accept what people submitted in the review queue.
1 min7 steps
 Interactive
Compliance
Connect an AWS account to Compliance with a read-only key, see it verified, and follow the AWS continuous tests down to each resource by region.
1 min7 steps
 Interactive
Compliance
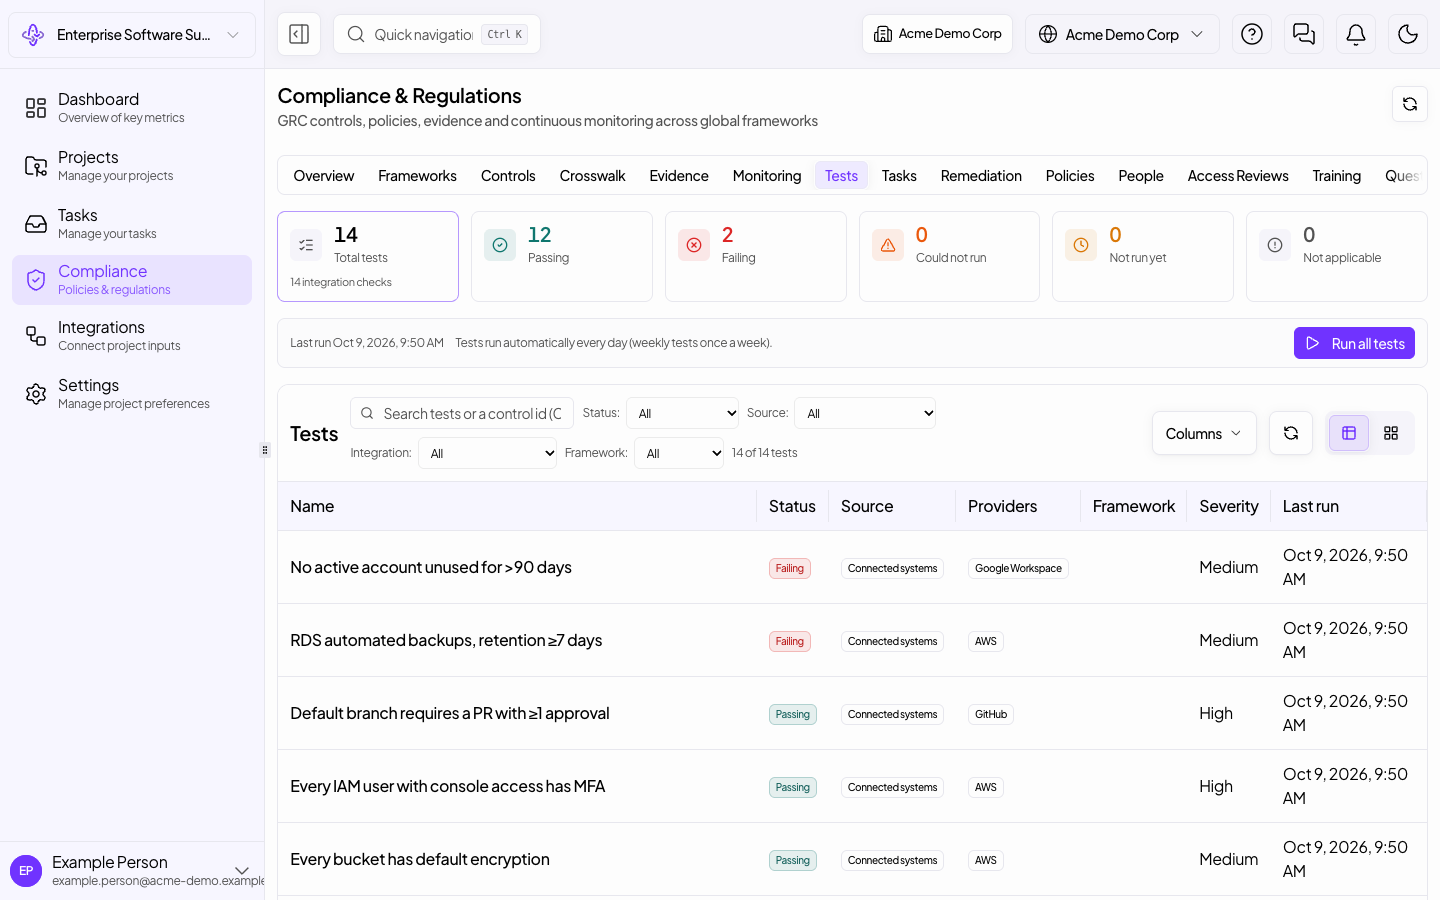
Run the continuous tests, open the one that fails, see the affected accounts and the owner, fix it at the source, rerun the test and see the task close.
2 min9 steps
 Interactive
Compliance
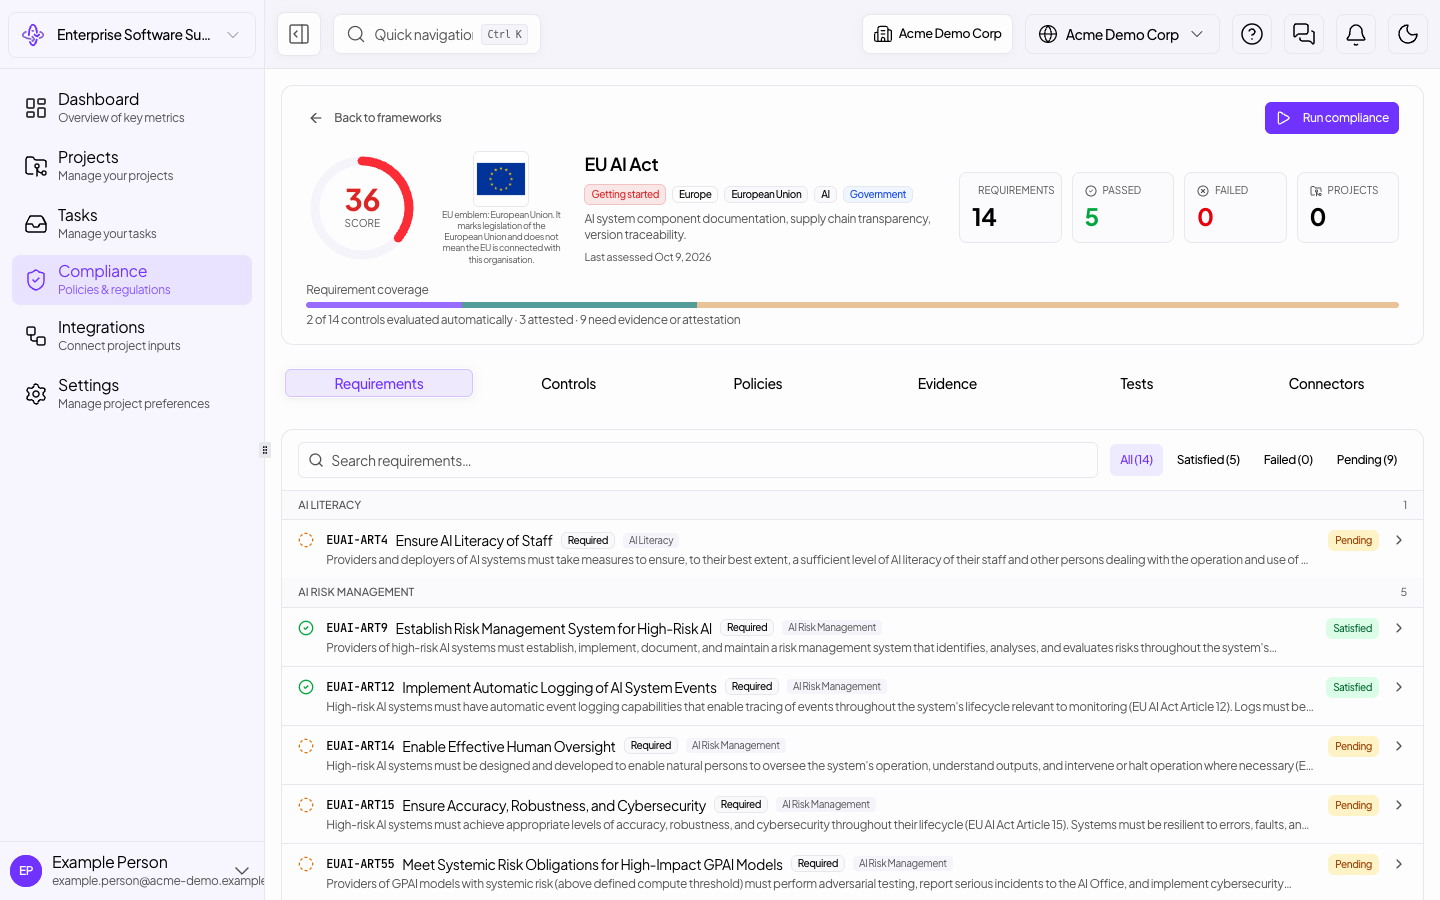
Track EU AI Act obligations as controls, attach technical documentation evidence to Article 11, and start the technical documentation policy from its template.
1 min6 steps
 Interactive
Compliance
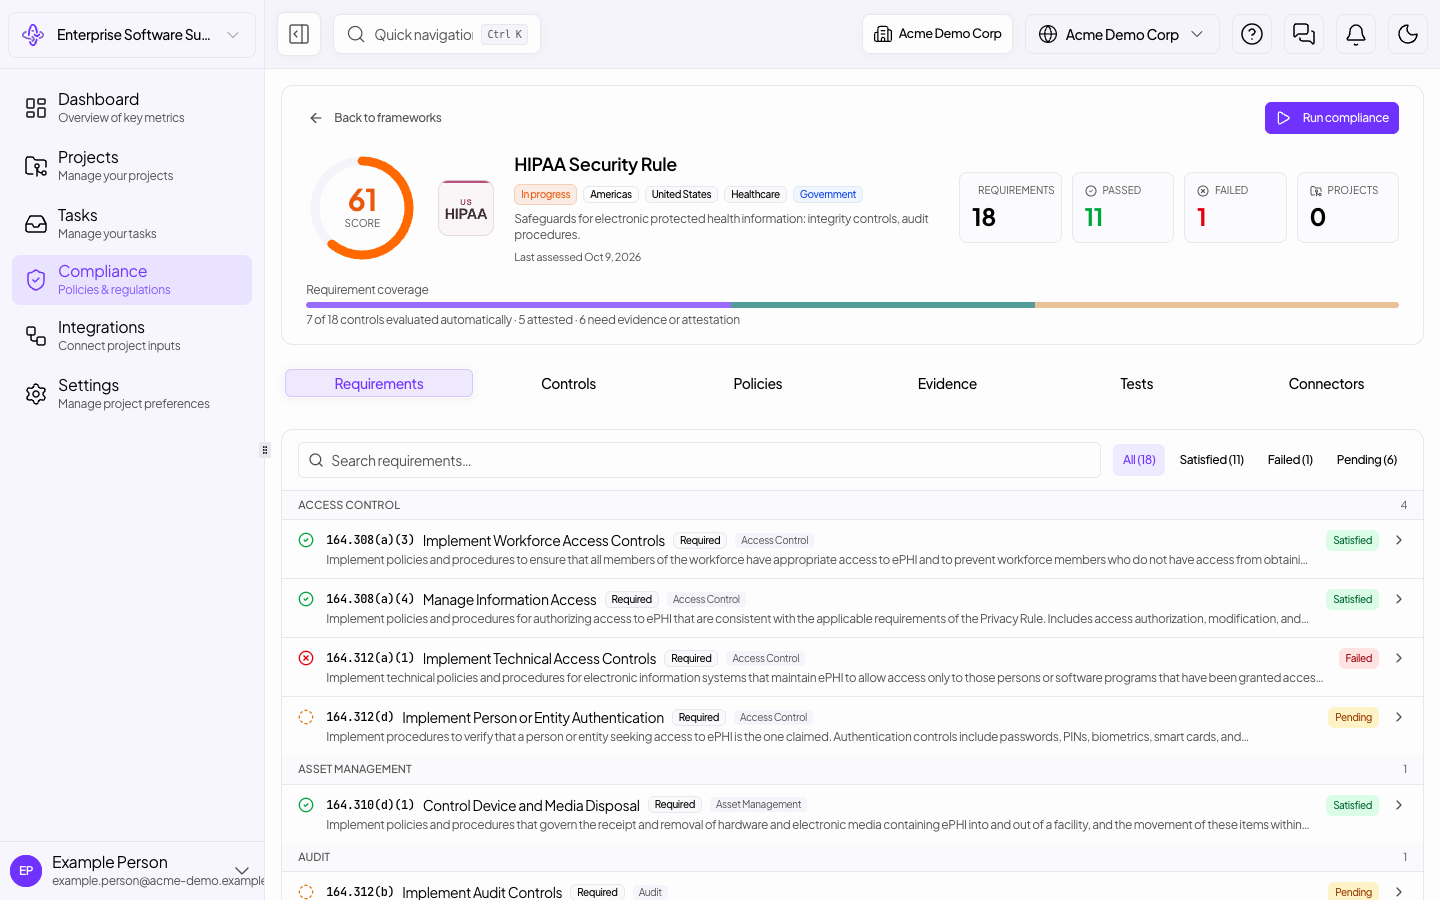
Track the HIPAA Security Rule safeguards, the continuous tests that evidence the technical safeguards, a business associate control, and the BAA management policy template.
1 min7 steps
 Interactive
Compliance
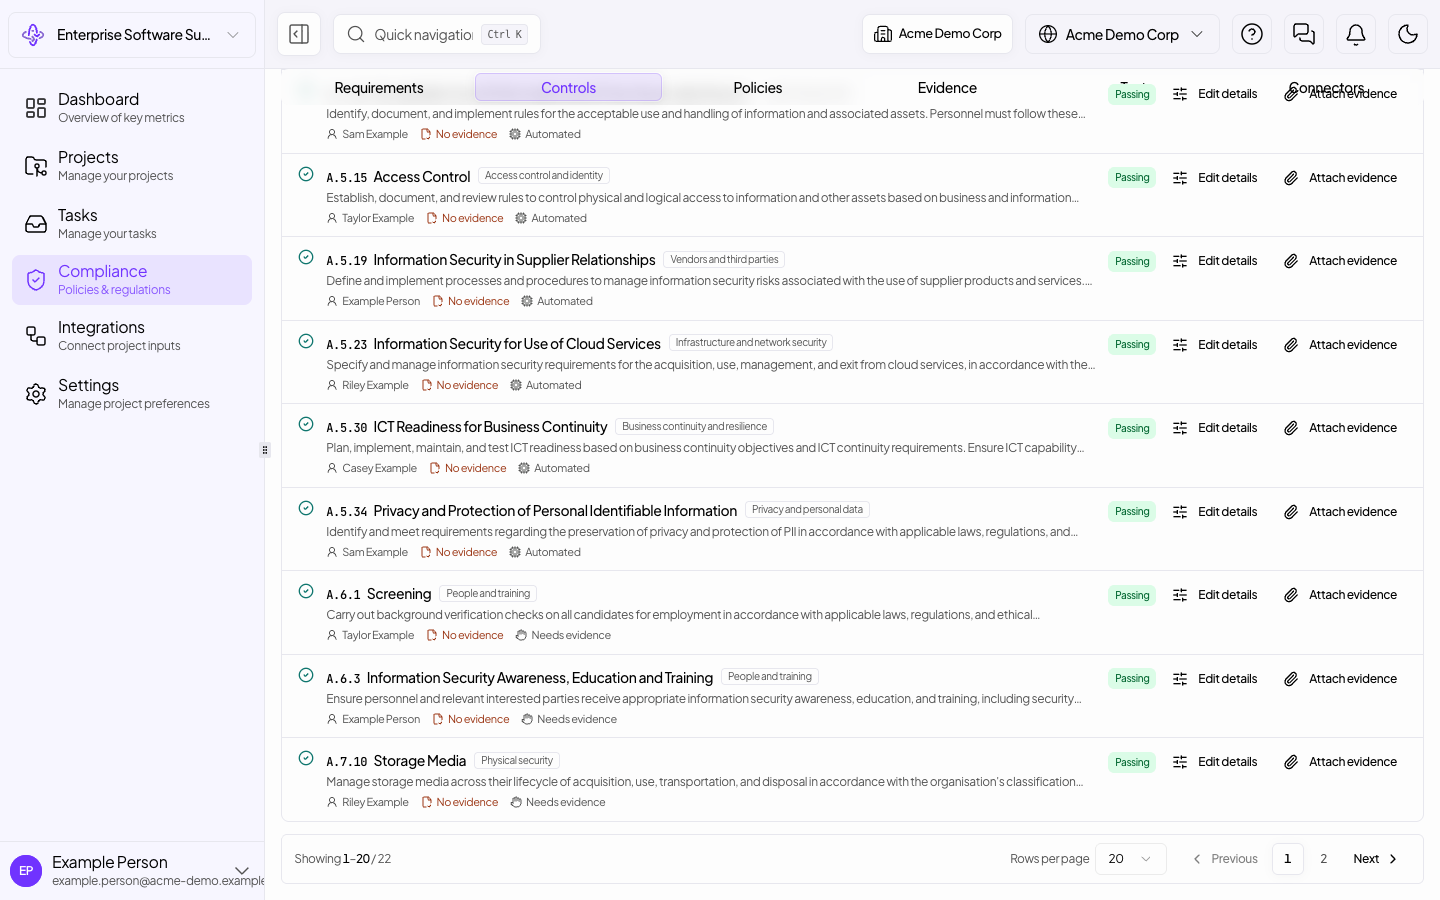
Work through ISO/IEC 27001 Annex A controls: scope one out with a written justification, start the Statement of Applicability from its template, and plan the Stage 1 audit.
2 min8 steps
 Interactive
Compliance
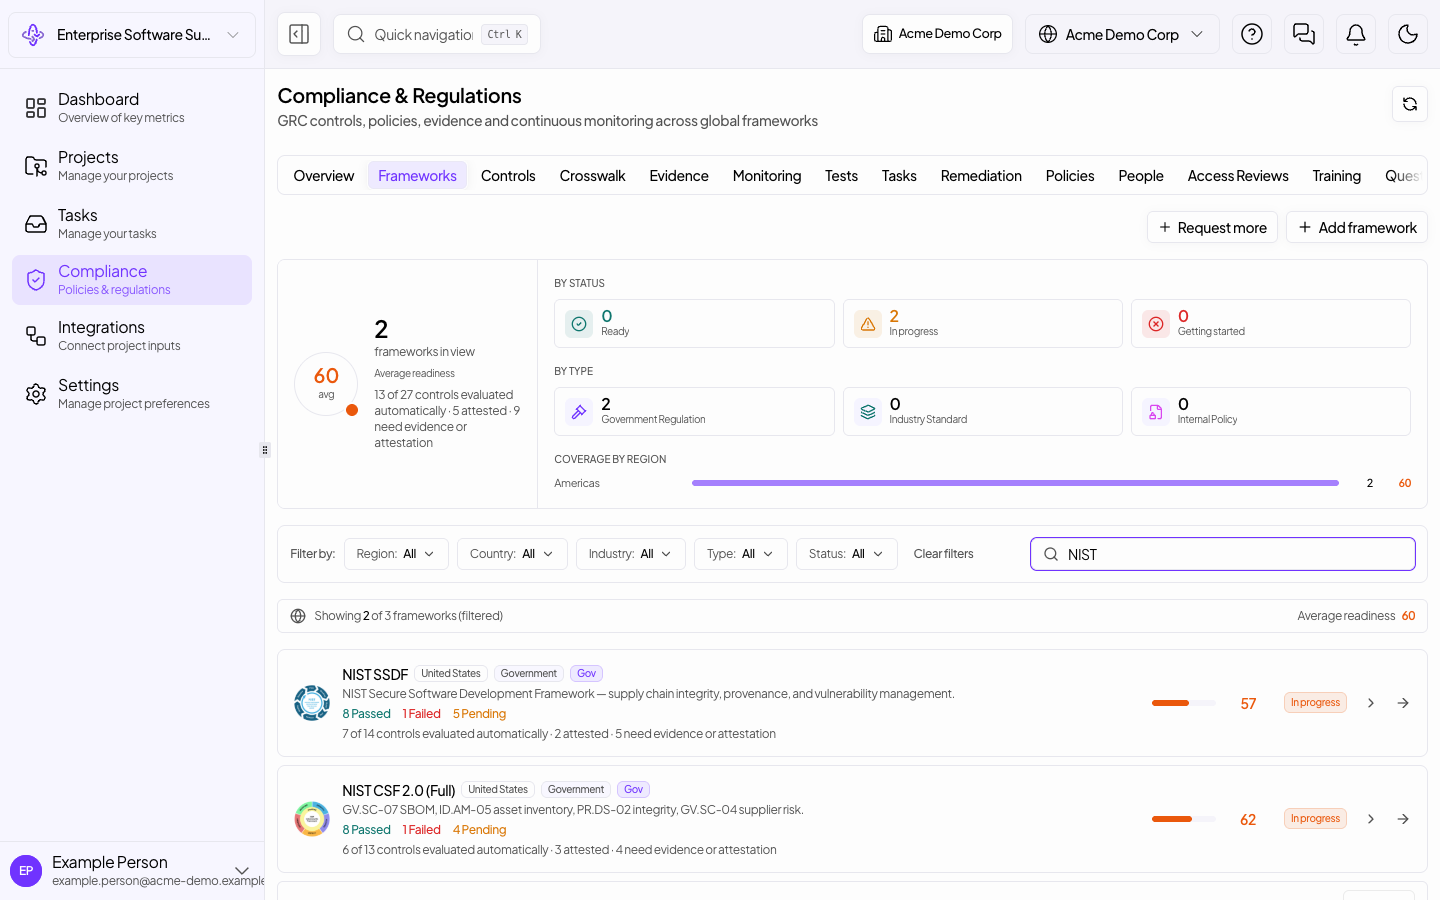
Track NIST CSF 2.0 and NIST SSDF side by side: readiness per framework, requirements by function and practice group, and an SSDF policy from its template.
1 min7 steps
 Interactive
Compliance
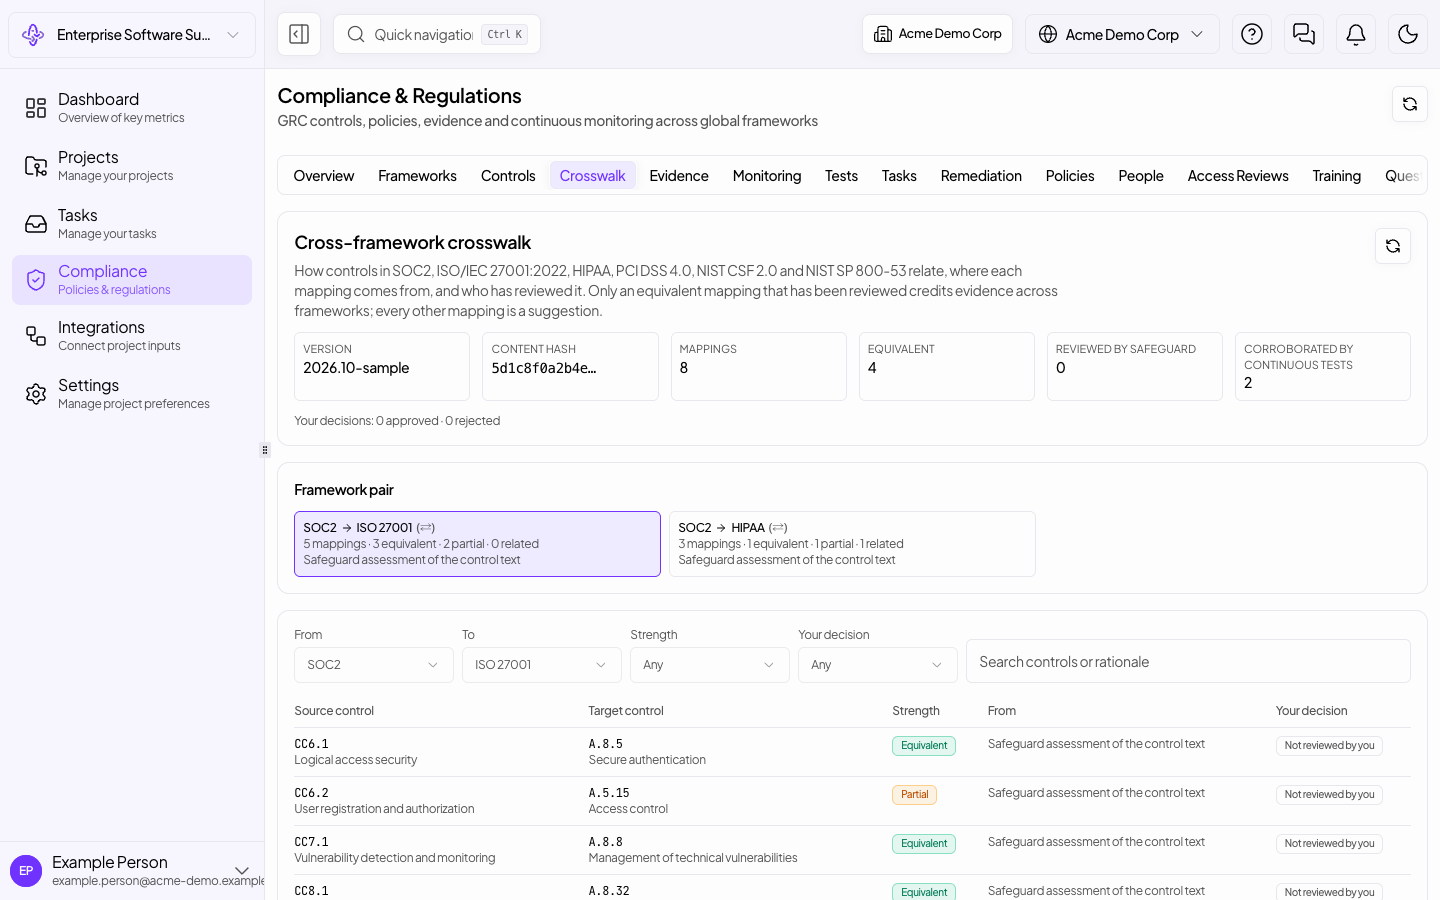
See how a SOC2 control maps to ISO/IEC 27001 and HIPAA in the crosswalk, approve a mapping, and let its evidence count toward the other framework.
1 min6 steps
 Interactive
Compliance
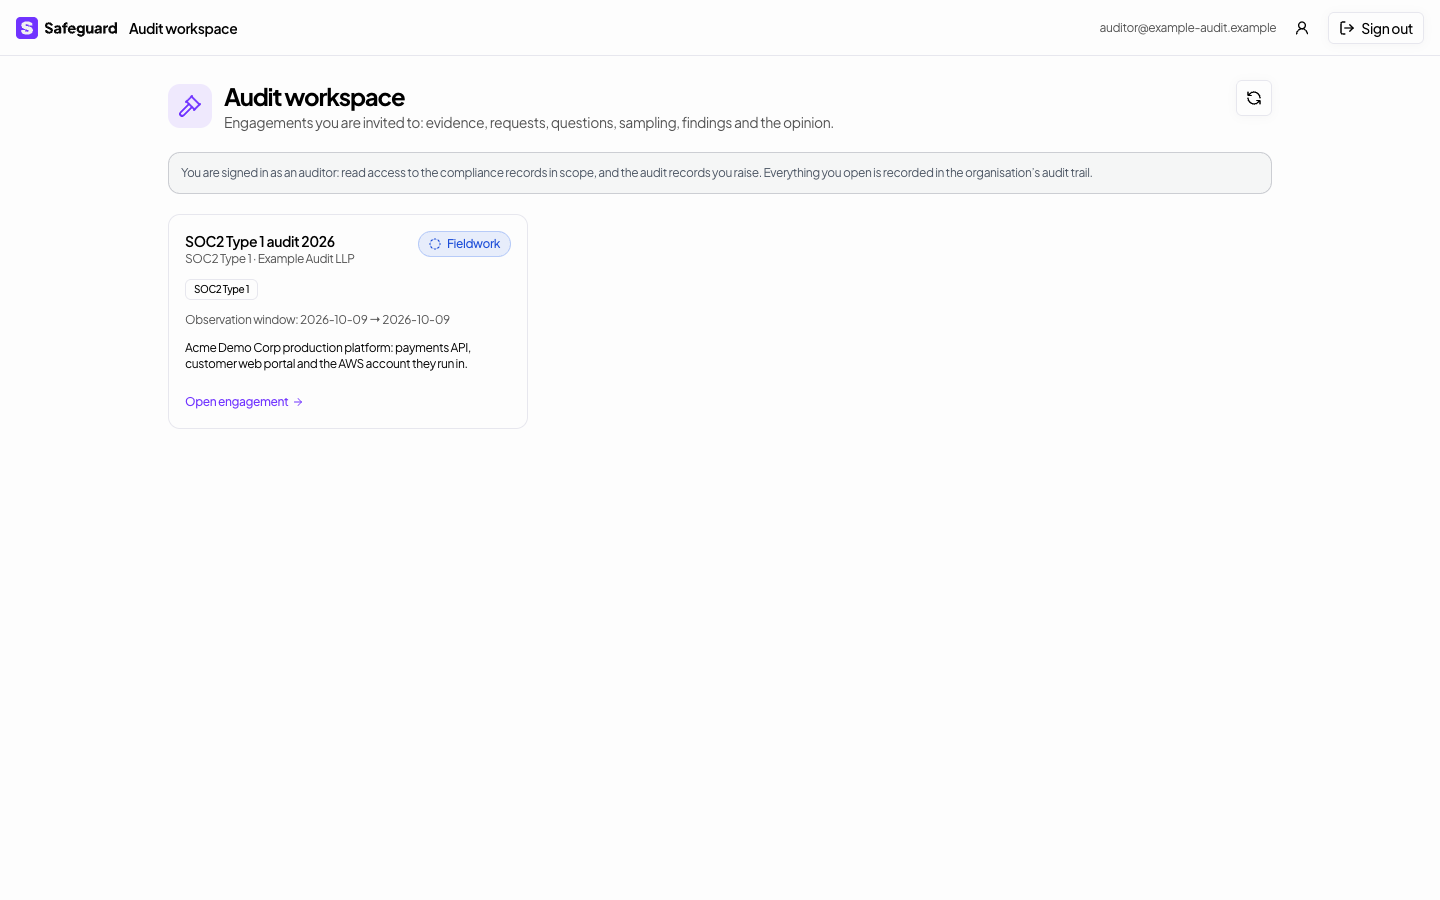
What an invited auditor sees: their engagements, evidence requests with linked evidence, accepting a request, raising a finding and asking a question.
2 min8 steps
 Interactive
Compliance
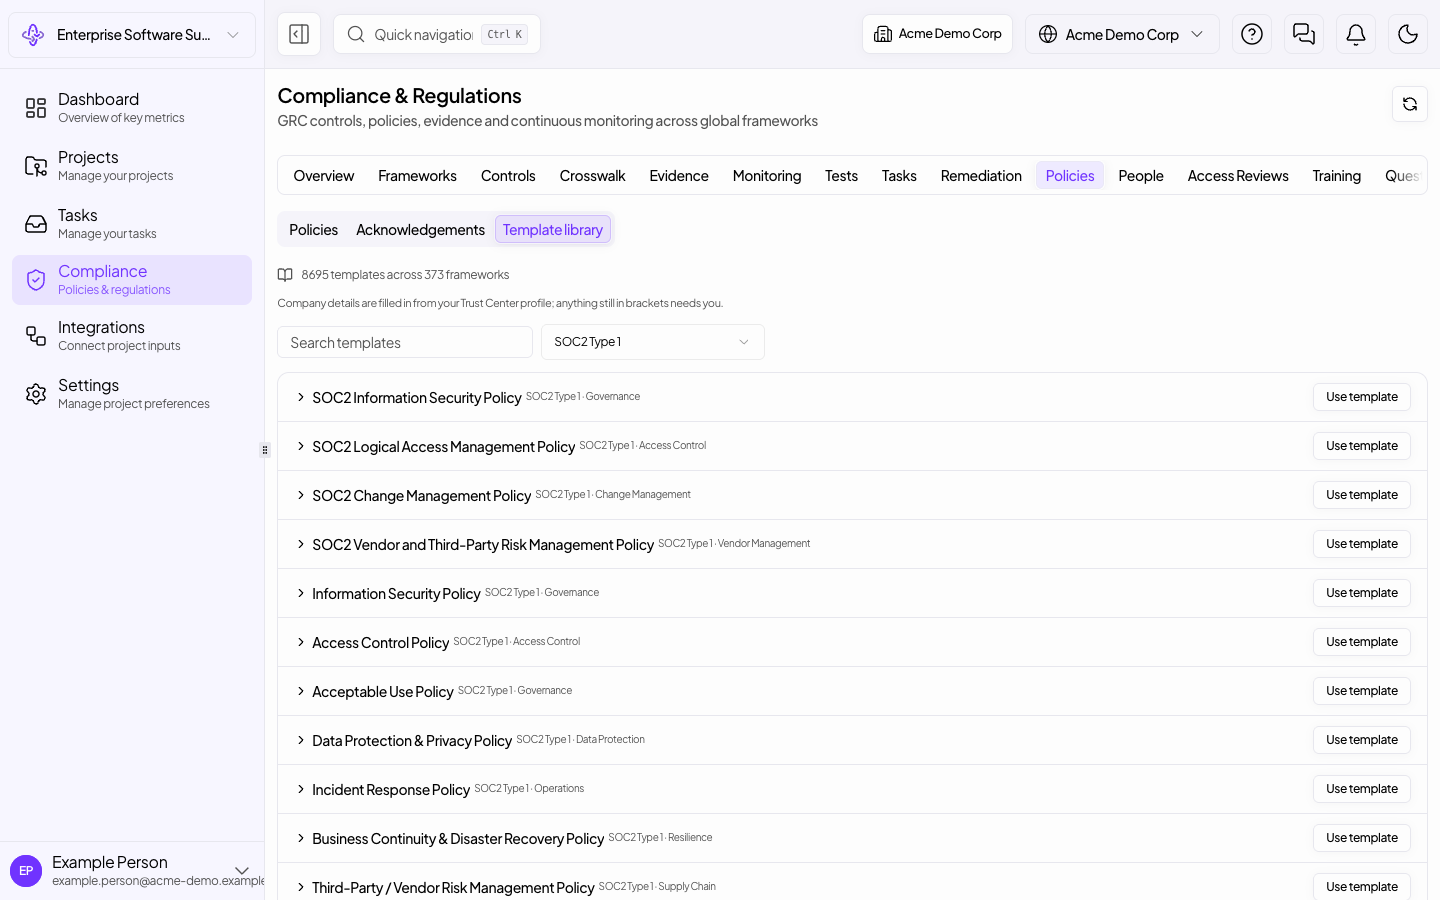
Start a policy from a SOC2 template, submit it for review, approve the version, and run an acknowledgement campaign with per-person progress.
2 min9 steps
 Interactive
Compliance
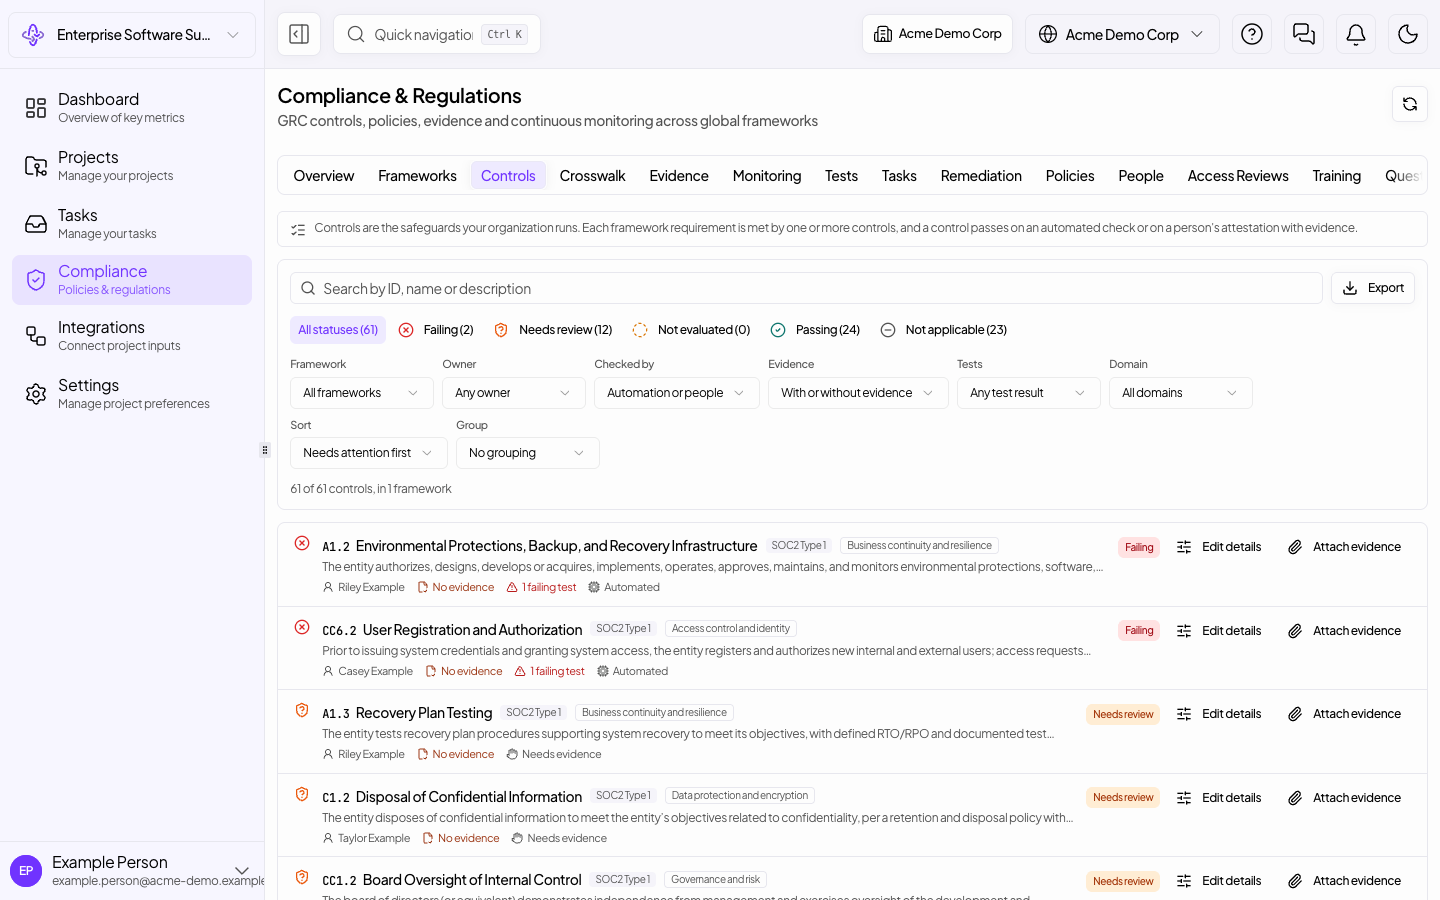
Filter the SOC2 controls that need evidence, open one, assign an owner, attach evidence and attest it, and see the control pass.
2 min9 steps
 Interactive
Compliance
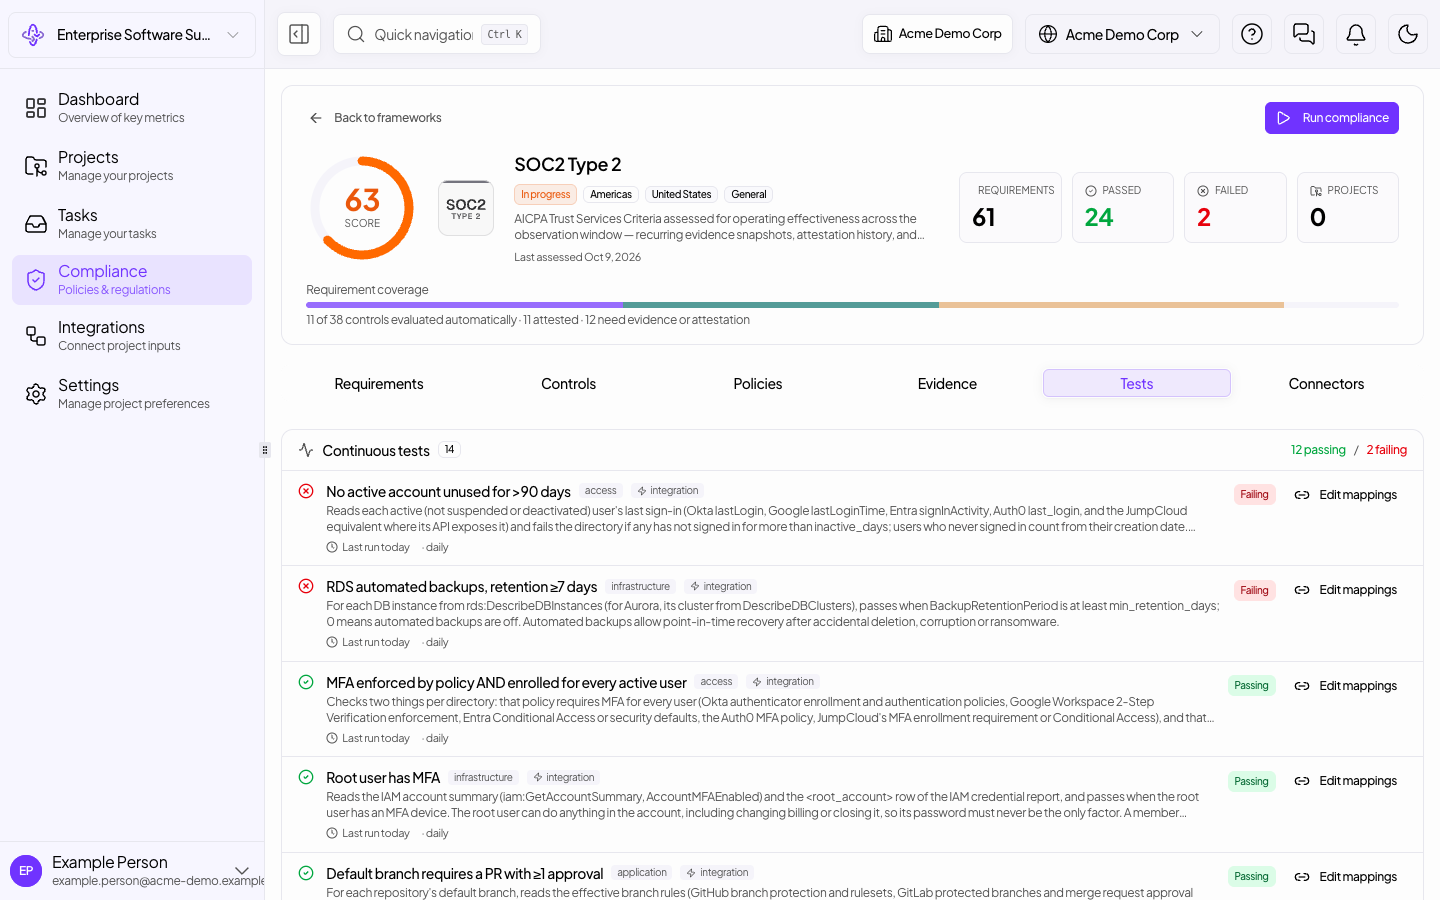
Continuous tests behind SOC2 Type 2, one test's daily history across the observation window, a failing resource and an exclusion request, evidence history and the auditor's sample.
2 min9 steps
 Interactive
Compliance
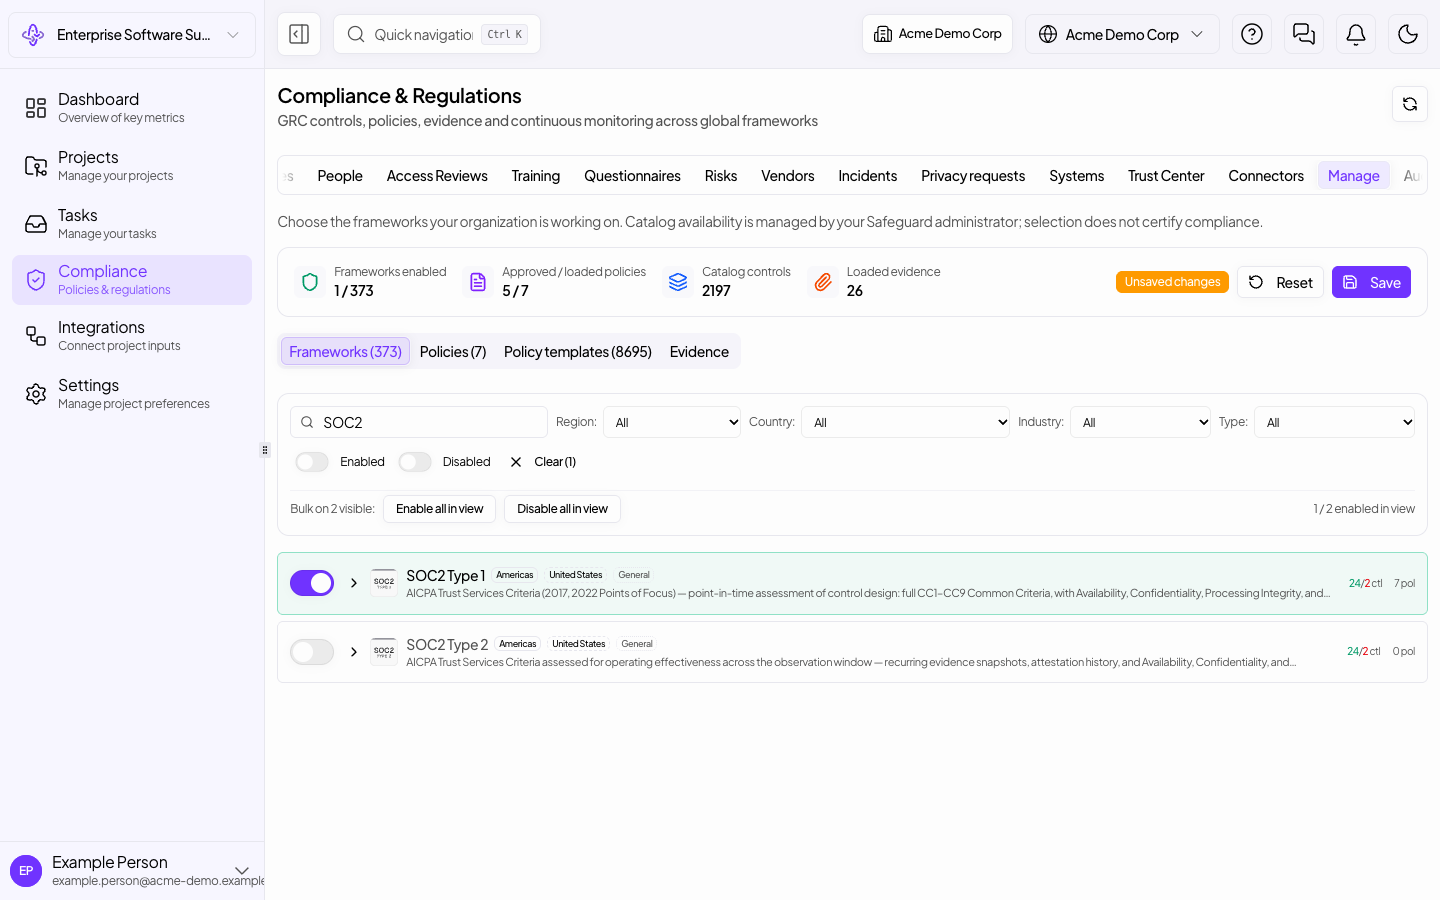
Turn on SOC2 Type 1, read the readiness score and what it rests on, open a failing control and its task, and set up the audit engagement with your auditor.
2 min9 steps
 Interactive
Academy
Safeguard Academy routes each person to what fits their job: learning paths for a first week, developers, AppSec engineers and founders heading to an audit, and role filters for developers, security, compliance, and legal and procurement teams.
1 min8 steps
 Interactive
Supply chain security
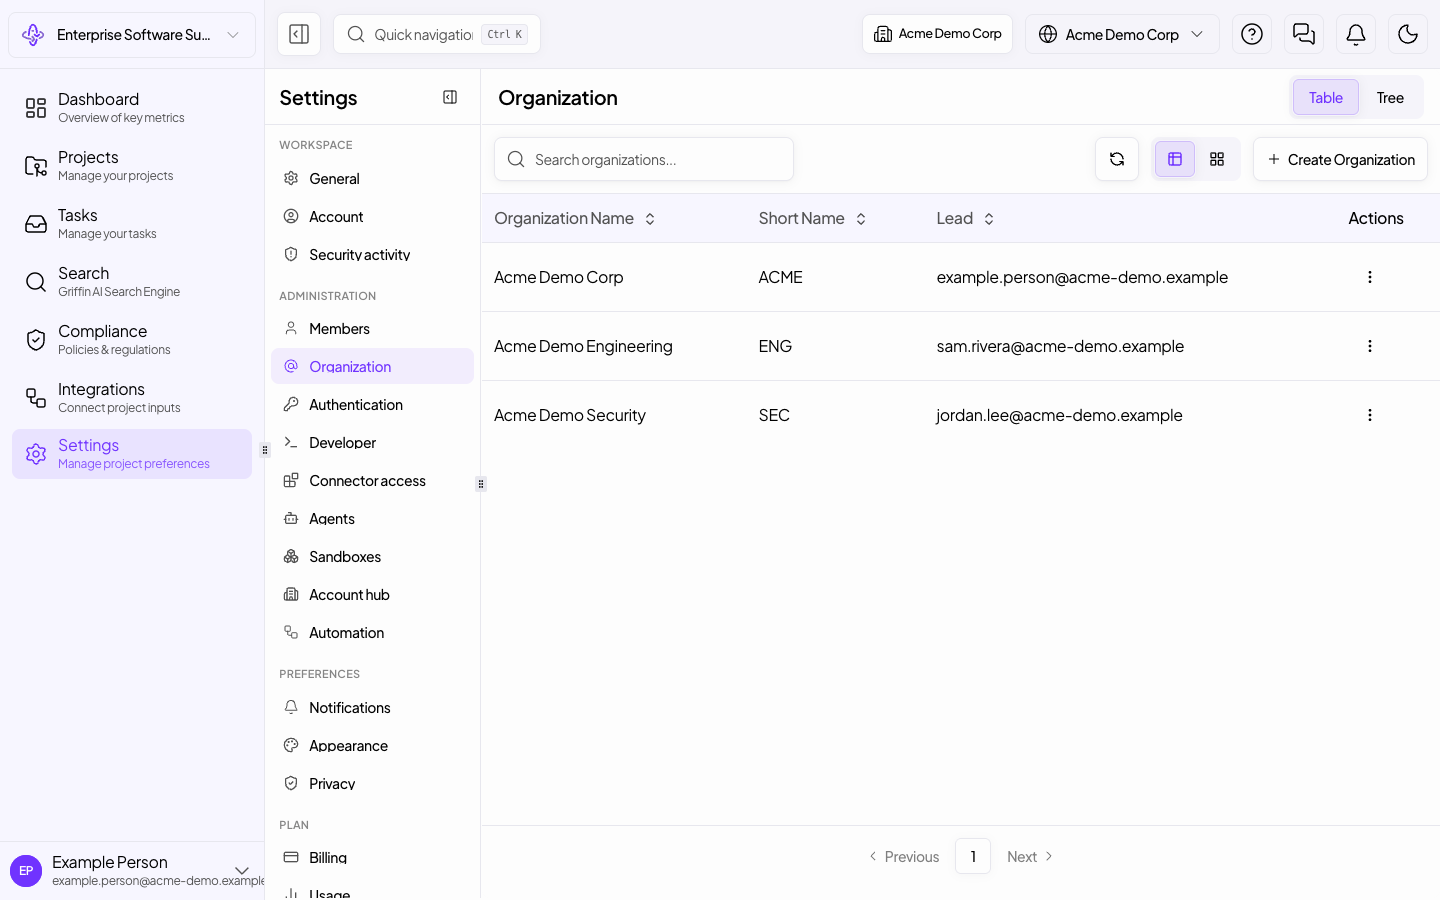
The first jobs of a workspace admin: shape the organization, give people the right roles, set up single sign-on, and decide what Safeguard may do on its own.
2 min8 steps
 Interactive
Compliance
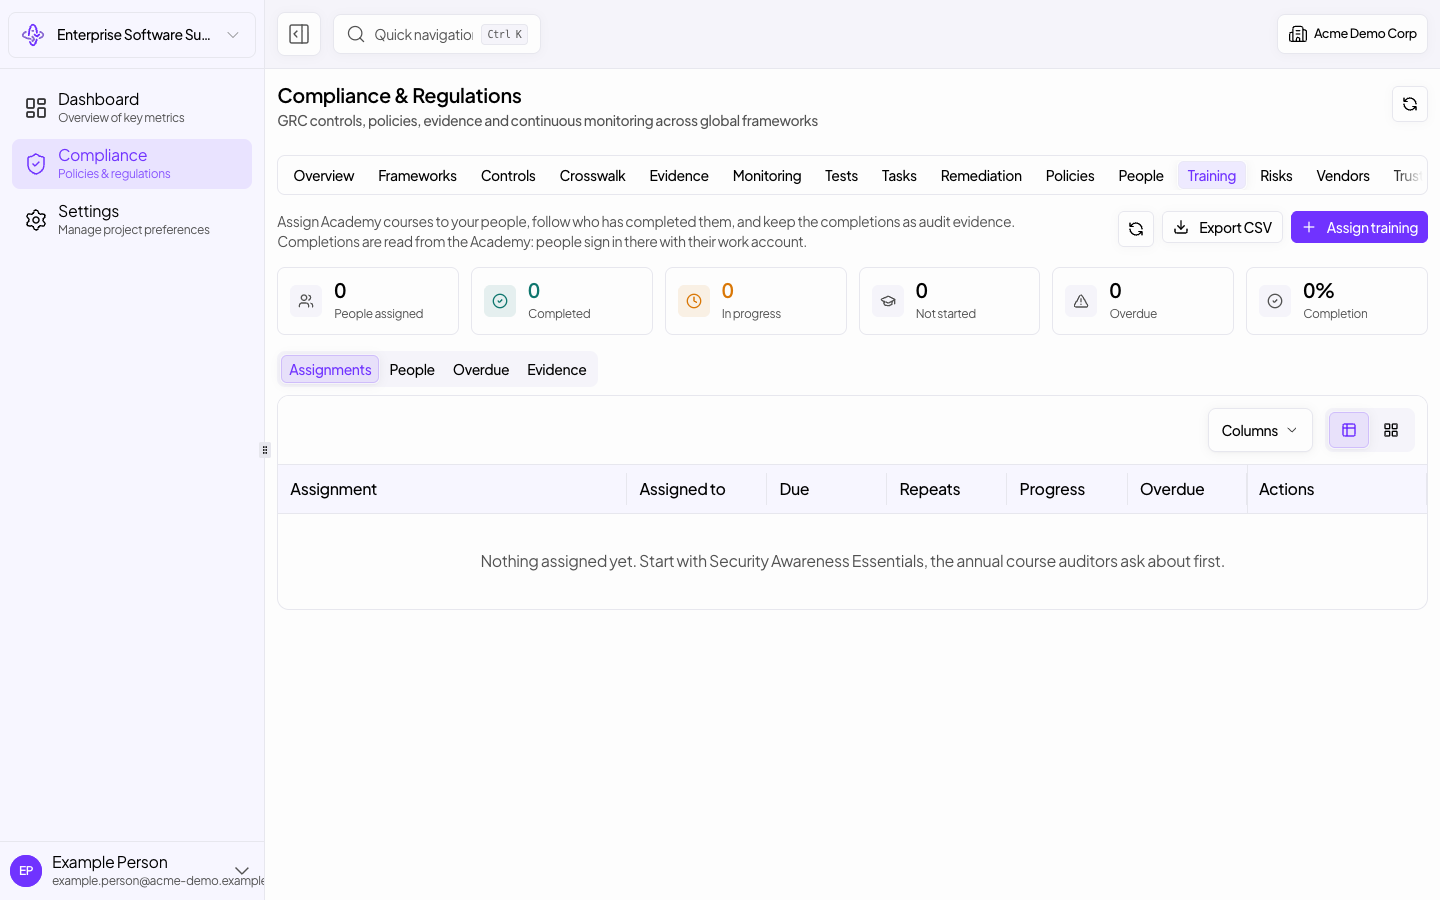
Assign Safeguard Academy security awareness courses to everyone, follow who has finished, remind the people who are late, and keep the completions as evidence for SOC2 and ISO 27001 controls.
2 min9 steps
 Interactive
Academy
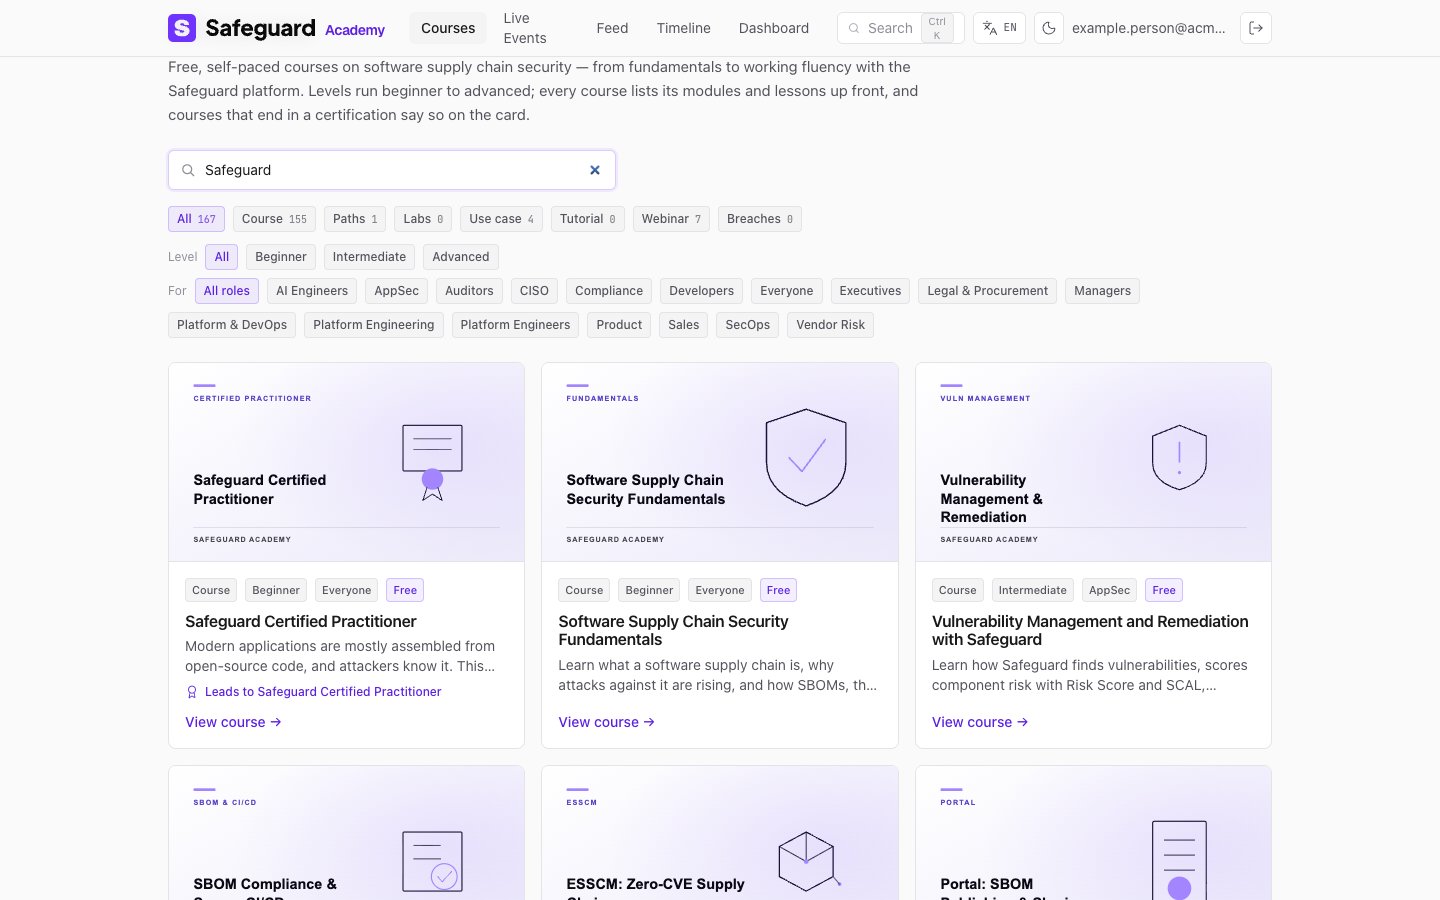
Learn Safeguard in Safeguard Academy: find the courses on using the platform, see what the Safeguard Certified Practitioner exam covers, follow your progress and company training in My learning, and share a certificate anyone can verify.
2 min8 steps
 Interactive
Supply chain security
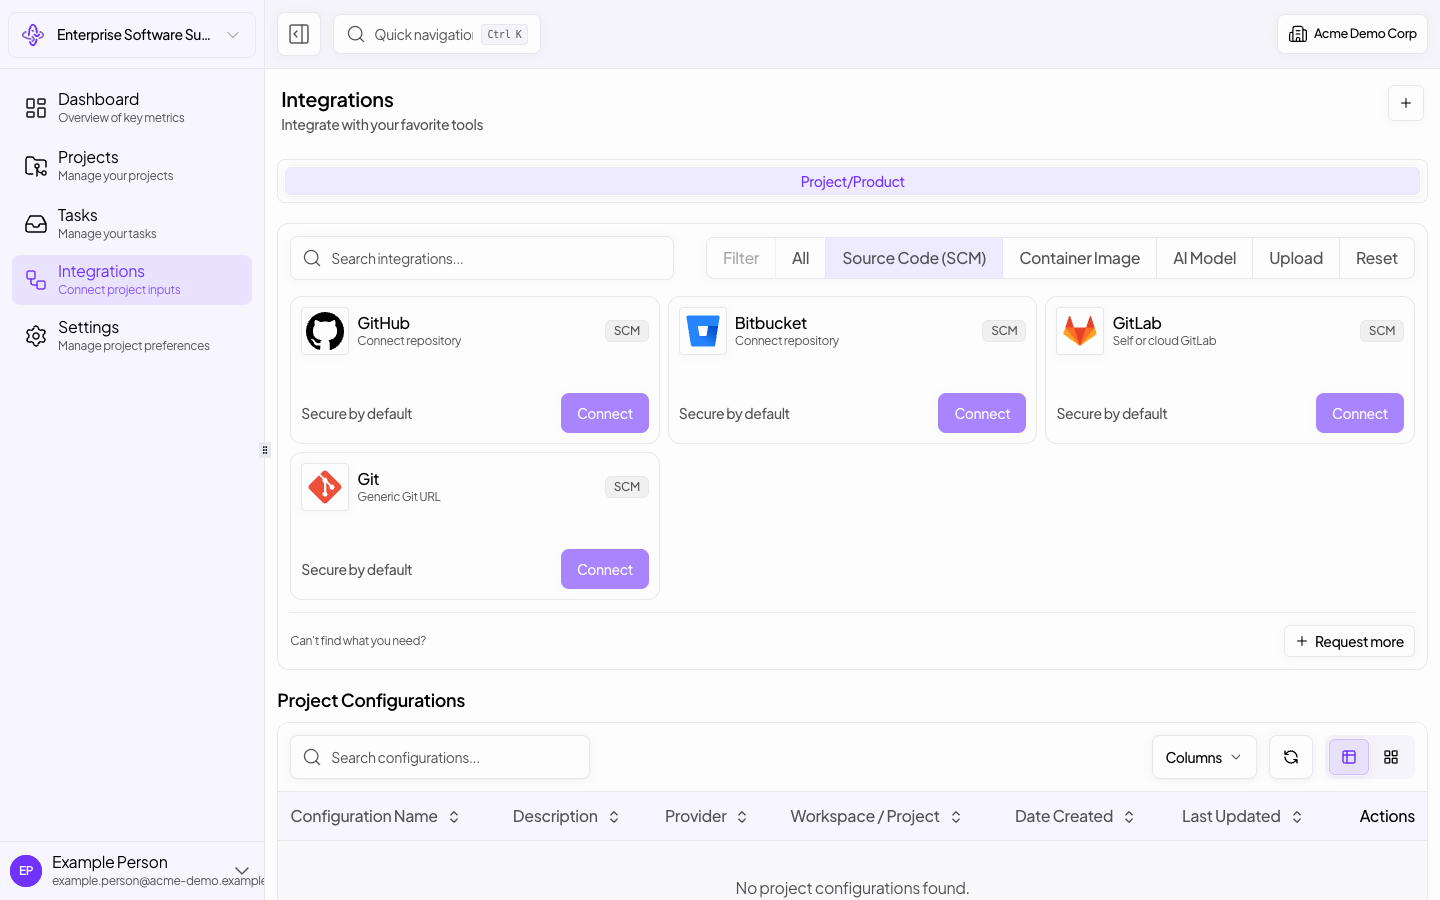
Your first session in a new workspace: connect GitHub, choose the repos and start the first scan, find the finding that matters, and open the pull request that fixes it.
2 min9 steps
 Interactive
Supply chain security
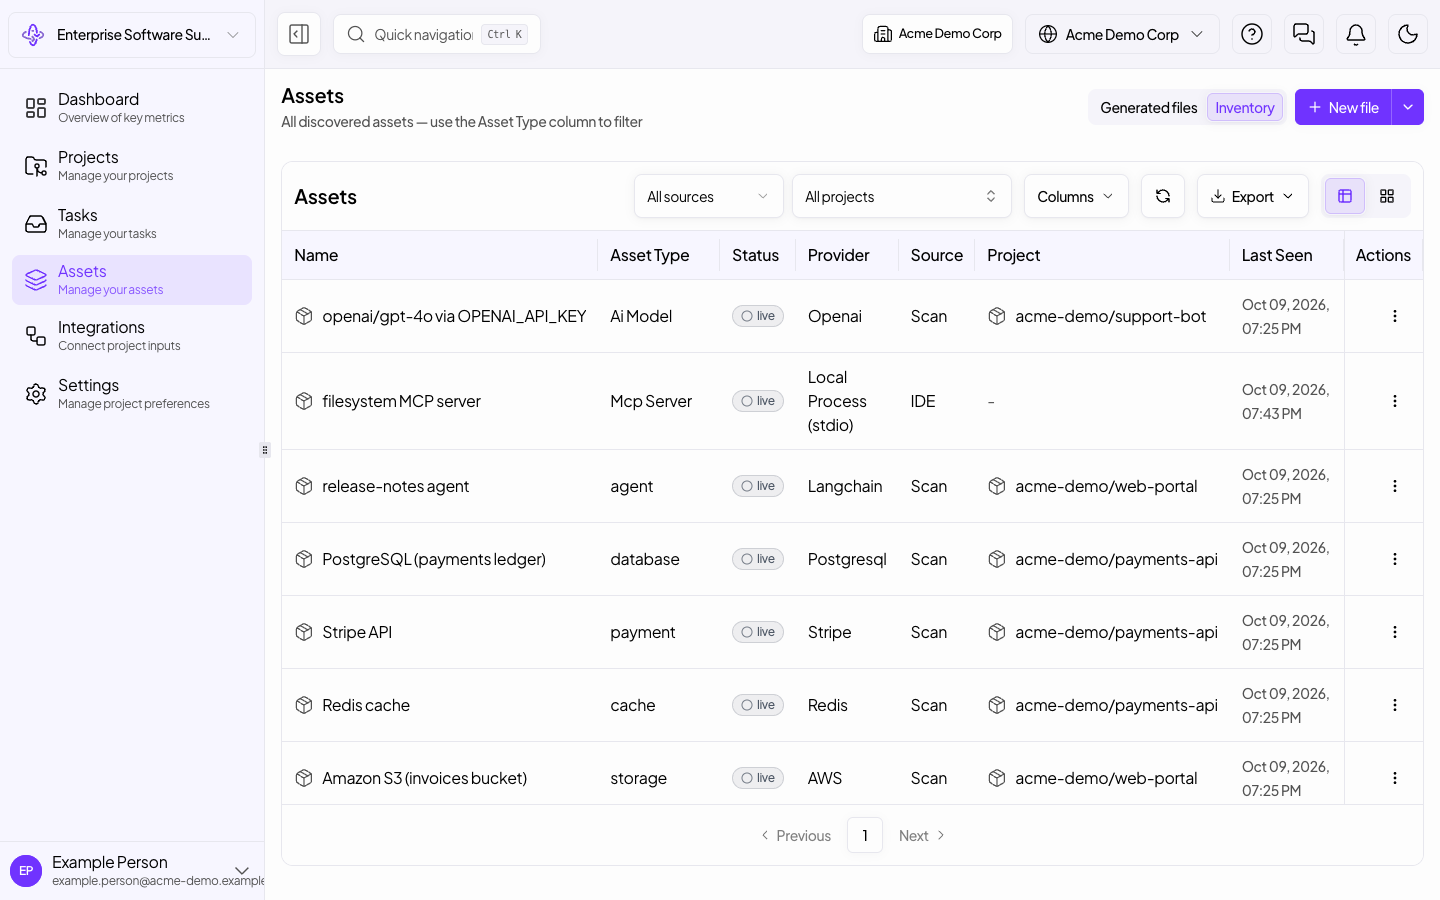
See the assets found by repository and container scans and by IDE extensions (AI models, MCP servers, agents, databases, third-party services) and block, suspend or quarantine one.
2 min8 steps
 Interactive
Supply chain security
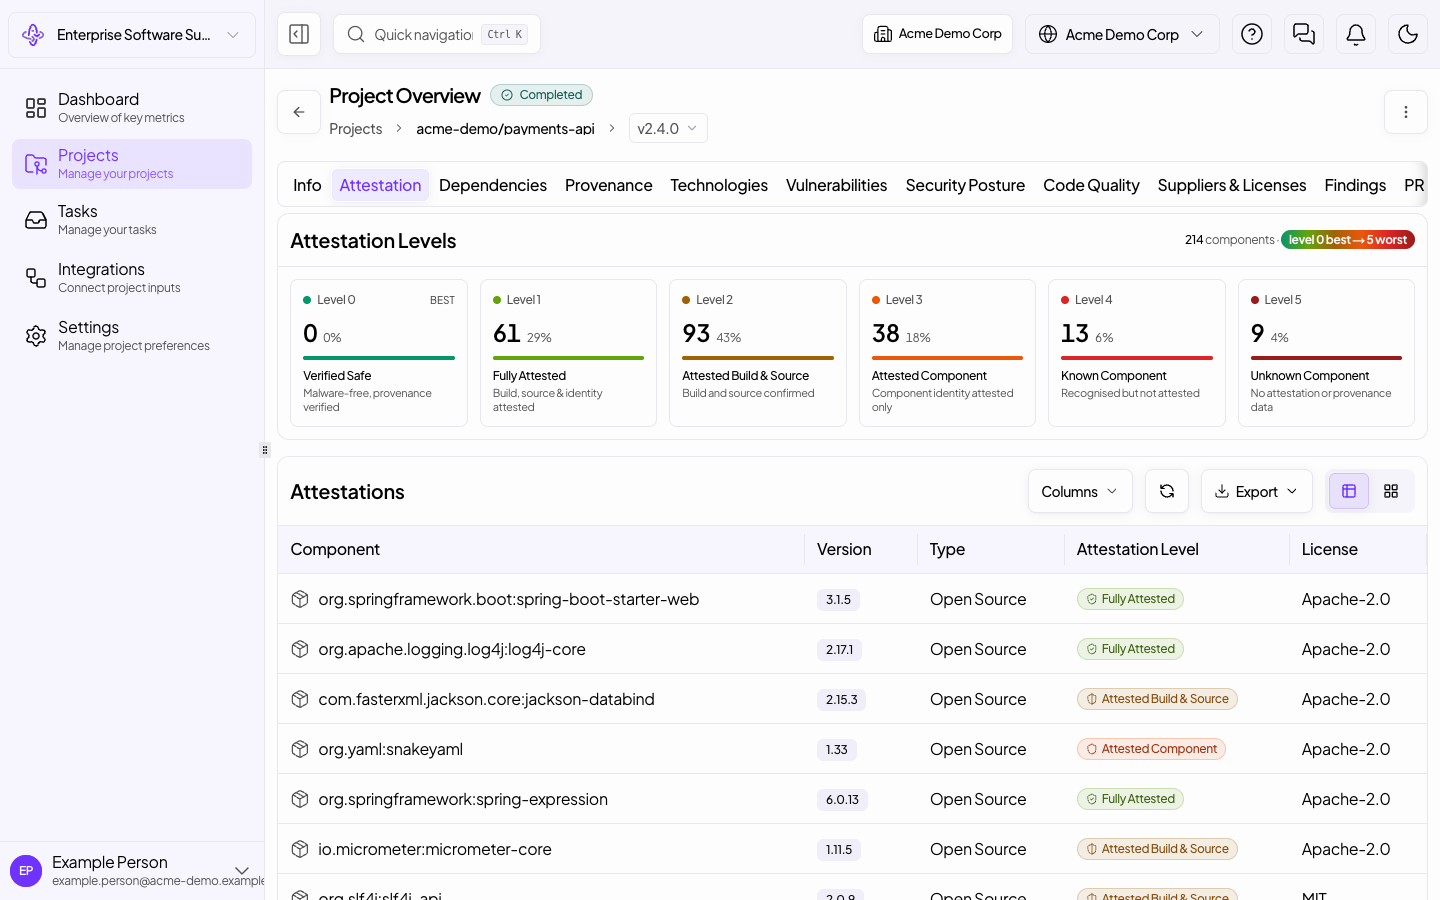
See each component's Safeguard Component Attestation Level (SCAL), what each level means, the commit provenance of your dependencies, and the SLSA v1.0 provenance document.
1 min7 steps
 Interactive
Supply chain security
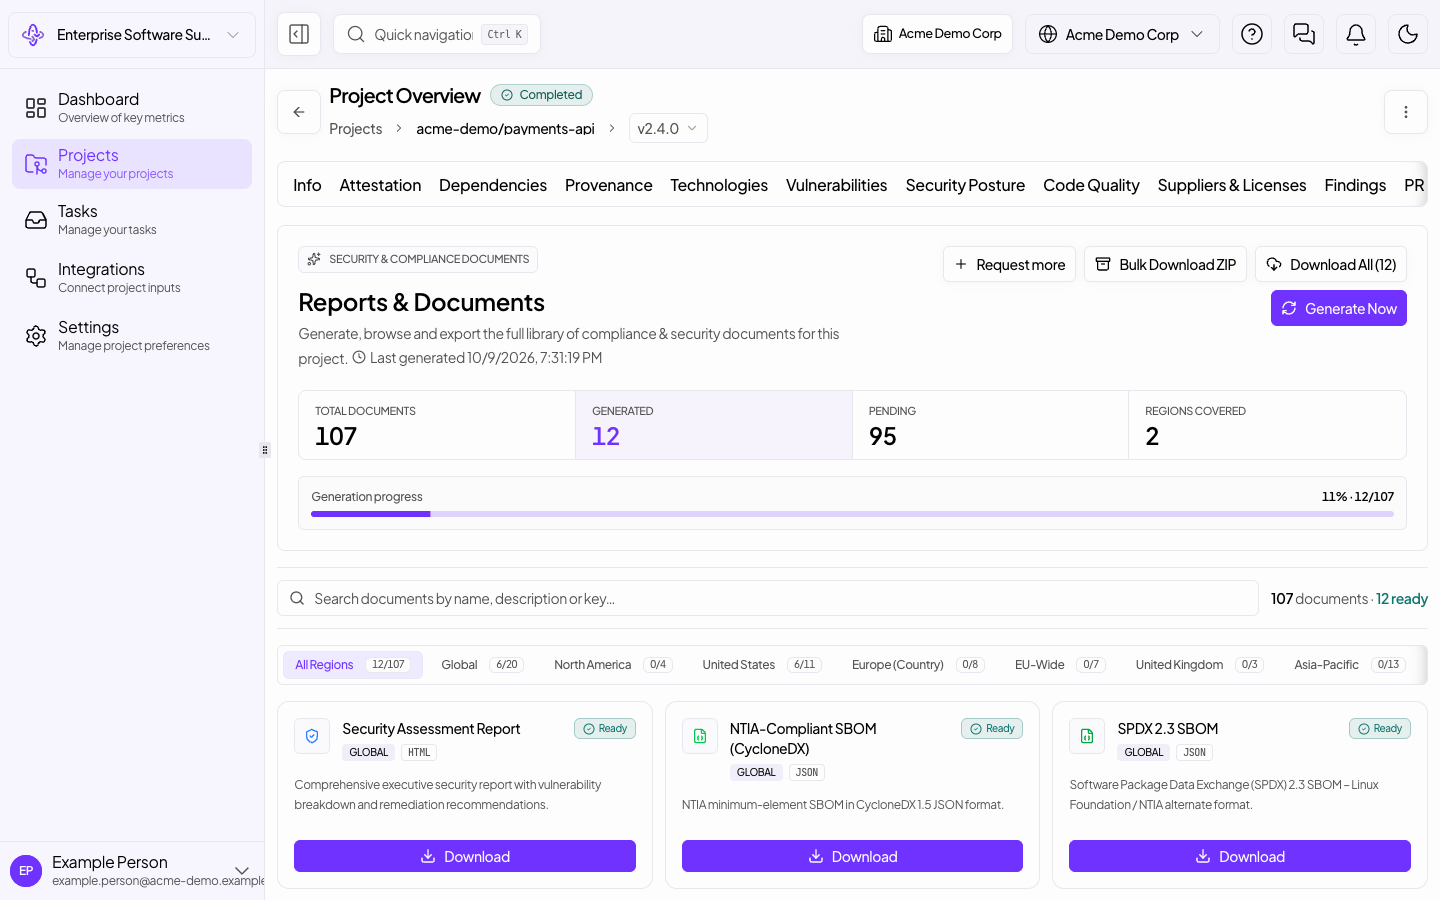
Download the EO 14028 report, NIST SSDF report and FedRAMP-format SBOM generated for a project, and publish the product with a named self-attestation signer.
1 min7 steps
 Interactive
Tprm
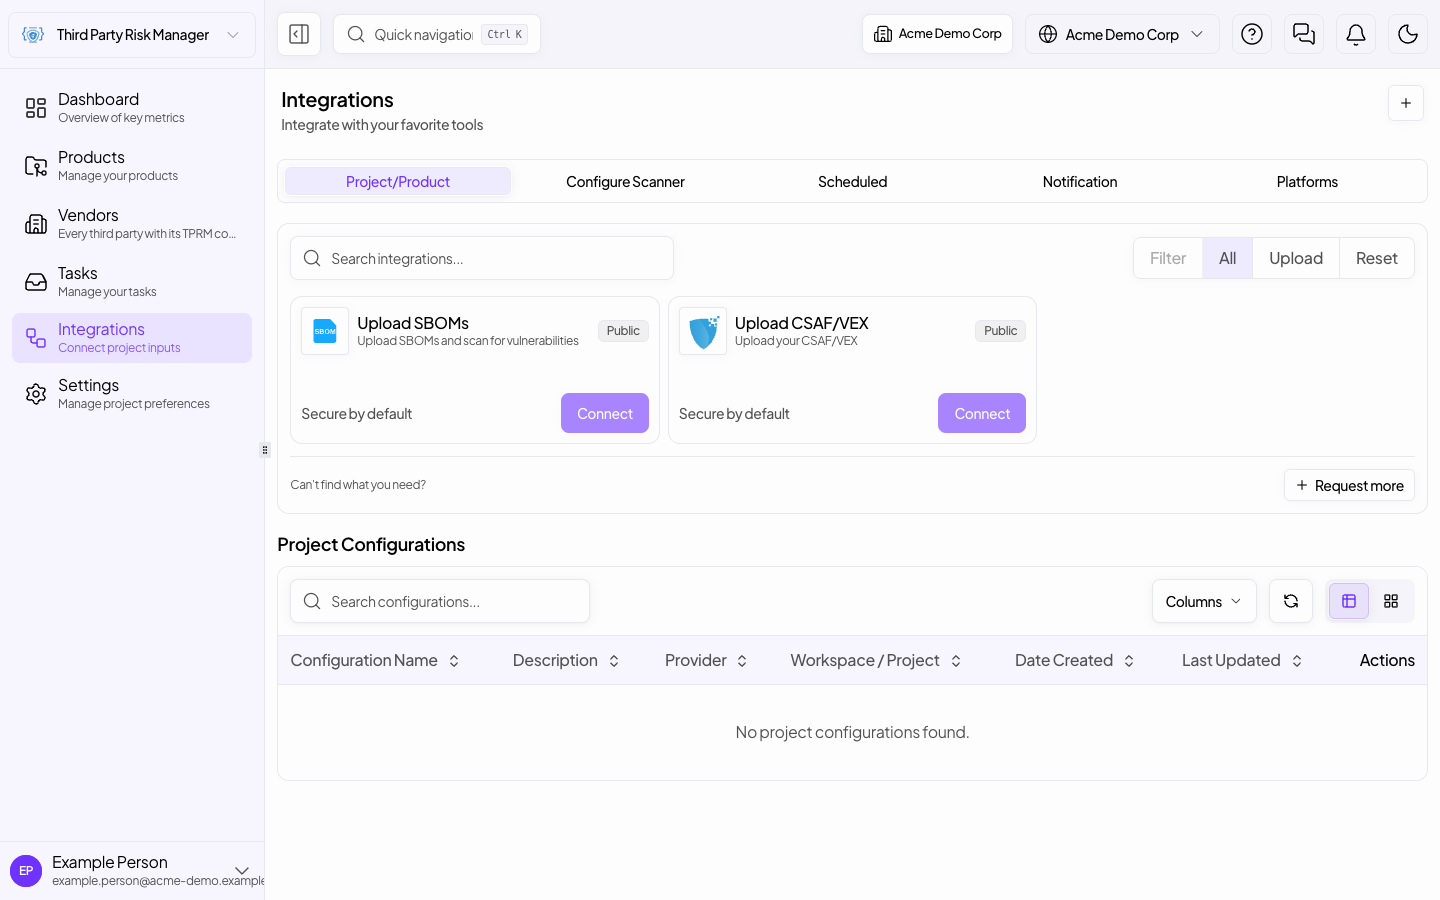
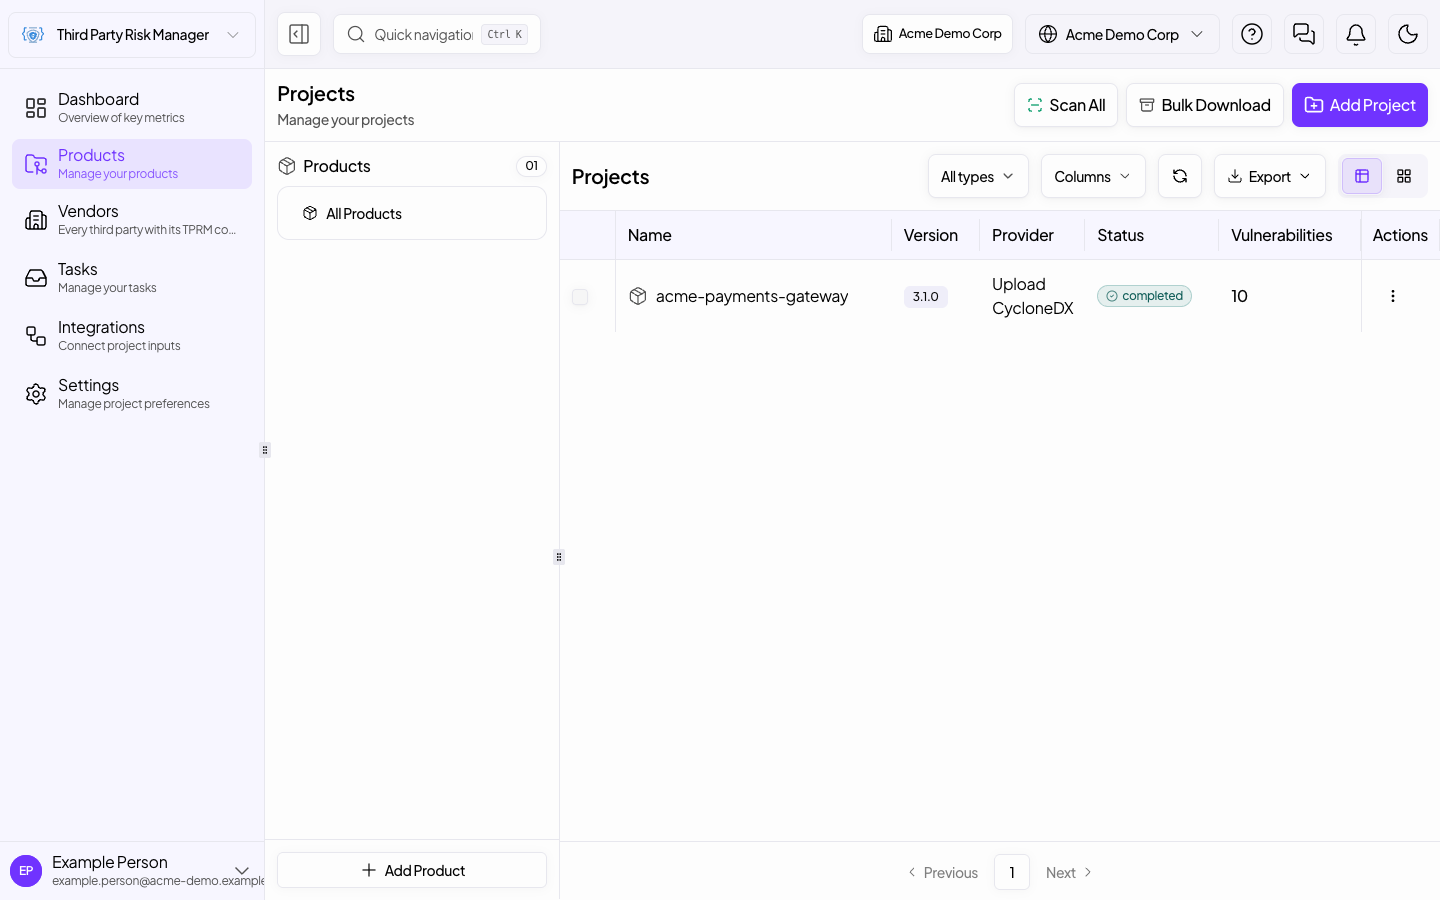
Upload a supplier's CSAF, CycloneDX or OpenVEX document, and record a vulnerability's VEX state (Not Affected, Affected, Fixed, Under Investigation) with a justification.
2 min9 steps
 Interactive
Tprm
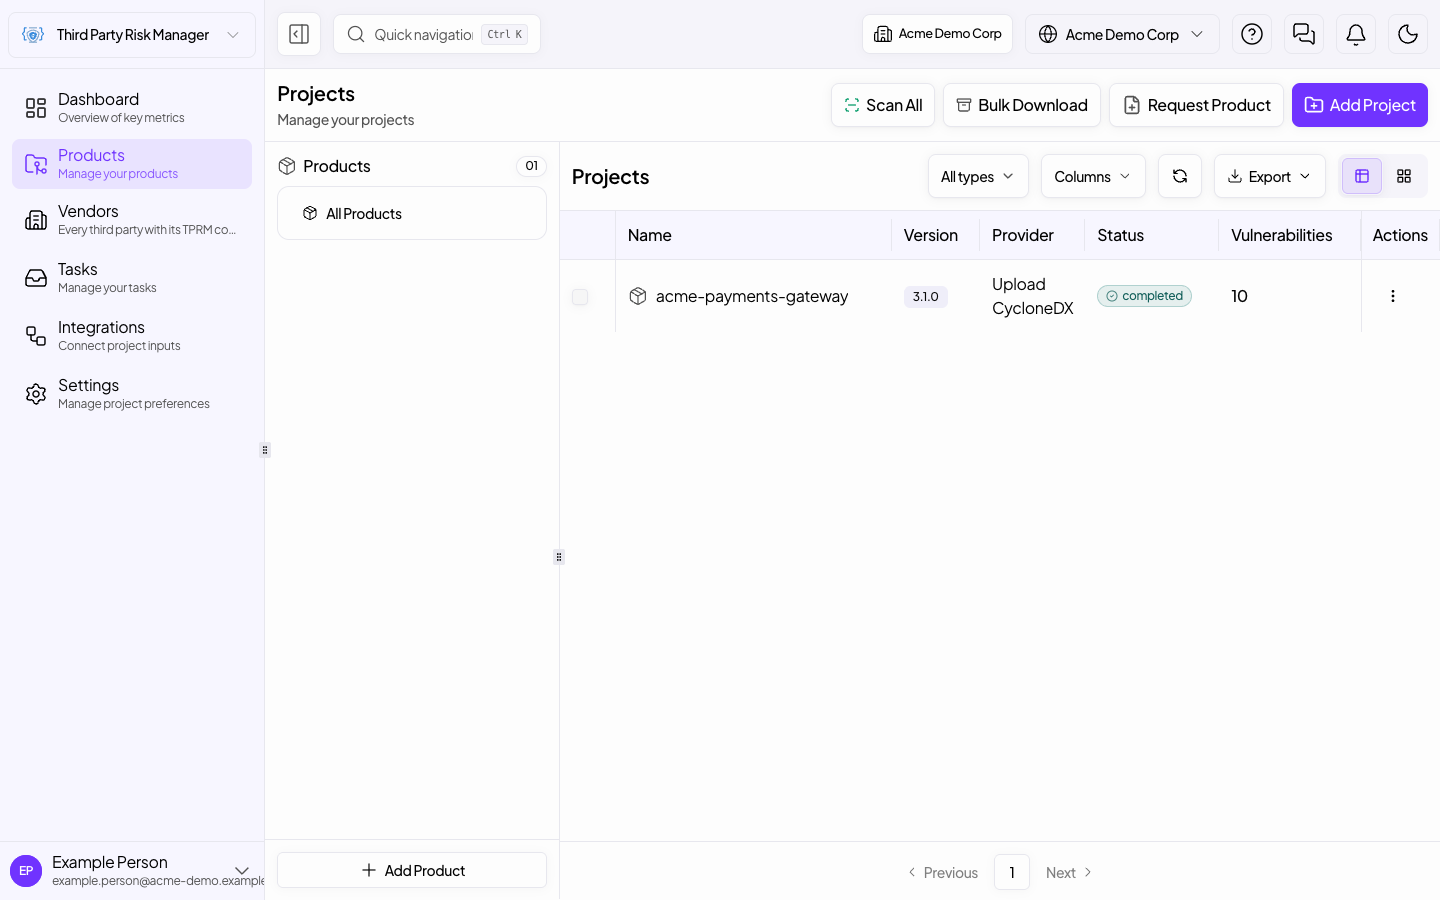
Rescan a supplier's SBOM on a schedule, get a notification when the scan finishes, and see the newly matched vulnerability.
2 min9 steps
 Interactive
Tprm
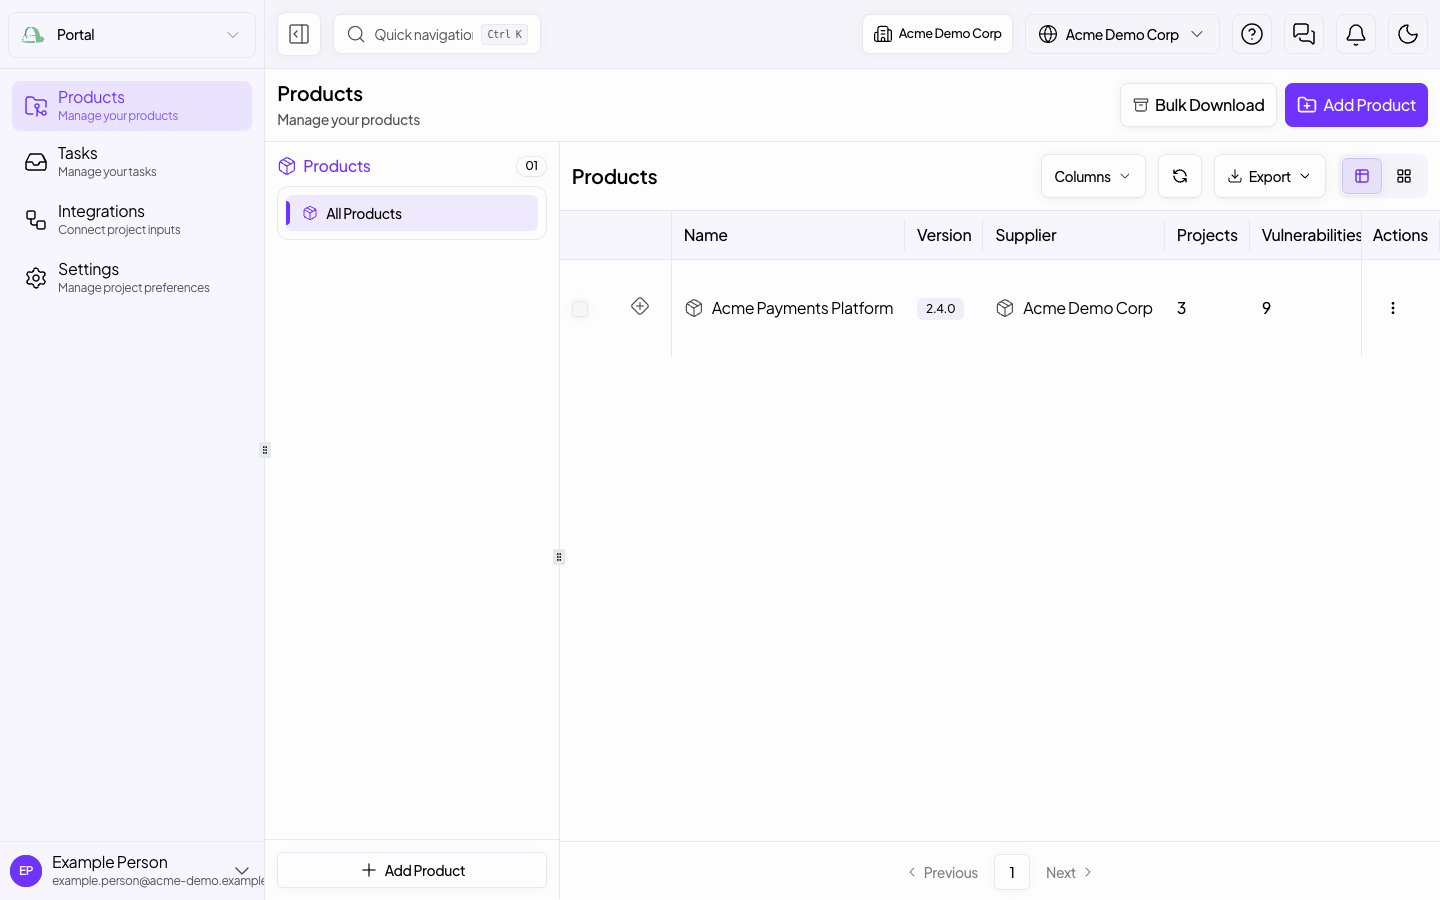
From Third Party Risk Manager, request a product and its SBOMs from a distributor, reseller or customer, and see the request arrive as a task in the supplier's Portal.
2 min9 steps
 Interactive
Portal
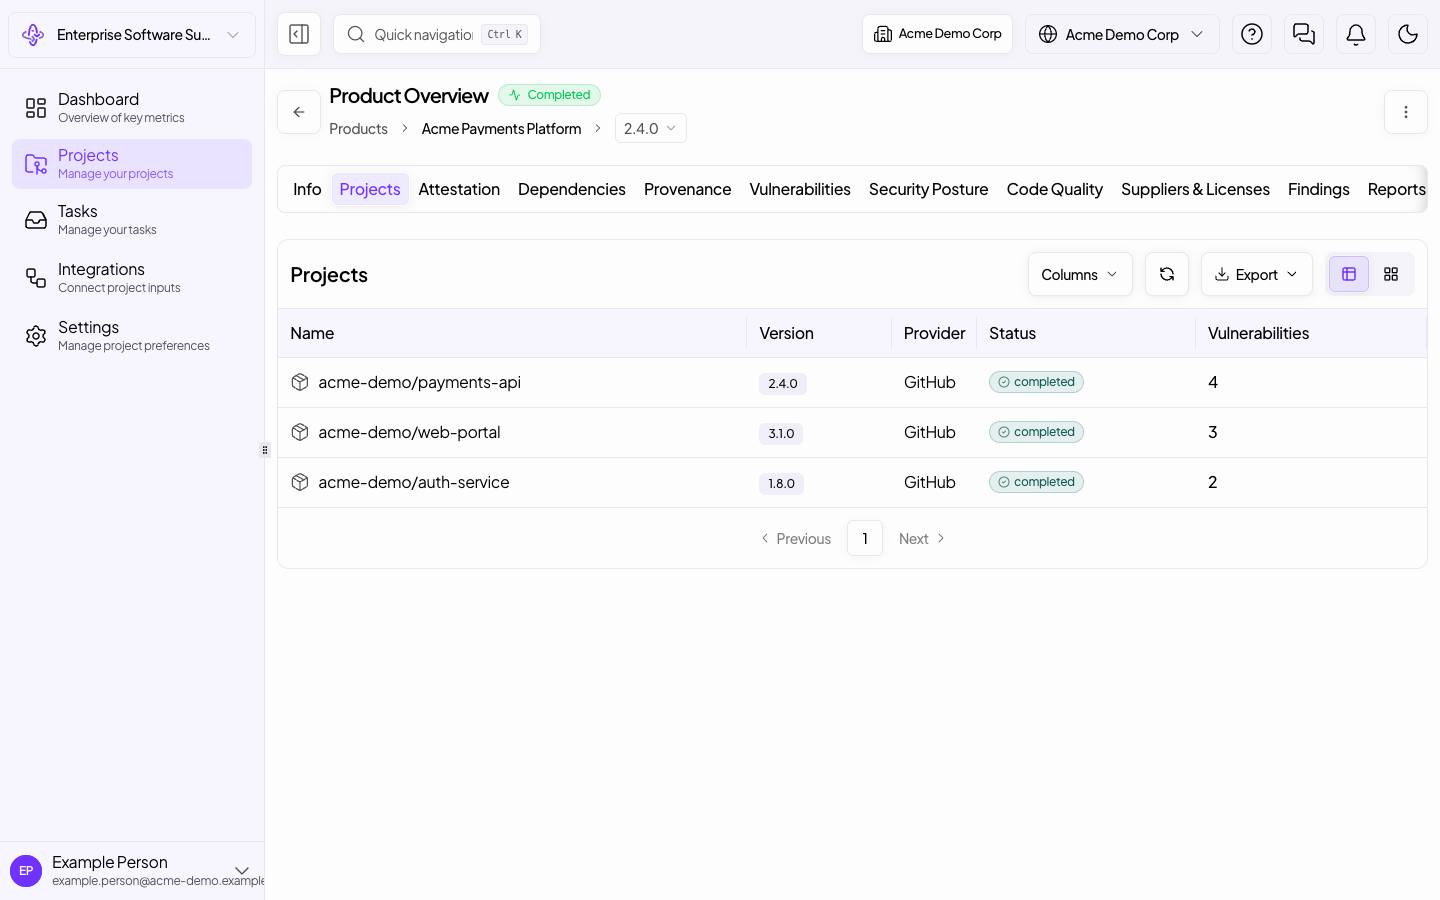
From Portal, share a published product with the distributors, resellers and customers in your company directory, choosing NTIA-compliant, enriched or custom SBOM detail.
1 min7 steps
 Interactive
Portal
Generate a CSAF 2.0 VEX for a product, then publish the product with its SBOMs from Enterprise SSCA to Portal as an immutable copy, signed off by a named person.
2 min9 steps
 Interactive
Supply chain security
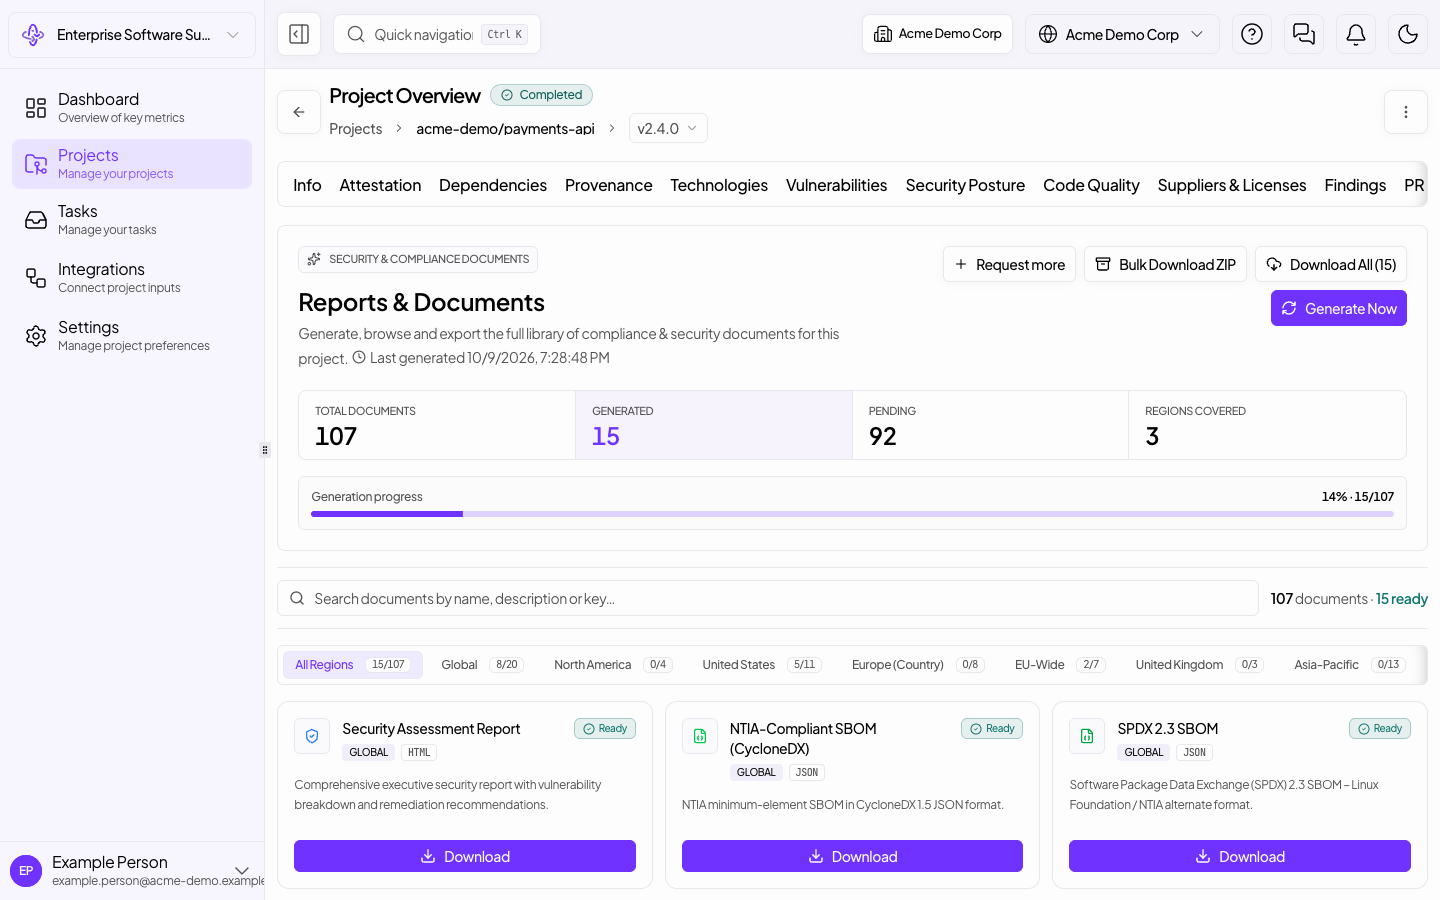
Download an SBOM in the format each reader needs (NTIA CycloneDX, SPDX 2.3, enriched CycloneDX, FedRAMP, BSI TR-03183 and more), bundle documents as a ZIP, or export any table.
1 min7 steps
 Interactive
Supply chain security
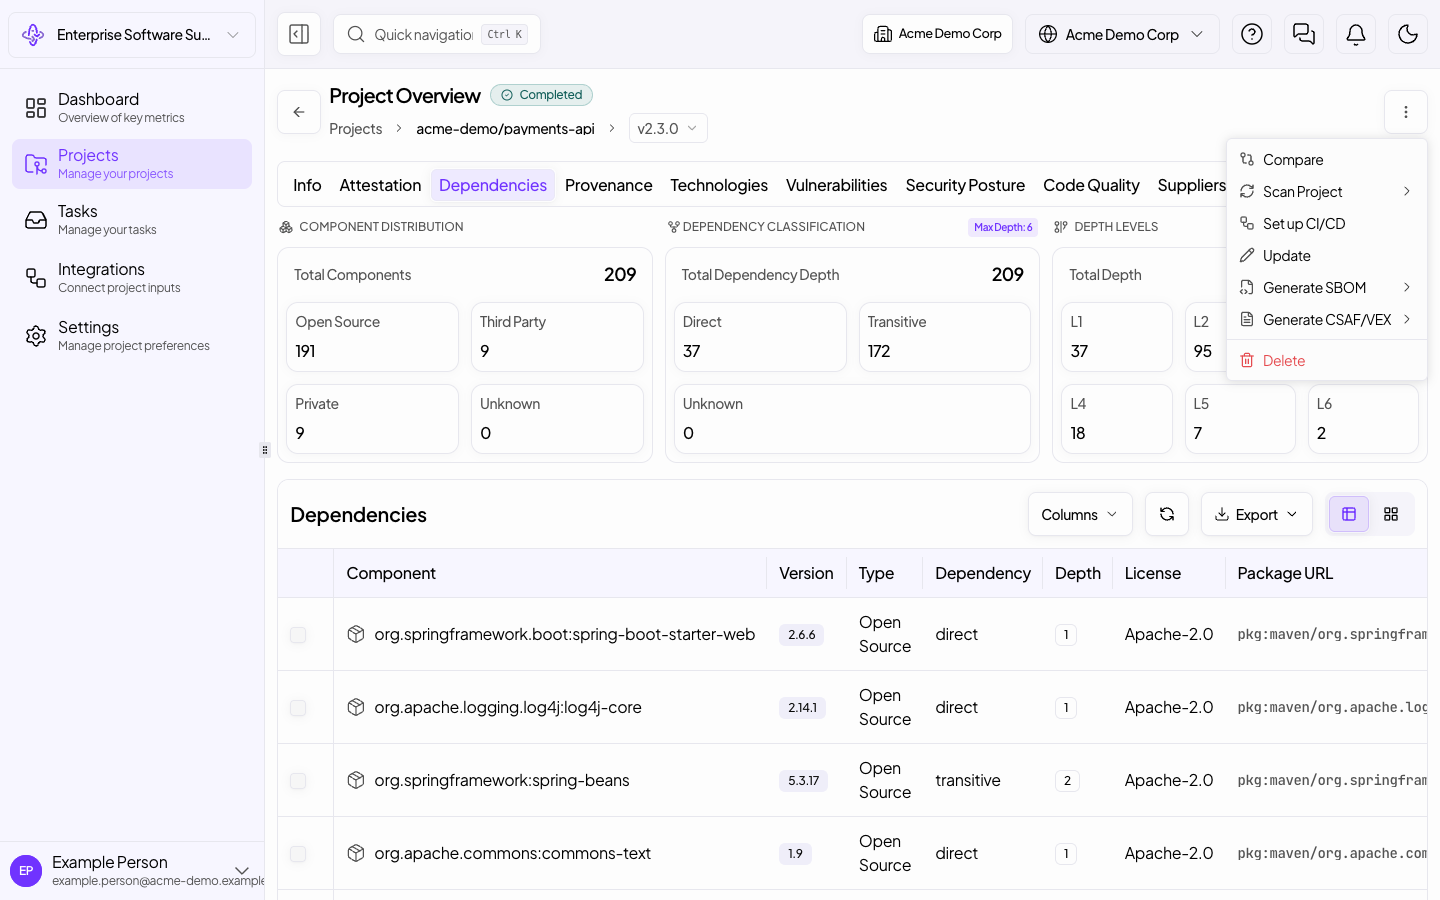
Compare two versions of a project side by side: vulnerabilities fixed, introduced and shared, risk score, and component, licence and attestation changes.
1 min7 steps
 Interactive
Tprm
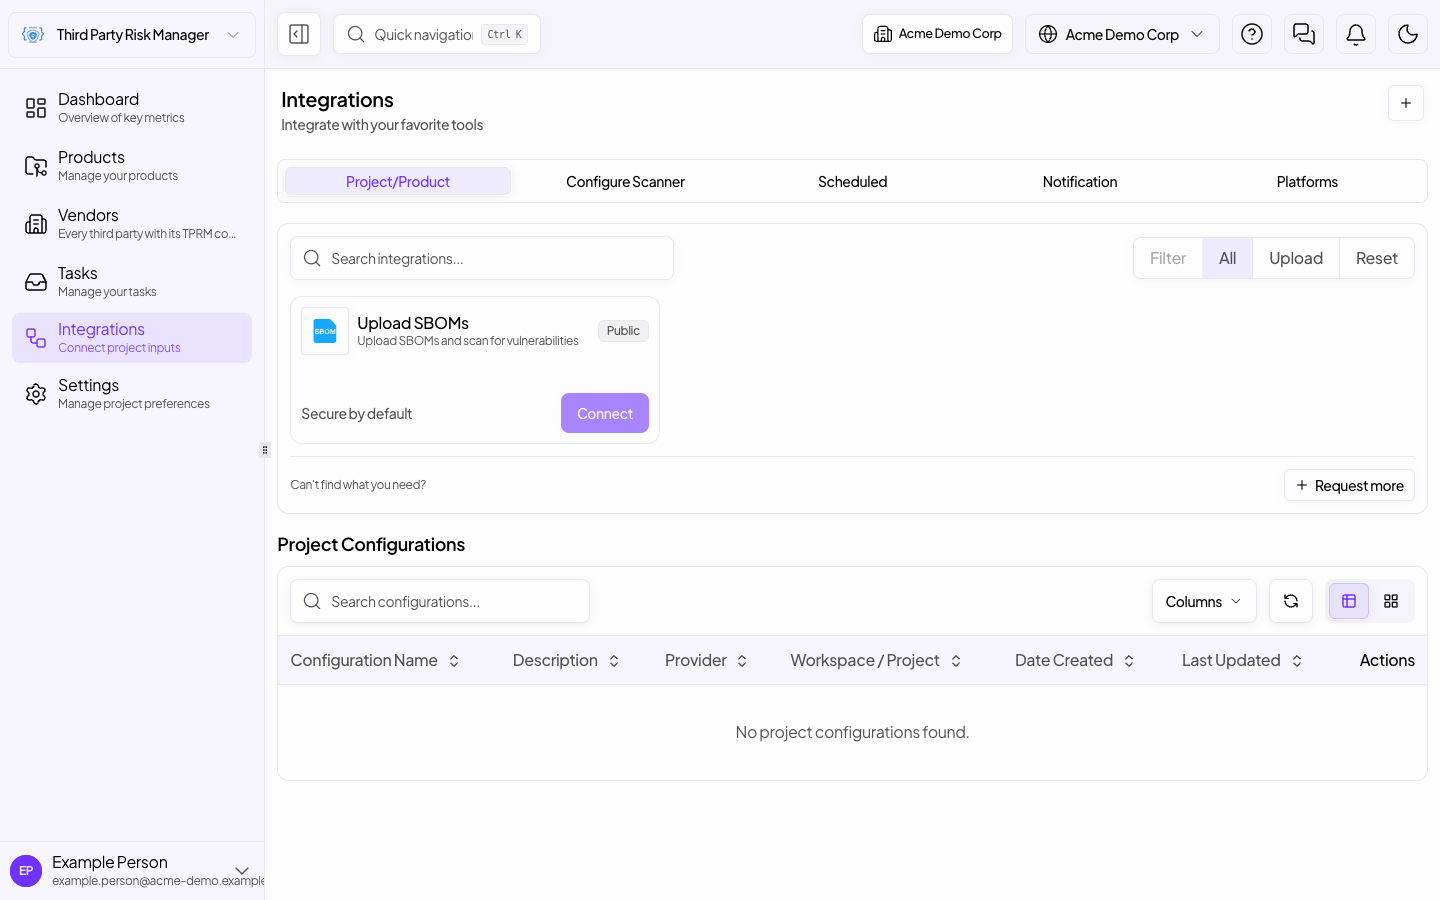
Upload an SBOM a supplier sent you, tie it to that vendor, and see its components and the known vulnerabilities in them.
2 min9 steps
 Interactive
Supply chain security
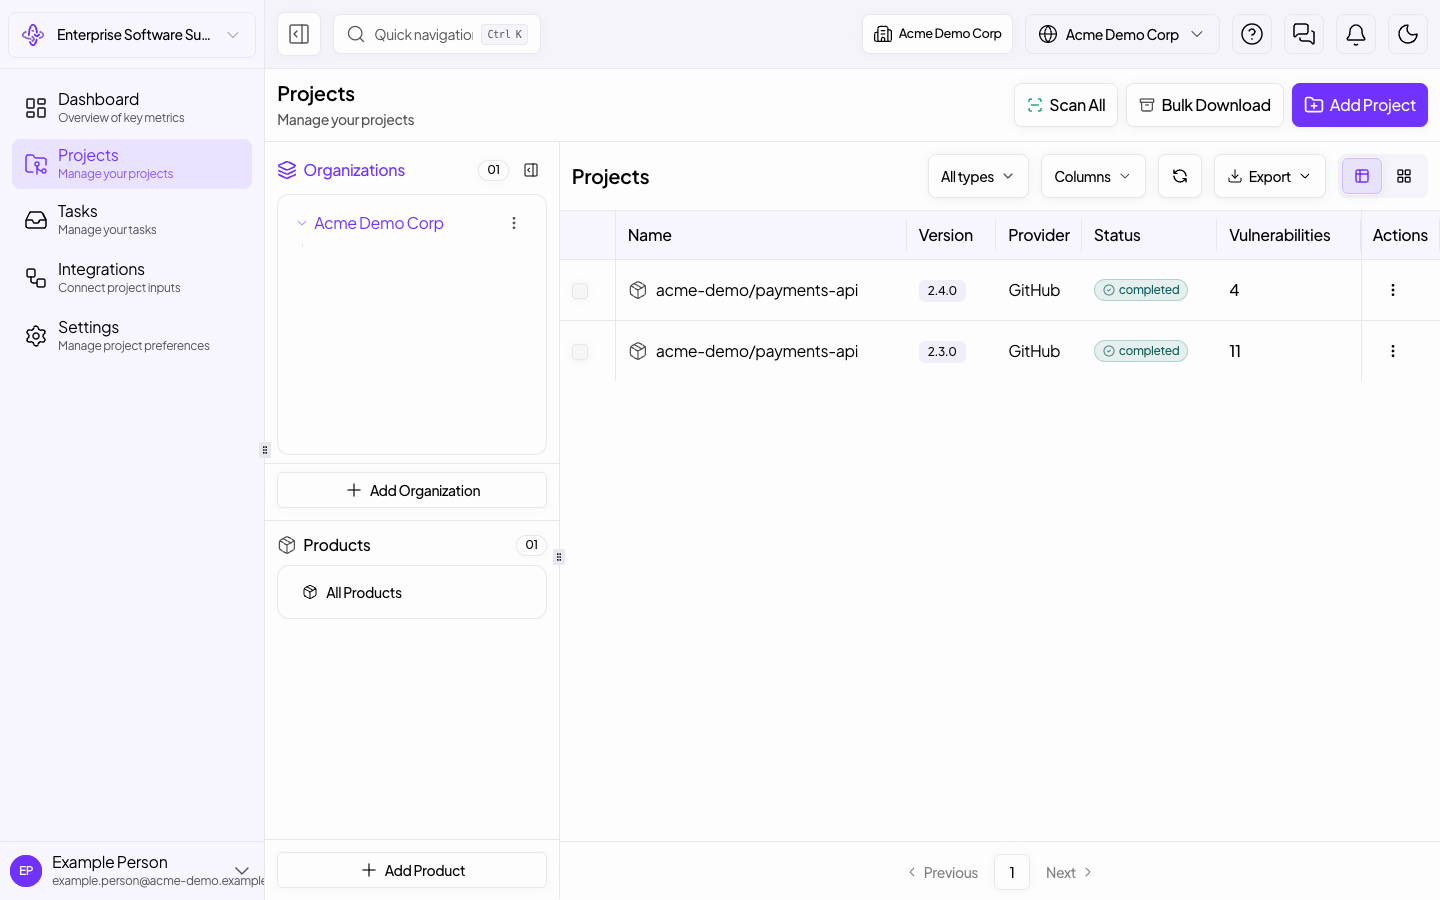
Generate a CycloneDX, SPDX or SWID SBOM for a scanned project from its dependency inventory, and pick it up from your notifications when it is ready.
1 min7 steps
 Interactive
Supply chain security
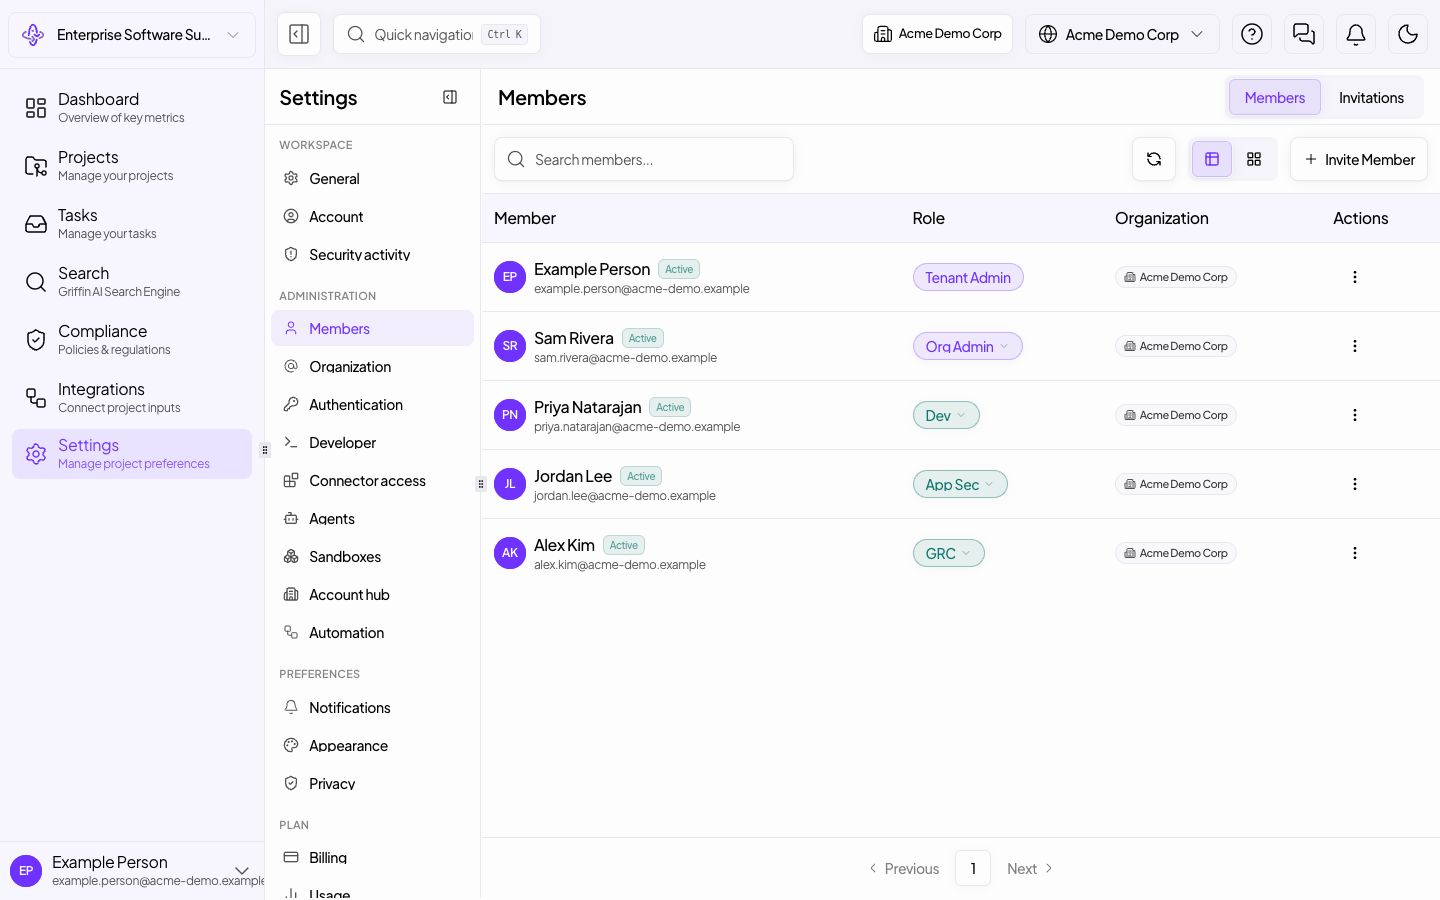
Invite a teammate with their organizations and products, set roles from the members list, and add a SAML identity provider for single sign-on.
2 min9 steps
 Interactive
Supply chain security
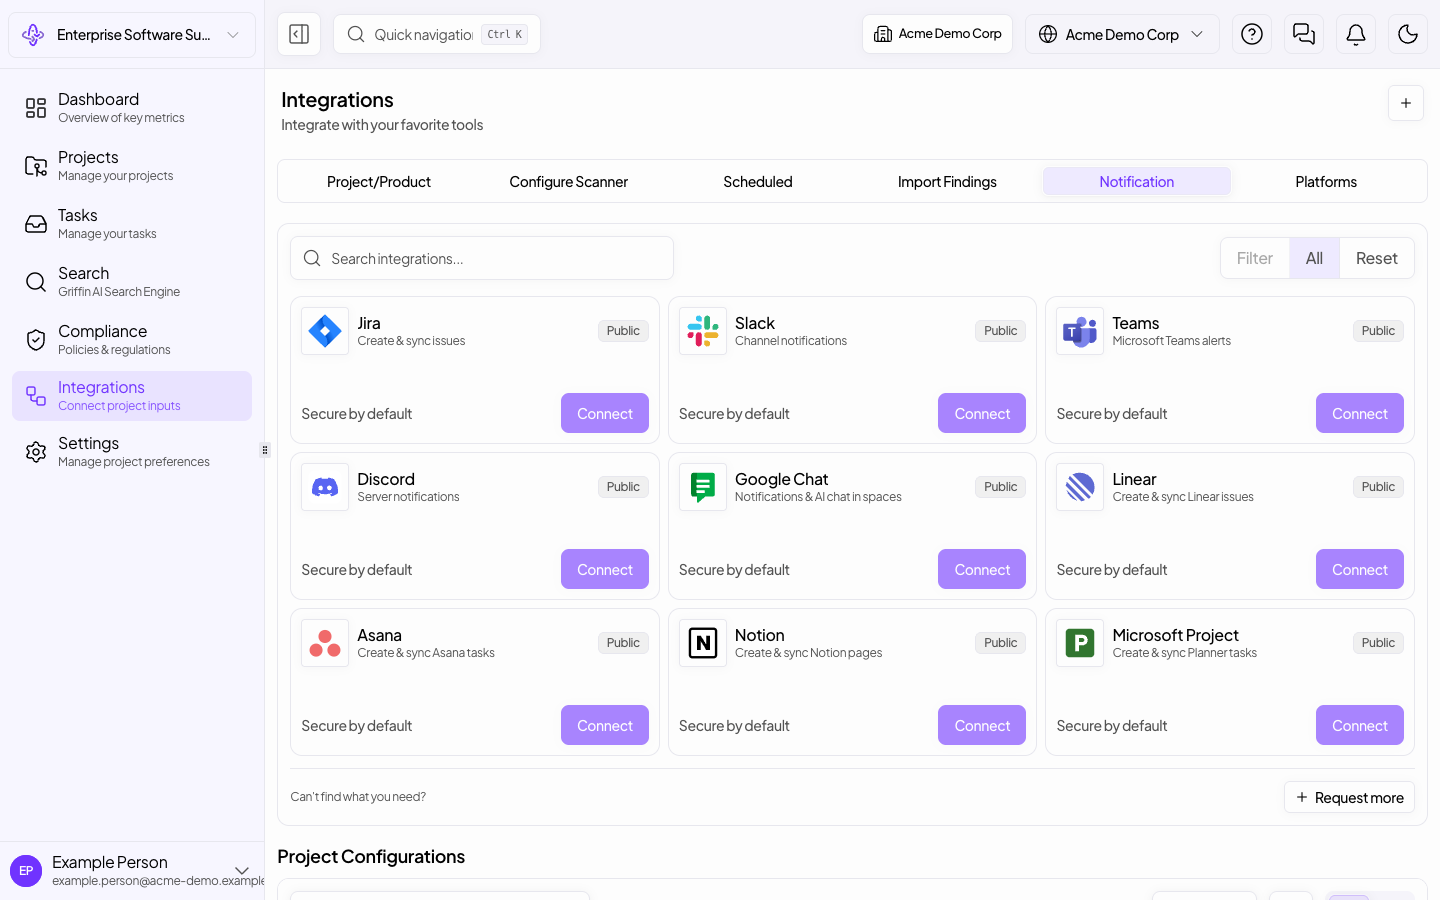
Connect Slack and Jira (Teams connects the same way), map Jira statuses, and choose which notification categories reach chat.
2 min9 steps
 Interactive
Models
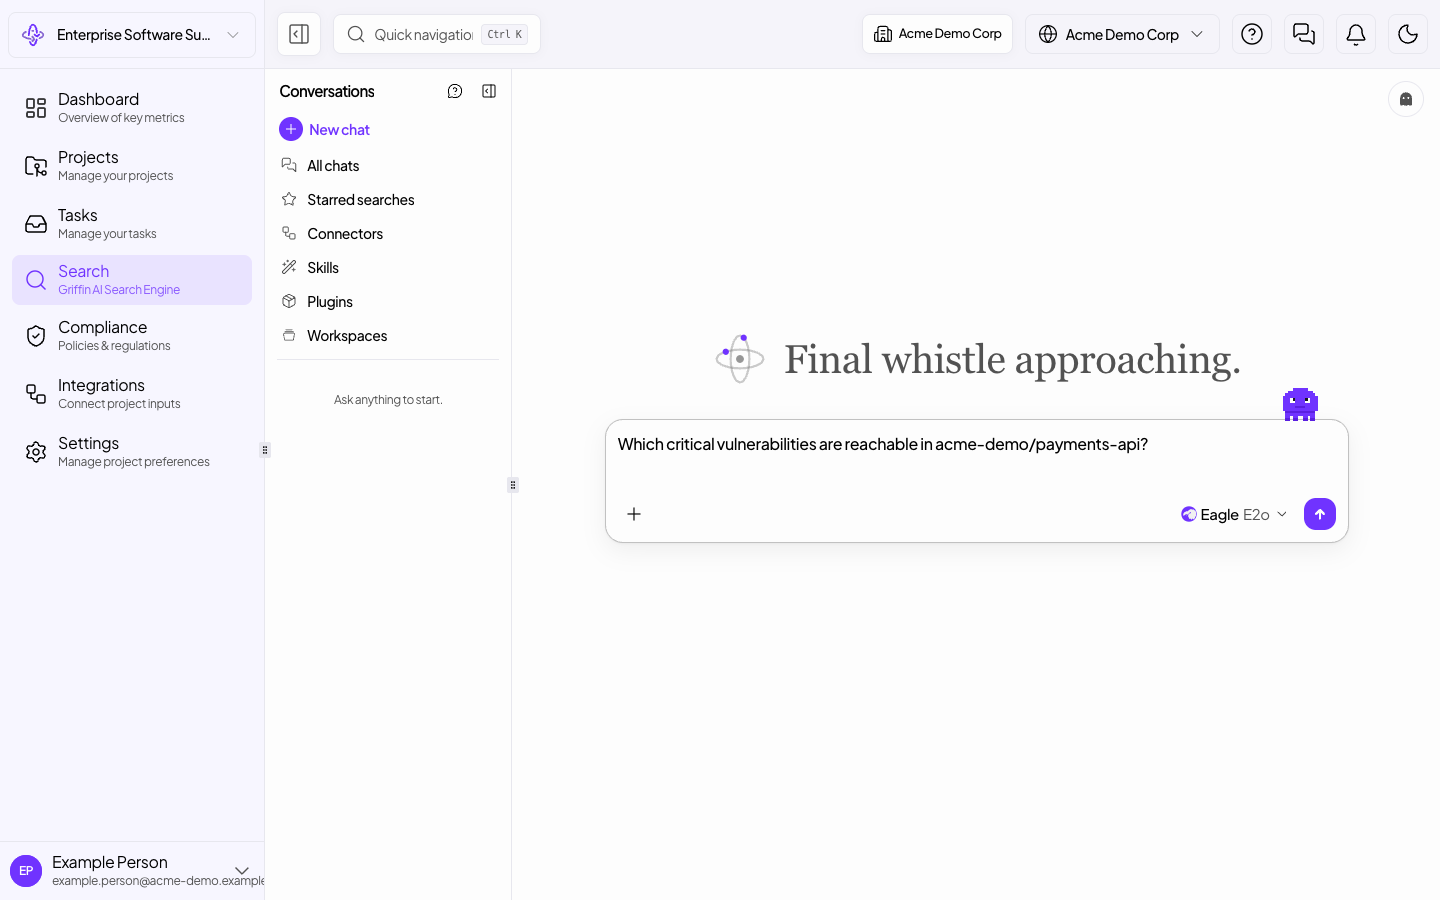
Choose the model for each conversation (Zero, Griffin, Eagle or Lion), decide which families your people may use, and add a model on your own account with job routing.
1 min8 steps
 Interactive
Supply chain security
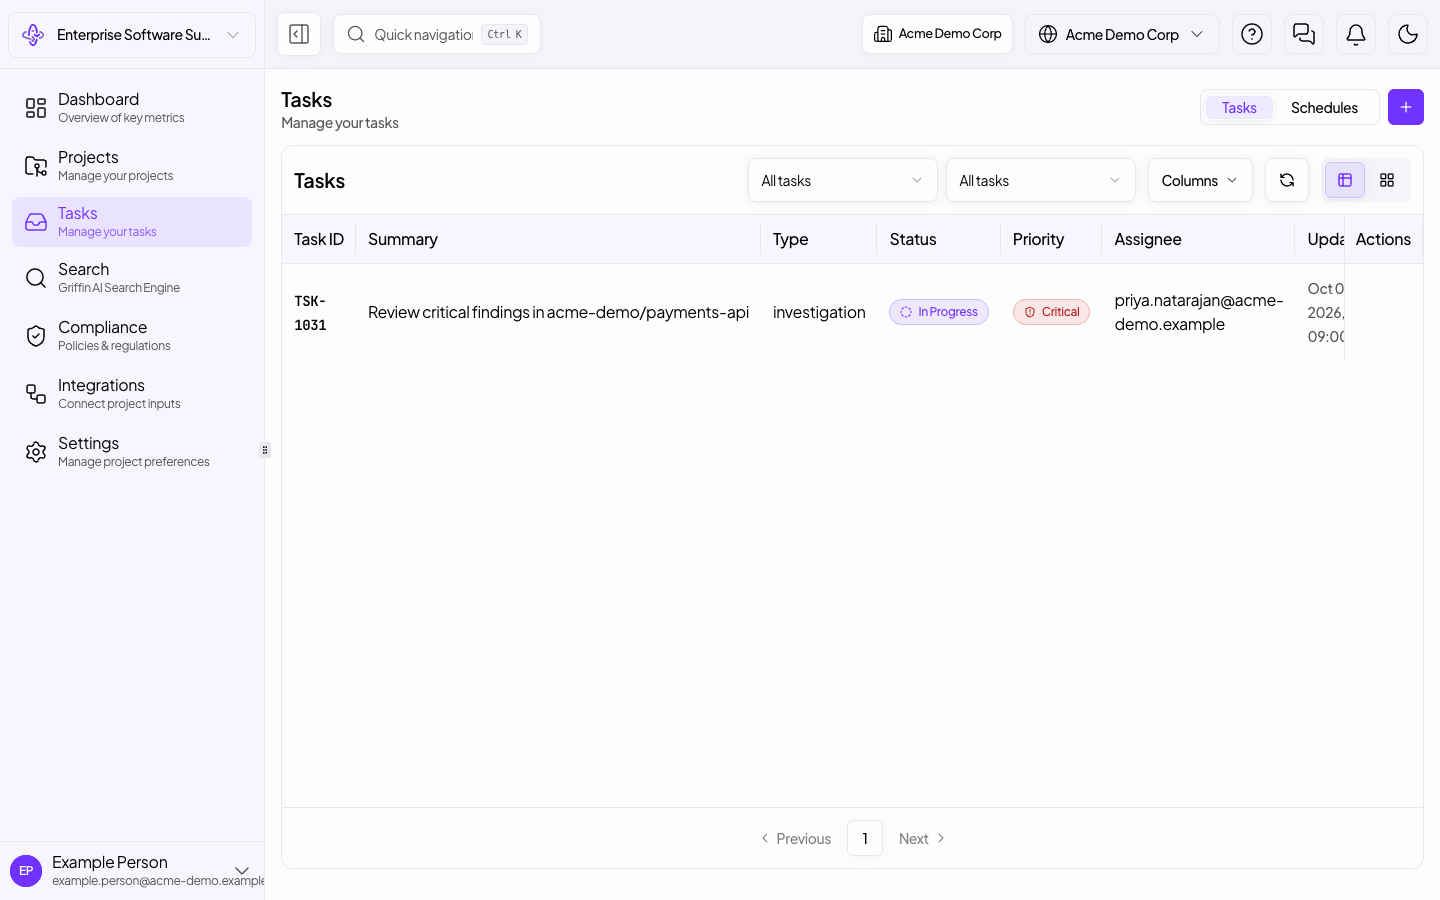
See every report schedule held for your workspace, then choose how scheduled report notifications reach you, the email digest, and the report style.
1 min7 steps
 Interactive
Supply chain security
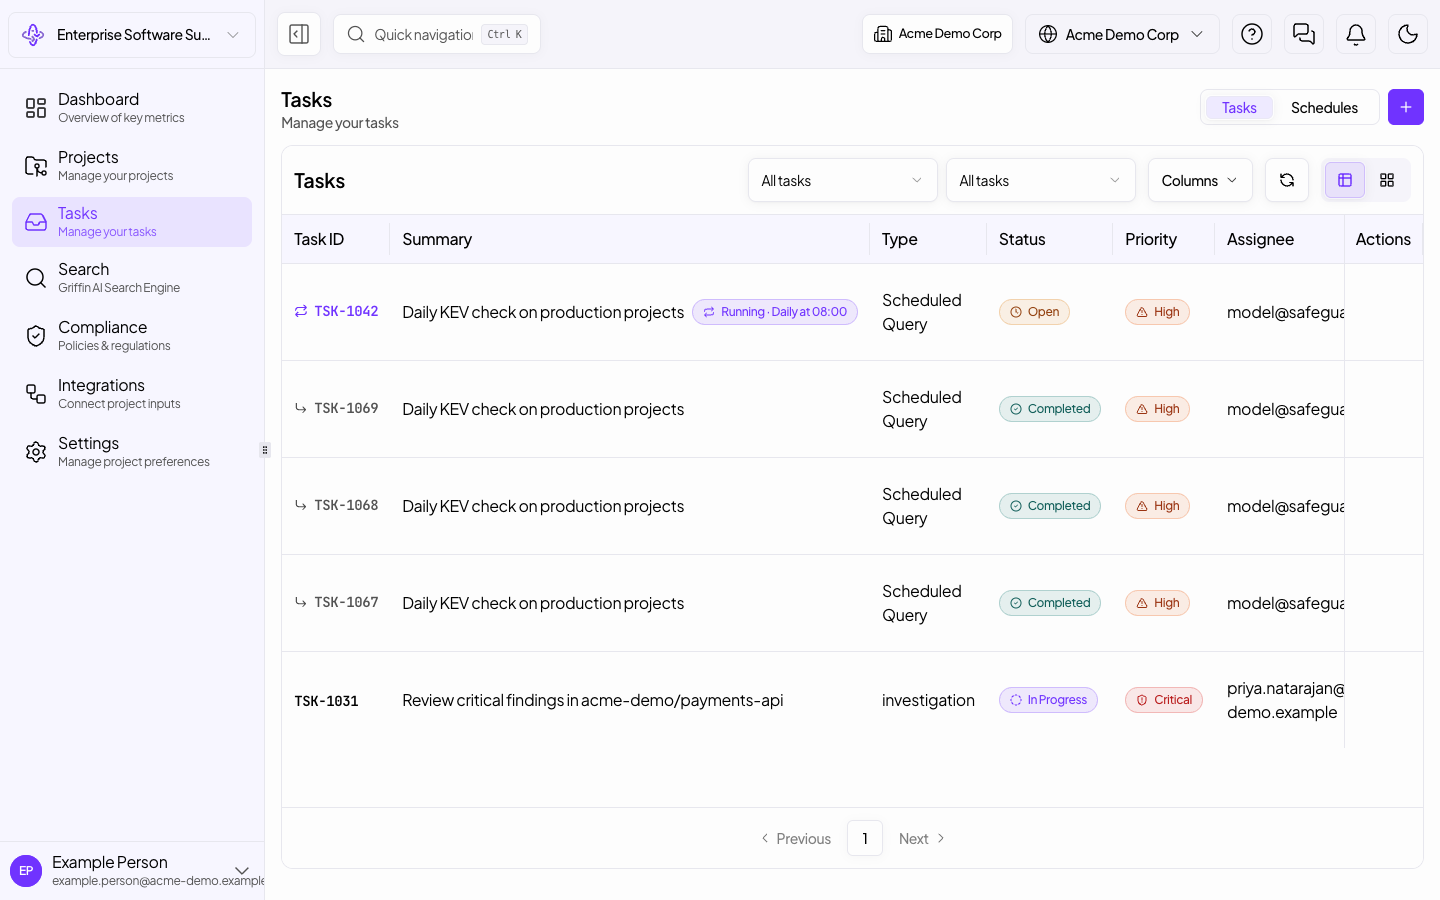
Create a task that repeats on a schedule, choose the model that answers it, let an agent run it with your approval, and follow every run.
1 min9 steps
 Interactive
Supply chain security
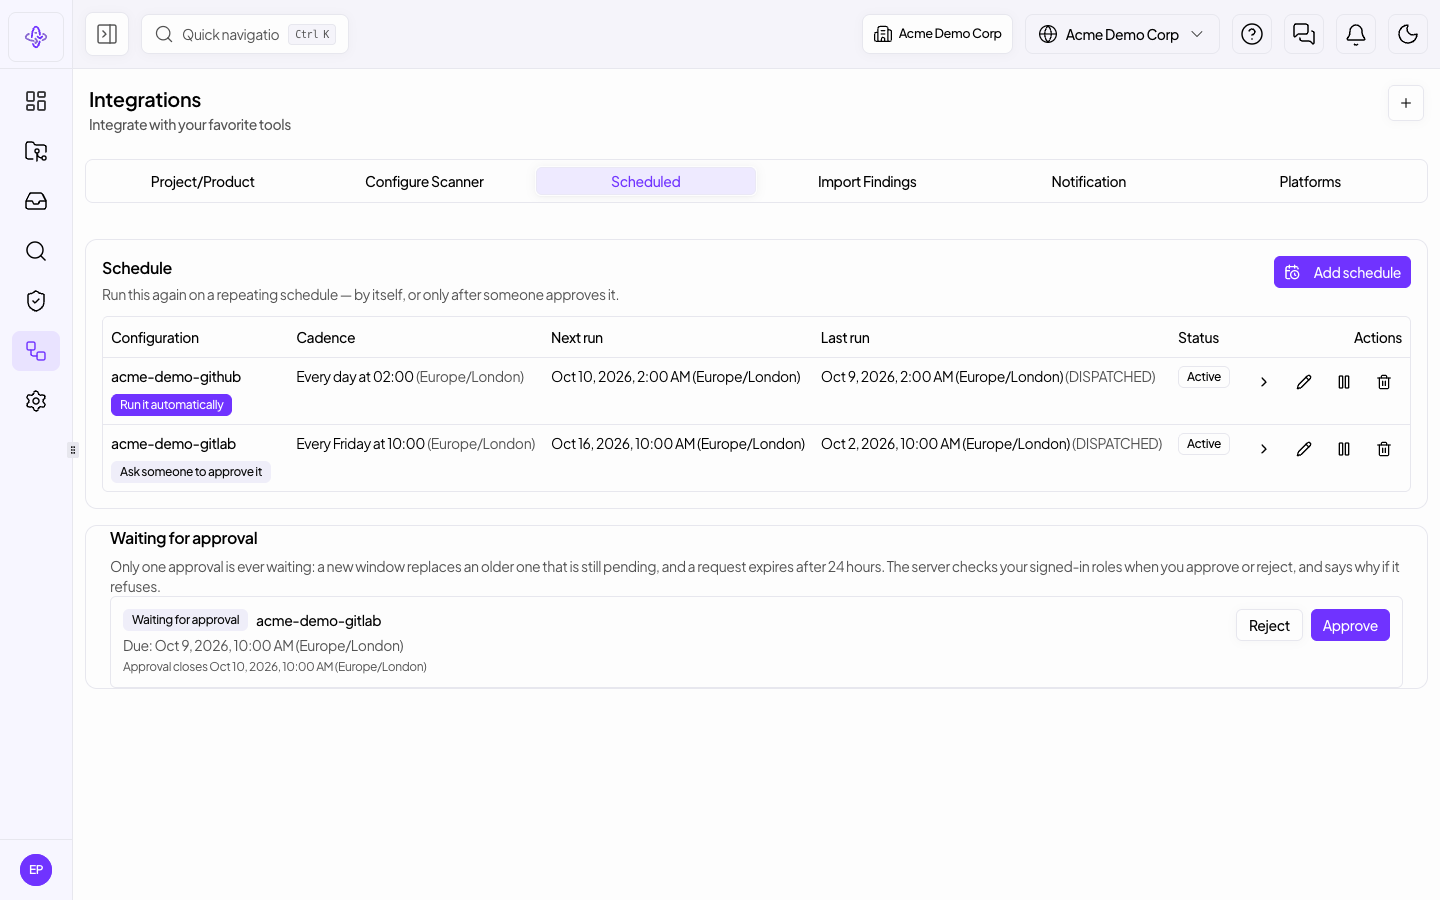
Schedule each connected integration to scan on a cadence, by itself or only after someone approves, and follow every run.
1 min9 steps
 Interactive
Search
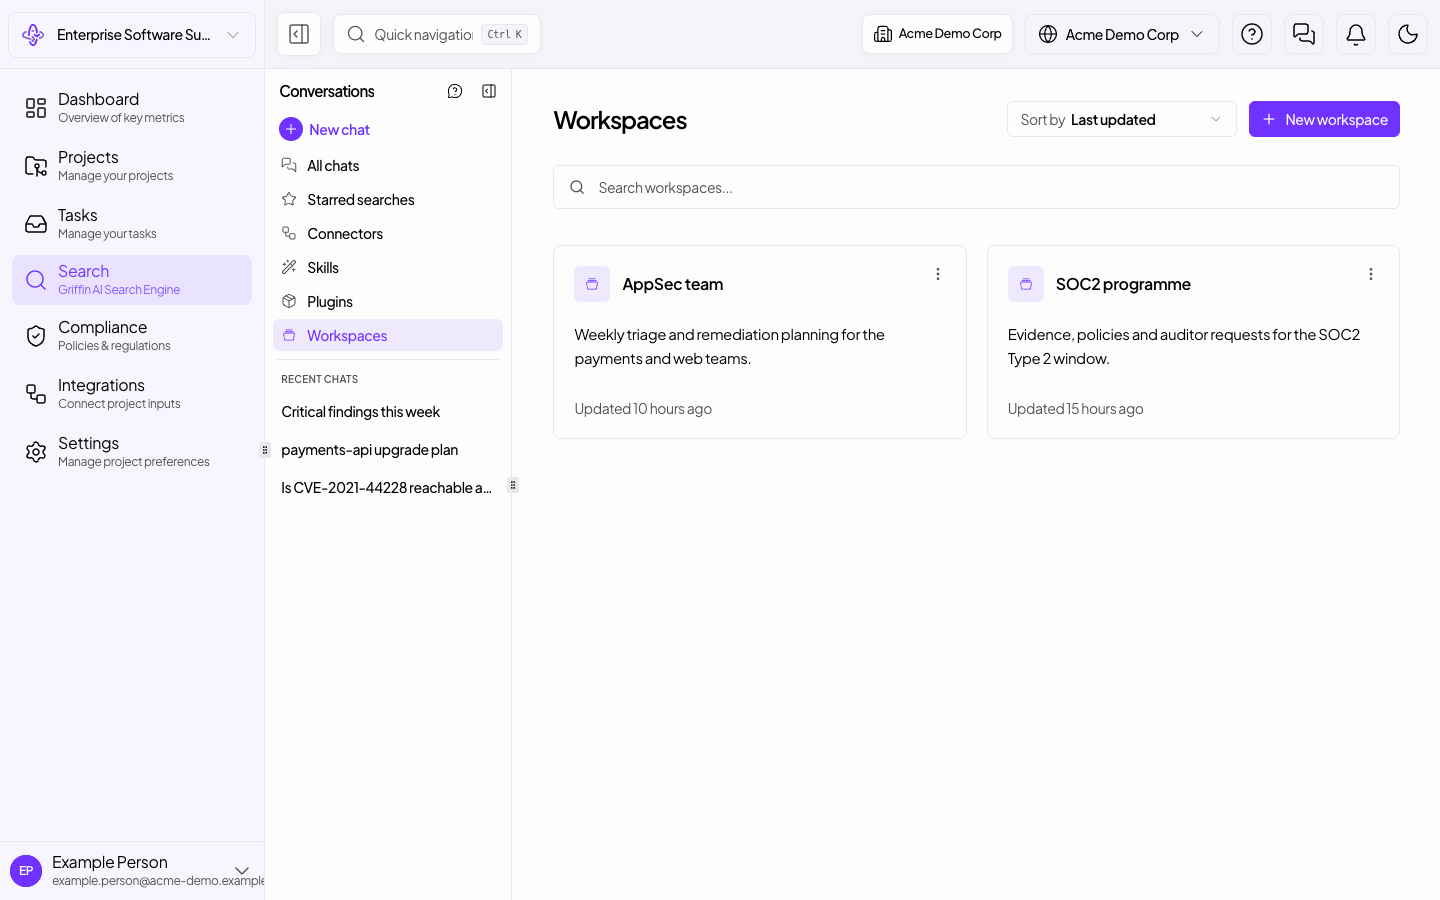
Create a workspace with its own instructions, open it to start scoped conversations, and see a team workspace with its skills and conversations.
1 min7 steps
 Interactive
Search
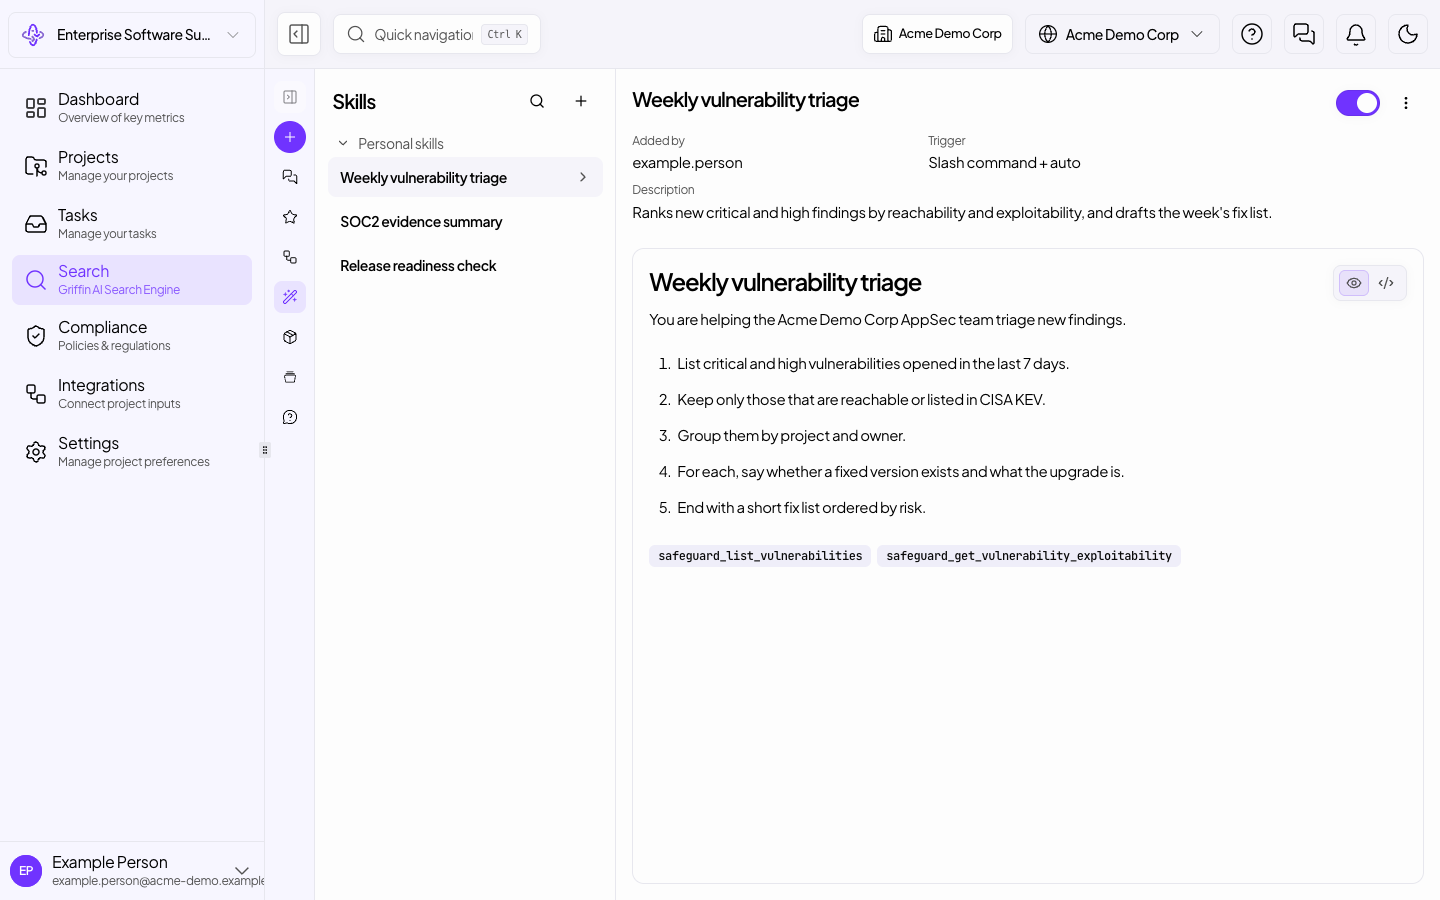
Write a reusable skill once (instructions plus the Safeguard MCP tools it may use), switch it on, start a conversation with it, and see skills applied as a workspace's context.
1 min8 steps
 Interactive
Search
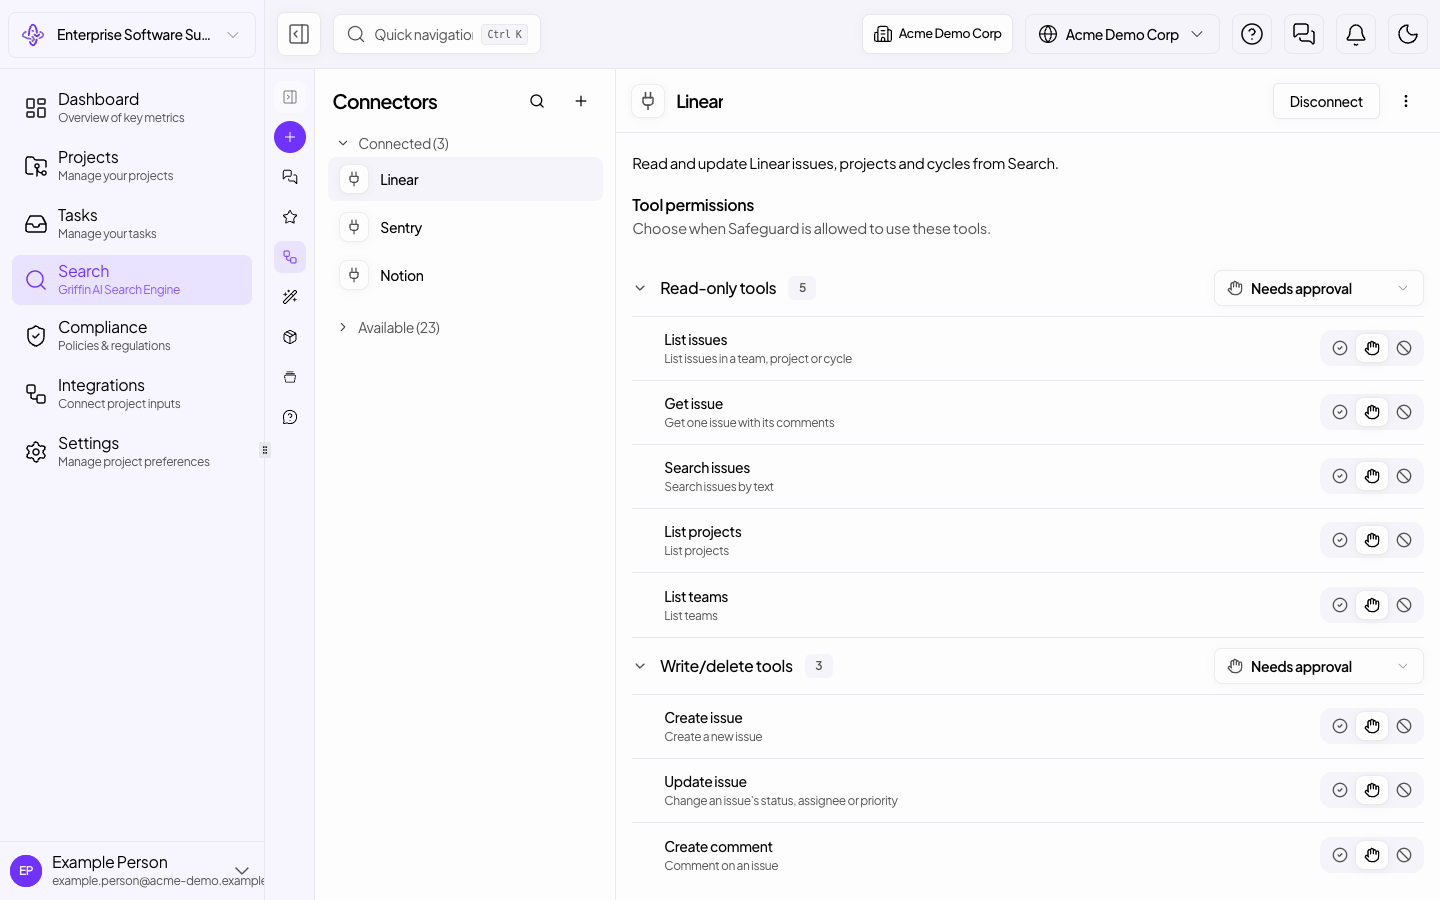
Connect the tools your team uses to Search through their MCP servers, and decide what each tool may do: always allow, ask first, or deny.
1 min8 steps
 Interactive
Supply chain security
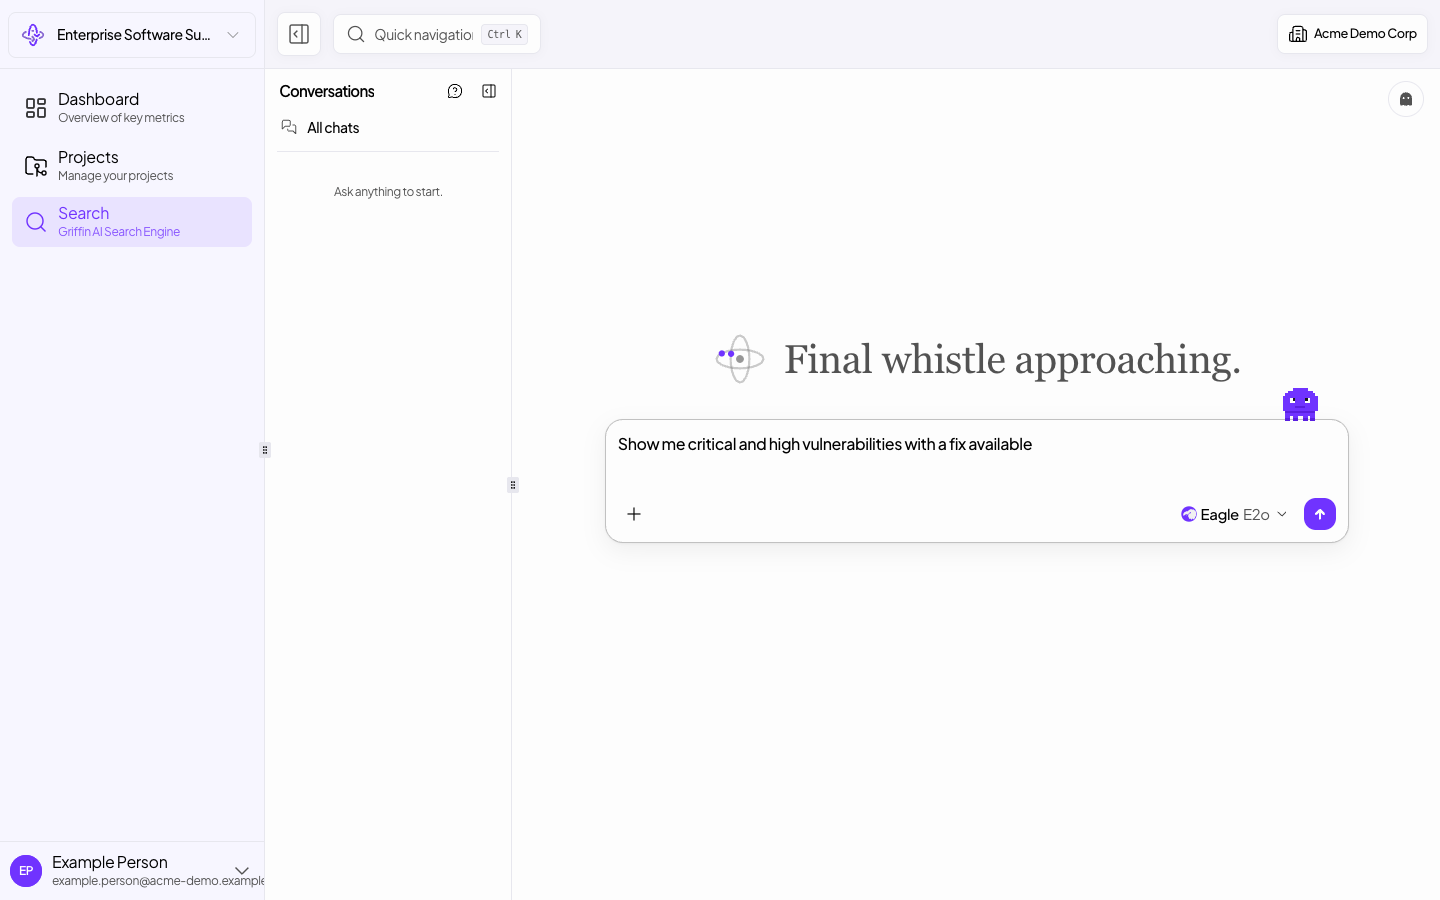
Ask Search a question in plain English and get a live table from your own workspace, export it, and follow up in the same conversation.
2 min7 steps
 Interactive
Supply chain security
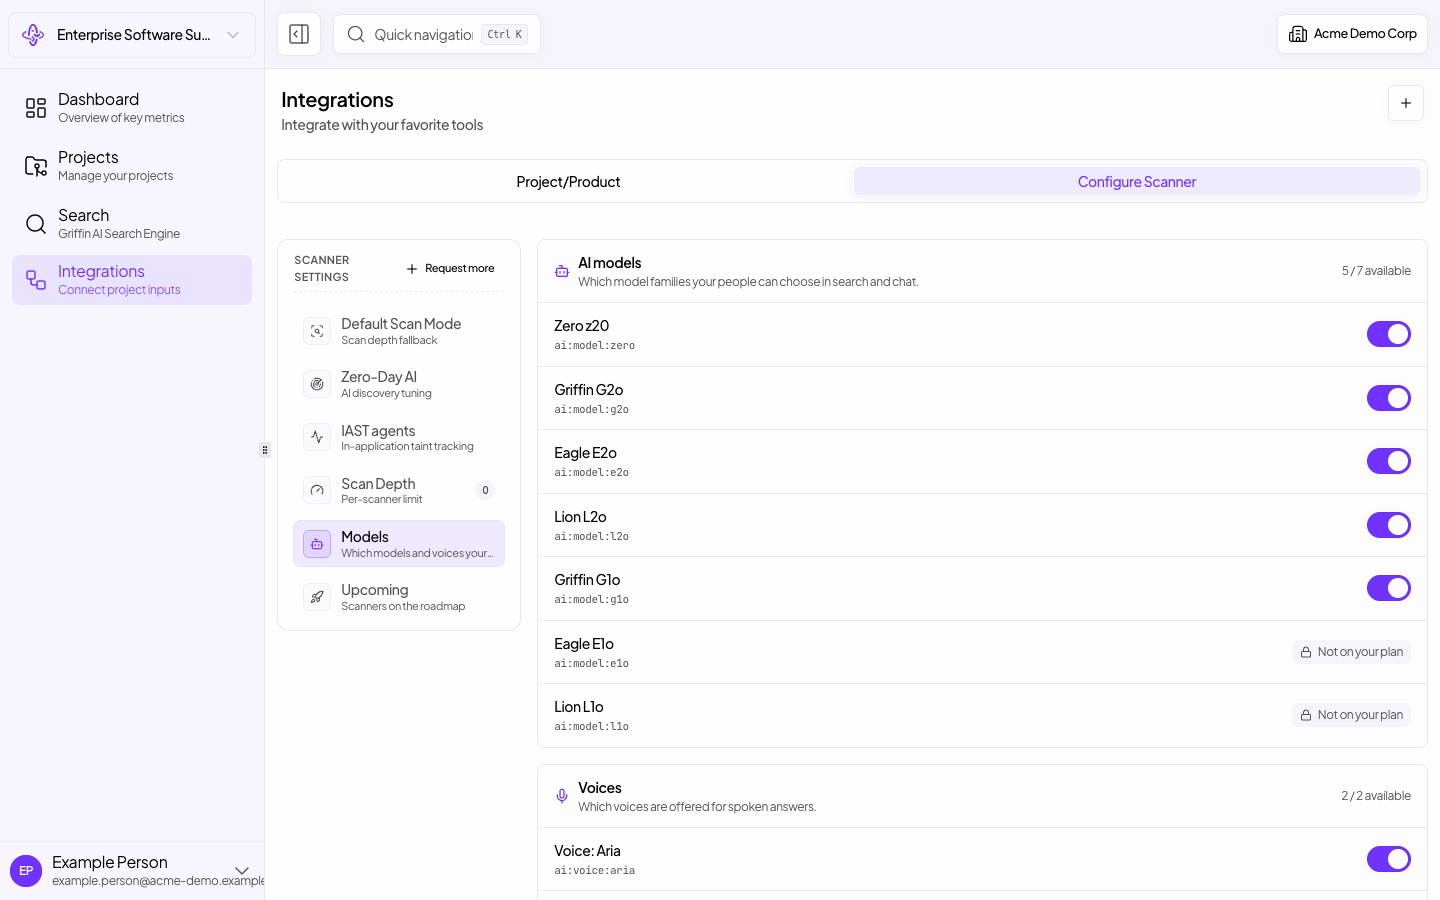
Decide which model families people can use, keep only Zero (no language model), and add your own model with the API it speaks and the jobs routed to it.
2 min7 steps
 Interactive
Supply chain security
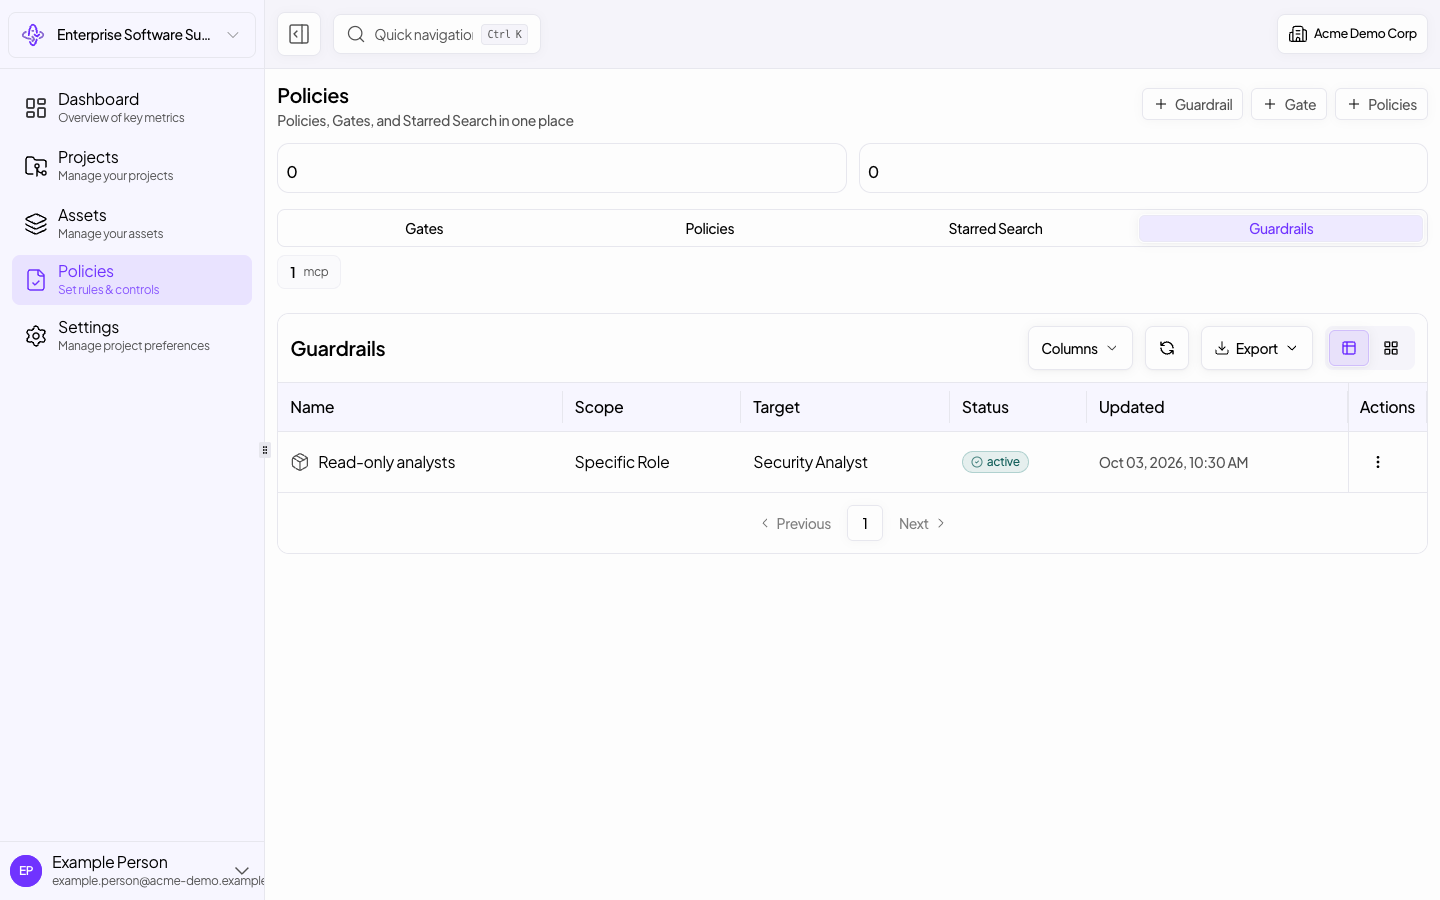
Write an MCP proxy guardrail for agents: which tools a role may use, which fields they may see and how many requests they may make, then see each agent's identity.
2 min9 steps
 Interactive
Supply chain security
Connect ChatGPT to the Safeguard MCP server with OAuth on Safeguard's own consent page, see the connection, and decide which tools ChatGPT can use.
2 min7 steps
 Interactive
Supply chain security
Connect Claude to the Safeguard MCP server with OAuth on Safeguard's own consent page, see the connection, and decide which tools Claude can use.
2 min7 steps
 Interactive
Supply chain security
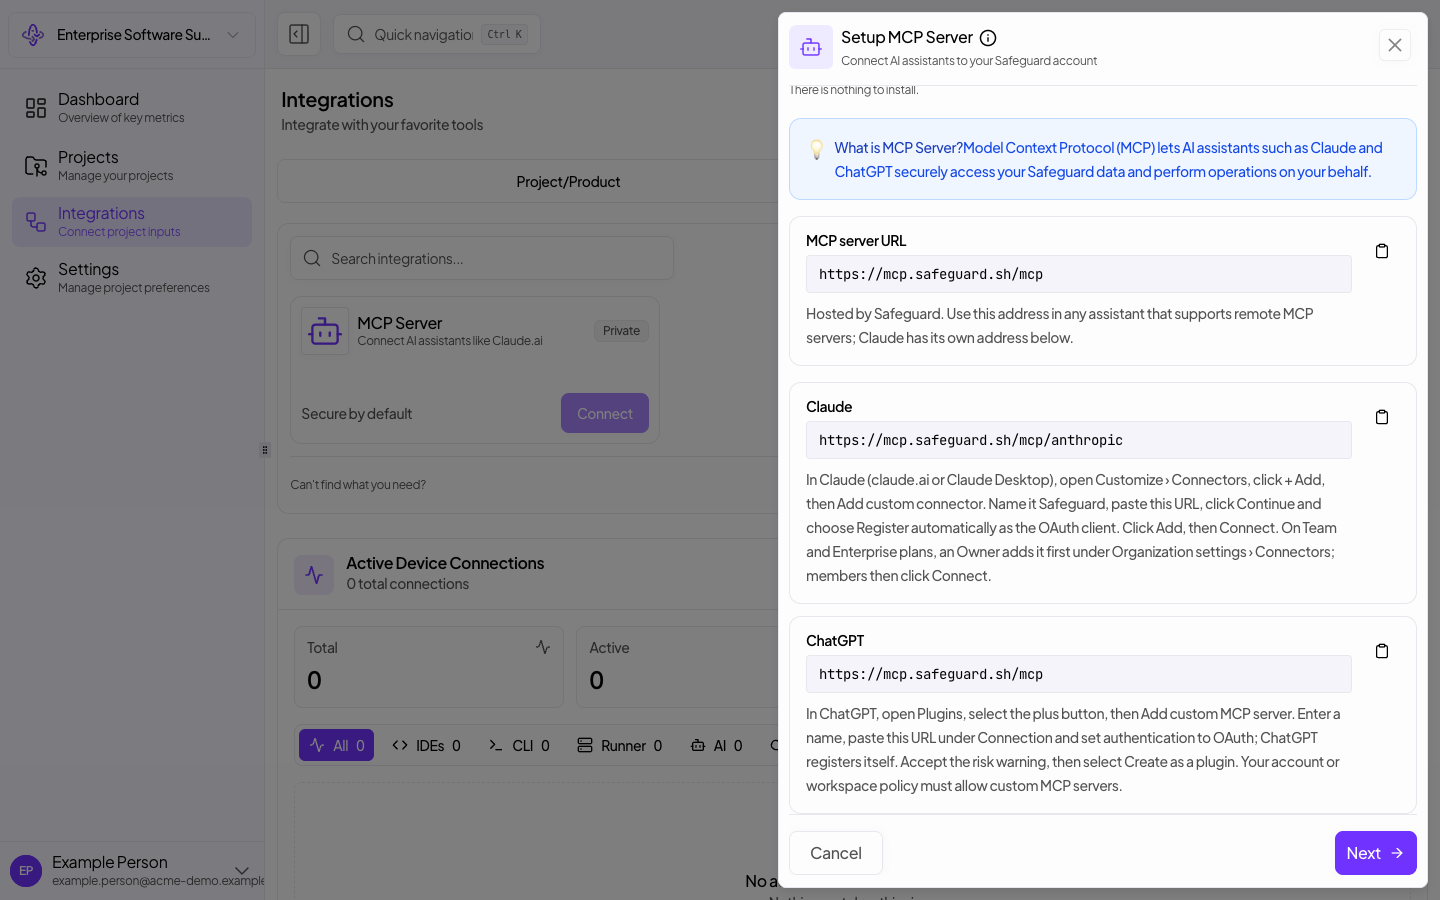
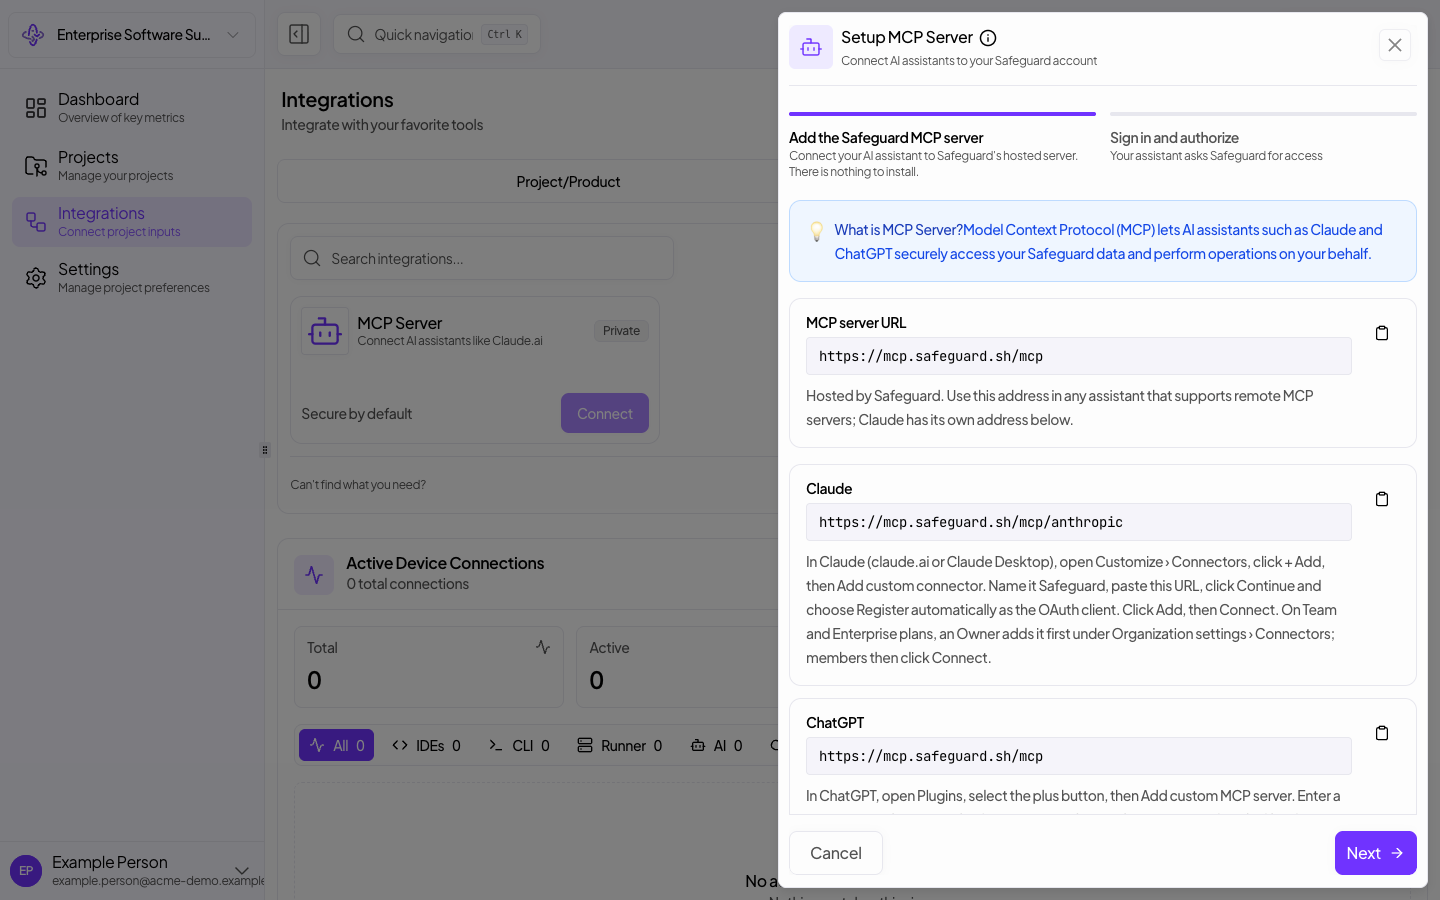
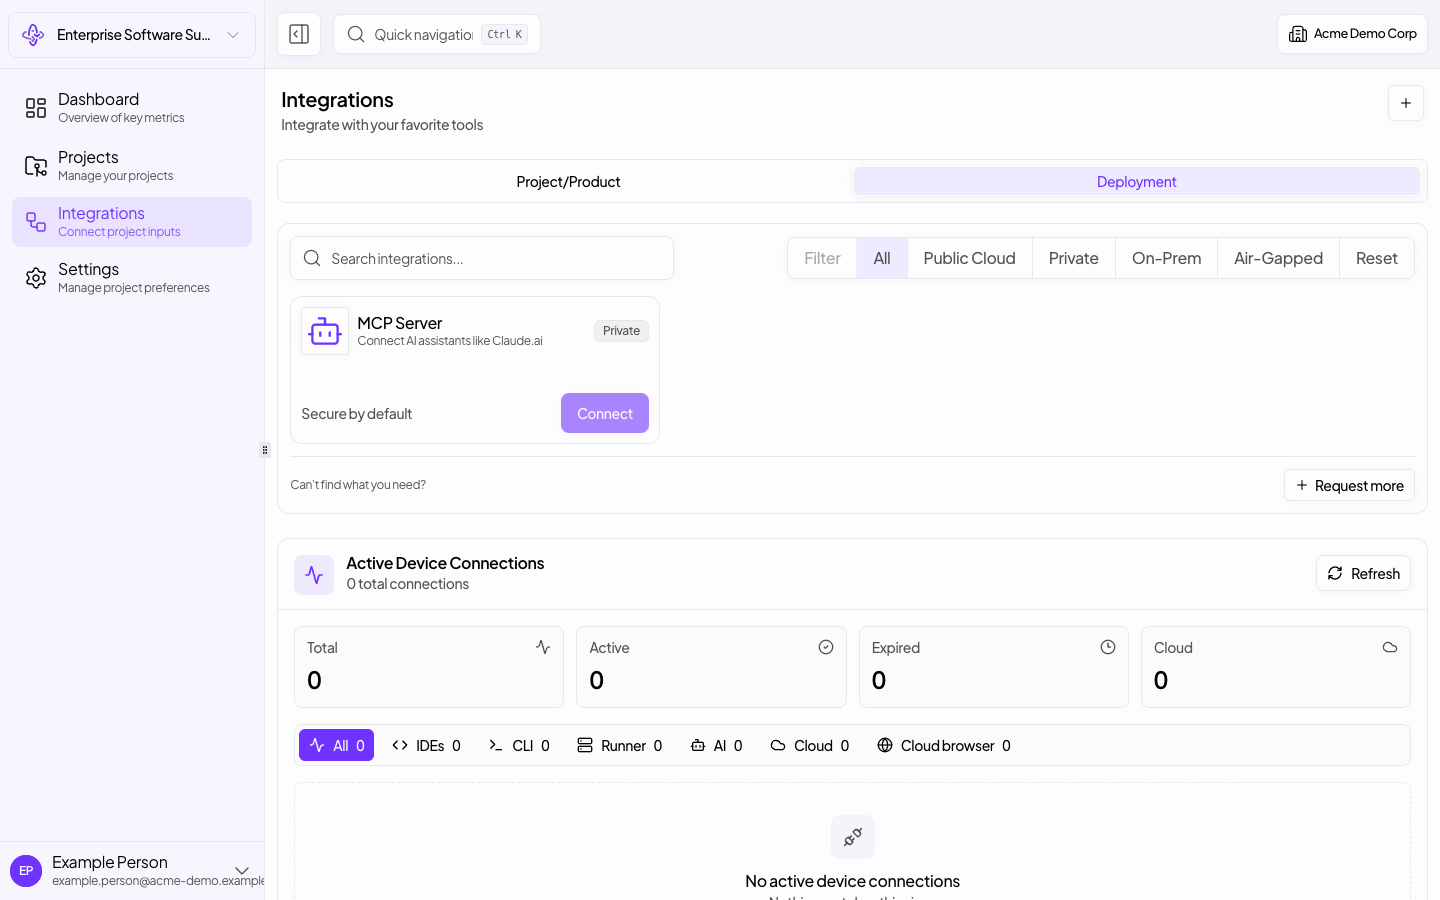
Connect AI assistants to the hosted Safeguard MCP server with OAuth or an MCP key, and decide which tools they can use.
2 min9 steps
 Interactive
Supply chain security
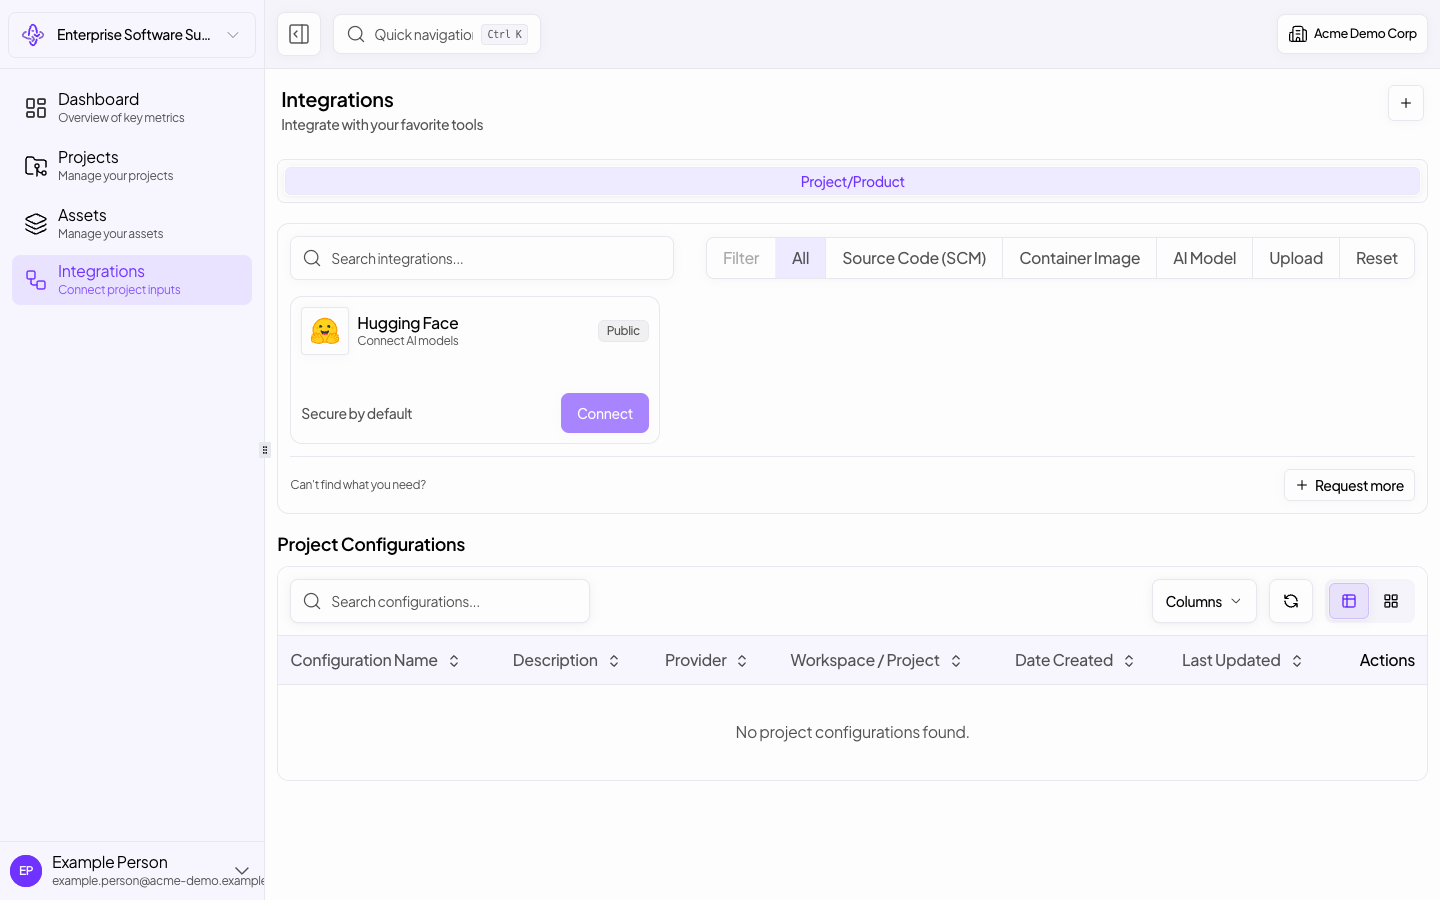
Connect Hugging Face model repositories as projects and scan them, then check a model's record: its size, and AI-BOM checks that flag unsafe weight formats and missing training data.
2 min8 steps
 Interactive
Supply chain security
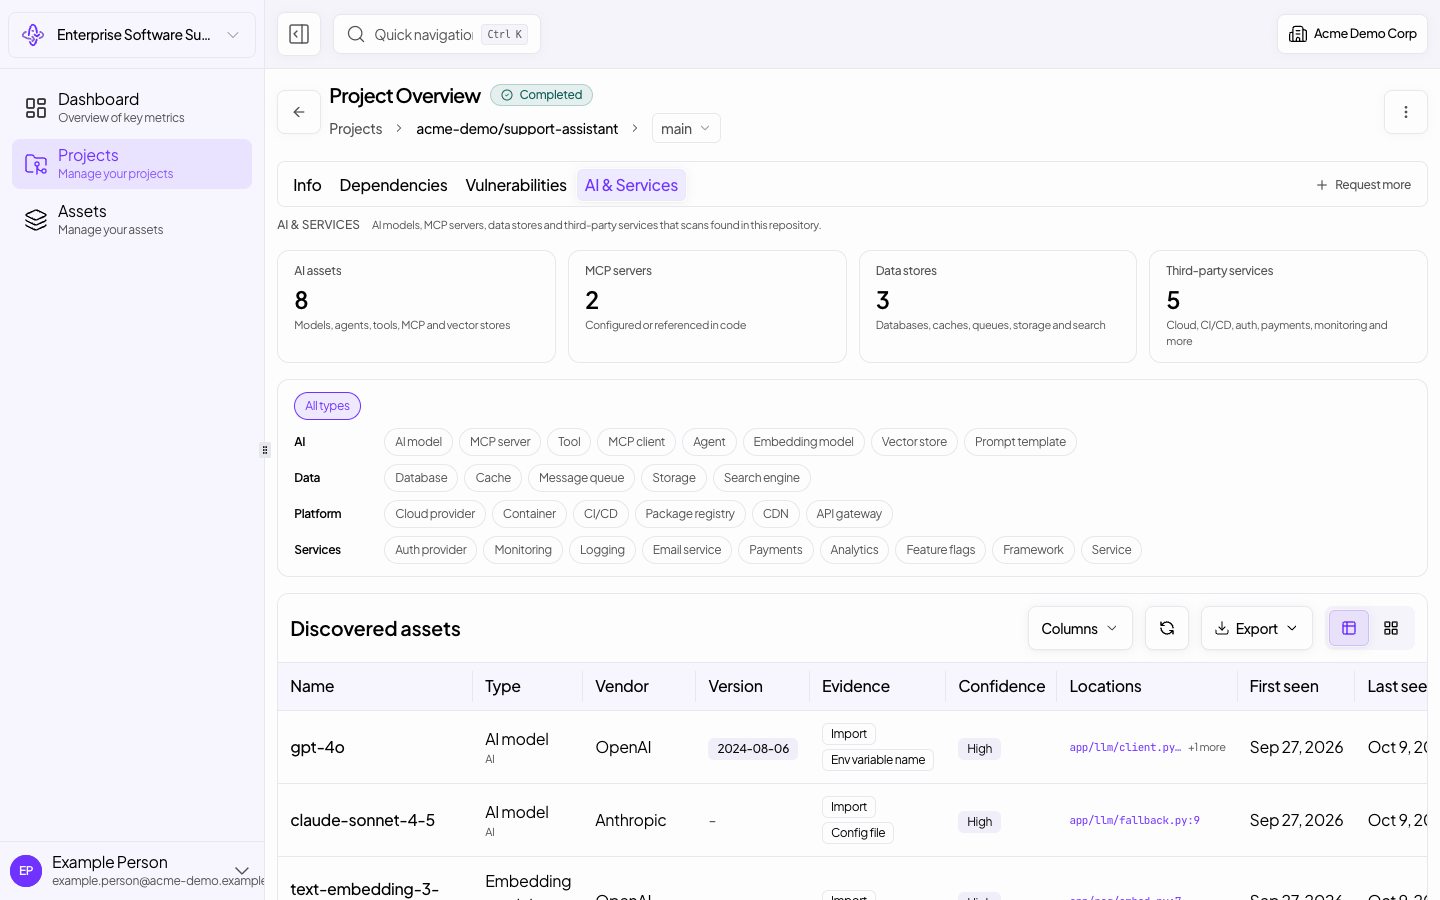
See the AI models, agents, MCP servers and vector stores a scan found in a repository, with file and line, then the workspace inventory and a model's CycloneDX ML-BOM.
2 min8 steps
 Interactive
Supply chain security
Connect your Anthropic organization with an access key, sync the Claude Activity Feed from the Compliance API, and read each event in Safeguard.
2 min7 steps
 Interactive
Compliance
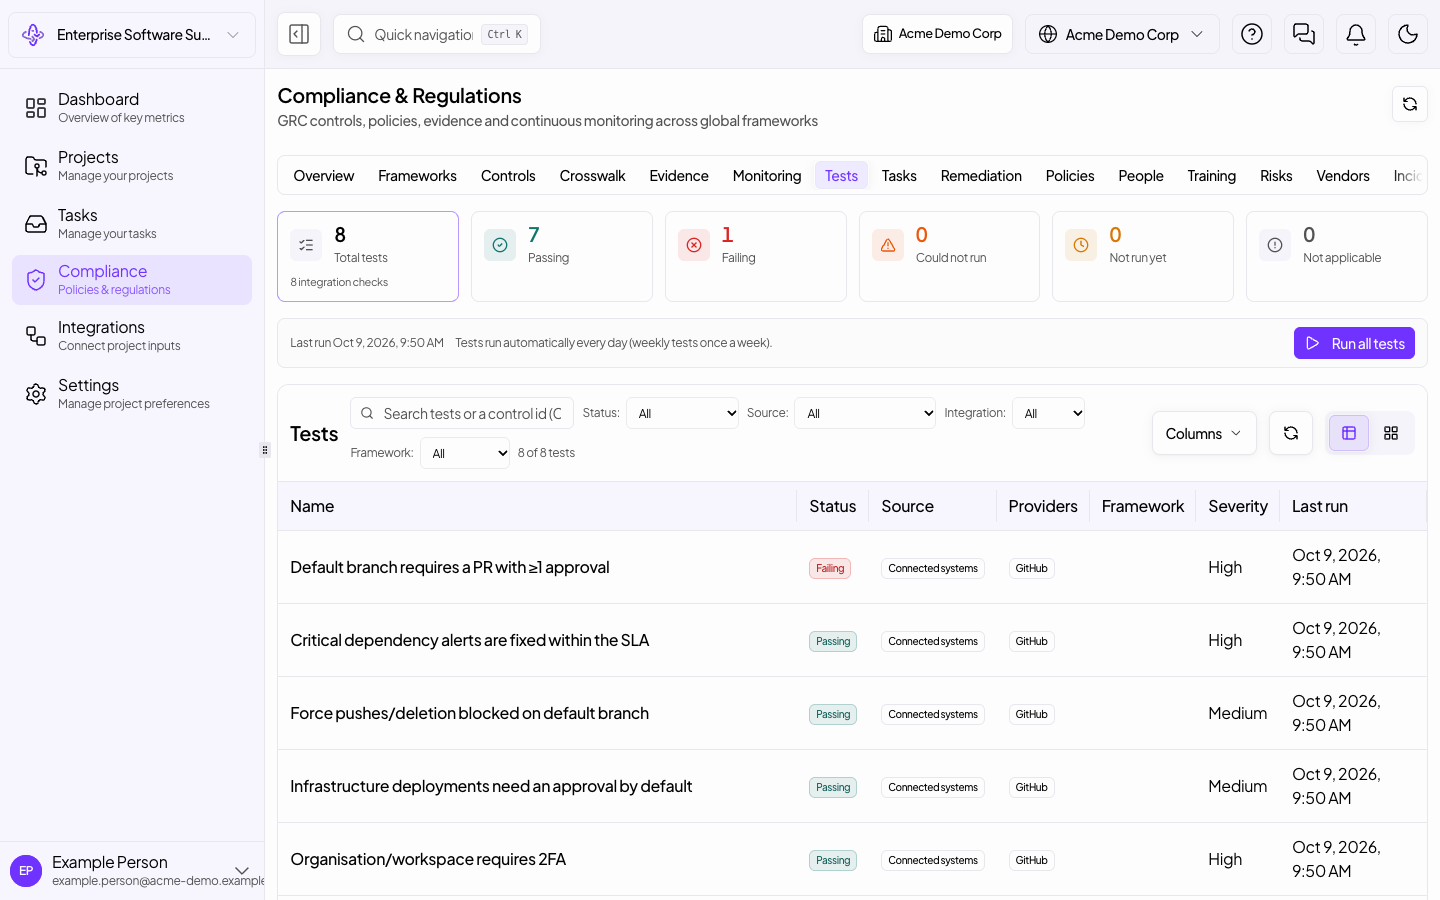
Request an exception for a failing check with a reason, a named approver and an end date, then approve a colleague's request, with every decision kept on the test.
1 min7 steps
 Interactive
Supply chain security
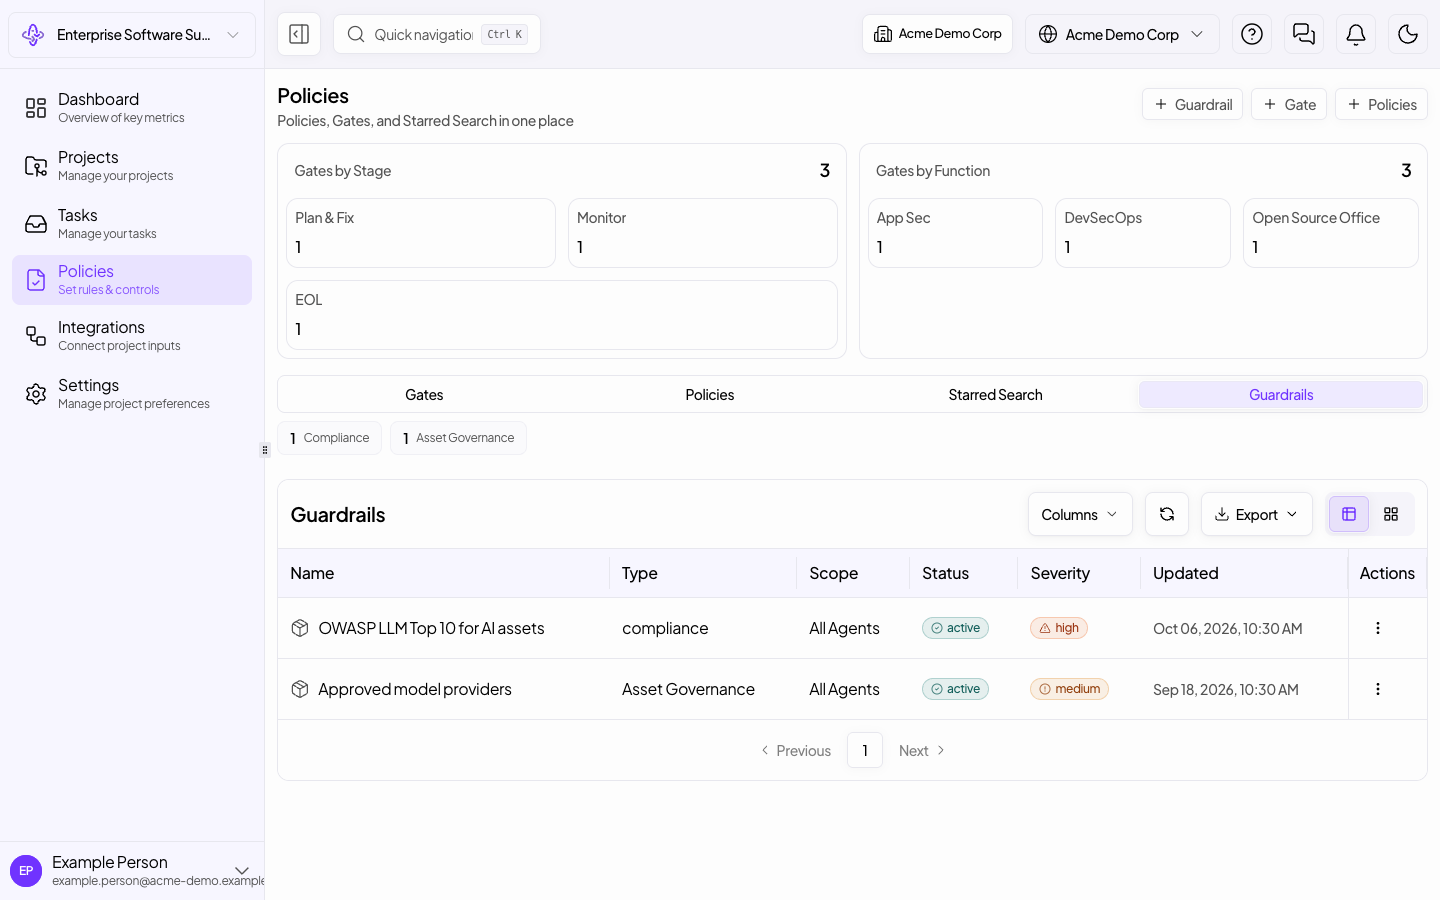
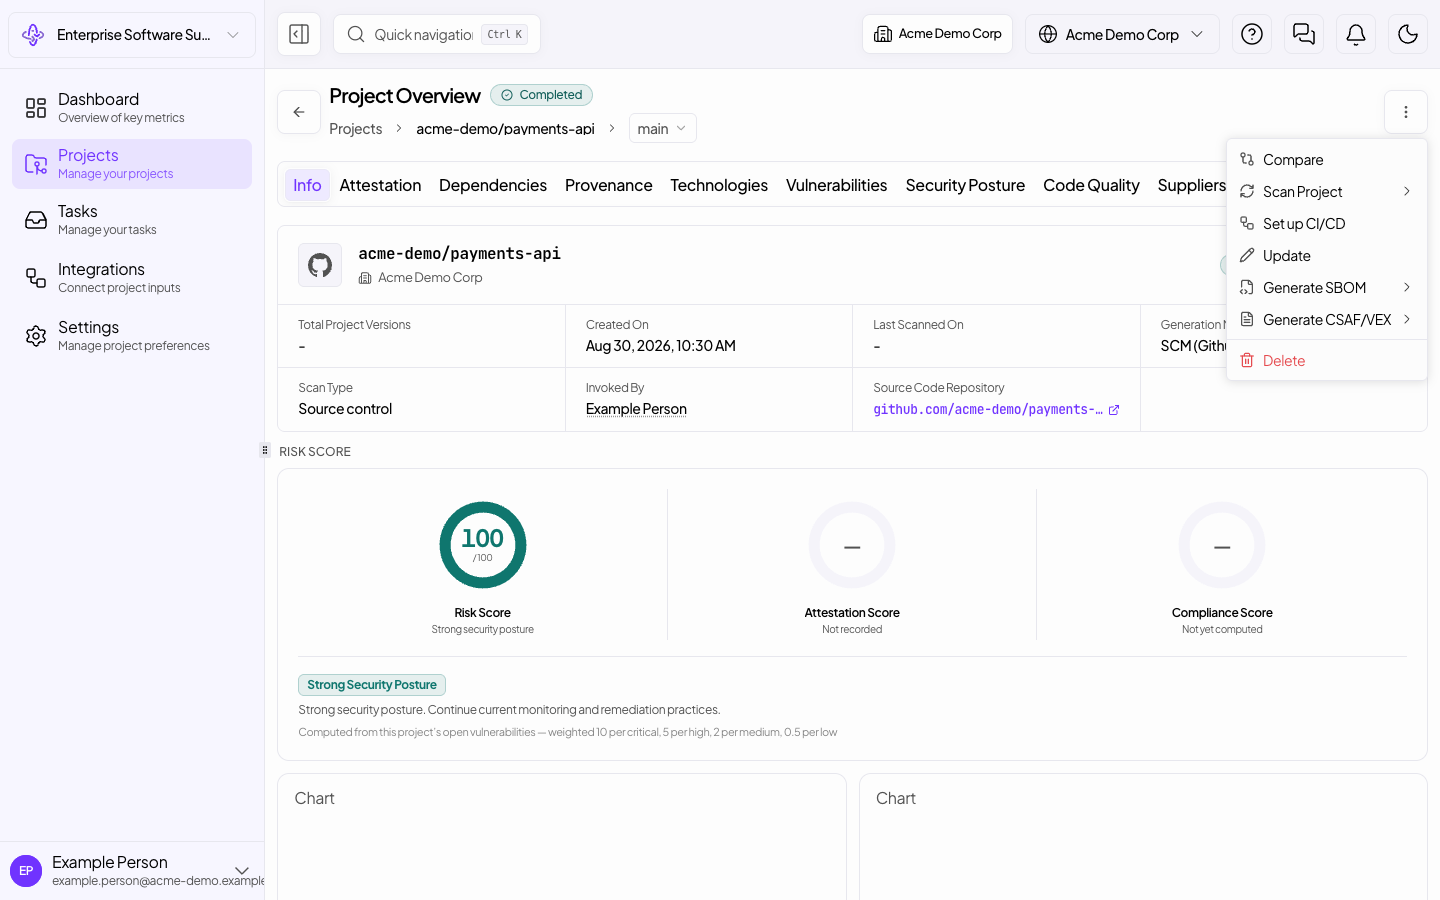
Create an MCP proxy guardrail for production agents: who it covers, which tools they may use, how it responds to unusual behaviour, and the policy as YAML.
2 min9 steps
 Interactive
Supply chain security
Add a Safeguard step to GitHub Actions, GitLab CI, Bitbucket Pipelines, Jenkins or Azure Pipelines that fails the build at the severity you choose, with its own CI/CD key.
2 min8 steps
 Interactive
Supply chain security
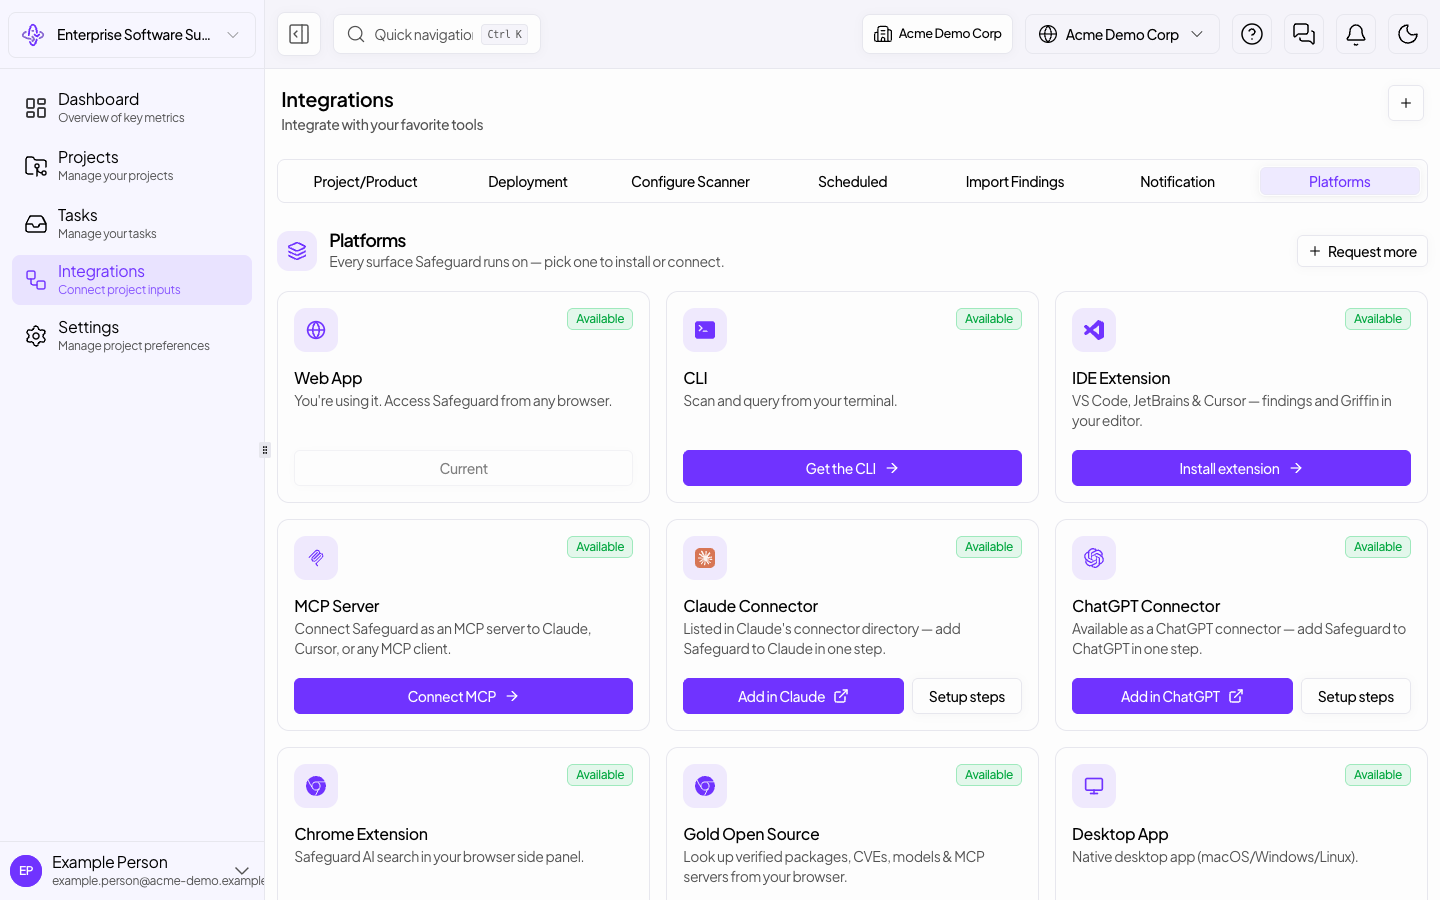
Connect the Safeguard IDE extension for VS Code, JetBrains or Open VSX editors: install, sign in with a device code, approve, and manage connected IDEs.
2 min8 steps
 Interactive
Supply chain security
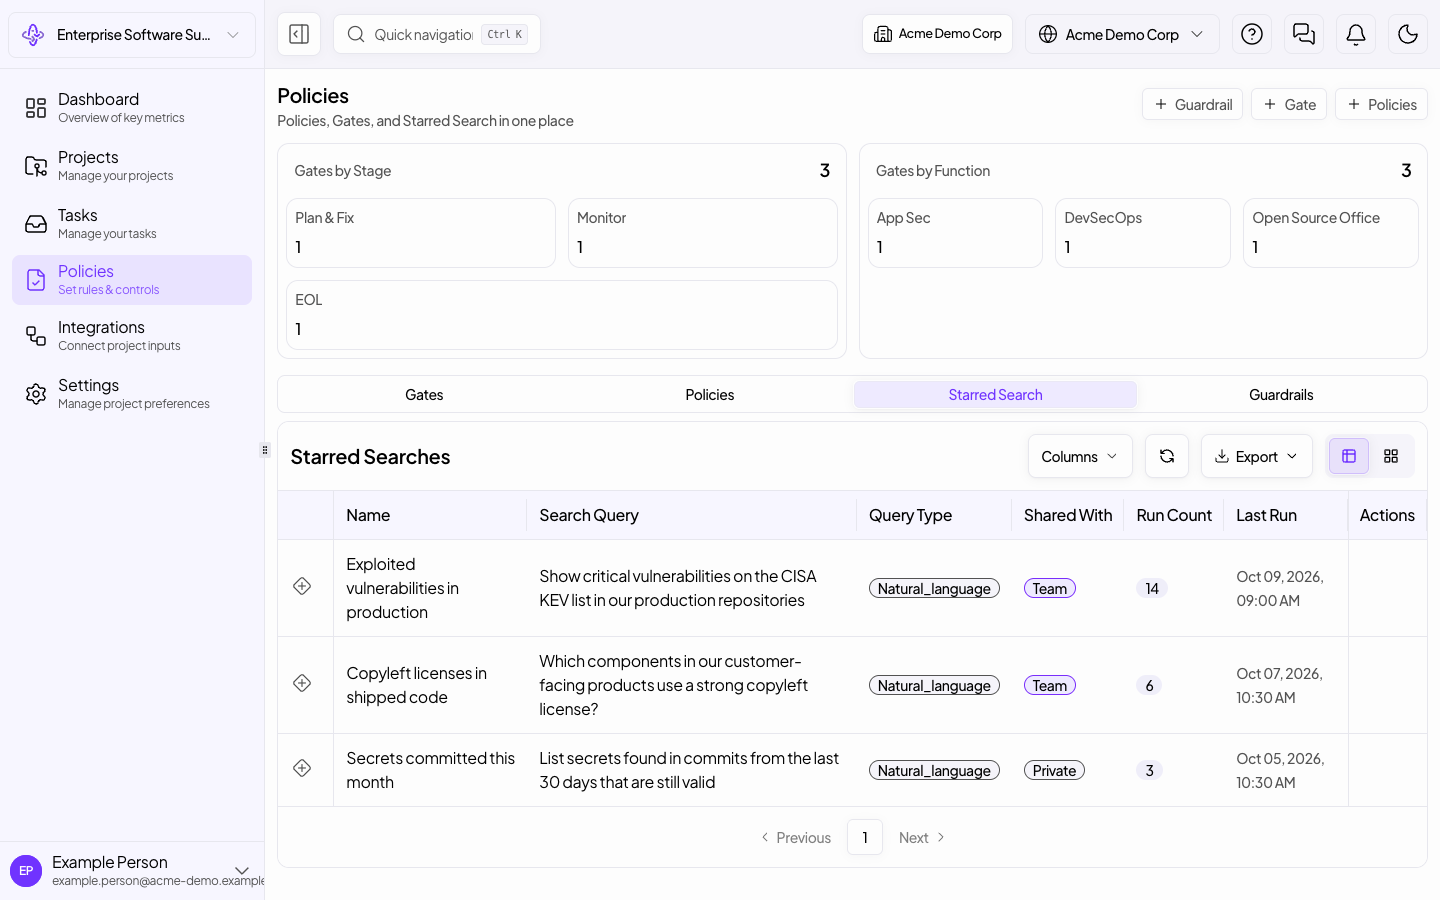
Turn a question asked in plain English into a policy: set its severity, action and threshold, attach it to a gate, and see it linked.
2 min8 steps
 Interactive
Supply chain security
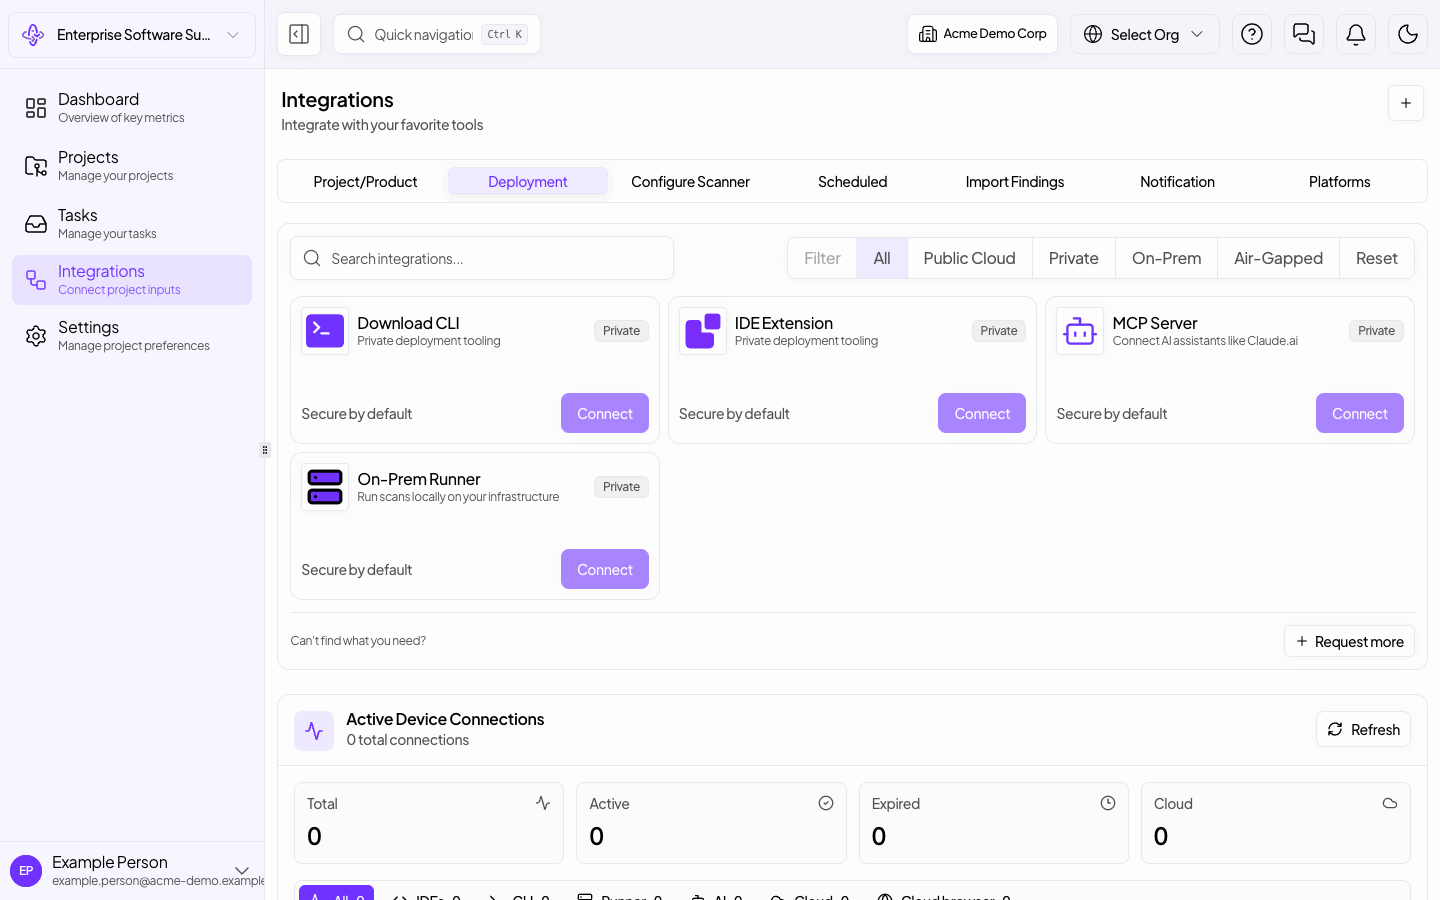
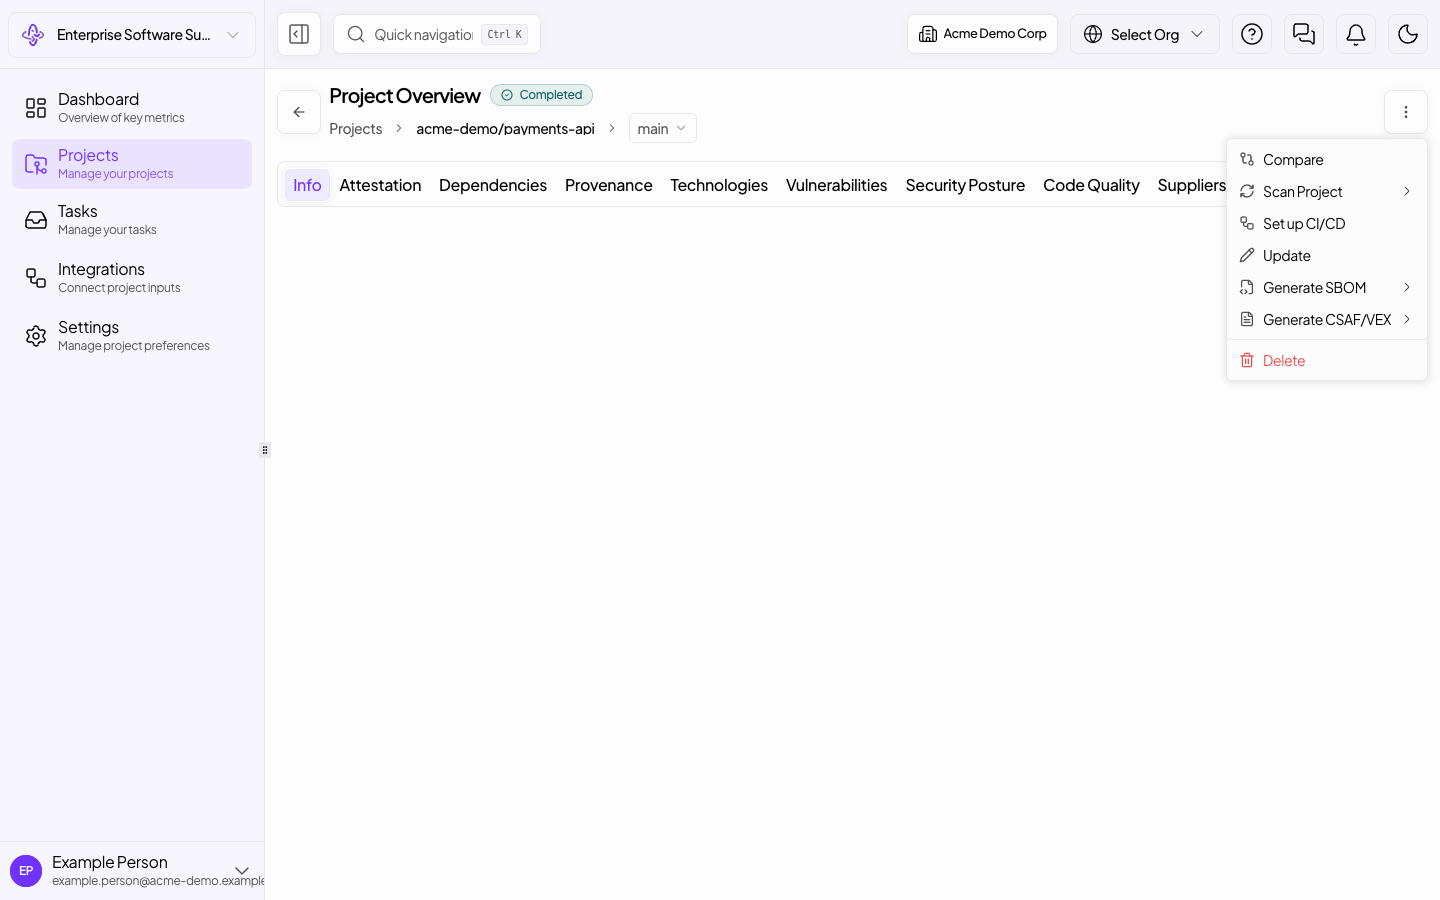
Set up the on-prem runner: pick the platform, start it, approve it with its device code, and use the same CLI to scan from your terminal.
2 min8 steps
 Interactive
Supply chain security
Add a Safeguard scan step to GitHub Actions, GitLab CI, Bitbucket Pipelines, Jenkins or Azure Pipelines, choose where it scans and which severity fails the build, and create its CI/CD key.
2 min8 steps
 Interactive
Supply chain security
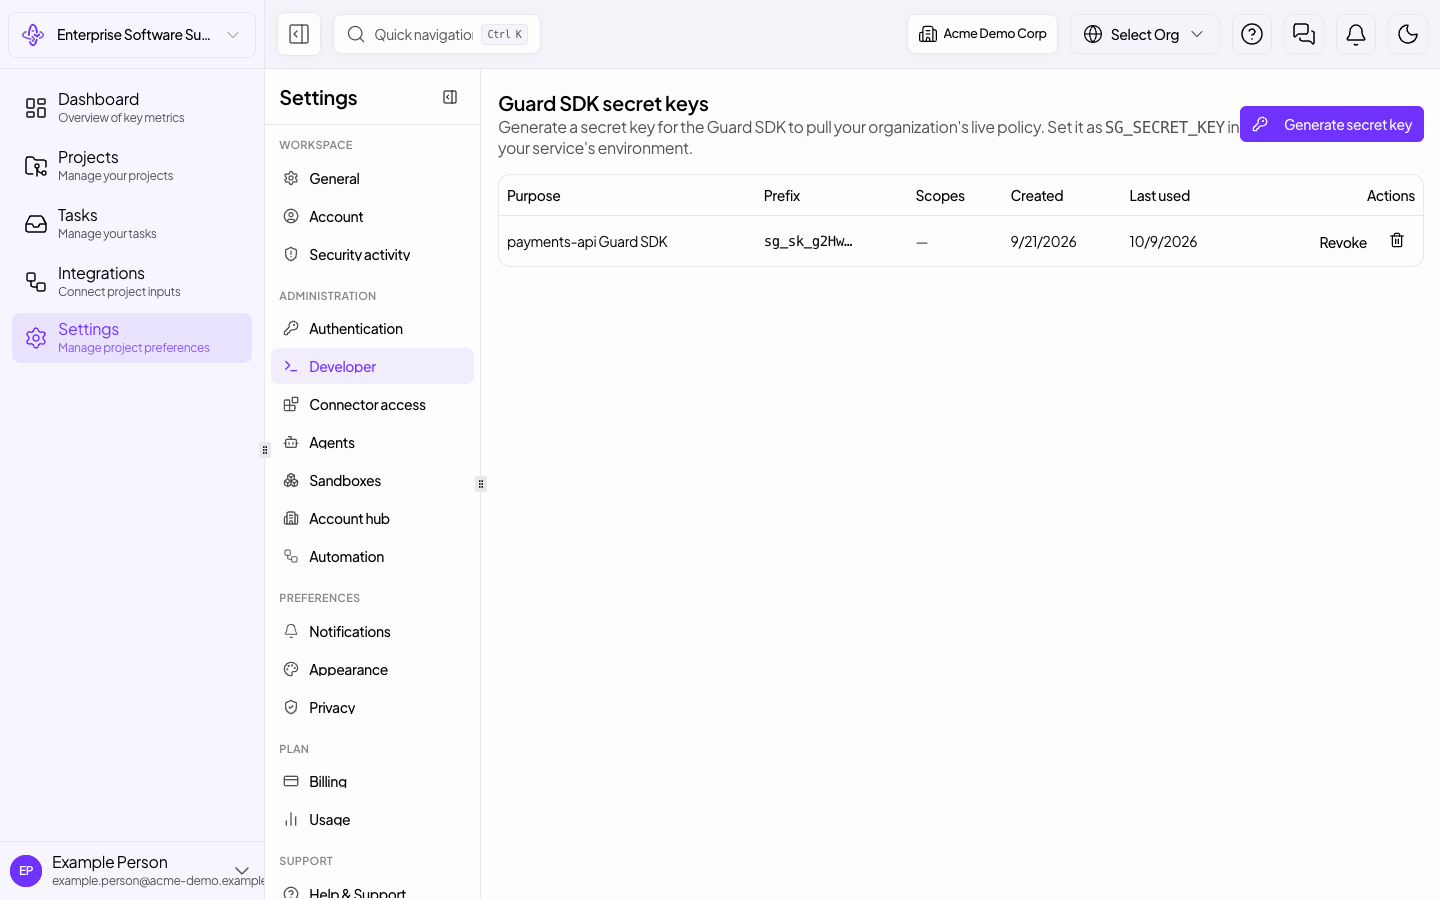
Create a key that does one job: a Guard SDK key, a CI/CD scanning key, or an MCP key for an agent platform, shown once and revocable.
1 min7 steps
 Interactive
Supply chain security
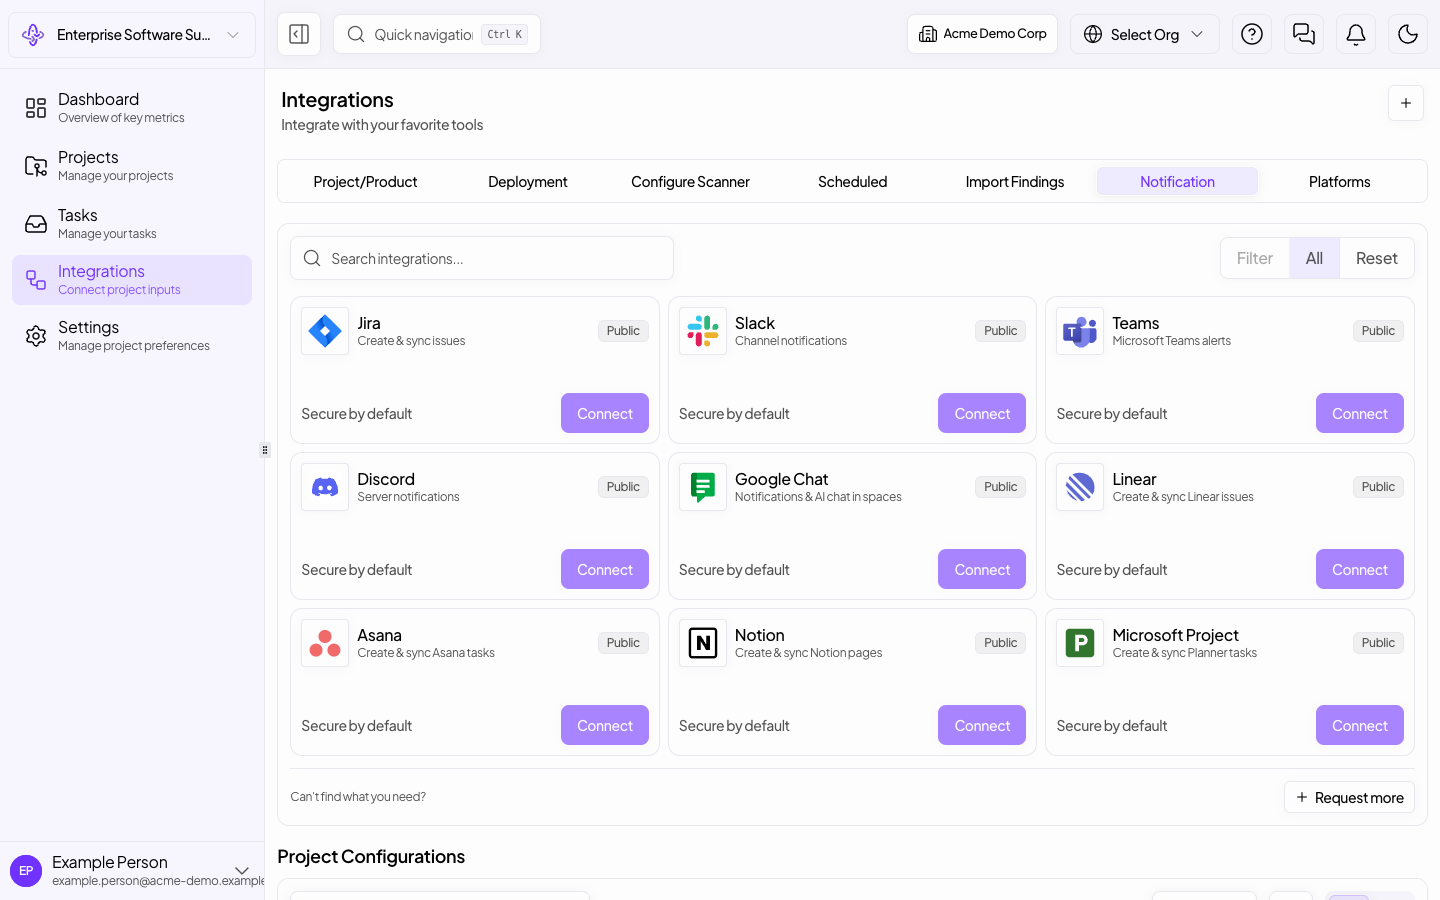
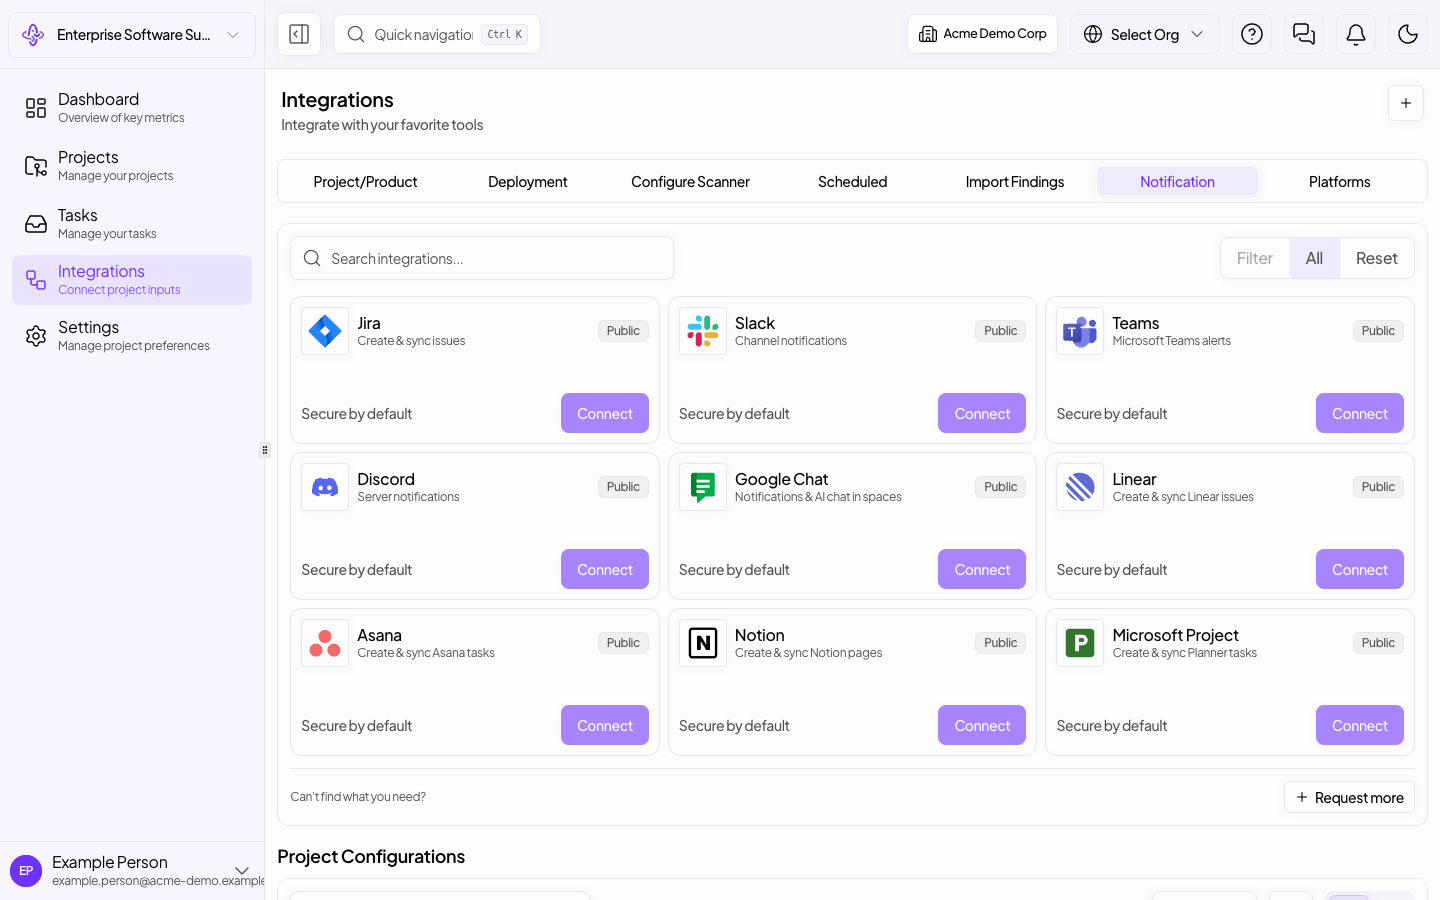
Connect Linear, Asana, Notion or Microsoft Project (Planner) and choose where Safeguard creates items.
1 min7 steps
 Interactive
Supply chain security
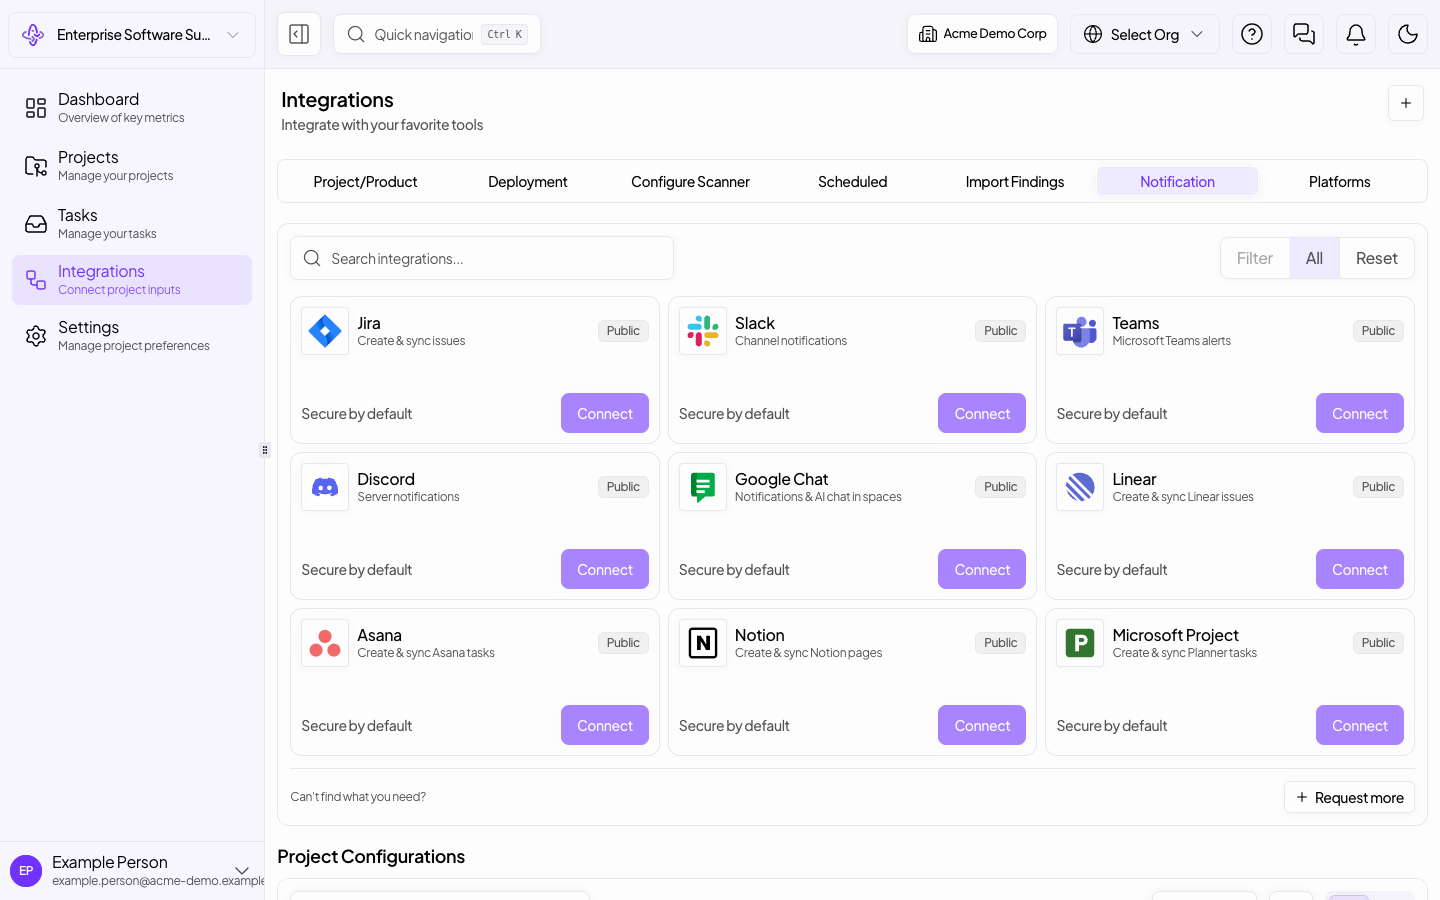
Send Safeguard alerts to a Discord channel and a Google Chat space through webhooks you create there.
1 min8 steps
 Interactive
Supply chain security
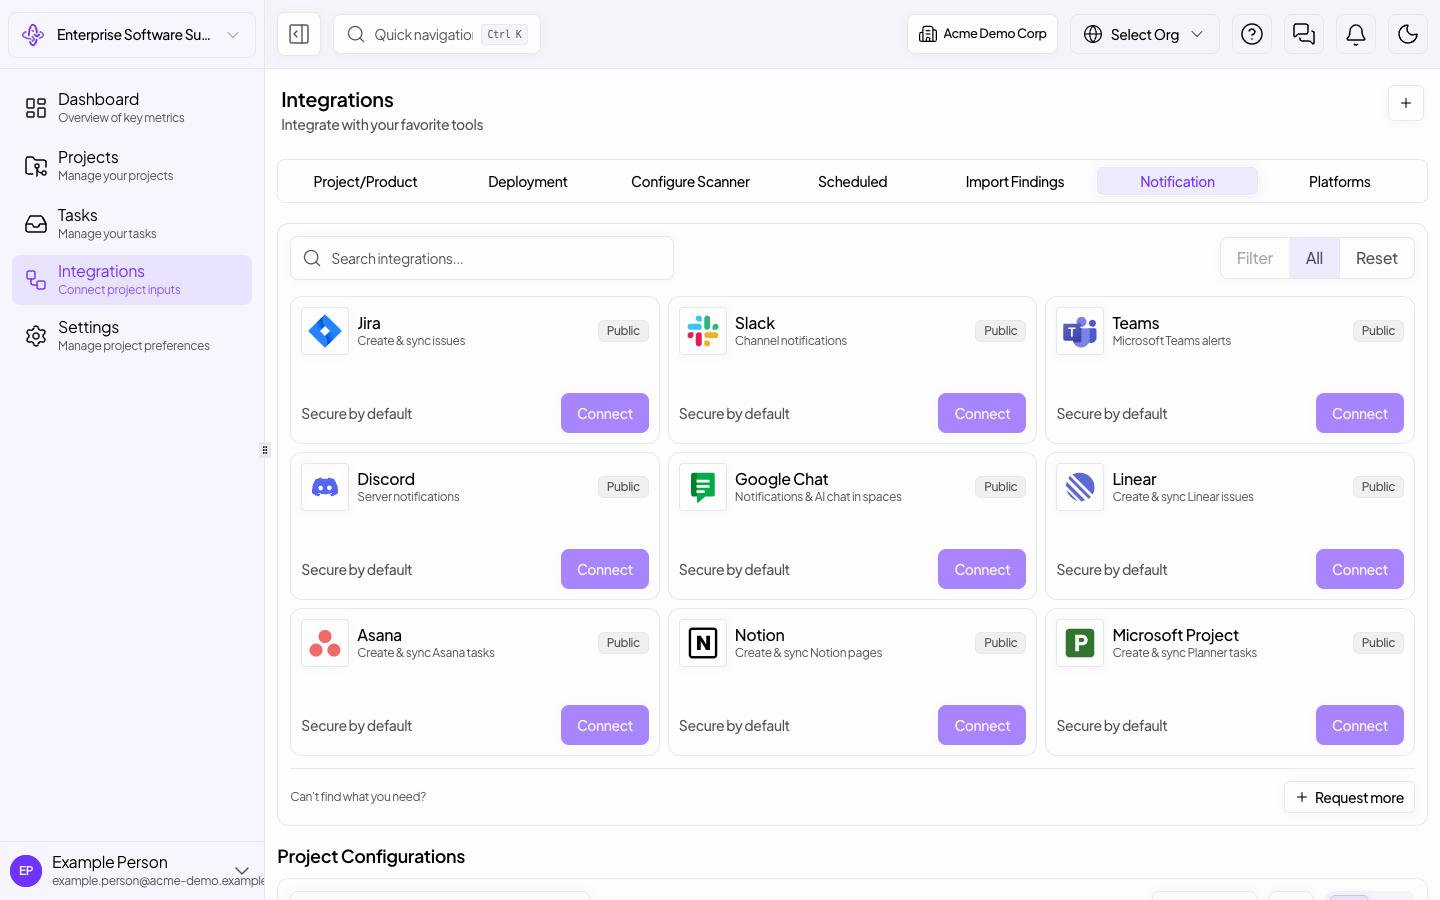
Connect Jira Cloud with an API token, choose the project, match its workflow statuses, and let code-analysis alerts open issues in it.
2 min8 steps
 Interactive
Supply chain security
Connect Microsoft Teams with an incoming webhook or a Bot Framework app, pick the team and channel, and choose which categories reach chat.
1 min8 steps
 Interactive
Supply chain security
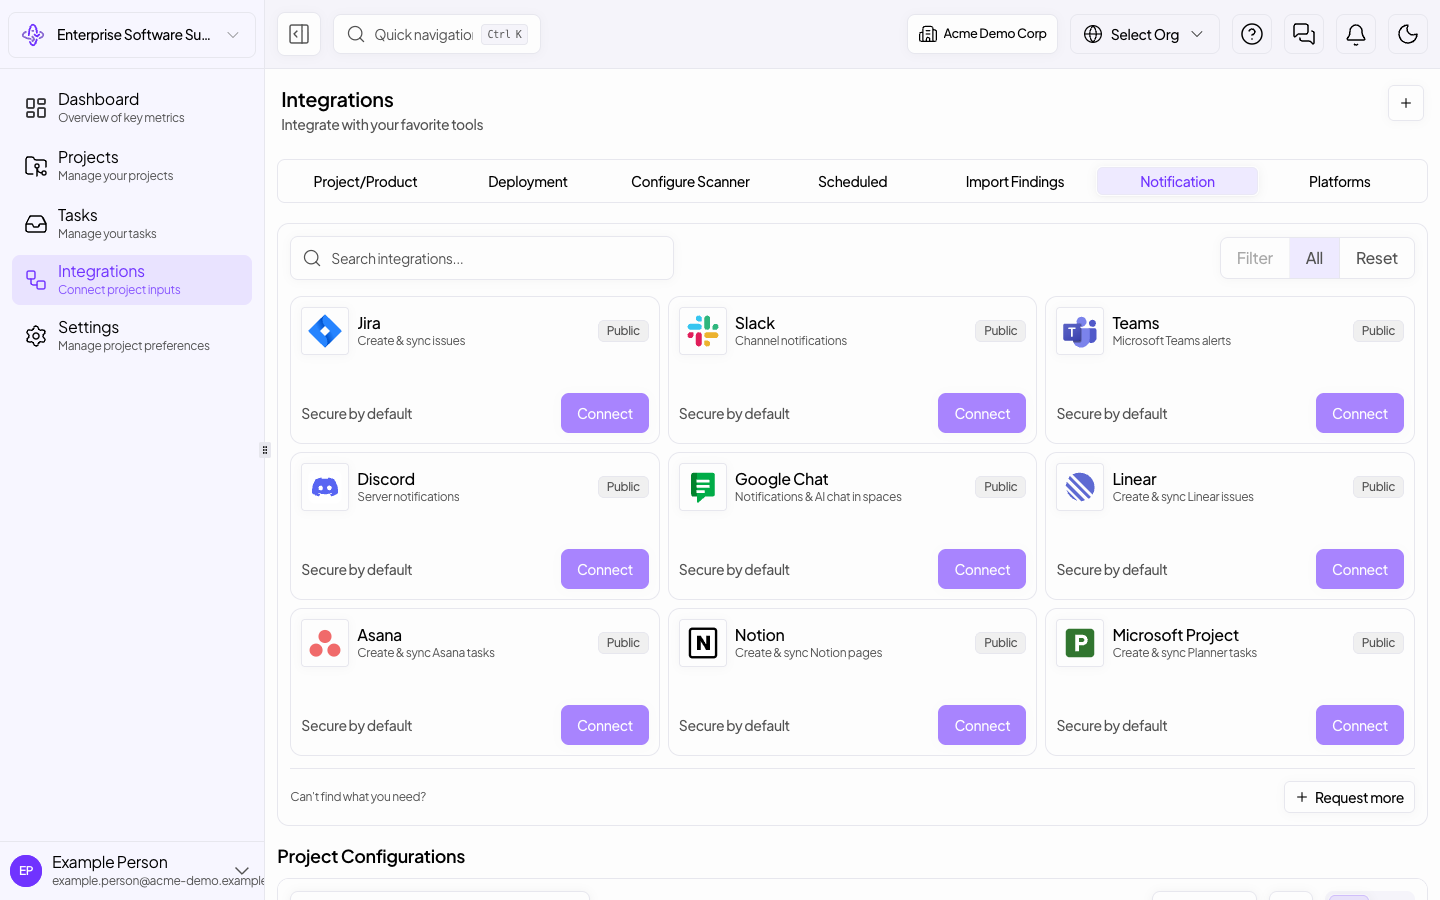
Connect Slack for alerts in a channel, choose which categories reach chat, and link your Slack account so @Safeguard answers your questions in Slack with your own access.
2 min9 steps
 Interactive
Supply chain security
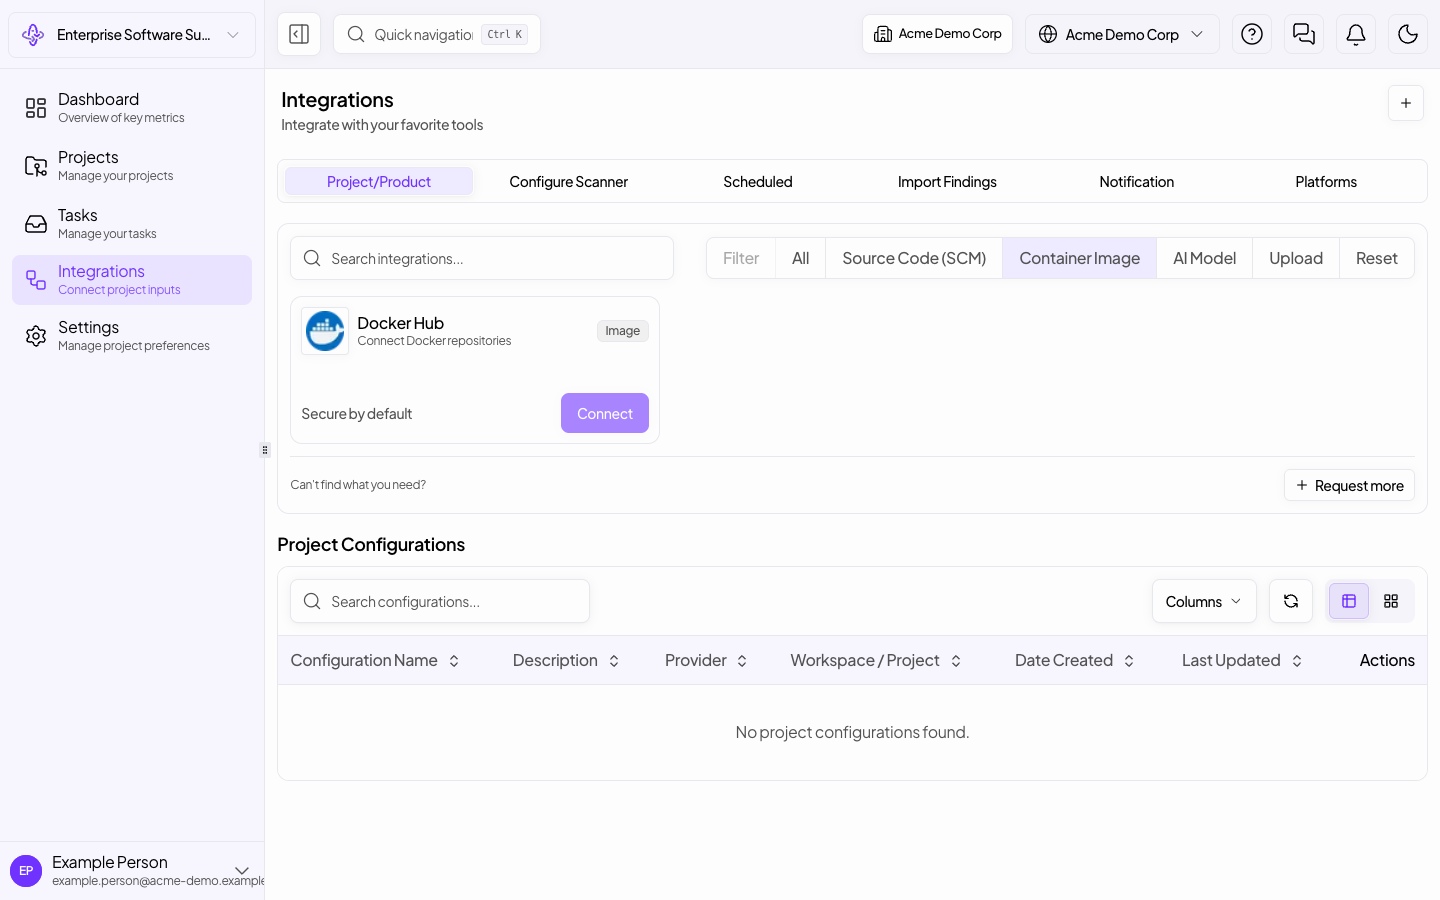
Connect a Docker Hub image, scan it, and see vulnerabilities in its operating system packages and its application libraries, with the fixed versions.
50 sec7 steps
 Interactive
Supply chain security
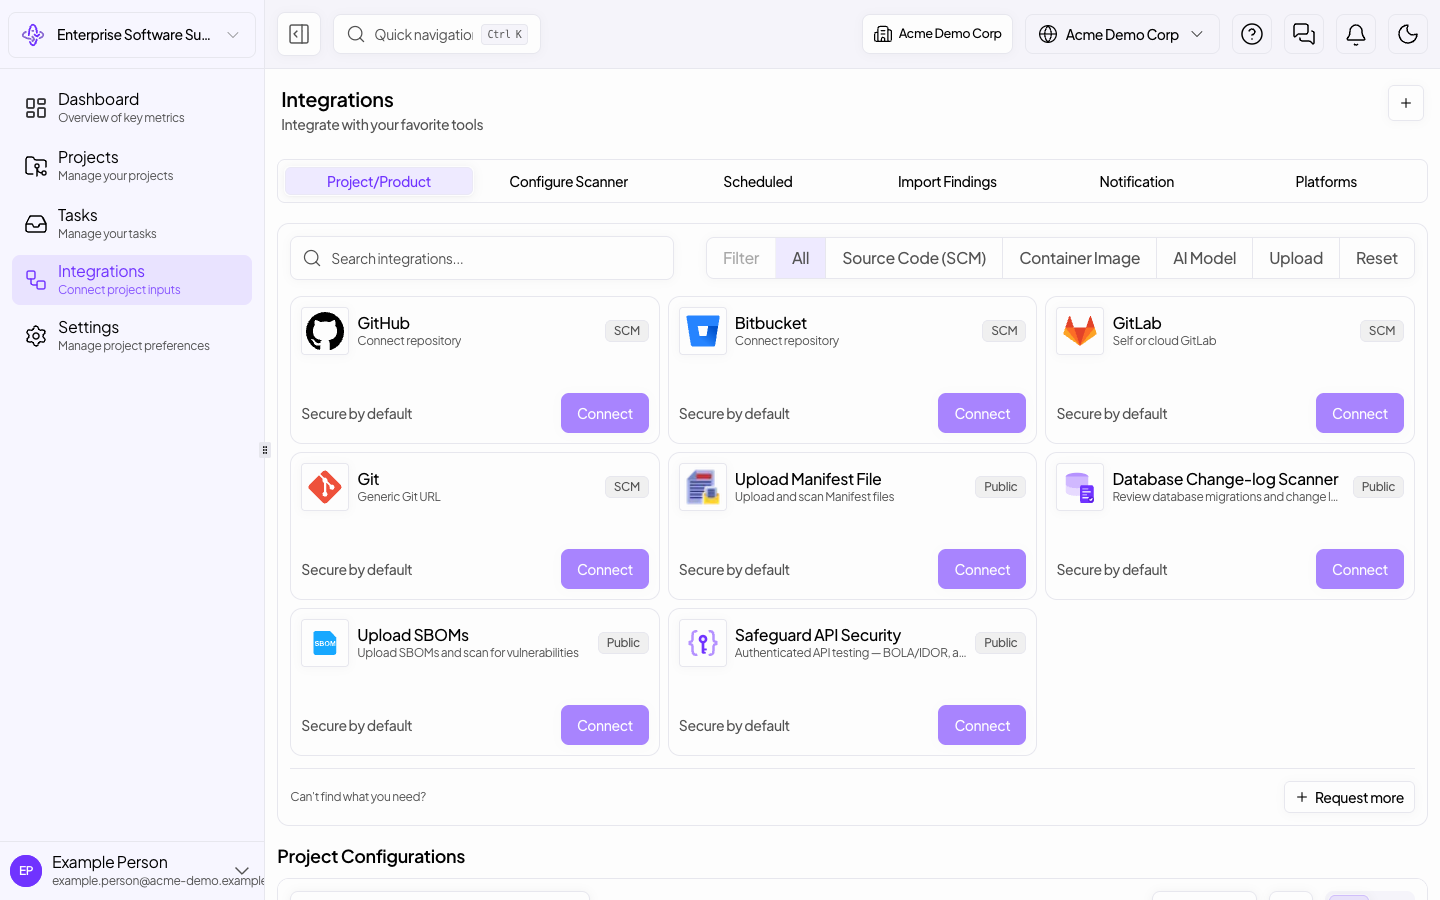
Upload an OpenAPI spec, give Safeguard a token, and get API findings such as broken object level authorization, each with the request that proves it.
1 min9 steps
 Interactive
Supply chain security
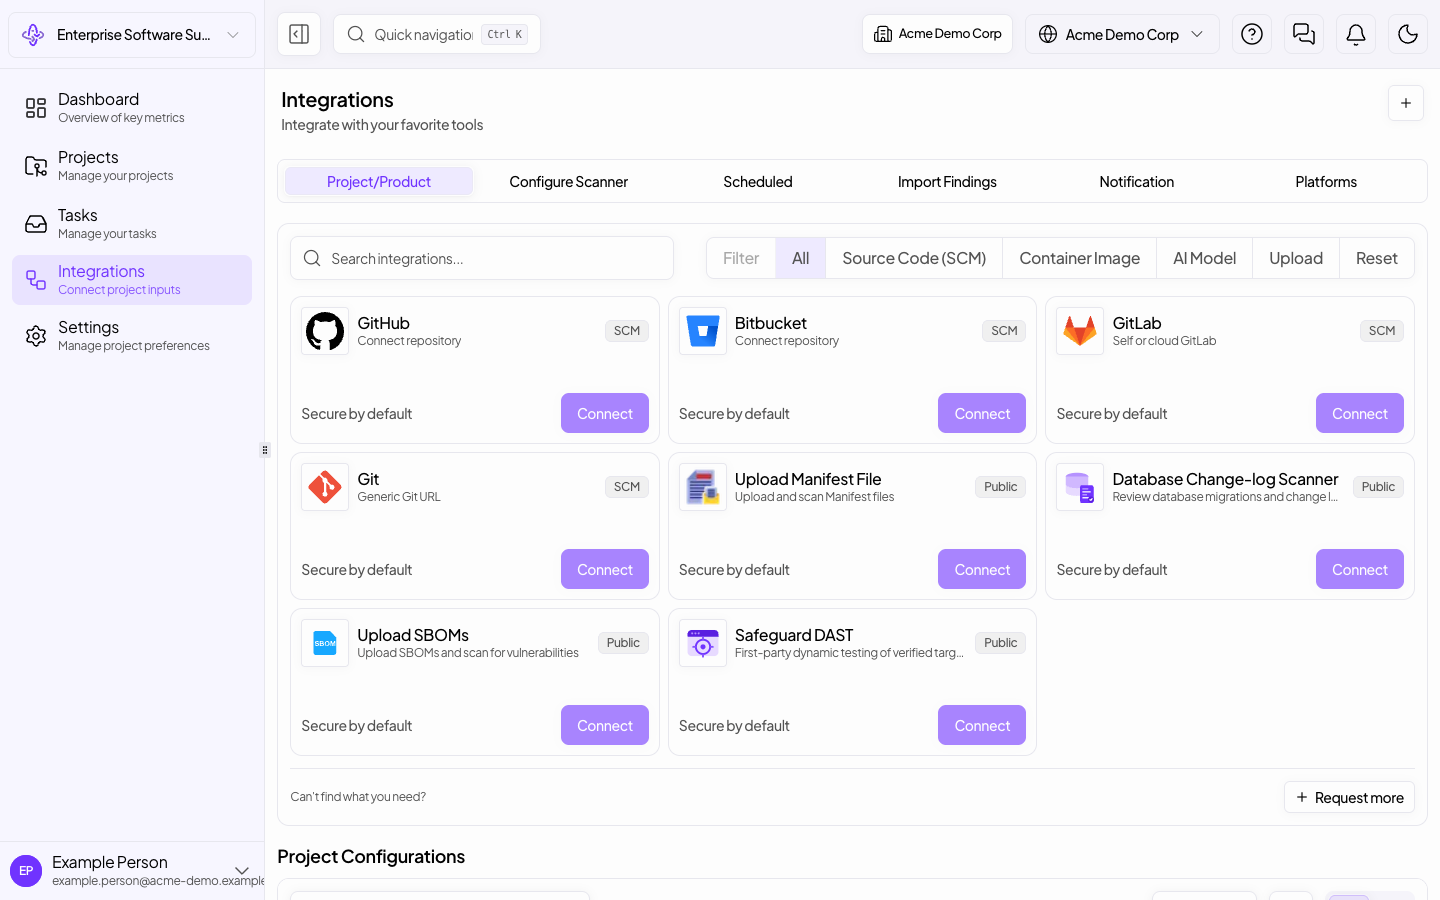
Point Safeguard DAST at a web app you own, sign in with a test account, launch a scan, and read verified findings with the request and response that prove them.
1 min9 steps
 Interactive
Supply chain security
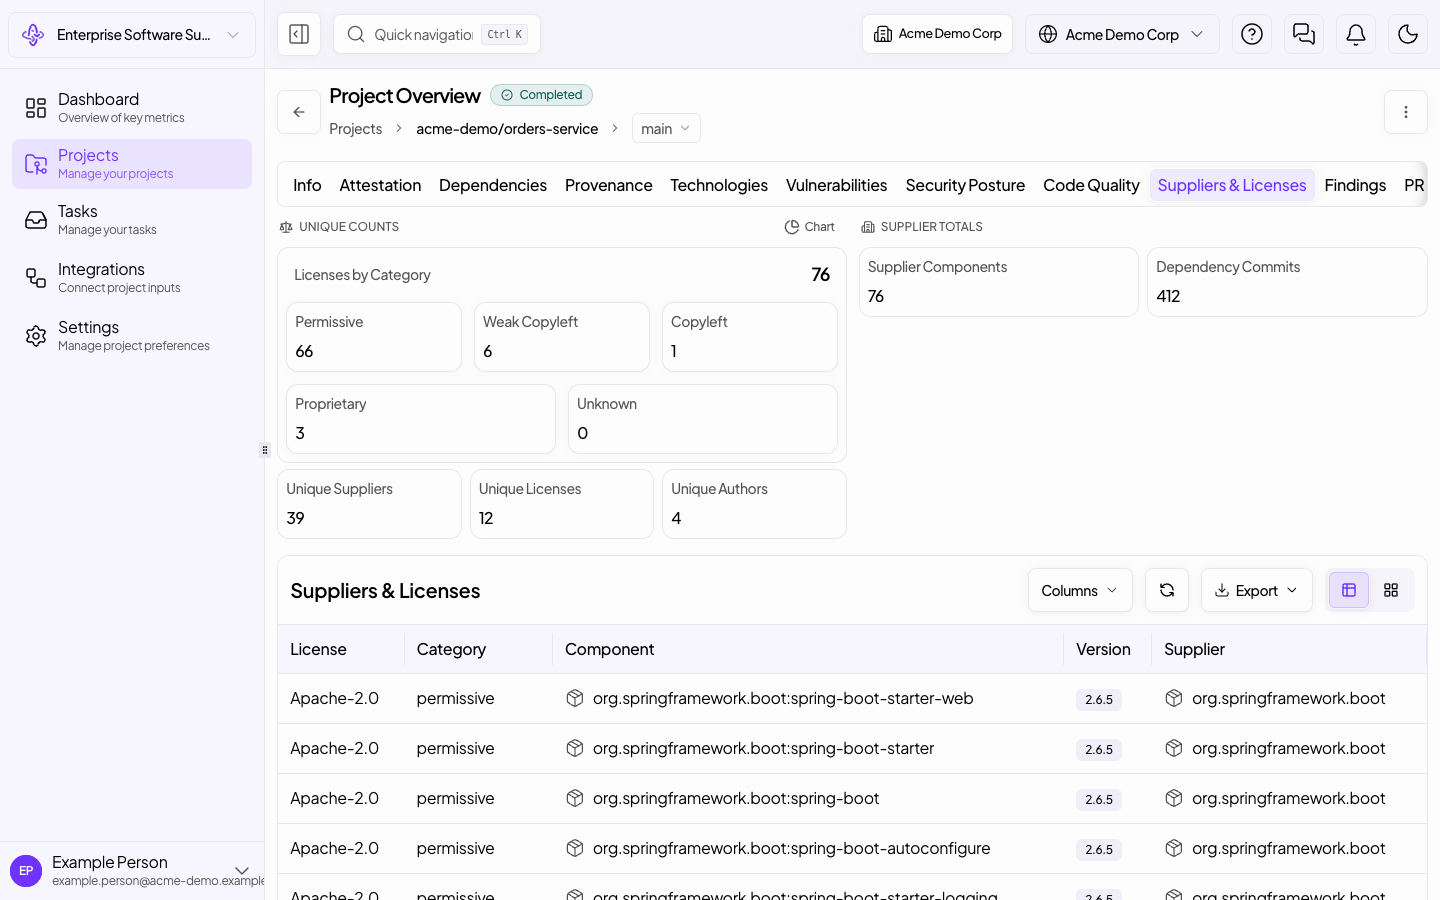
See the license of every component, find copyleft licenses that carry obligations, and read what each license requires before you ship.
50 sec7 steps
 Interactive
Supply chain security
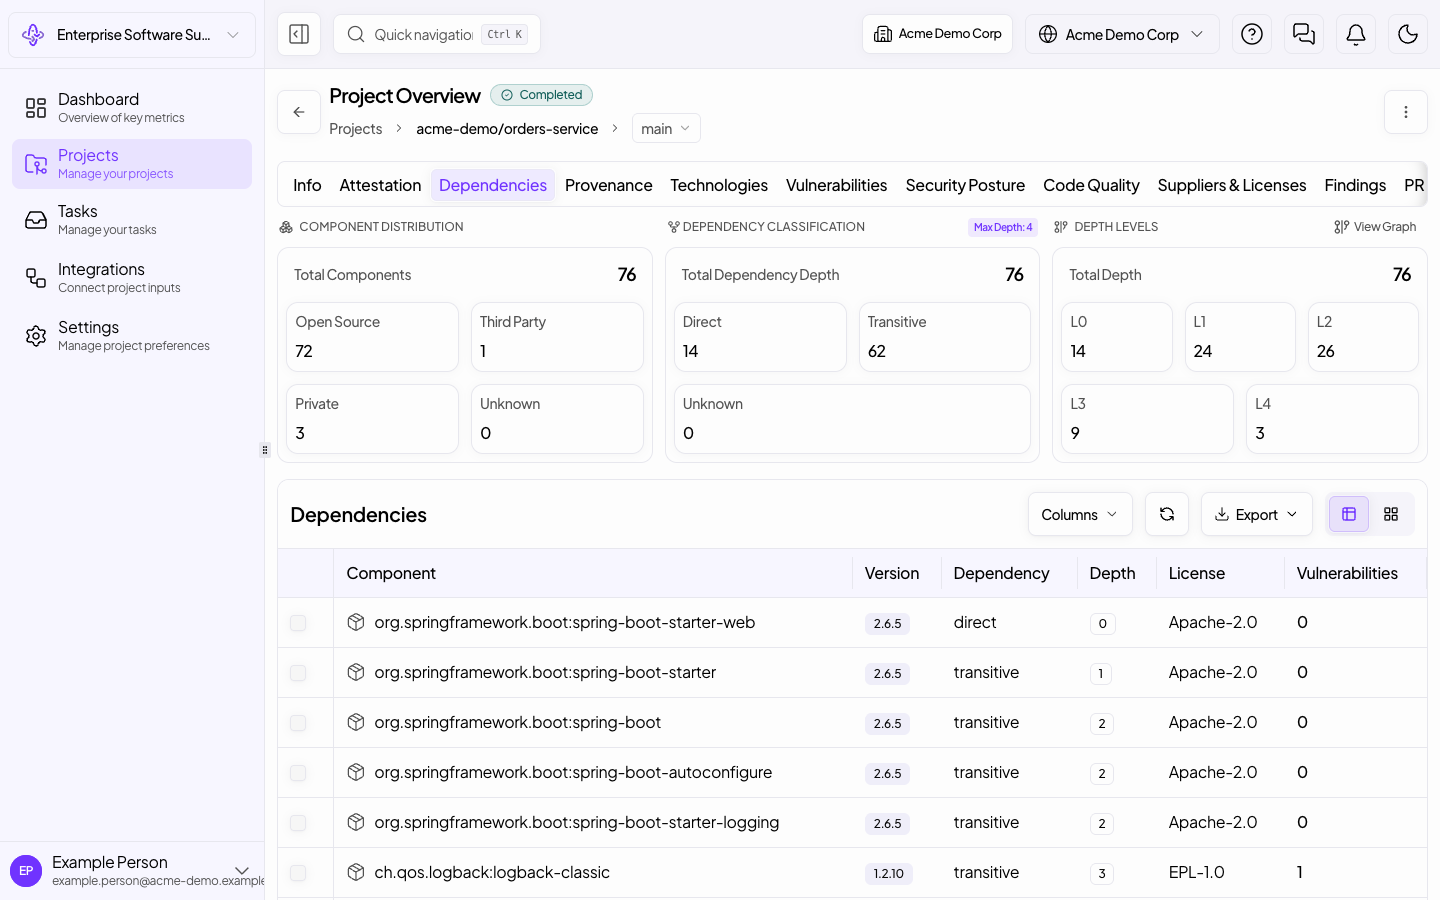
See every open-source component in a project, direct and transitive, with its depth, license and vulnerabilities, and trace where each one comes from.
50 sec7 steps
 Interactive
Supply chain security
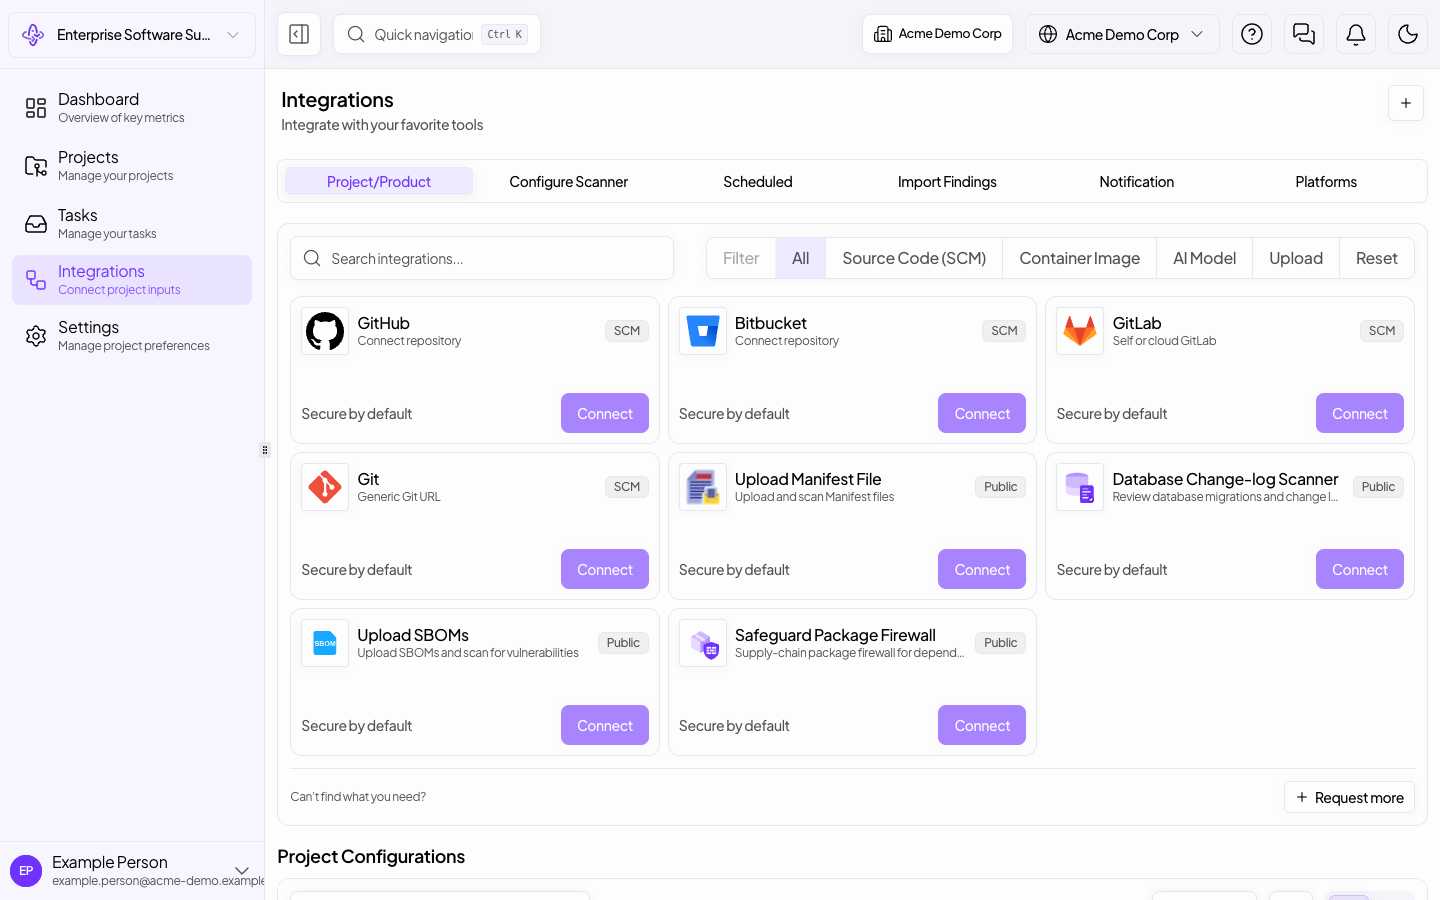
Turn on the Package Firewall and see malicious, typosquatted and dependency-confusion packages flagged in a project, with what each one does and how to remove it.
1 min9 steps
 Interactive
Supply chain security
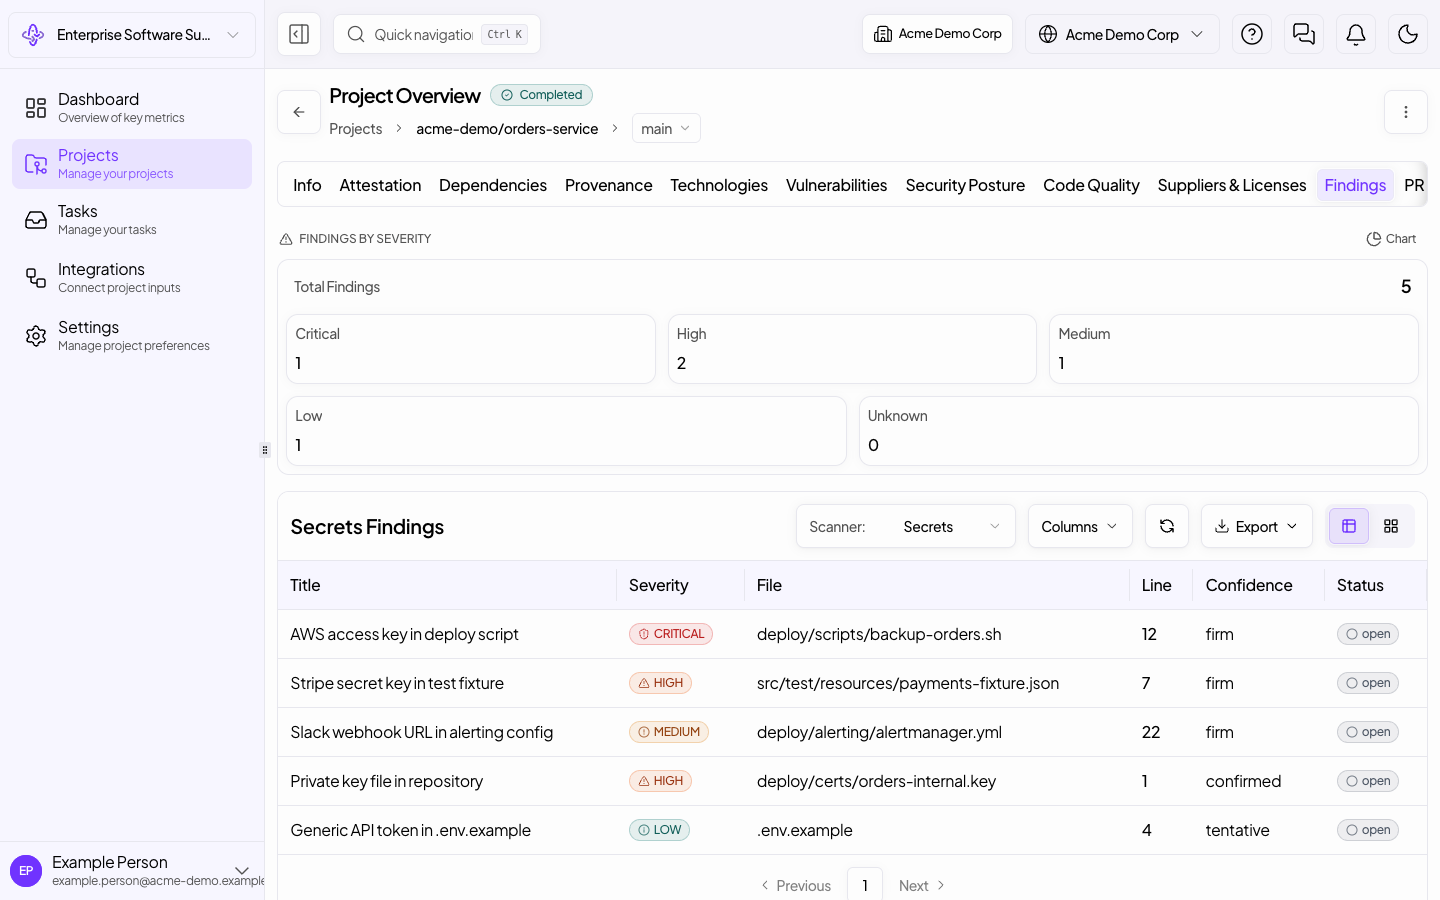
Find credentials committed to your repositories, see where each one is and whether it was verified, and follow the steps to rotate and remove it.
50 sec7 steps
 Interactive
Supply chain security
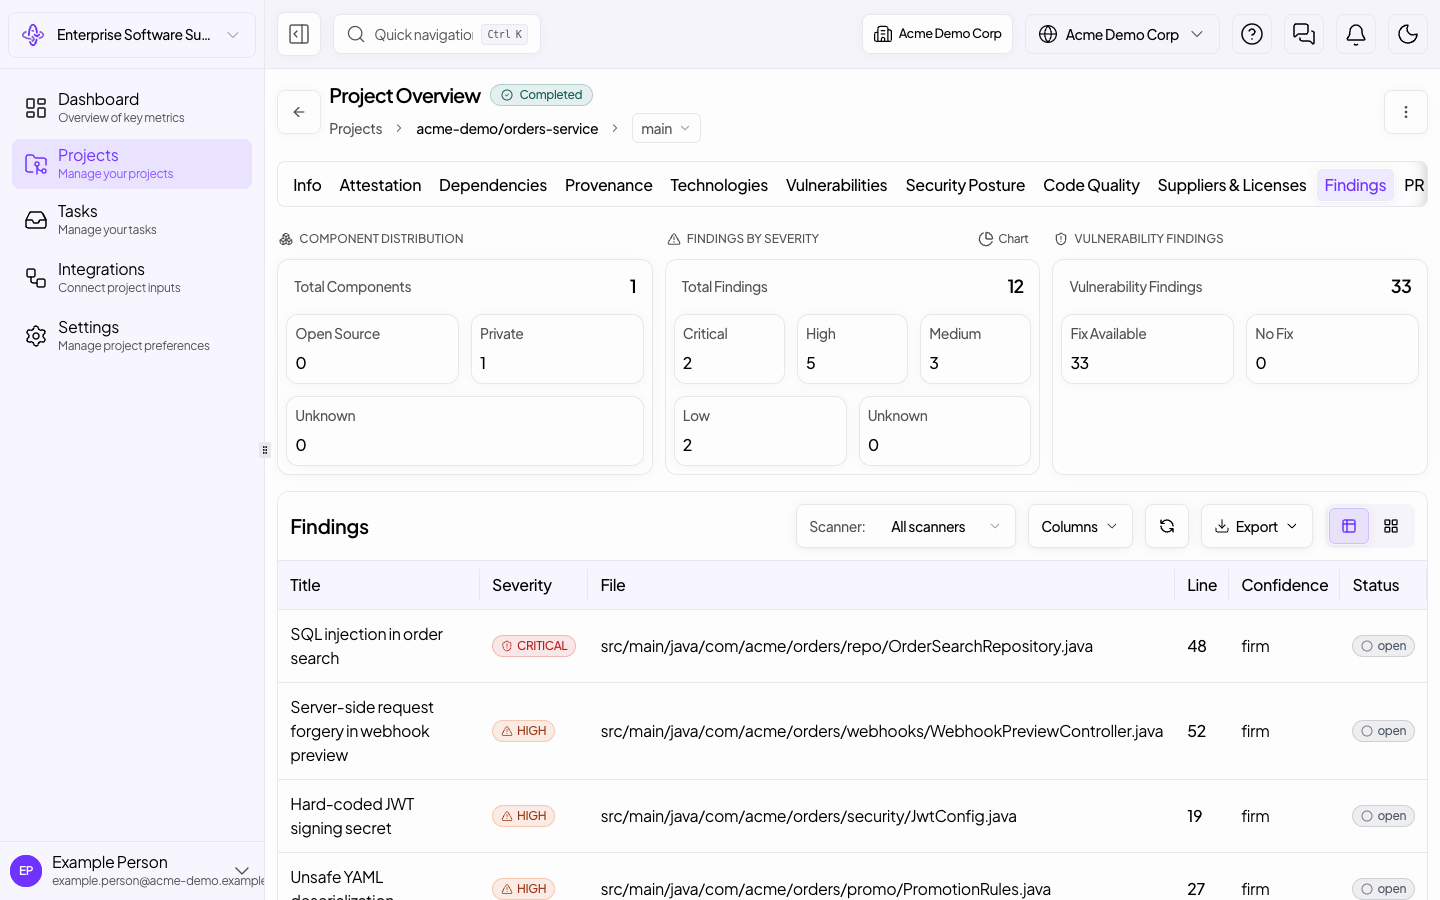
Find security flaws in your own code: each SAST finding names the file and line, traces the data from source to sink, and gives a fix.
55 sec8 steps
 Interactive
Supply chain security
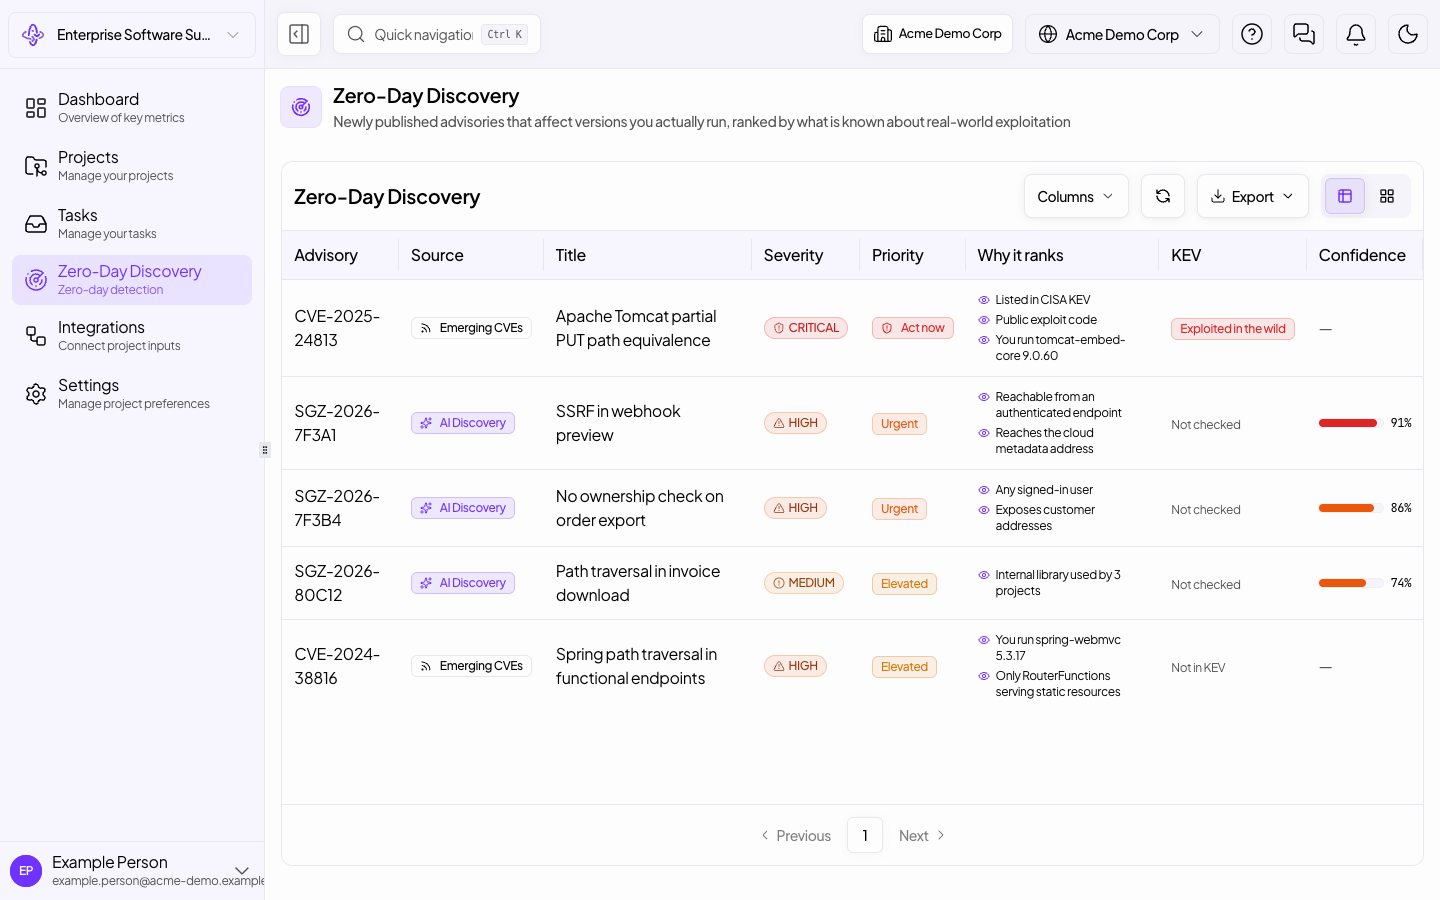
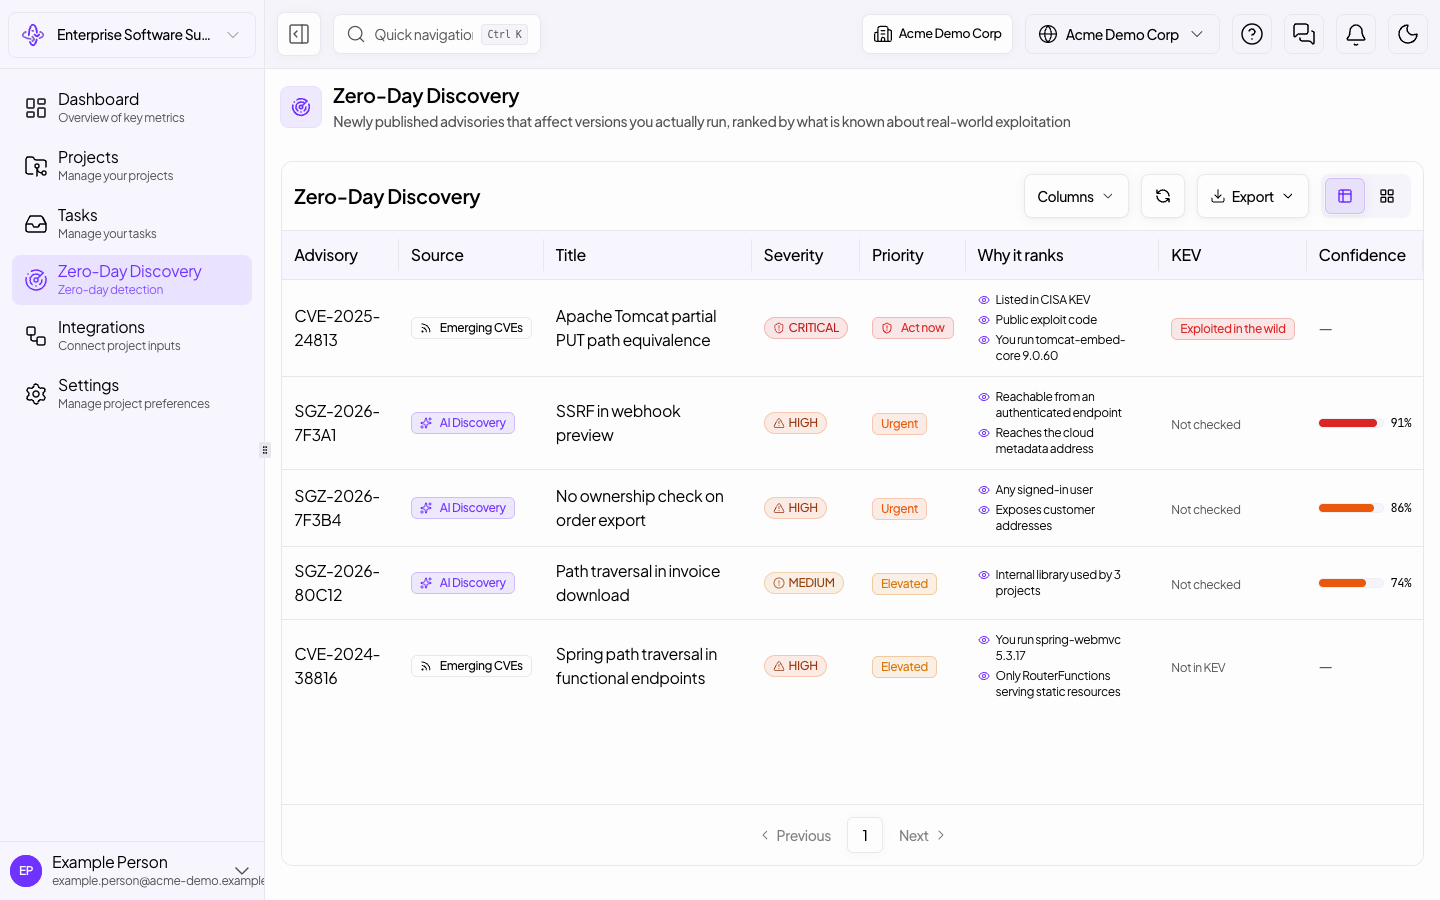
Watch newly published advisories that match the versions you run, ranked by urgency, and triage the zero-days inside a project.
55 sec7 steps
 Interactive
Supply chain security
Review vulnerabilities Safeguard found in your own code before any CVE exists: the vulnerable code, the exploit path and a ready code fix.
50 sec7 steps
 Interactive
Supply chain security
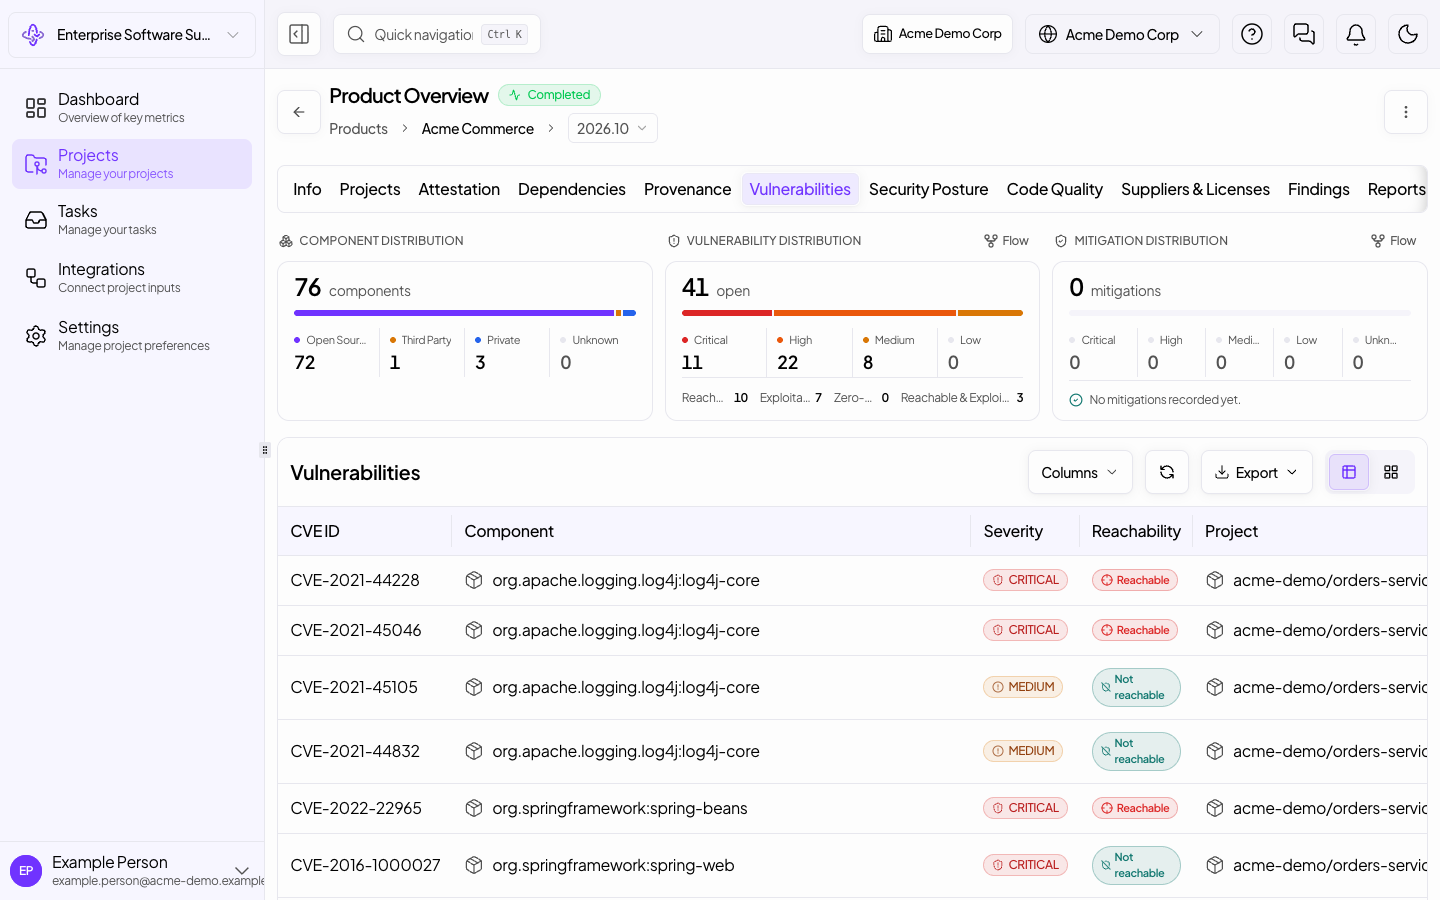
Triage vulnerabilities across a product's projects: filter by severity, read KEV, EPSS and SLA, and move a finding through its status workflow.
1 min8 steps
 Interactive
Supply chain security
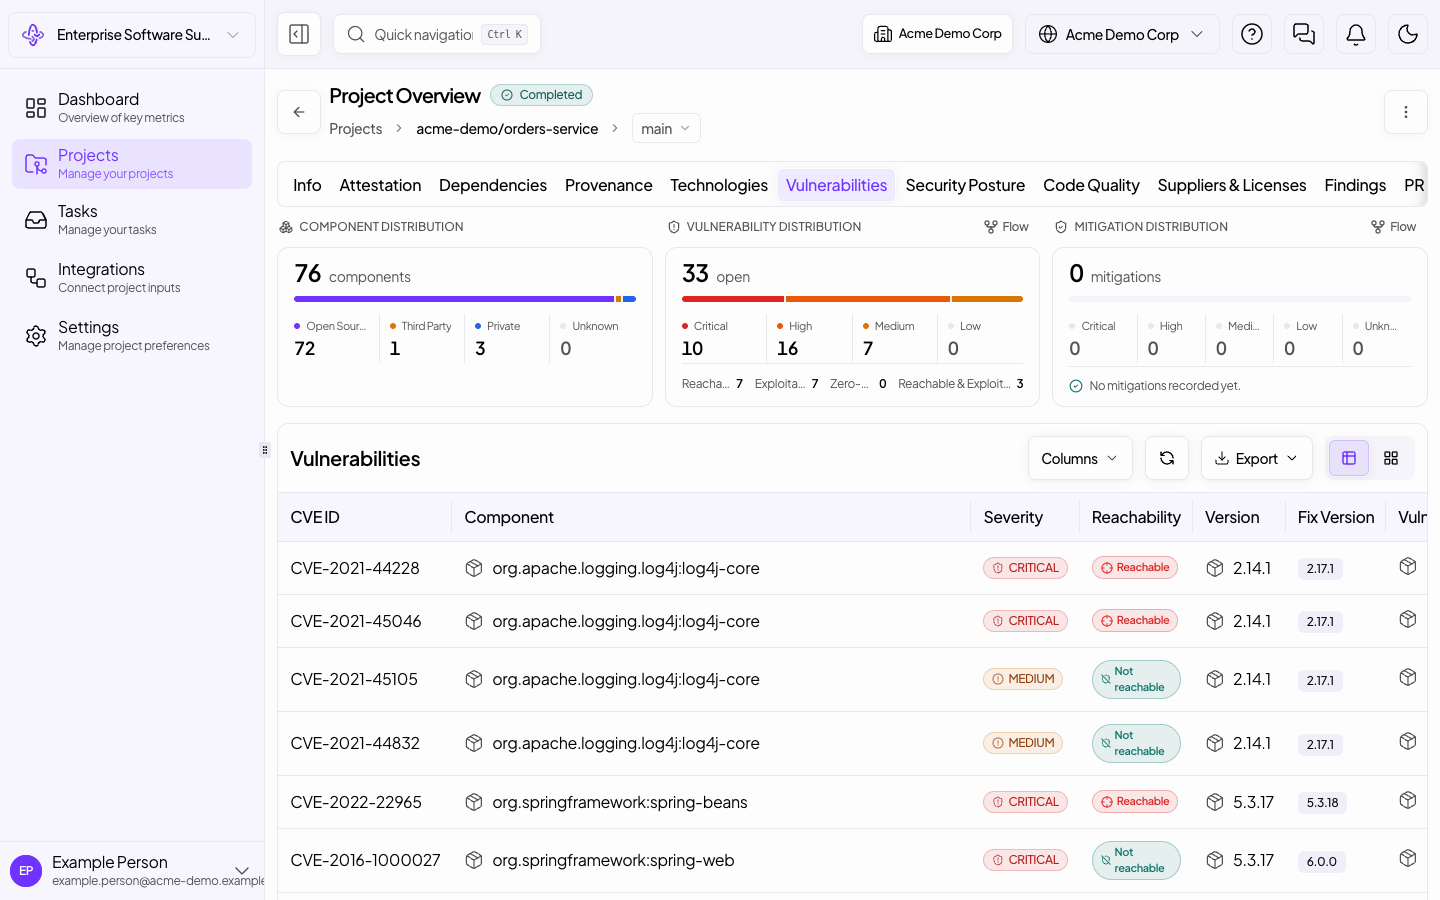
Go from reachable findings to the ones an attacker can use, rung by rung: dependency affected, code reachable, environment applicable, application exploitable.
1 min7 steps
 Interactive
Supply chain security
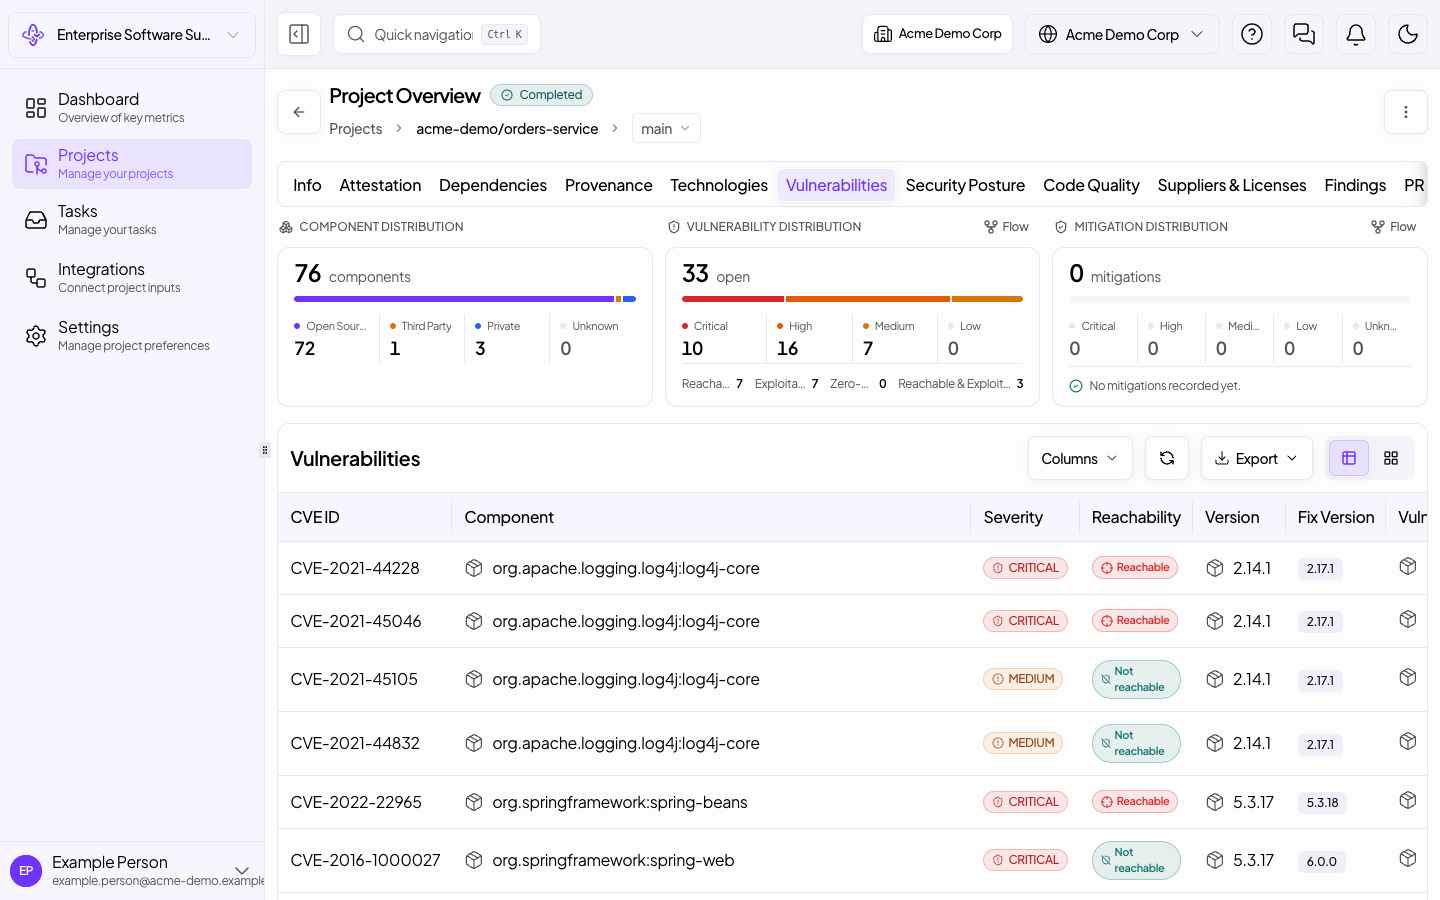
See which open-source vulnerabilities your code can actually reach, how many drop out, and the evidence behind each verdict.
55 sec7 steps
 Interactive
Gold
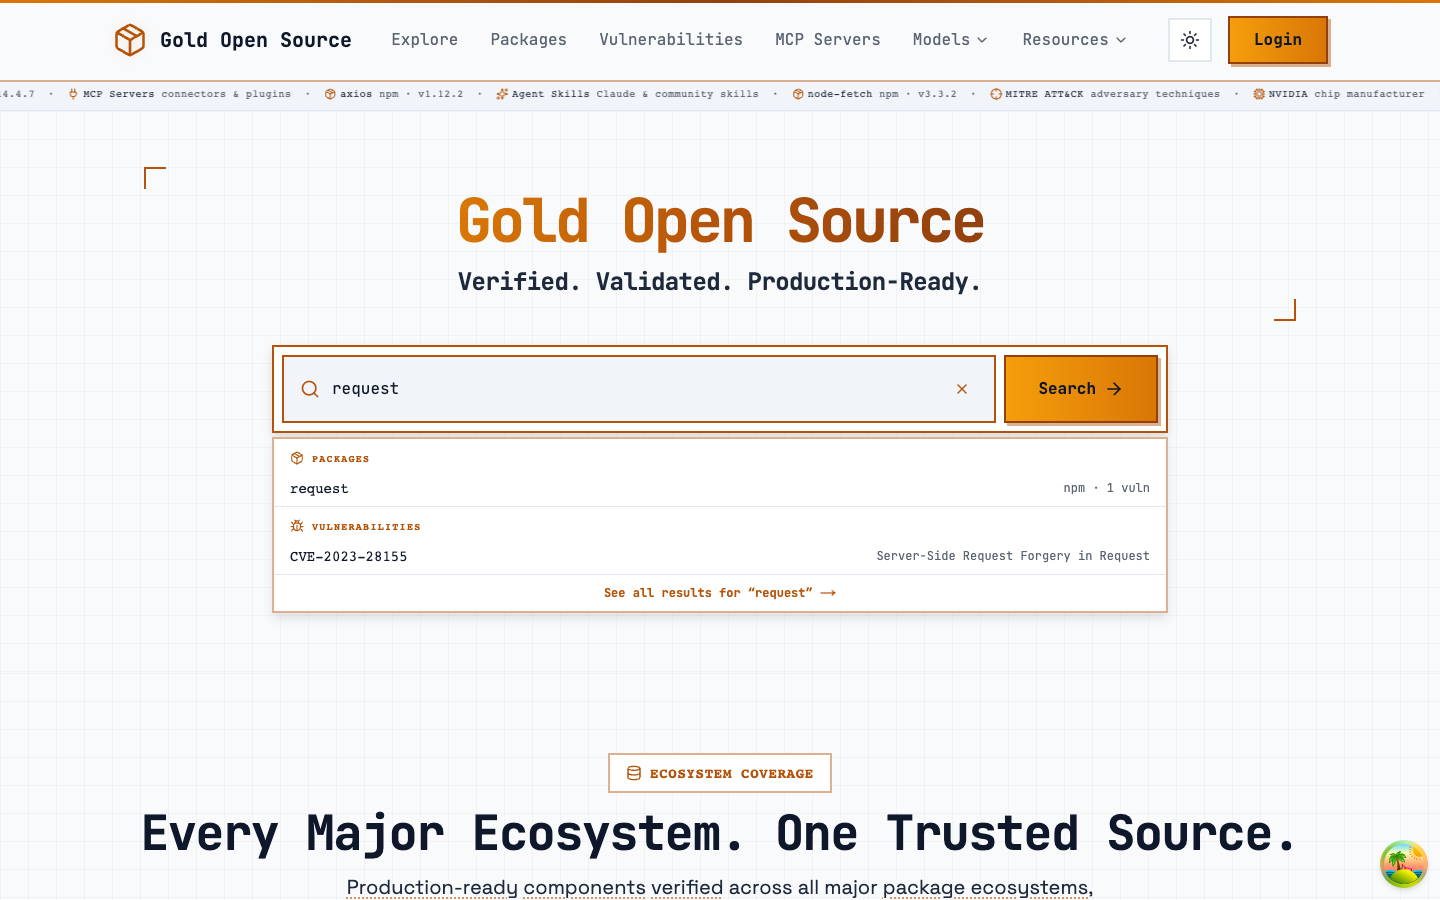
Look up a package on Gold Open Source, see why it falls short, and pick a Gold alternative with no known vulnerabilities that passed malware screening.
2 min8 steps
 Interactive
Osm
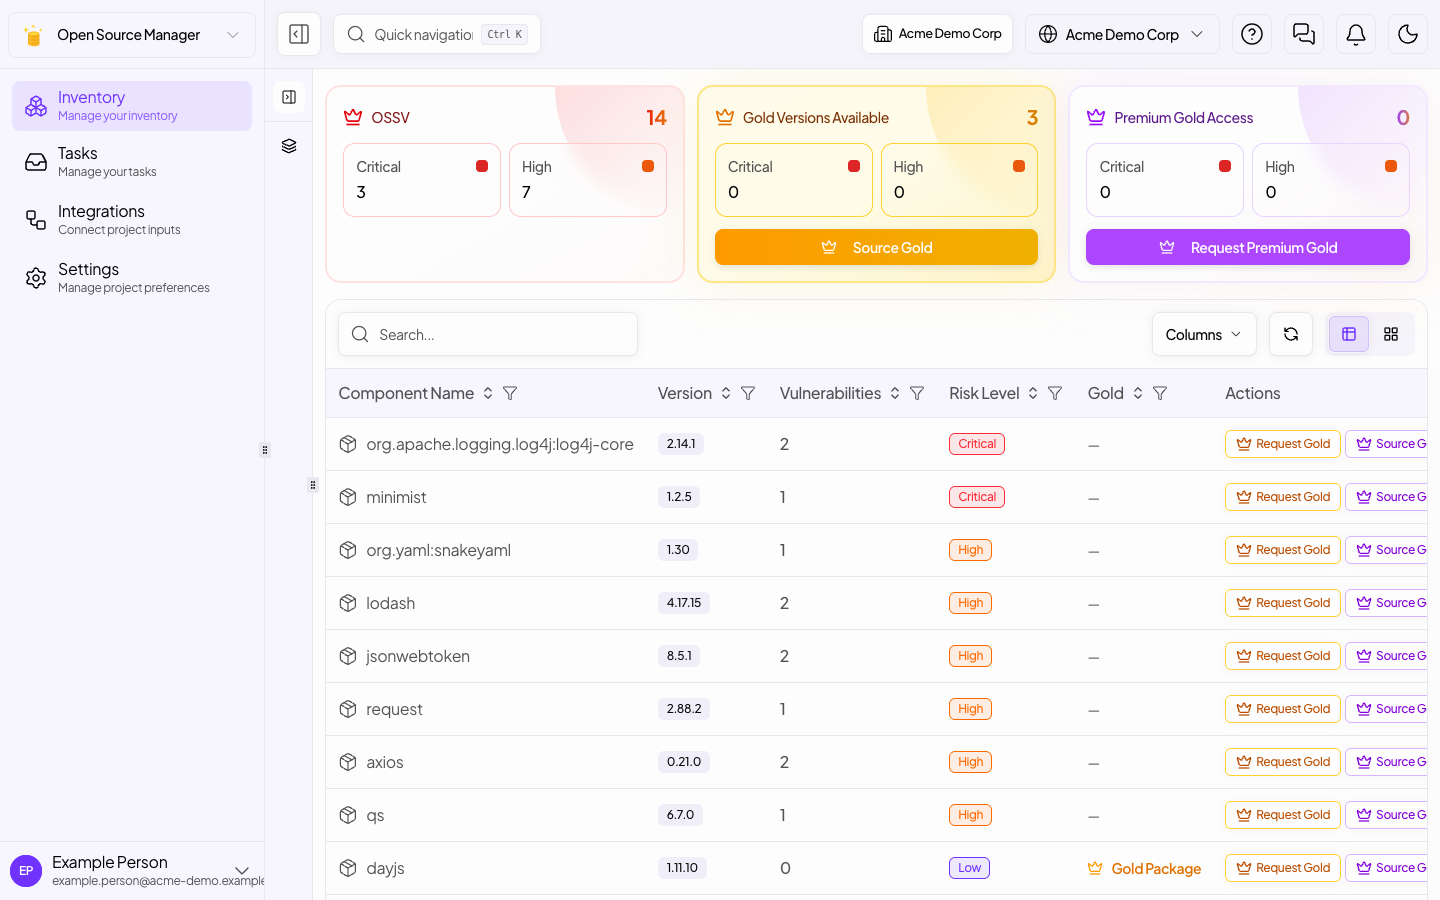
From your open source inventory, request a Gold version of a vulnerable package, or of every vulnerable package at once.
2 min8 steps
 Interactive
Supply chain security
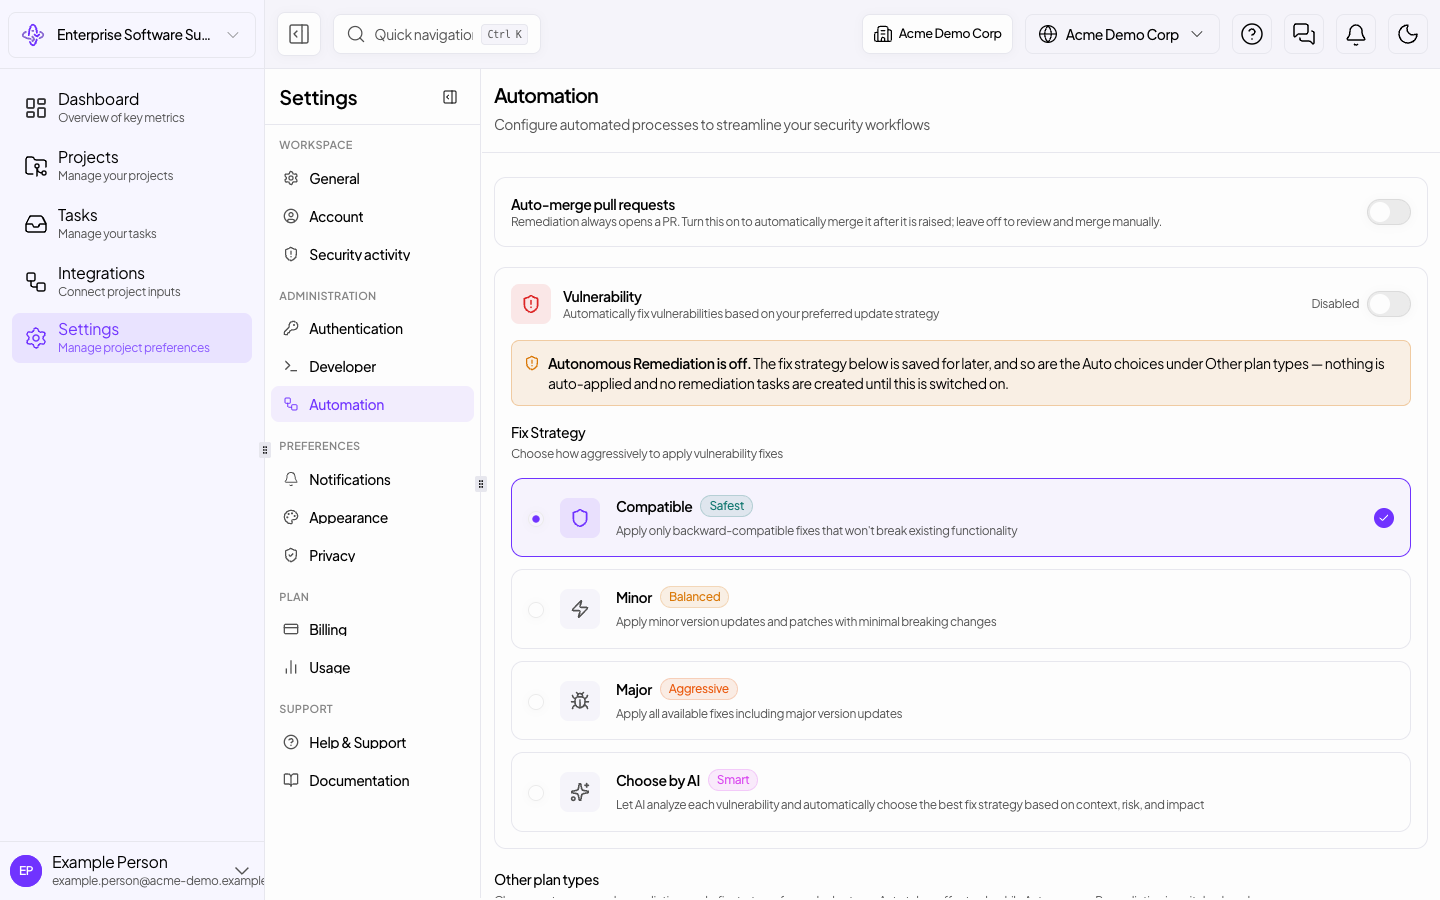
Set how Safeguard fixes each kind of issue: a strategy for vulnerabilities and for eight other plan types, each Manual or Auto.
2 min8 steps
 Interactive
Supply chain security
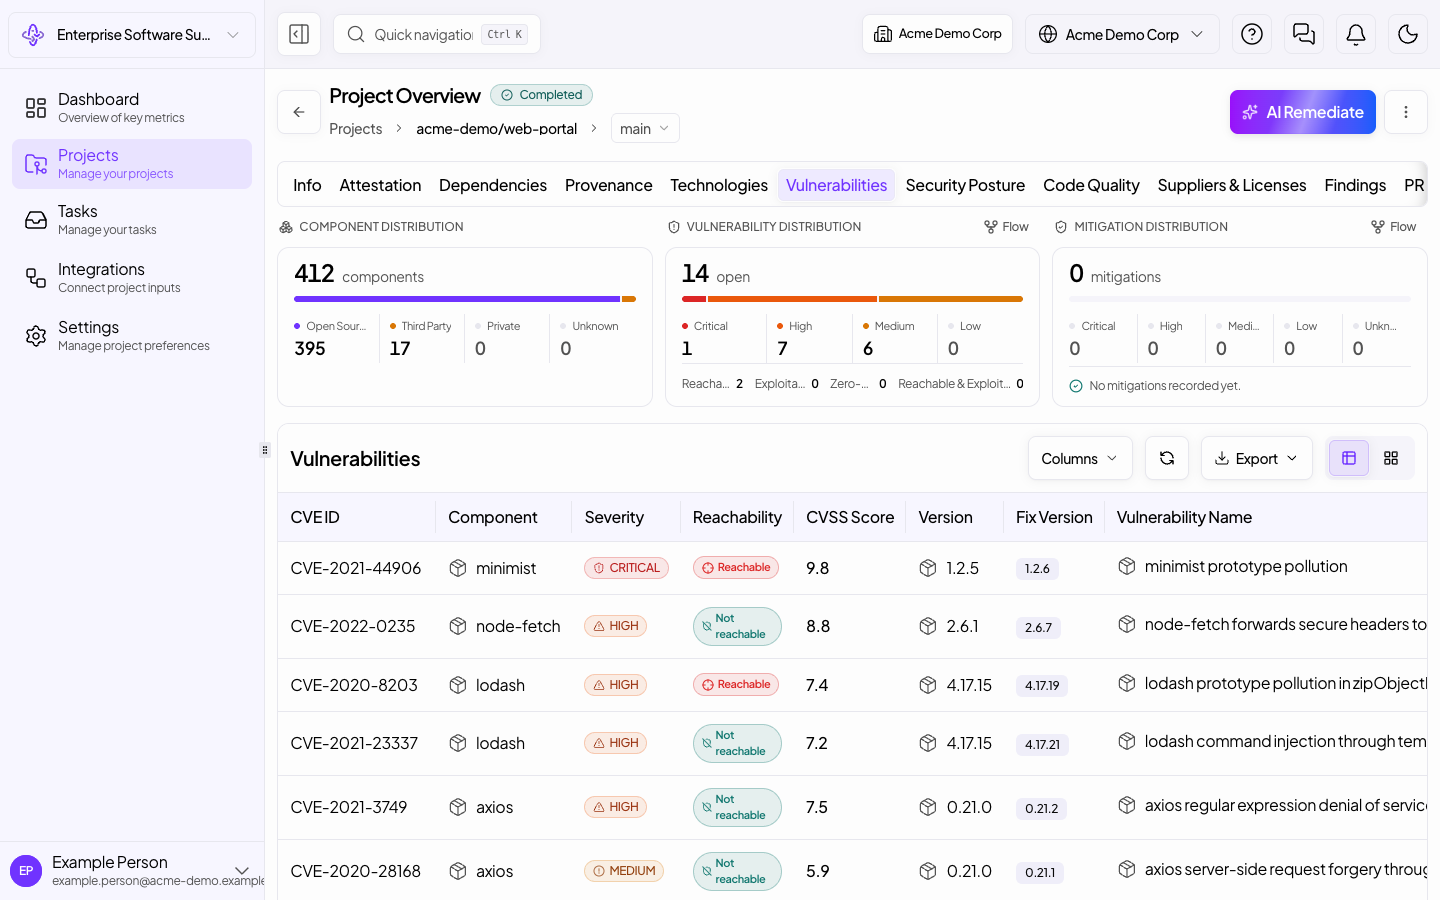
See which vulnerable packages have a fixed release today, compare compatible, minor and major upgrade plans, and start the fix.
2 min8 steps
 Interactive
Supply chain security
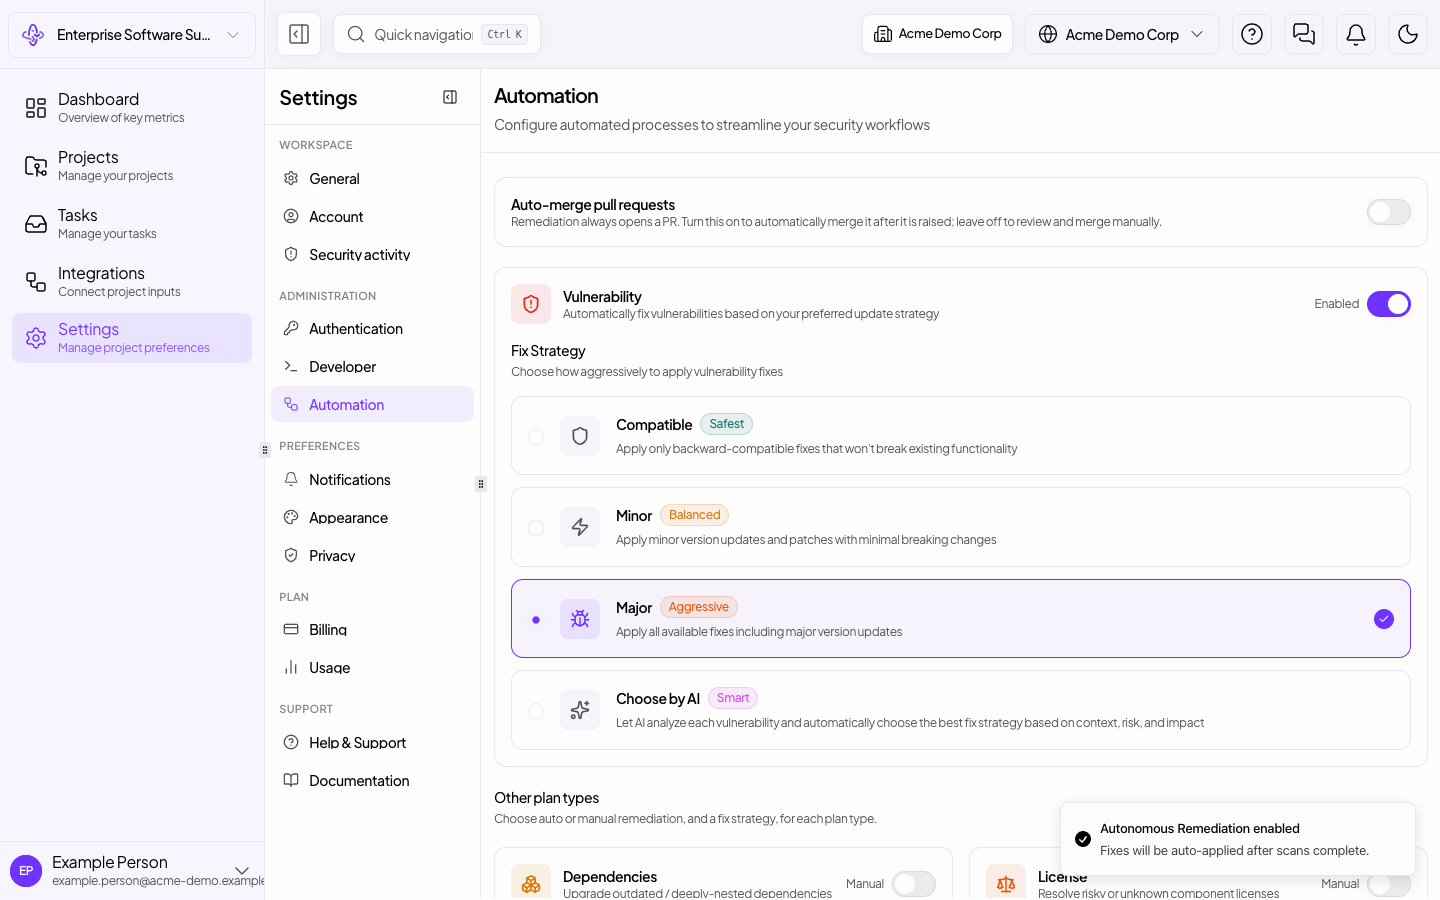
Turn on Autonomous Remediation, run AI Remediate across every project in a product, and review one pull request per project.
2 min8 steps
 Interactive
Compliance
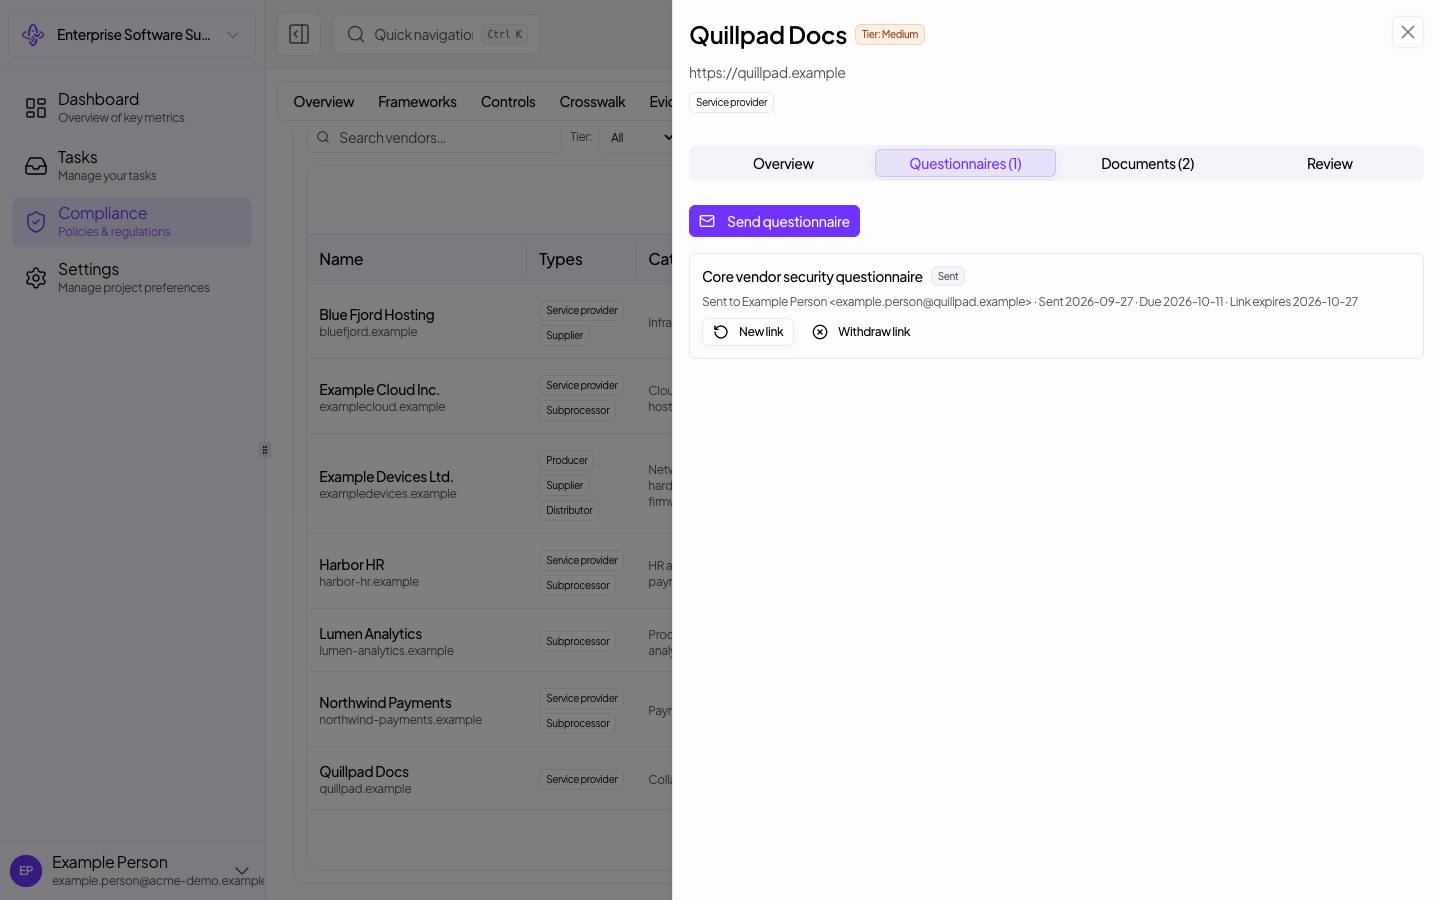
When a contract ends, withdraw the vendor's open questionnaire link, file its data deletion confirmation, and record a review with the outcome Terminated.
1 min7 steps
 Interactive
Compliance
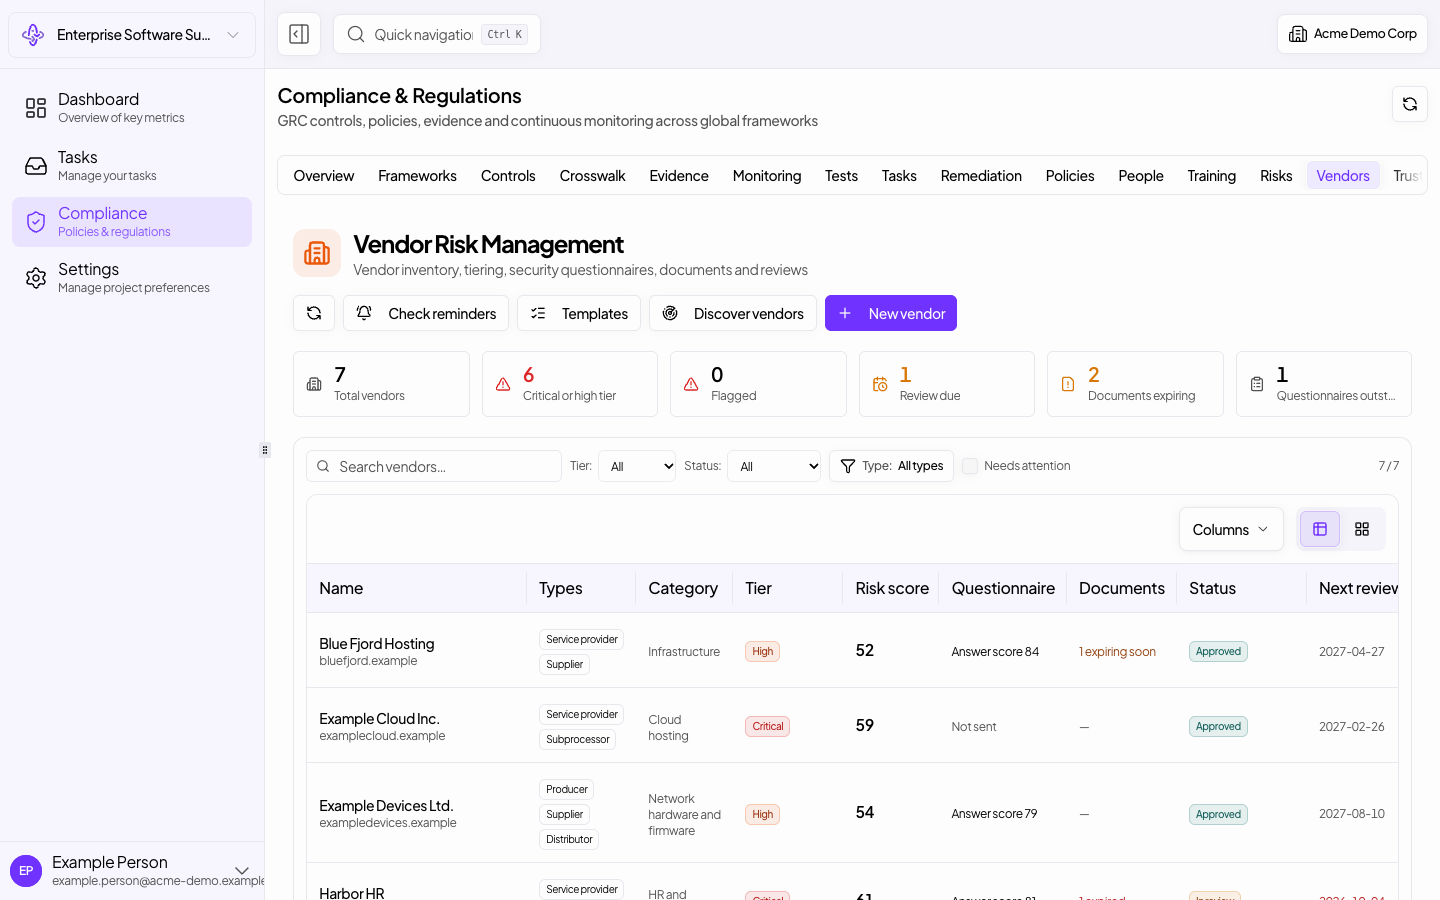
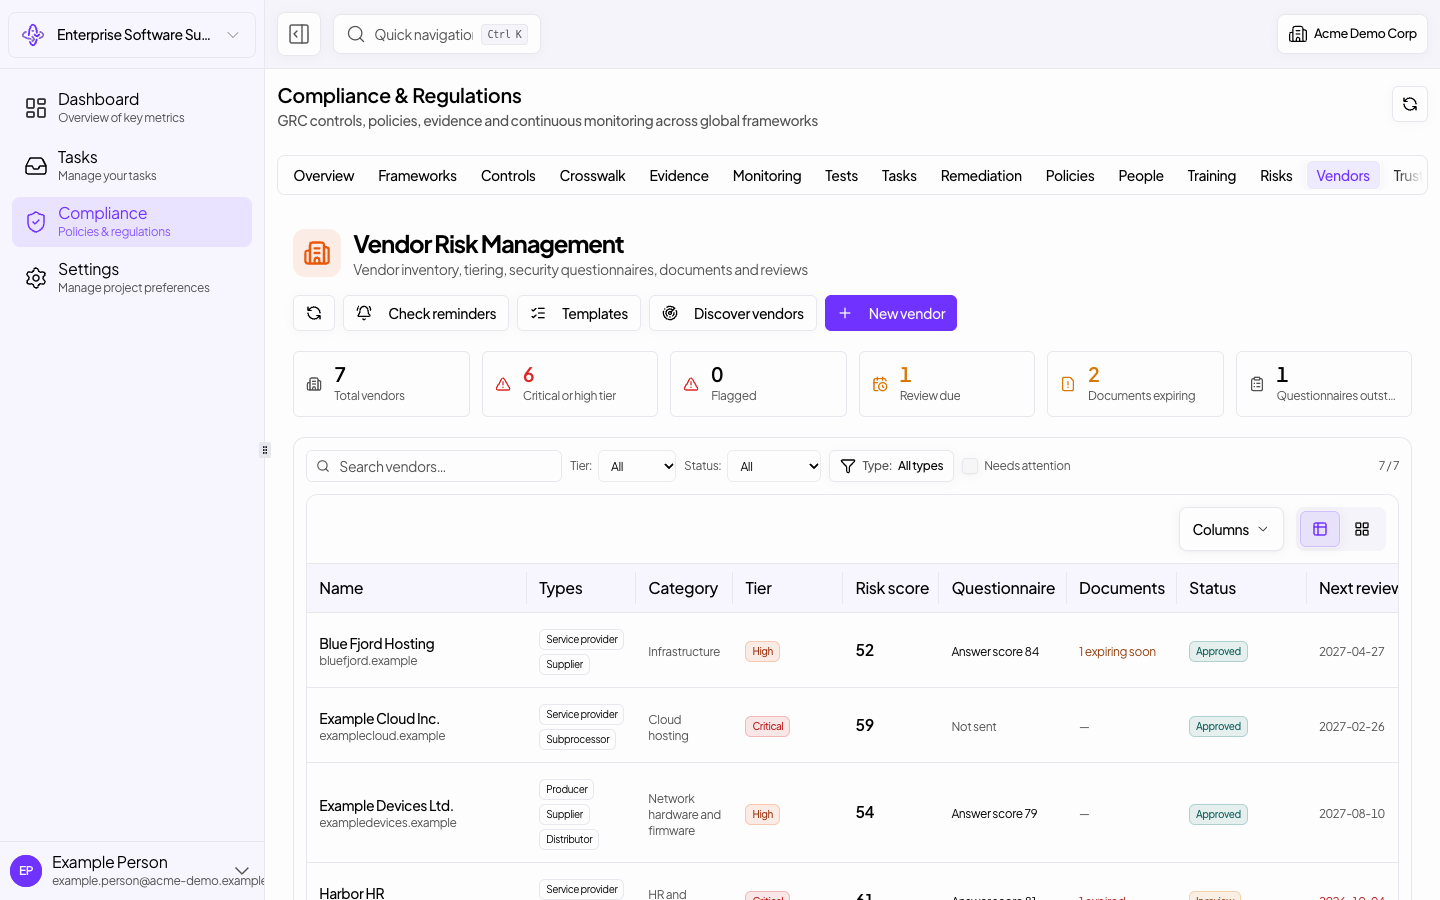
Each vendor has a review cadence. See the reviews that are due, record a review with its outcome, and let the daily reminder check do the chasing.
1 min8 steps
 Interactive
Compliance
Find the apps your people sign in to through your identity providers, import the ones that are vendors, ignore the rest, and add TPRM companies that are not in the register yet.
2 min9 steps
 Interactive
Tprm
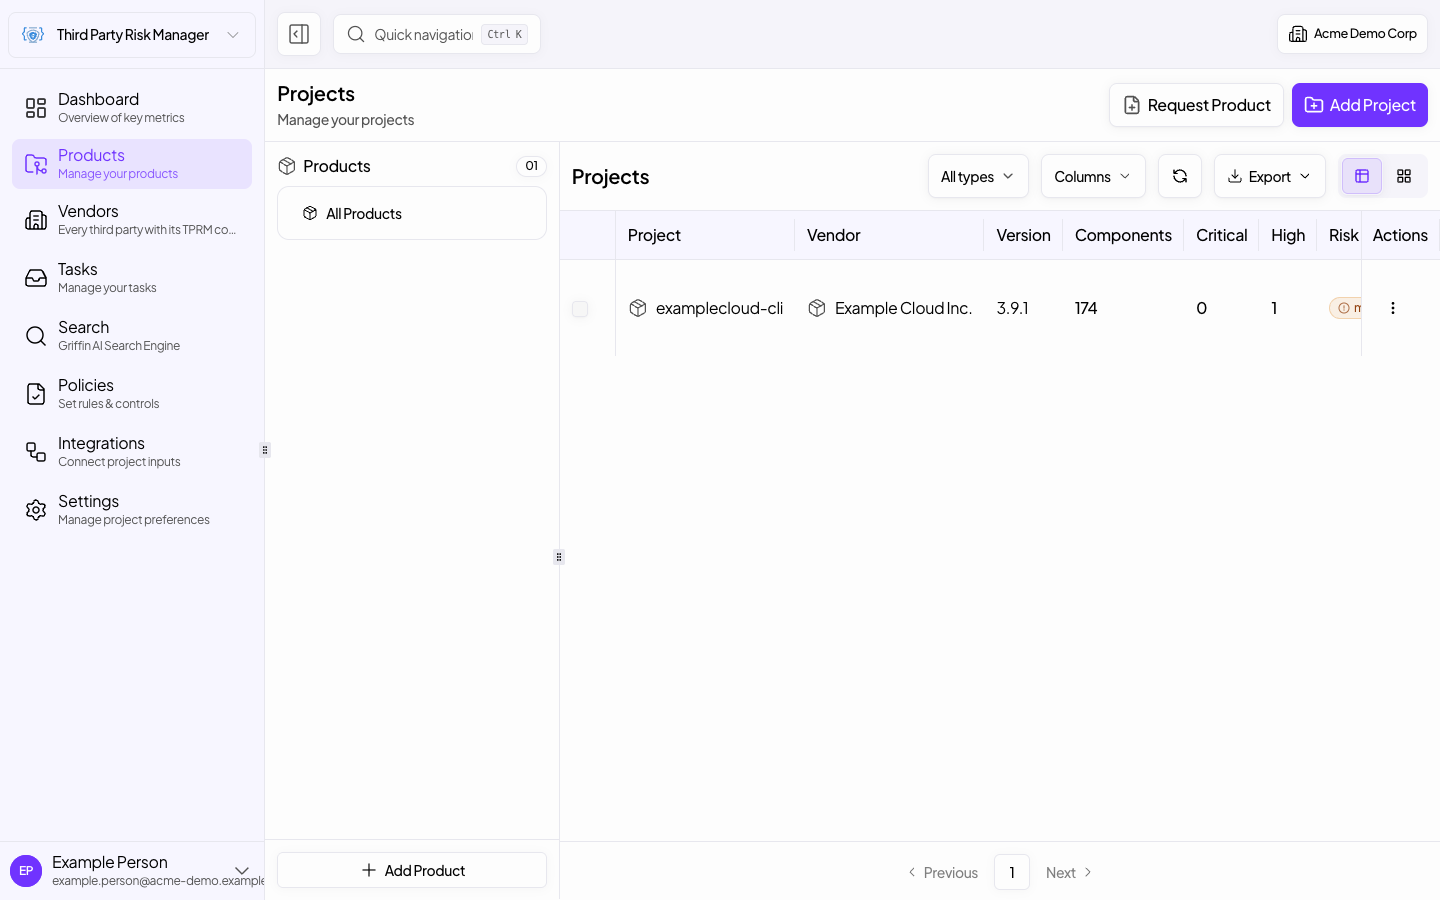
In TPRM, request a product and its projects from a supplier, follow the request, and see the shared product's projects and vulnerabilities under the vendor.
2 min9 steps
 Interactive
Compliance
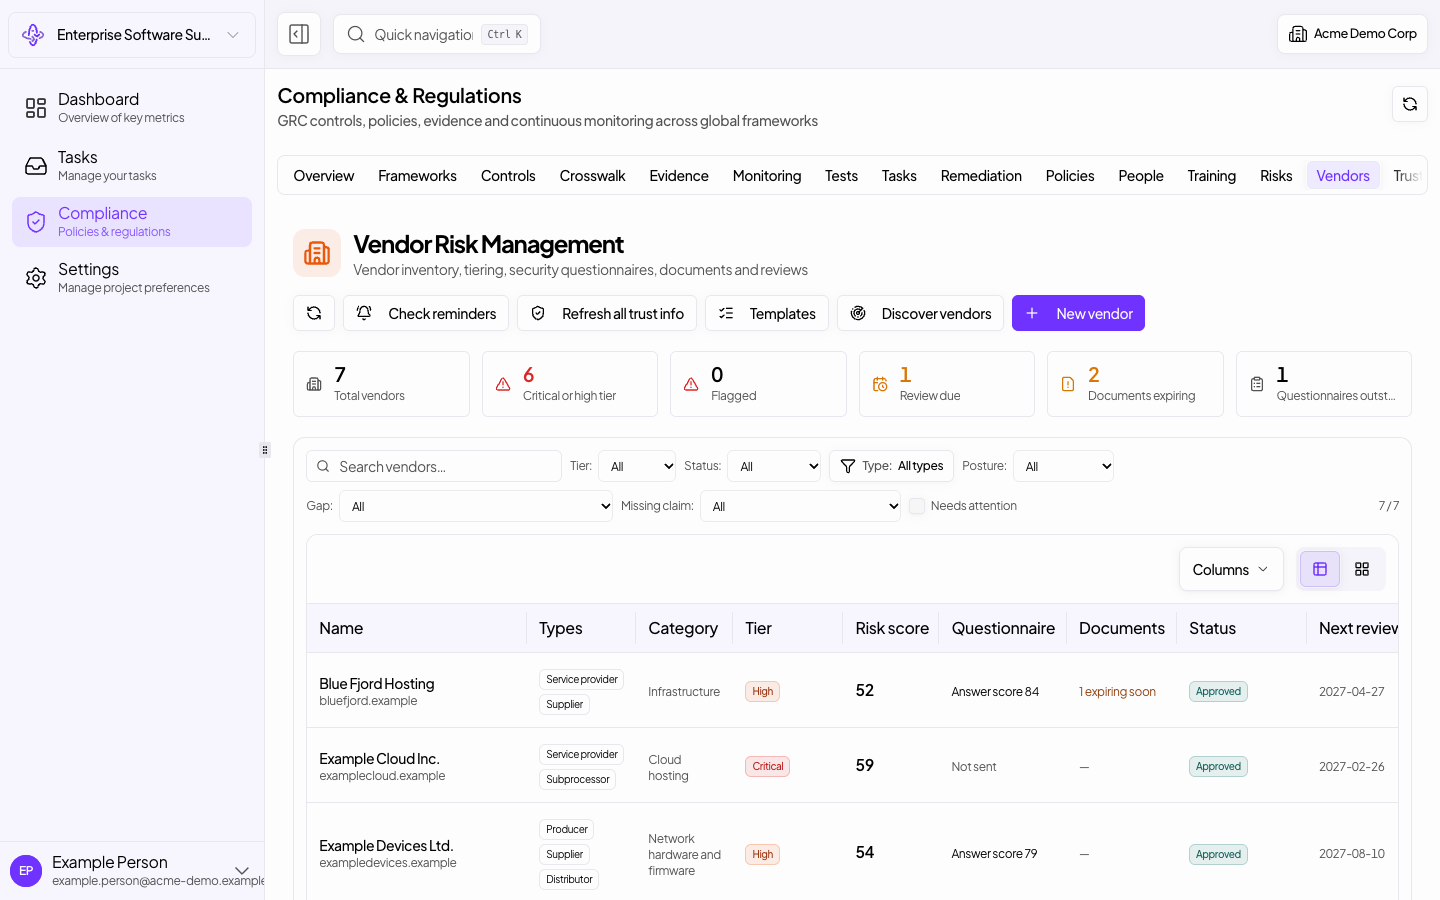
Read every vendor's trust page again, see which vendors moved, what changed for one of them, the suggestion to reassess, and the daily reminder check.
1 min8 steps
 Interactive
Compliance
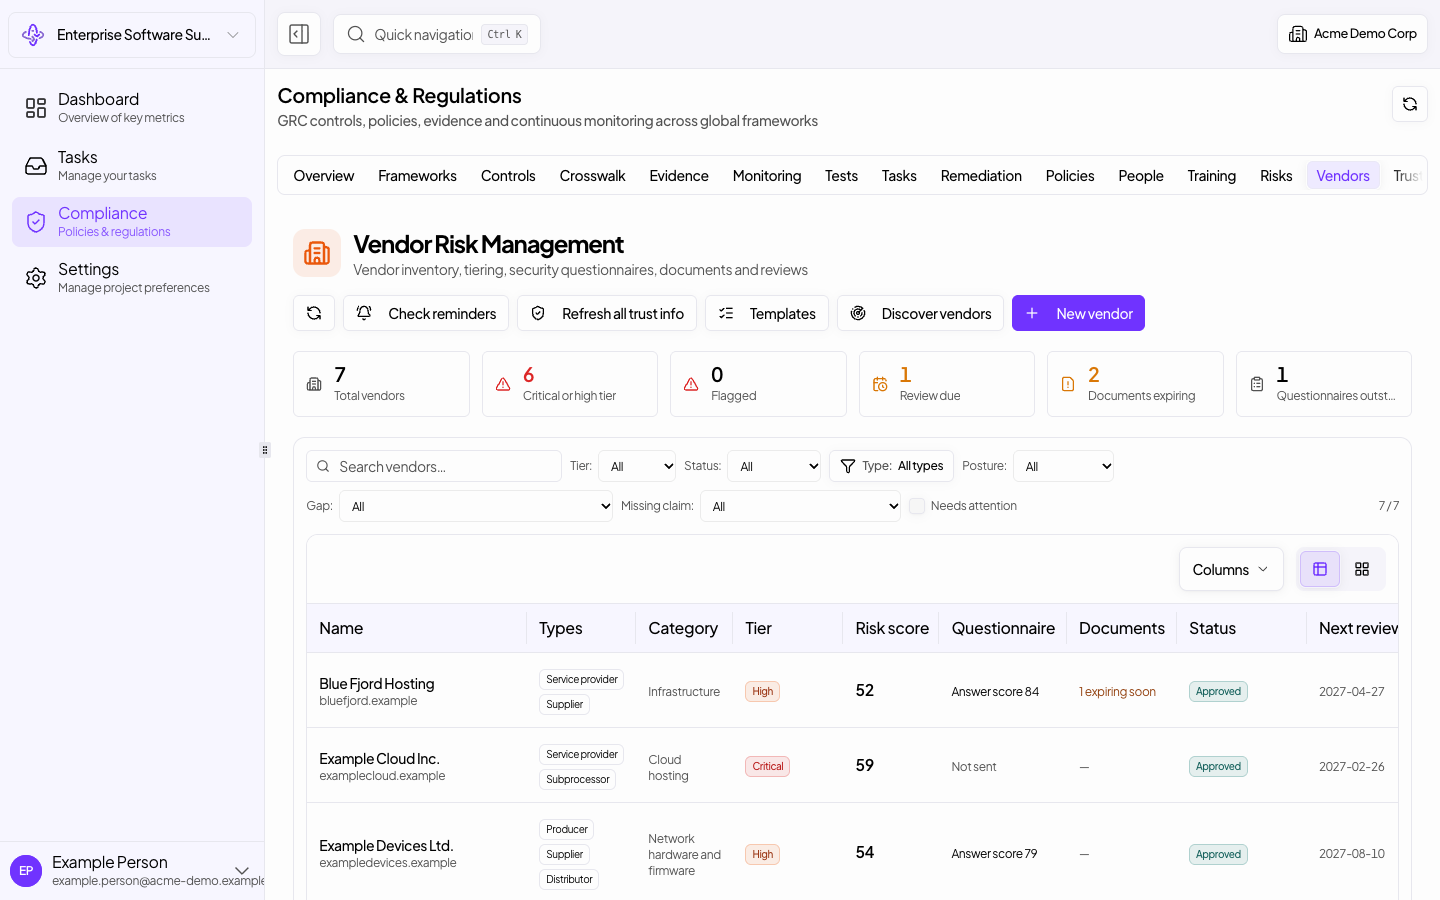
Safeguard reads each vendor's public trust page: its claims, documents, status page incidents and what changed, and sums it up as a posture with gaps and a suggestion.
1 min7 steps
 Interactive
Compliance
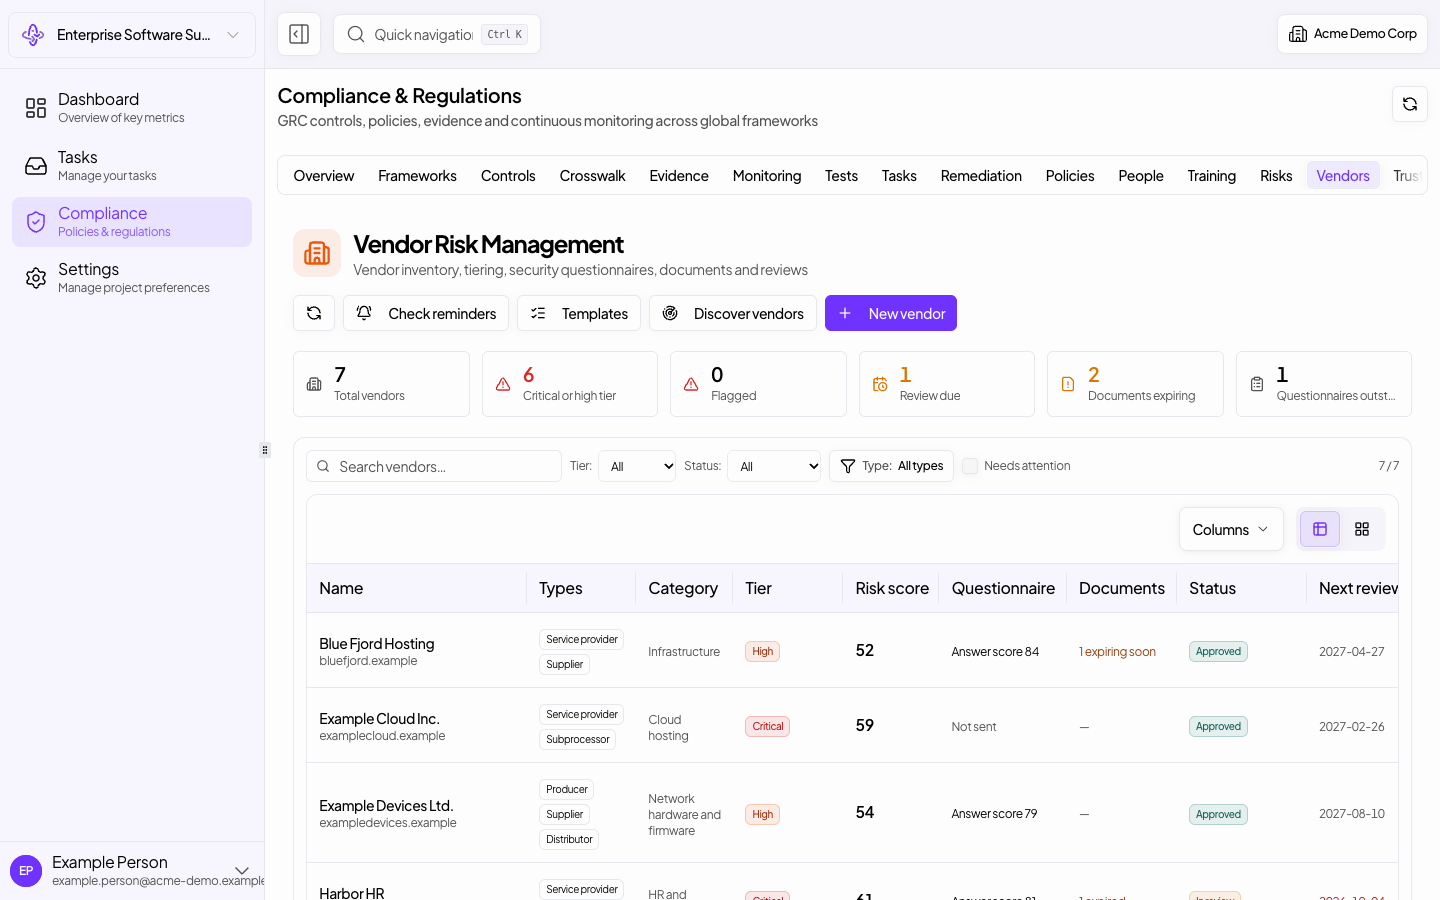
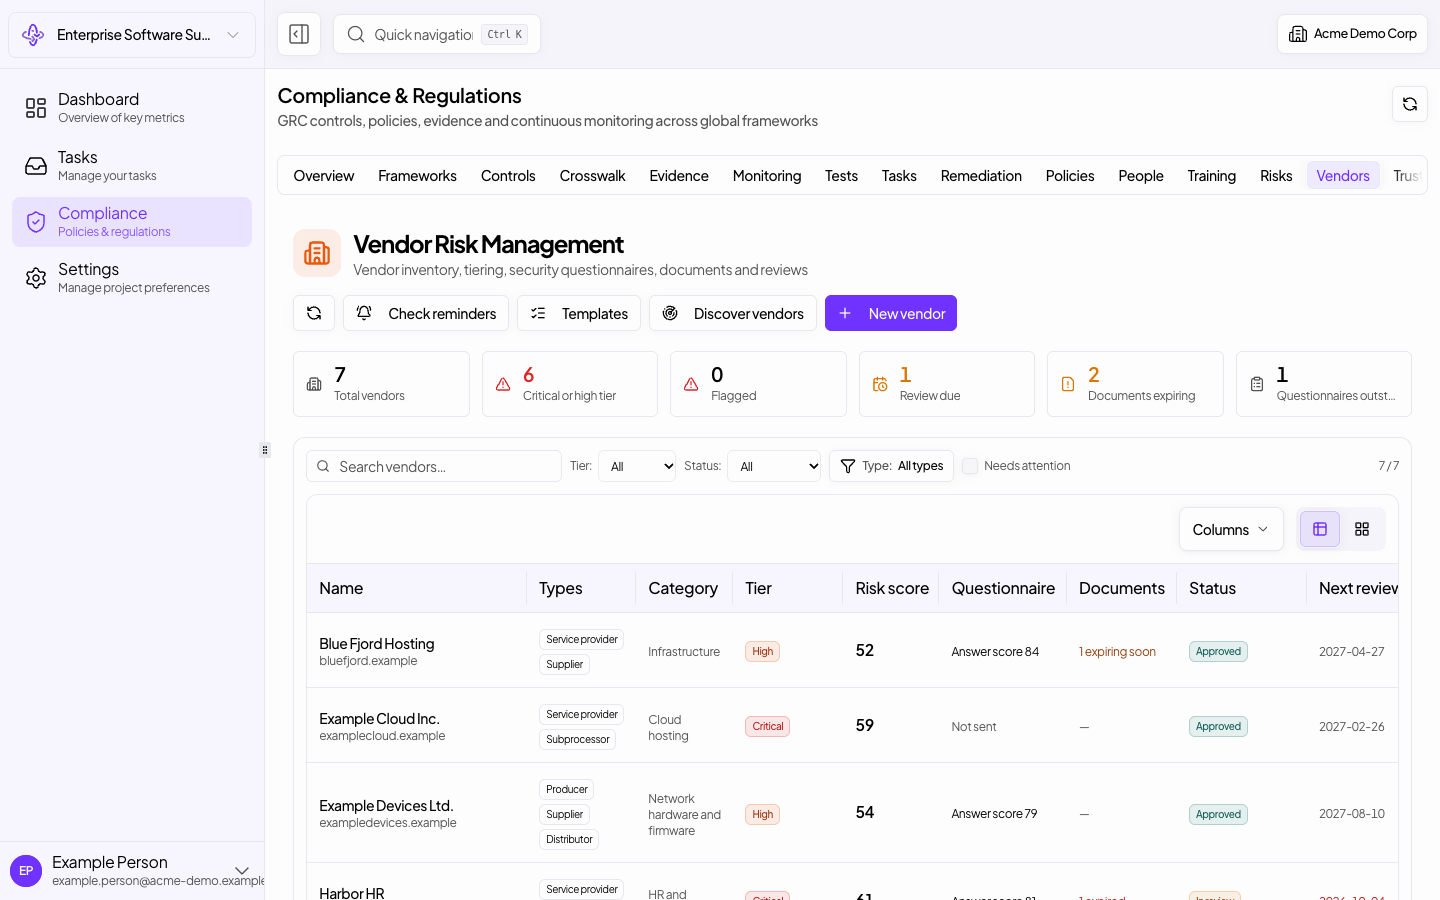
Keep each vendor's SOC2 reports, DPAs, pen test summaries and certificates with their dates, see what is expiring, add the new report and mark it reviewed.
1 min7 steps
 Interactive
Compliance
Pick a questionnaire template, let the vendor answer through a secure link without an account, and get the answers back scored, with a critical answer flagged for review.
2 min9 steps
 Interactive
Tprm
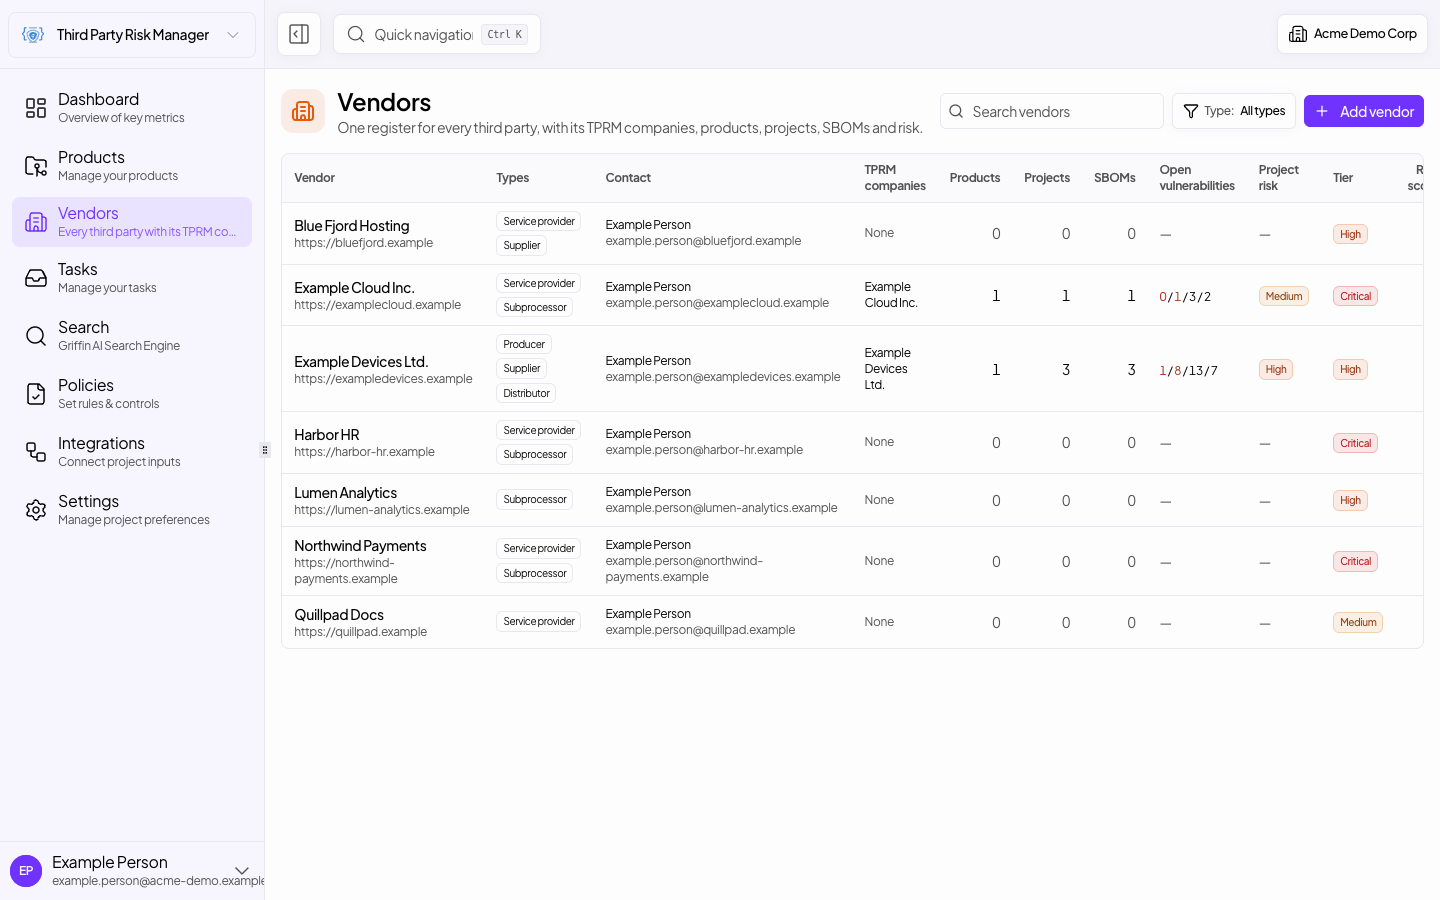
Add a vendor in TPRM with its profile, contact, criticality and the data it handles, and see the tier and risk score Safeguard works out, with its TPRM company linked.
1 min7 steps
 Interactive
Compliance
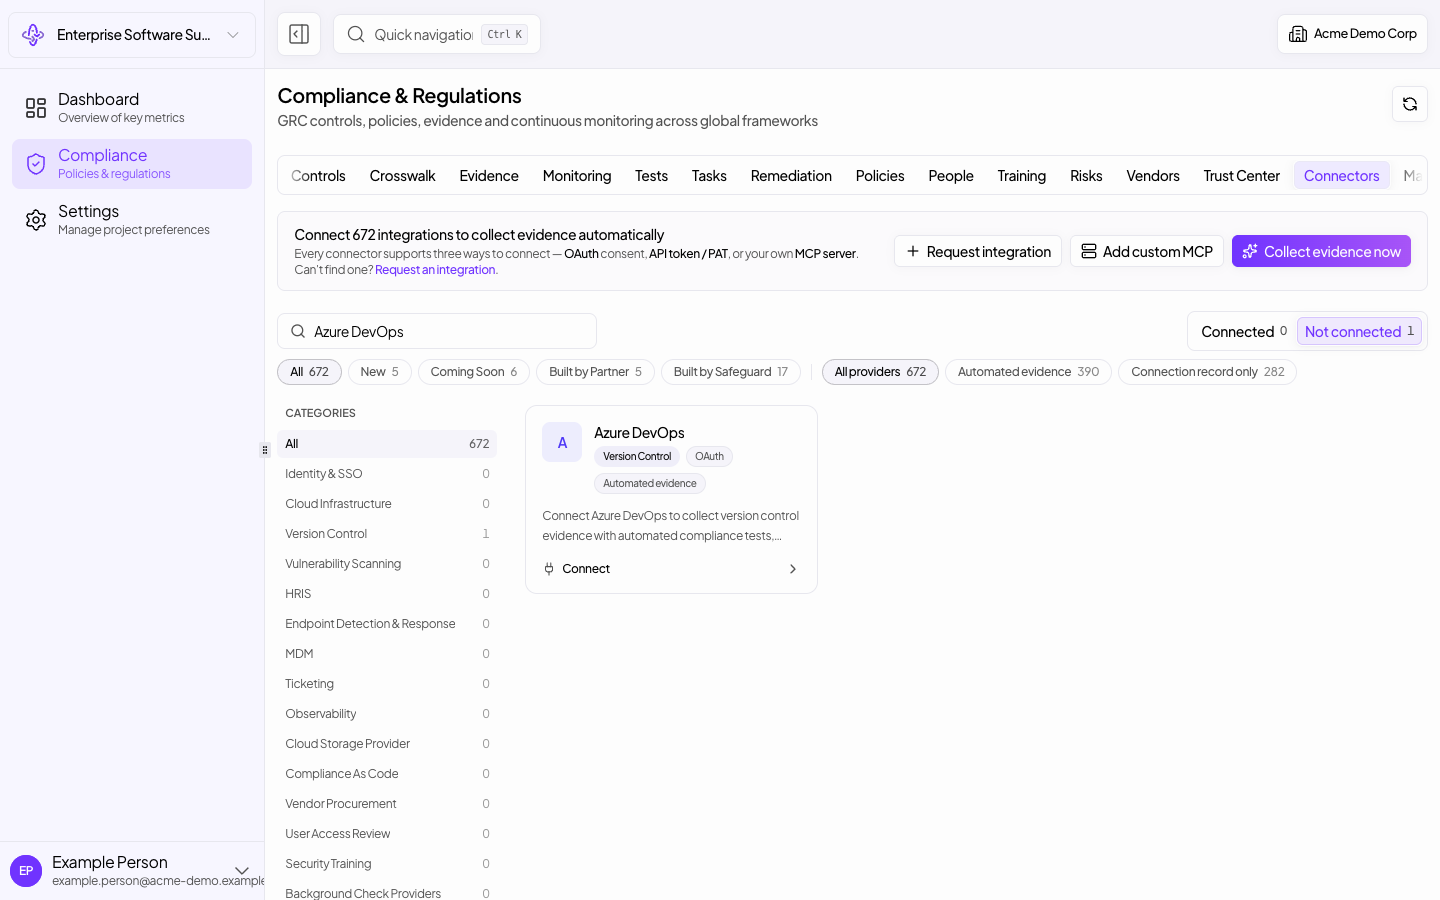
Connect Azure DevOps as a compliance connector with your organization and an Entra app, then run its continuous tests on branch rules and access.
2 min8 steps
 Interactive
Supply chain security
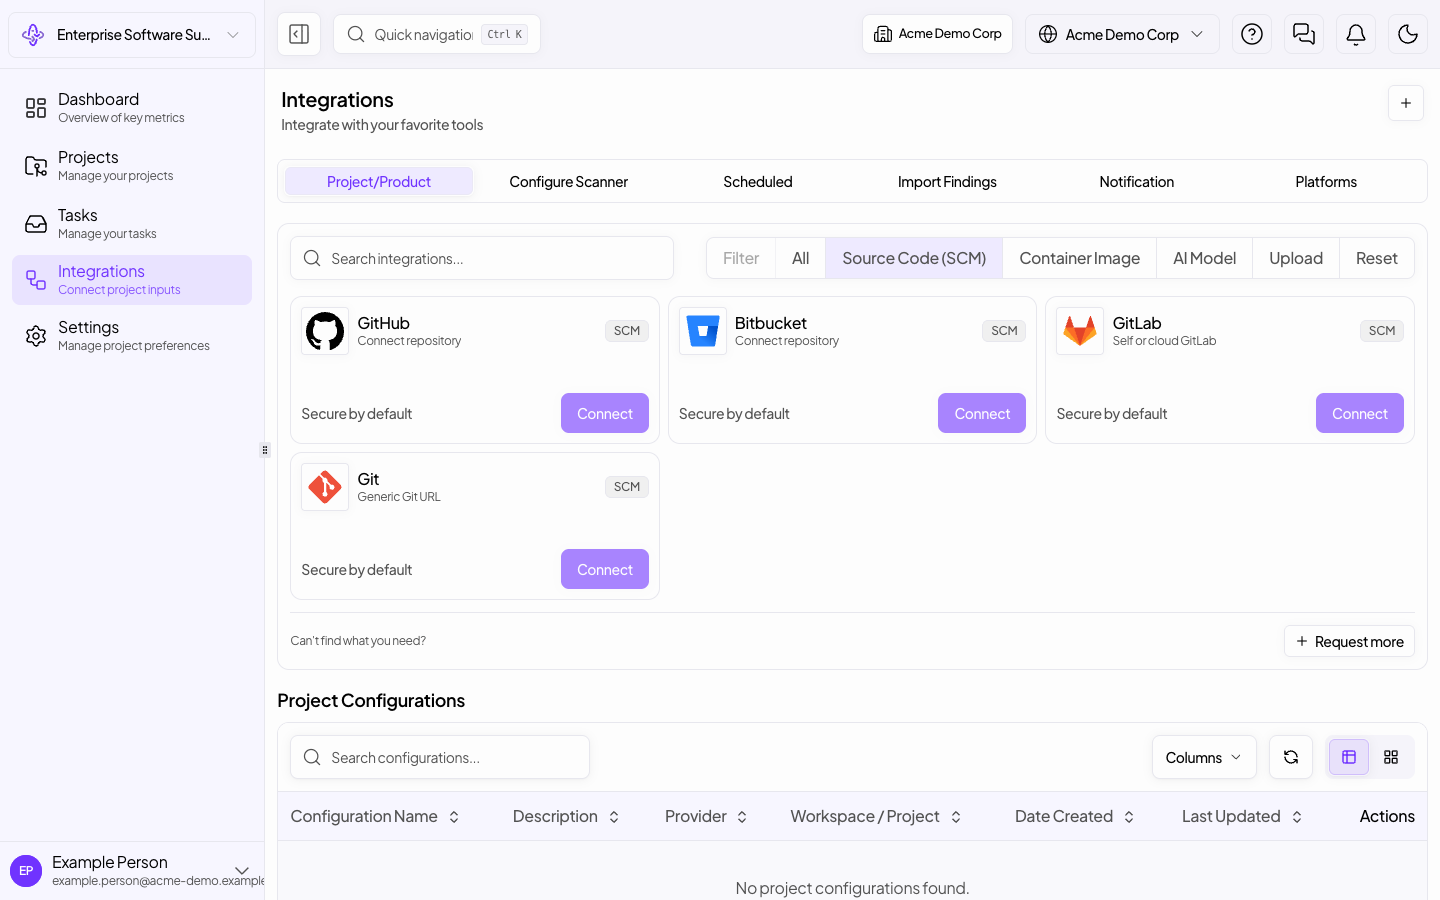
Connect GitLab with an access token, choose the repositories and branches to scan, pick the scan depth, and watch the first scans run.
2 min9 steps
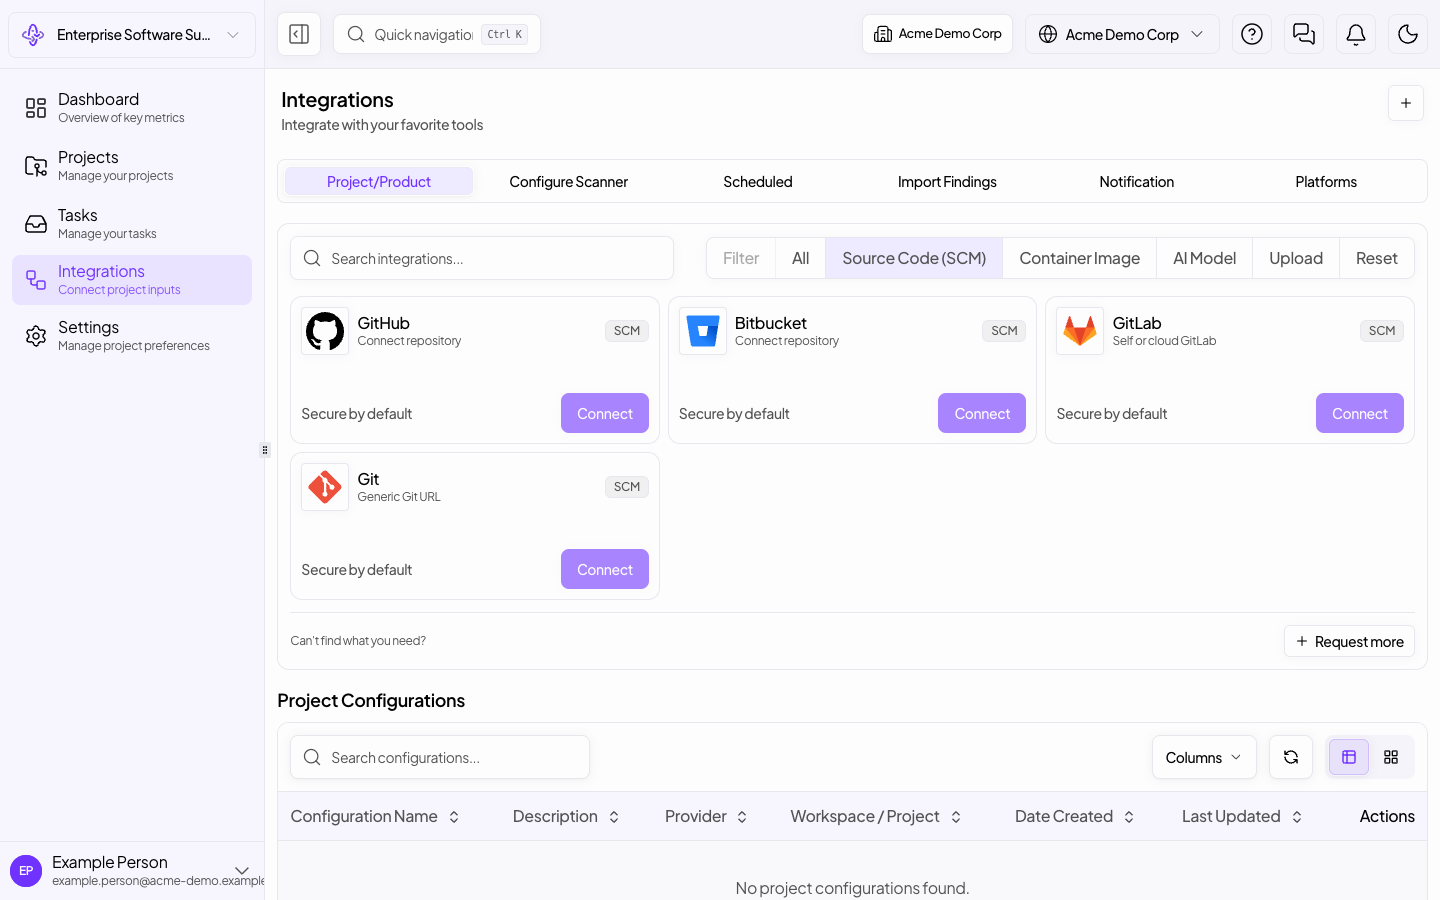 Interactive
Supply chain security
Connect GitHub with an access token, choose the repositories and branches to scan, pick the scan depth, and watch the first scans run.
2 min9 steps
 Interactive
Trust center
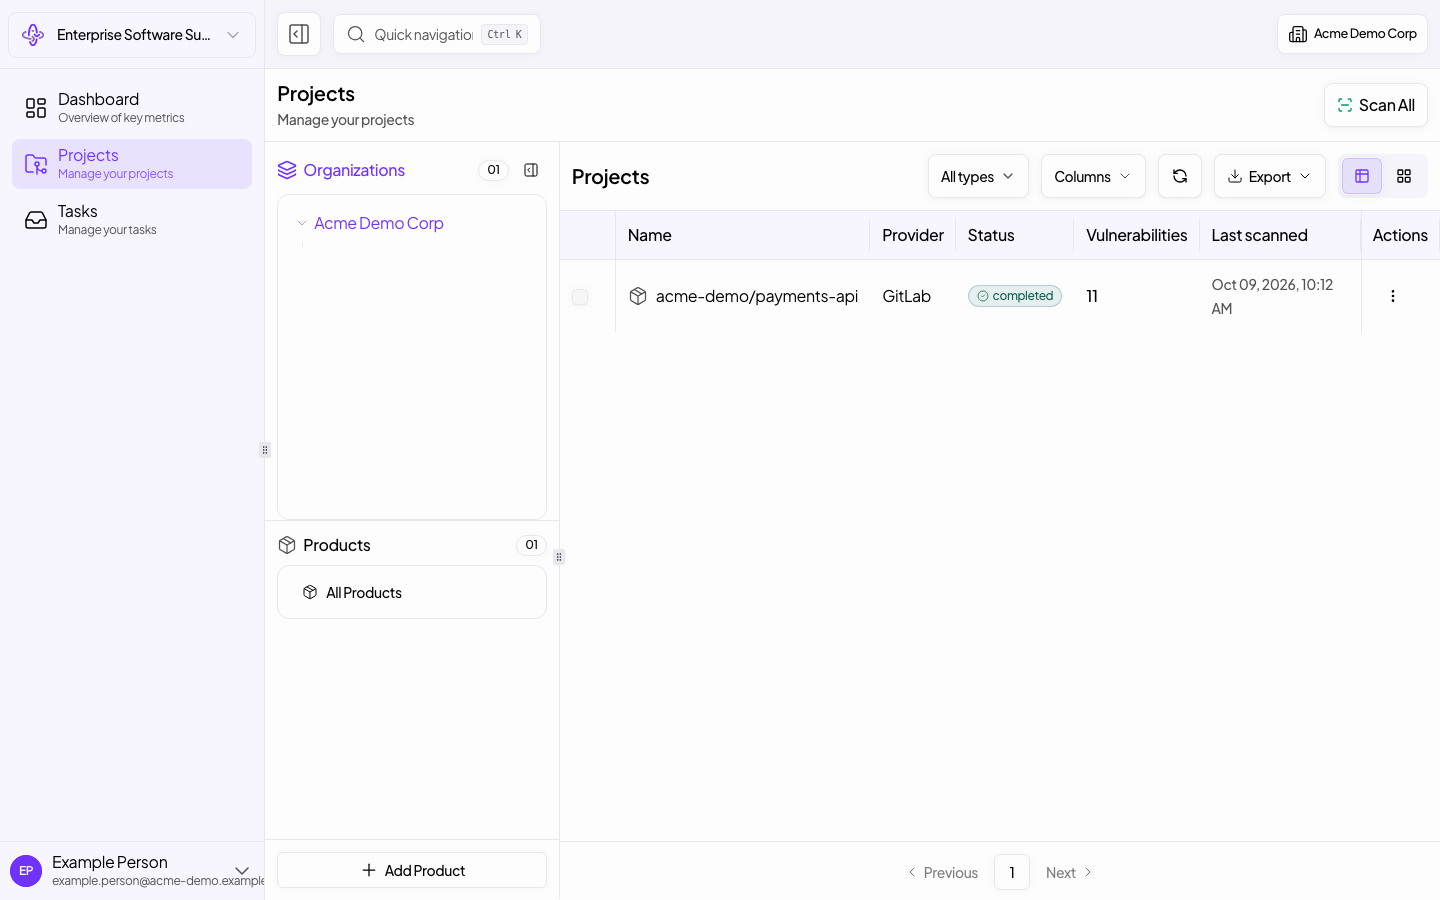
Turn on your public Trust Center, choose the frameworks and documents it shows, and share one link that buyers can search with Ctrl+K.
2 min7 steps
 Interactive
Supply chain security
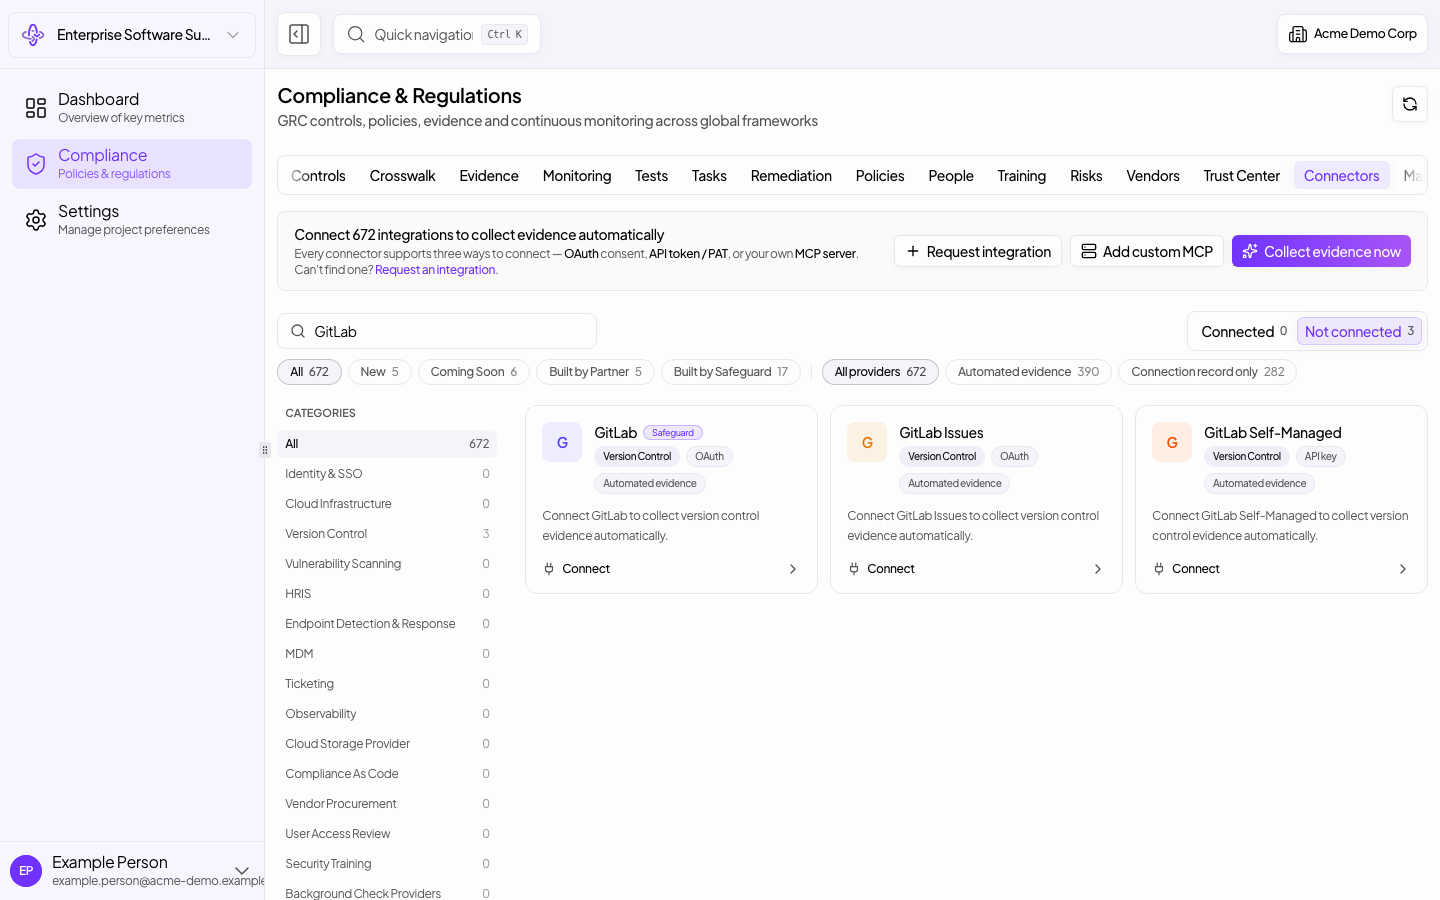
Open a scanned repo, check a critical Log4Shell finding, see how far it reaches in your code, then let AI Remediate open the fix pull request.
2 min9 steps
 Interactive
Compliance
Connect GitLab with the GitLab.com address already filled in, run the access tests, see the evidence they collect, and hand it to your auditor in an audit workspace.
2 min9 steps
 Interactive
Supply chain security
The sign-in and account security controls Safeguard customers can use today: authenticator-app two-factor authentication with backup codes, single sign-on through SAML or OpenID Connect, ending sessions, and the security activity log.
2 min12 steps
 Interactive
Supply chain security
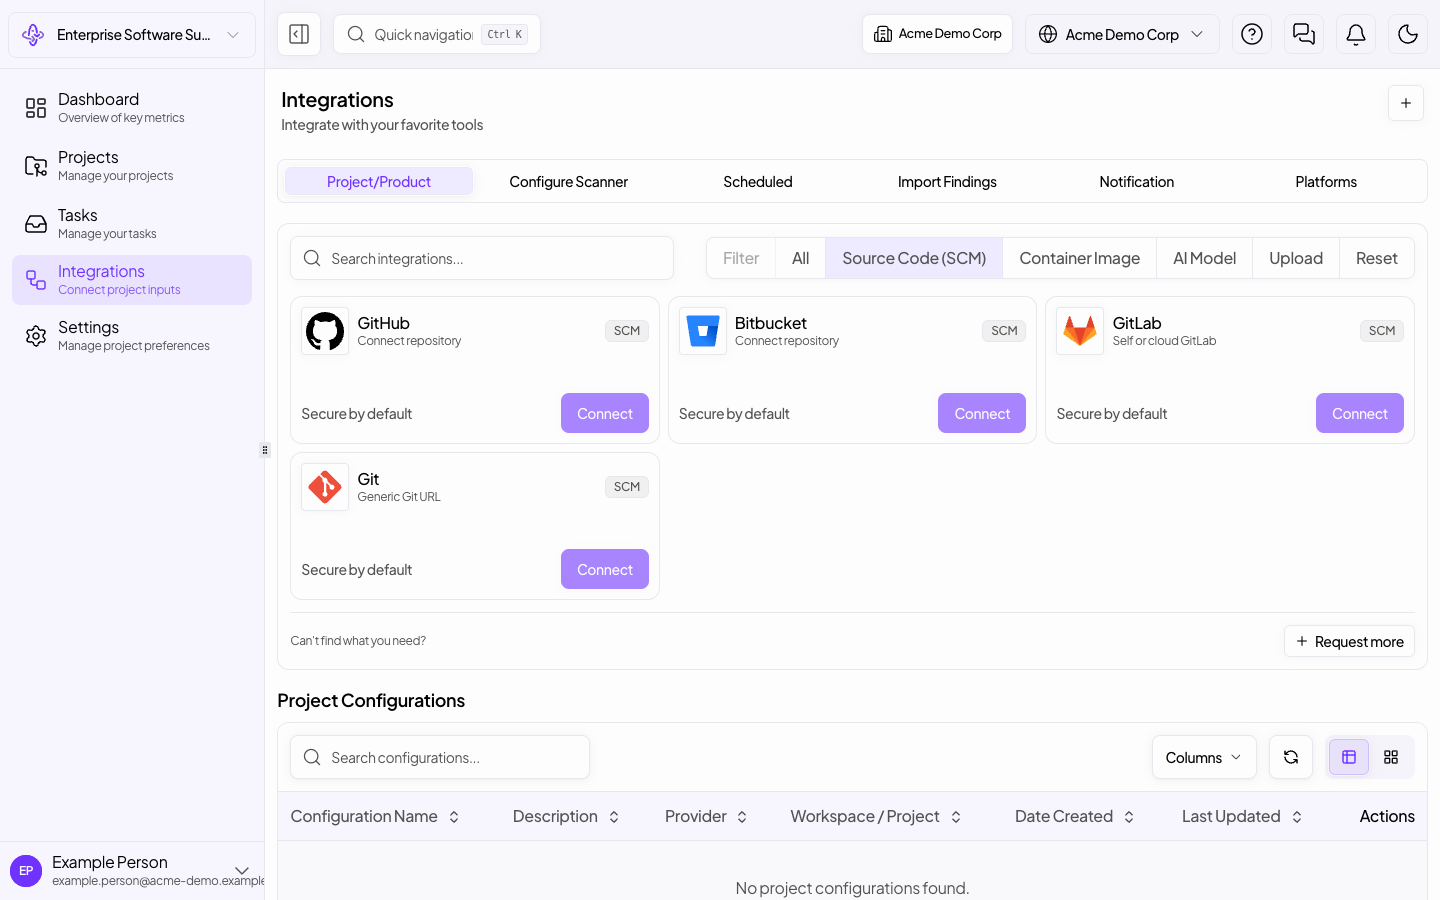
Connect Bitbucket with an access token, choose the repositories and branches to scan, pick the scan depth, and watch the first scans run.
2 min9 steps
 Interactive
Compliance
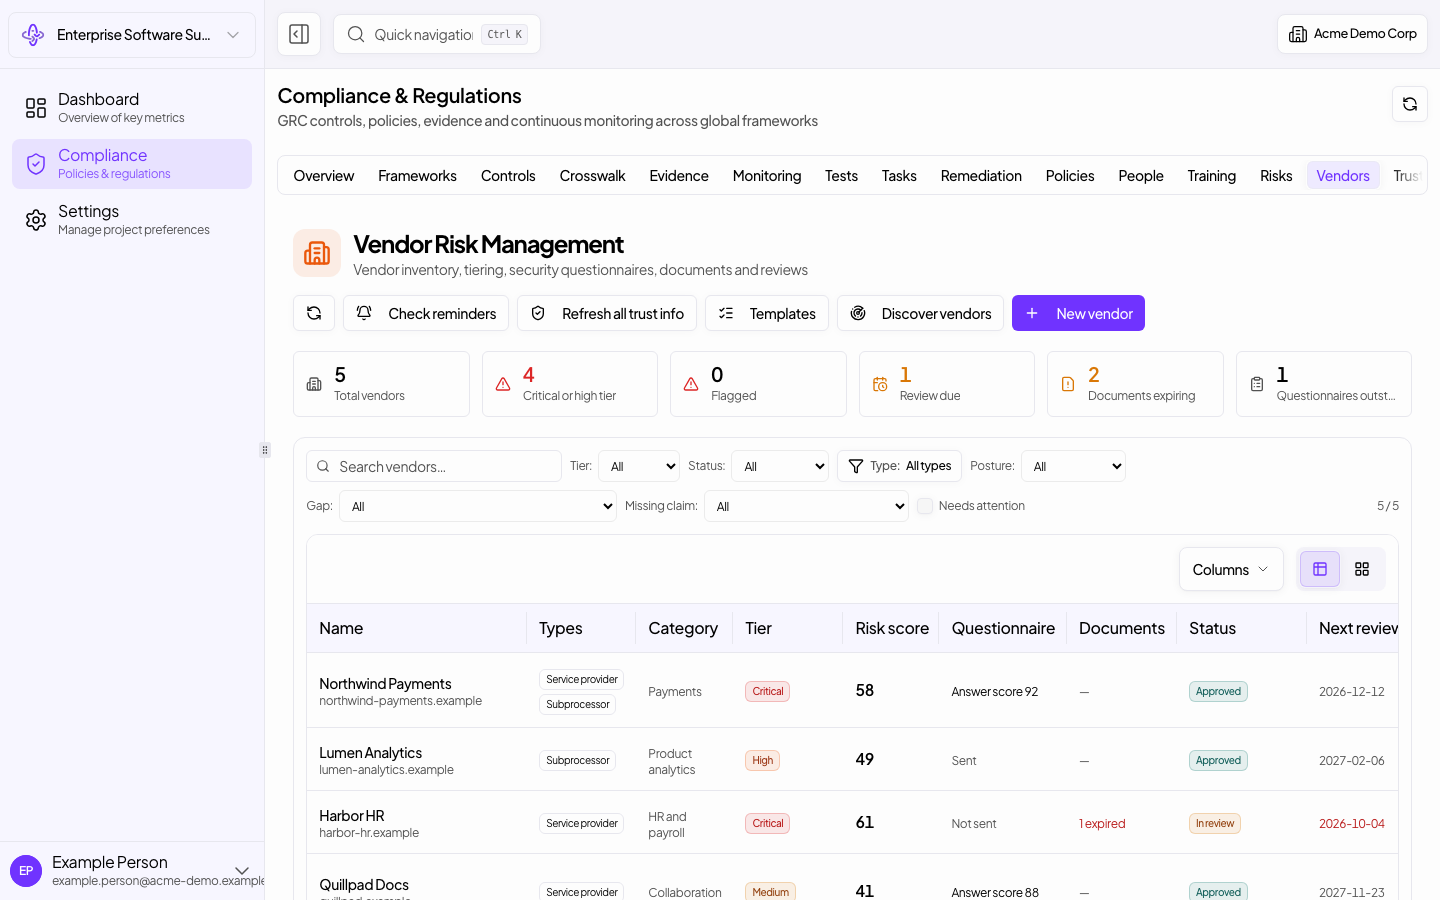
Add a vendor, read its public trust page and SOC2 report details, check the risk score and send a security questionnaire, all from Compliance, Vendors.
2 min9 steps
Your first fix PR is minutes away.
No sales call required, even your agent can complete the purchase over MCP.