

Safeguard on social
Every post we have published on our social profiles, newest first, with the copy exactly as posted. Each card links to the original post.
Latest posts
RSS feed Instagram
Revocation alone does not fix a CA compromise. A stolen CA key can sign its own "good" answers, so replace certificates and remove the old CA from every trust store. Apps that ship their own CA bundle or pin a key ignore operating system trust store changes. Safeguard's SBOMs he…
Read the full postHide the full post
Revocation alone does not fix a CA compromise. A stolen CA key can sign its own "good" answers, so replace certificates and remove the old CA from every trust store. Apps that ship their own CA bundle or pin a key ignore operating system trust store changes. Safeguard's SBOMs help you find them. Link in bio: safeguard.sh/resources/blog/ca-compromise-response-runbook-inventory-revoke-reissue
- X
Revoking a compromised CA is not the fix. The key can sign its own CRLs and OCSP "good" answers. Replace certs and remove trust. Apps with bundled CA lists or pinned keys ignore OS trust store changes. Runbook: https://t.co/8SZQss8SIg https://t.co/xU4VakRsiN
 TikTokVideo
Your coding agents already emit telemetry. Send OpenAI Codex or Claude Code OpenTelemetry to Safeguard and see what they actually did, as AI detections your SOC can act on. Token is send-only, credentials redacted. Setup guide: https://na2.hubs.ly/H08FpBy0 (link in bio) #aisecur…
Read the full postHide the full post
Your coding agents already emit telemetry. Send OpenAI Codex or Claude Code OpenTelemetry to Safeguard and see what they actually did, as AI detections your SOC can act on. Token is send-only, credentials redacted. Setup guide: https://na2.hubs.ly/H08FpBy0 (link in bio) #aisecurity #devsecops #opentelemetry
 Instagram
CVE-2026-113788 lets any Lagoon user run code through the core ssh service. Every release before 2.33.2 is affected, and 2.33.1 has no security fix. Fixed in 2.33.2 (lagoon-core chart 1.62.2, 25 August 2026). Workaround: disable the ssh service. No exploitation reported in the s…
Read the full postHide the full post
CVE-2026-113788 lets any Lagoon user run code through the core ssh service. Every release before 2.33.2 is affected, and 2.33.1 has no security fix. Fixed in 2.33.2 (lagoon-core chart 1.62.2, 25 August 2026). Workaround: disable the ssh service. No exploitation reported in the sources we checked. Safeguard's SBOM scan flags vulnerable components in your estate. Link in bio: http://safeguard.sh/resources/blog #Lagoon #CVE #Kubernetes #SupplyChainSecurity
 LinkedInVideo
The software you buy ships open source too. Atlassian's 20 October security bulletin lists 176 entries, 75 unique CVEs, and every one sits in a bundled third-party library: Apache Tomcat, Netty, Bouncy Castle and others. The bulletin counts 162 high-severity and 14 critical-seve…
Read the full postHide the full post
The software you buy ships open source too. Atlassian's 20 October security bulletin lists 176 entries, 75 unique CVEs, and every one sits in a bundled third-party library: Apache Tomcat, Netty, Bouncy Castle and others. The bulletin counts 162 high-severity and 14 critical-severity third-party vulnerabilities. As of 26 October none of the critical CVEs is in CISA's KEV catalog. Several of the upstream CVEs went public in August (Bouncy Castle on 3 August, Netty on 19 August, Tomcat on 25 August). The fixed builds in the bulletin are dated 20 October. That is the point for AppSec and platform leads. When you buy or self-host a product, you inherit its dependencies and its patch calendar. Your scanner sees the old JAR, and the supported fix is the vendor release. Three questions for every vendor product you run: 1. What open source is bundled inside it? 2. Which version of the product are we on? 3. Which build carries the fix? If a supplier gives you an SBOM, Safeguard can import it and match its components to known vulnerabilities. Lag table, fixed versions and checks in our post: https://lnkd.in/gRQvmzdg #AppSec #SupplyChainSecurity #VulnerabilityManagement
 InstagramVideo
The software you buy ships open source too. Atlassian's October security bulletin lists 75 unique CVEs, all in bundled third-party libraries such as Tomcat, Netty and Bouncy Castle. Know what is inside each vendor product and which version you run. Walkthrough: link in bio (http…
Read the full postHide the full post
The software you buy ships open source too. Atlassian's October security bulletin lists 75 unique CVEs, all in bundled third-party libraries such as Tomcat, Netty and Bouncy Castle. Know what is inside each vendor product and which version you run. Walkthrough: link in bio (http://safeguard.sh/resources/blog) #AppSec #SupplyChainSecurity #VulnerabilityManagement #SBOM
 FacebookVideo
The software you buy ships open source too. Atlassian's October security bulletin lists 75 unique CVEs, all in bundled third-party libraries such as Tomcat, Netty and Bouncy Castle. Several were public in August, and the fixed builds are dated 20 October. Know what is inside eac…
Read the full postHide the full post
The software you buy ships open source too. Atlassian's October security bulletin lists 75 unique CVEs, all in bundled third-party libraries such as Tomcat, Netty and Bouncy Castle. Several were public in August, and the fixed builds are dated 20 October. Know what is inside each vendor product and which version you run. If a supplier gives you an SBOM, Safeguard can import it and match its components to known vulnerabilities. Details: https://na2.hubs.ly/H08JhBV0
- YouTubeVideo
Atlassian's October security bulletin lists 75 unique CVEs, all in bundled third-party libraries such as Tomcat, Netty and Bouncy Castle. When you buy a product you inherit its dependencies and its patch calendar. Know what is inside each vendor product and which version you run…
Read the full postHide the full post
Atlassian's October security bulletin lists 75 unique CVEs, all in bundled third-party libraries such as Tomcat, Netty and Bouncy Castle. When you buy a product you inherit its dependencies and its patch calendar. Know what is inside each vendor product and which version you run. Walkthrough: https://na2.hubs.ly/H08JhP10 #AppSec #SupplyChainSecurity #Shorts
- Facebook
CVE-2026-113788 lets any Lagoon user run code through the core ssh service. Every release before 2.33.2 is affected, and 2.33.1 has no security fix. The fix is Lagoon 2.33.2 (lagoon-core chart 1.62.2, 25 August 2026). No exploitation reported in the sources we checked. Safeguard…
Read the full postHide the full post
CVE-2026-113788 lets any Lagoon user run code through the core ssh service. Every release before 2.33.2 is affected, and 2.33.1 has no security fix. The fix is Lagoon 2.33.2 (lagoon-core chart 1.62.2, 25 August 2026). No exploitation reported in the sources we checked. Safeguard's SBOM scan flags vulnerable components in your estate. What to patch and check: https://na2.hubs.ly/H08J3Jb0
- LinkedIn
CVE-2026-113788 lets any Lagoon user run code through the core ssh service. Every release before 2.33.2 is affected. 2.33.1 has no security fix, so treat it as vulnerable. Fixed in Lagoon 2.33.2, shipped in the lagoon-core Helm chart 1.62.2 on 25 August 2026. The attacker needs…
Read the full postHide the full post
CVE-2026-113788 lets any Lagoon user run code through the core ssh service. Every release before 2.33.2 is affected. 2.33.1 has no security fix, so treat it as vulnerable. Fixed in Lagoon 2.33.2, shipped in the lagoon-core Helm chart 1.62.2 on 25 August 2026. The attacker needs a Lagoon user account. The score is 9.4 from the GitHub CNA. Exploitation: none reported in the sources we checked. CISA's SSVC entry on 23 October recorded exploitation none, and the CVE was not in the KEV catalog as of the 26 October release. Check: the advisory says exploitation may show up in the ssh service container logs as "too many arguments". A clean log is not proof of safety. Workaround if you cannot upgrade yet: disable the ssh service in Lagoon core. The newer ssh-portal services are not affected. How Safeguard helps: its SBOM scan flags vulnerable components in your estate so you can see where you run them. What to patch and check: https://lnkd.in/gD9Vk4iB #Lagoon #CVE #Kubernetes #SupplyChainSecurity
- XVideo
Atlassian's October bulletin: 75 unique CVEs, all in bundled libraries like Tomcat, Netty and Bouncy Castle. The software you buy ships open source too, so you inherit its dependencies. Know what is inside each vendor product and which version you run. https://t.co/WNLaHEwXlC ht…
Read the full postHide the full post
Atlassian's October bulletin: 75 unique CVEs, all in bundled libraries like Tomcat, Netty and Bouncy Castle. The software you buy ships open source too, so you inherit its dependencies. Know what is inside each vendor product and which version you run. https://t.co/WNLaHEwXlC https://t.co/wwsdZLhPnP
- X
CVE-2026-113788: any Lagoon user can run code via the core ssh service. Every release before 2.33.2 is affected; 2.33.1 has no fix. Patch to 2.33.2 or disable the ssh service. No exploitation reported in the sources we checked. https://t.co/pK9DxjmWCX https://t.co/3yZ0hbXCxv
 TikTokVideo
The software you buy ships open source too. Atlassian's October bulletin: 75 unique CVEs, all in bundled libraries. Know what is inside each vendor product. Walkthrough: https://na2.hubs.ly/H08JhL80 (link in bio) #AppSec #SupplyChain
 Instagram
The maintainer has not shipped a fix for a dependency you use. There are two gaps: a fix that exists but has not reached your builds, and no fix at all. Swipe for the route: an SBOM per build, tested remediation pull requests (switched off until you turn them on), upstream first…
Read the full postHide the full post
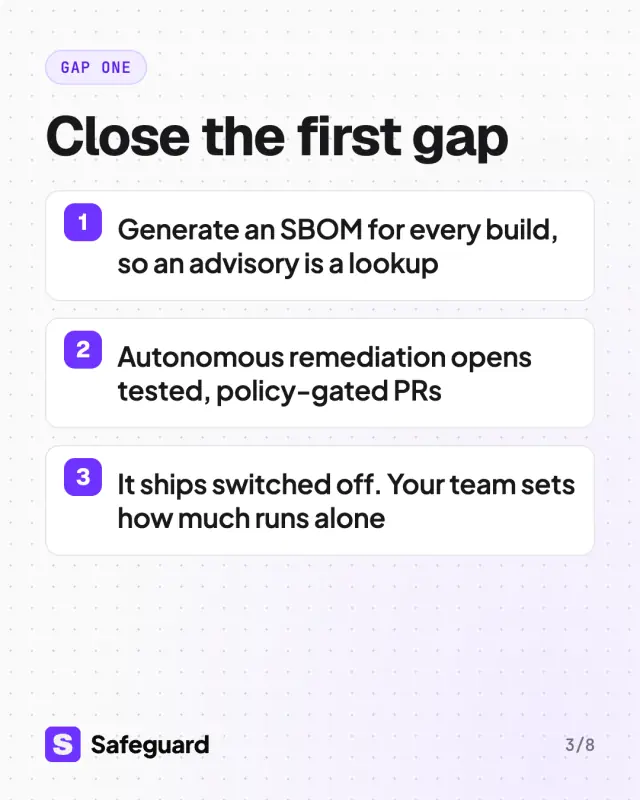
The maintainer has not shipped a fix for a dependency you use. There are two gaps: a fix that exists but has not reached your builds, and no fix at all. Swipe for the route: an SBOM per build, tested remediation pull requests (switched off until you turn them on), upstream first, then a fork and a hardened Gold build when upstream will not move. And the honest limit: vendor appliances, hosted services and operating systems you do not build still need the vendor's fix. Look up your top twenty dependencies free at http://gold.safeguard.sh. Full brief: link in bio (http://safeguard.sh/blog). #opensource #supplychainsecurity #appsec #sbom #devsecops
 LinkedIn
The maintainer has not shipped a fix for the dependency you use. Waiting is a plan, but not a good one. There are two gaps. A fix exists but has not reached your builds. Or no fix exists yet. Gap one: generate an SBOM for every build, so a new advisory is a lookup, not a search.…
Read the full postHide the full post
The maintainer has not shipped a fix for the dependency you use. Waiting is a plan, but not a good one. There are two gaps. A fix exists but has not reached your builds. Or no fix exists yet. Gap one: generate an SBOM for every build, so a new advisory is a lookup, not a search. Safeguard's autonomous remediation opens tested, policy-gated pull requests to the fixed version. It ships switched off, so your team decides how much runs on its own. Gap two: we first work to get the fix accepted upstream, because a fix at the source helps everyone. If the issue is severe or upstream will not move, we build a fork, fix the vulnerability there and publish a hardened Gold build. Gold builds are held to a bar: zero exploitable critical or high CVEs, a completed license check, a public evidence page, signed provenance (SLSA Build Level 3 is the design target) and continuous monitoring. One honest limit: if the vulnerable code sits in a vendor appliance, a hosted service or an operating system you do not build, the fix still comes from that vendor. Swipe the 8 slides, then look up your top twenty dependencies on https://lnkd.in/g6VsKZEE (free, no login). Ask which packages Gold covers today before you plan around it. Full brief: https://lnkd.in/gYy8QxSP #OpenSource #SupplyChainSecurity #AppSec #SBOM
 Facebook
The maintainer has not shipped a fix for the dependency you use. There are two gaps: a fix that exists but has not reached your builds, and no fix at all. For the first, an SBOM per build turns an advisory into a lookup, and tested remediation pull requests move you to the fixed…
Read the full postHide the full post
The maintainer has not shipped a fix for the dependency you use. There are two gaps: a fix that exists but has not reached your builds, and no fix at all. For the first, an SBOM per build turns an advisory into a lookup, and tested remediation pull requests move you to the fixed version (it ships switched off, so you set how much runs on its own). For the second, we first work to get the fix accepted upstream. If the issue is severe or upstream will not move, we fork, fix it there and publish a hardened Gold build. One honest limit: vendor appliances, hosted services and operating systems you do not build still need the fix from the vendor. Full brief: https://na2.hubs.ly/H08CD_t0
- X
Upstream has not shipped a fix? Two gaps: a fix that has not reached your builds, and no fix at all. SBOM per build, tested remediation PRs, and for no-fix cases a hardened Gold fork. Limit: vendor appliances still need the vendor. https://t.co/u5A9jr4DZb https://t.co/8St5JJUiTe
- InstagramVideo
The router you forgot you own is part of your attack surface. ASUS fixed three High rated router flaws on 23 October. The CVE records list a firmware series and no fixed version. How many routers do you own, and do you know their firmware? Walkthrough: link in bio (http://safegu…
Read the full postHide the full post
The router you forgot you own is part of your attack surface. ASUS fixed three High rated router flaws on 23 October. The CVE records list a firmware series and no fixed version. How many routers do you own, and do you know their firmware? Walkthrough: link in bio (http://safeguard.sh/resources/blog) #NetworkSecurity #VulnerabilityManagement #CVE #ITSecurity
 LinkedInVideo
The router you forgot you own is part of your attack surface. On 23 October ASUS fixed three High rated flaws in routers on its 102 firmware series: an authentication bypass (CVE-2026-93489, CVSS v4 score 8.7) and two root command injections (CVE-2026-75775 and CVE-2026-75779).…
Read the full postHide the full post
The router you forgot you own is part of your attack surface. On 23 October ASUS fixed three High rated flaws in routers on its 102 firmware series: an authentication bypass (CVE-2026-93489, CVSS v4 score 8.7) and two root command injections (CVE-2026-75775 and CVE-2026-75779). The first lets an unauthenticated user on the adjacent network forge an access ticket and act as administrator. The CVE records list an affected firmware series and no fixed version. As of 26 October none of the three is in CISA's KEV catalog, and no exploitation has been reported. So the useful question for IT and security leads is not only what ASUS shipped. It is how many of these devices you own. The branch office. Remote workers' home setups. The unit in the closet nobody has logged into since install. Three things for this week: 1. Write down every router you own and its firmware version. 2. Update the ones that are behind. 3. Keep the admin page off the internet. Full walkthrough in our post: https://lnkd.in/gvp_JqYA #VulnerabilityManagement #NetworkSecurity #CVE
 FacebookVideo
ASUS fixed three High rated router flaws on 23 October: an authentication bypass (CVE-2026-93489) and two root command injections (CVE-2026-75775, CVE-2026-75779). The CVE records list a firmware series and no fixed version, and none is in CISA's KEV catalog as of 26 October. Ho…
Read the full postHide the full post
ASUS fixed three High rated router flaws on 23 October: an authentication bypass (CVE-2026-93489) and two root command injections (CVE-2026-75775, CVE-2026-75779). The CVE records list a firmware series and no fixed version, and none is in CISA's KEV catalog as of 26 October. How many routers do you own? The branch office, the home office, the one in the closet. Check the firmware on every one. What to check and how: https://na2.hubs.ly/H08Jhj80
- YouTubeVideo
ASUS fixed three High rated router flaws on 23 October: CVE-2026-93489 (authentication bypass) and CVE-2026-75775 and CVE-2026-75779 (root command injection). The CVE records list a firmware series and no fixed version. How many routers do you own, and do you know their firmware…
Read the full postHide the full post
ASUS fixed three High rated router flaws on 23 October: CVE-2026-93489 (authentication bypass) and CVE-2026-75775 and CVE-2026-75779 (root command injection). The CVE records list a firmware series and no fixed version. How many routers do you own, and do you know their firmware? Walkthrough: https://na2.hubs.ly/H08JhWD0 #NetworkSecurity #CVE #Shorts
- XVideo
Your forgotten router is an attack surface. ASUS fixed three High rated flaws on 23 Oct: CVE-2026-93489 auth bypass, CVE-2026-75775 and CVE-2026-75779 root commands. CVE records list a firmware series, no fixed version. How many routers do you own? https://t.co/QKWAiTYTdv https:…
Read the full postHide the full post
Your forgotten router is an attack surface. ASUS fixed three High rated flaws on 23 Oct: CVE-2026-93489 auth bypass, CVE-2026-75775 and CVE-2026-75779 root commands. CVE records list a firmware series, no fixed version. How many routers do you own? https://t.co/QKWAiTYTdv https://t.co/LPqtfIqwxC
 TikTokVideo
Patch the routers you forgot you own. ASUS fixed three High rated router flaws on 23 Oct. Check the firmware on every one. Walkthrough: https://na2.hubs.ly/H08Jh9T0 (link in bio) #cybersecurity #networksecurity #itsecurity
 Instagram
Two separate exposures at Amadeus, the airline booking technology provider, surfaced in October 2026. Korean Air and Asiana cite misuse of a system account login. heise online found an unauthenticated Spring Boot heap dump. No source links the two. Five questions to ask any book…
Read the full postHide the full post
Two separate exposures at Amadeus, the airline booking technology provider, surfaced in October 2026. Korean Air and Asiana cite misuse of a system account login. heise online found an unauthenticated Spring Boot heap dump. No source links the two. Five questions to ask any booking or SaaS vendor: which system accounts read our data, how credentials rotate, whether test environments hold real data, how many days of logs, and how many hours until they tell you. Link in bio: http://safeguard.sh/resources/blog #vendorrisk #thirdpartyrisk #appsec #cybersecurity
Follow Safeguard

Self-healing security runs on Safeguard.
Your first fix PR is minutes away.
No sales call required, even your agent can complete the purchase over MCP.