

Safeguard on social
Every post we have published on our social profiles, newest first, with the copy exactly as posted. Each card links to the original post.
Latest posts
RSS feed Instagram
Self-hosted GitLab? CVE-2026-97229 is a CVSS 10.0 CI regex flaw. It is fixed in 19.4.2, 19.3.5 and 19.2.8, and the real fix lives in the Ruby underneath. Check both versions, upgrade, then review CI runner exposure. Link in bio: http://safeguard.sh/resources/blog/gitlab-cve-2026…
Read the full postHide the full post
Self-hosted GitLab? CVE-2026-97229 is a CVSS 10.0 CI regex flaw. It is fixed in 19.4.2, 19.3.5 and 19.2.8, and the real fix lives in the Ruby underneath. Check both versions, upgrade, then review CI runner exposure. Link in bio: http://safeguard.sh/resources/blog/gitlab-cve-2026-97229-ci-regex-flaw-patch-self-hosted-gitlab-and-check-runner-exposure #GitLab #CVE #DevSecOps #SupplyChainSecurity
- Facebook
Running self-hosted GitLab? CVE-2026-97229 (CVSS 10.0, CI regex flaw) is fixed in 19.4.2, 19.3.5 and 19.2.8, but the real fix lives in the Ruby underneath. Here is how to check your GitLab and Ruby versions, upgrade, and review CI runner exposure. https://na2.hubs.ly/H08Lgdj0
Read the full postHide the full post
Running self-hosted GitLab? CVE-2026-97229 (CVSS 10.0, CI regex flaw) is fixed in 19.4.2, 19.3.5 and 19.2.8, but the real fix lives in the Ruby underneath. Here is how to check your GitLab and Ruby versions, upgrade, and review CI runner exposure. https://na2.hubs.ly/H08Lgdj0
- LinkedIn
Self-hosted GitLab: the version number may not be the whole answer for CVE-2026-97229. GitLab scores the CI regular expression flaw CVSS 10.0 and fixed it in 19.4.2, 19.3.5 and 19.2.8 on 12 October. Ruby then shipped fixes to its Onigmo regex engine on 23 October, where the unde…
Read the full postHide the full post
Self-hosted GitLab: the version number may not be the whole answer for CVE-2026-97229. GitLab scores the CI regular expression flaw CVSS 10.0 and fixed it in 19.4.2, 19.3.5 and 19.2.8 on 12 October. Ruby then shipped fixes to its Onigmo regex engine on 23 October, where the underlying bugs live. If you run GitLab's official packages or images, the GitLab version tells you most of the story. If you bring your own Ruby (source install, distro package, custom image), you also need a fixed Ruby. Alpine Linux reported an attempted exploitation of its own instance and found no evidence the attacker's code ran, though it could not rule it out. We have not seen wider confirmed exploitation. The post covers how to find your GitLab and Ruby versions on every install type, the upgrade path, CI and runner exposure, and when to rotate what. https://lnkd.in/gPwE52np #GitLab #CVE #DevSecOps #SupplyChainSecurity
- X
GitLab CVE-2026-97229, CVSS 10.0. Fixed in 19.4.2, 19.3.5, 19.2.8, but the real fix is in Ruby's Onigmo regex engine. Official packages: check the GitLab version. Own Ruby: check that too. Version commands and runner review: https://t.co/R4WYhHOb12 https://t.co/VBAkLVL3ES
 Instagram
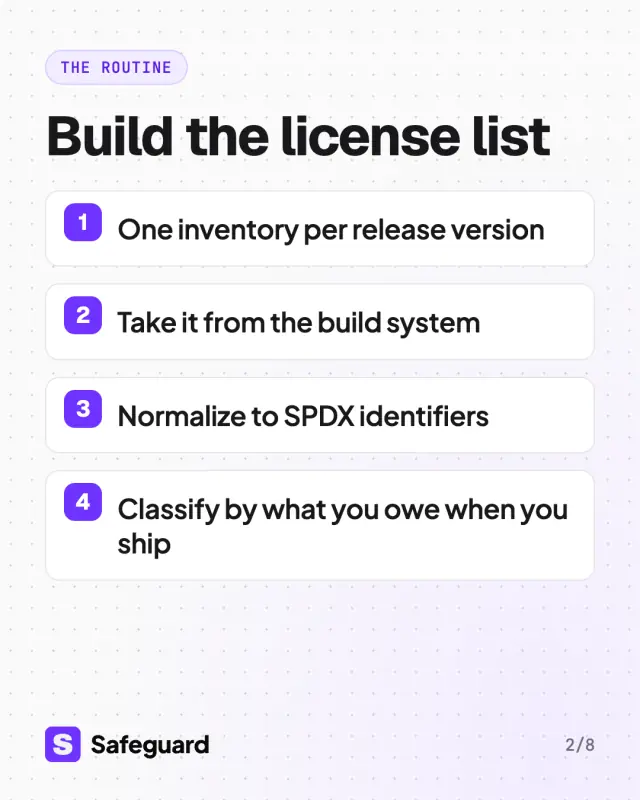
Is there GPL code in this OTA image? Answer it from an inventory with a license on every line, not from memory. Swipe for the routine: one inventory per release version, SPDX identifiers, a policy set before the release, exceptions with an approver and an expiry date, and the re…
Read the full postHide the full post
Is there GPL code in this OTA image? Answer it from an inventory with a license on every line, not from memory. Swipe for the routine: one inventory per release version, SPDX identifiers, a policy set before the release, exceptions with an approver and an expiry date, and the record kept with the release. Not legal advice. Counsel decides what a license requires of your product. Link in bio: http://safeguard.sh/resources/blog/use-case-license-compliance-before-shipping-firmware-in-automotive #OpenSourceCompliance #SBOM #Automotive #FirmwareSecurity
 Facebook
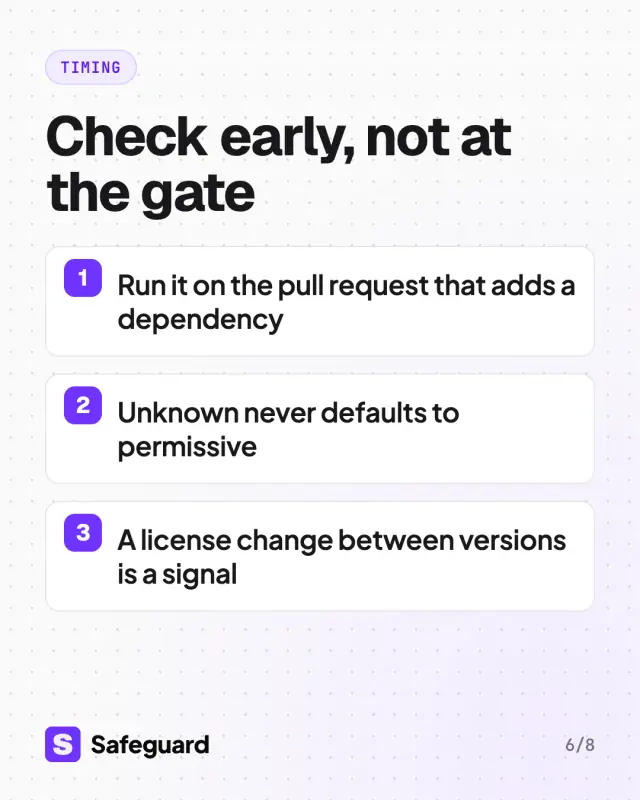
Is there GPL code in this OTA image? Answer it from an inventory with a license on every line, not from memory. Swipe for the routine: one inventory per release version, SPDX identifiers, a policy set before the release, exceptions with an approver and an expiry date, and a reco…
Read the full postHide the full post
Is there GPL code in this OTA image? Answer it from an inventory with a license on every line, not from memory. Swipe for the routine: one inventory per release version, SPDX identifiers, a policy set before the release, exceptions with an approver and an expiry date, and a record kept with the release. Not legal advice. Full workflow: https://na2.hubs.ly/H08Kyyt0
 LinkedIn
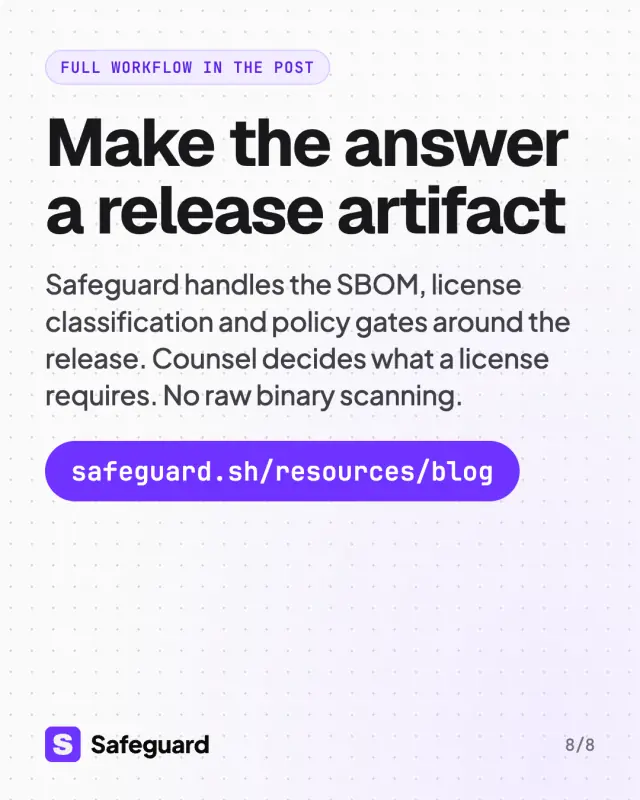
Is there GPL code in this OTA image? The honest answer comes from an inventory with a license on every line, not from a memory of what the team linked. The routine, in short: 1. Build the license list from the build system, one inventory per release version. 2. Normalize to SPDX…
Read the full postHide the full post
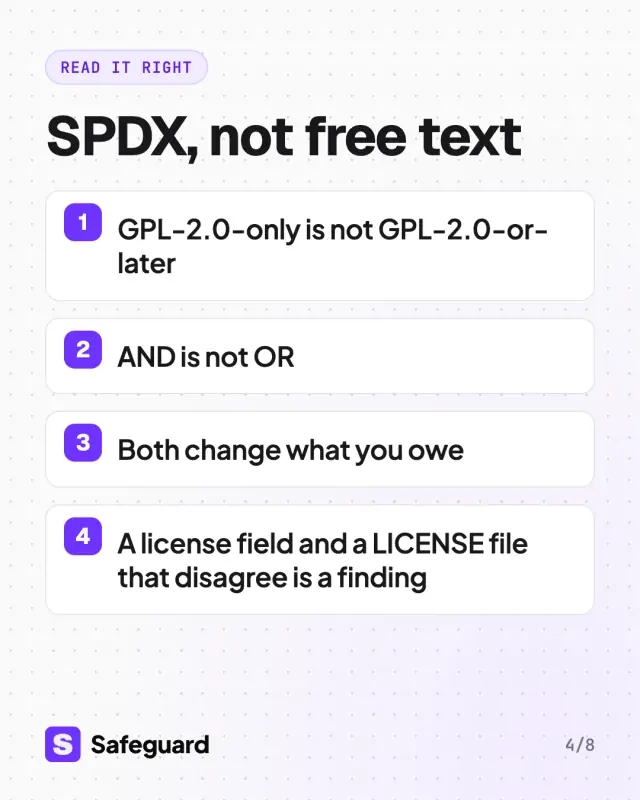
Is there GPL code in this OTA image? The honest answer comes from an inventory with a license on every line, not from a memory of what the team linked. The routine, in short: 1. Build the license list from the build system, one inventory per release version. 2. Normalize to SPDX identifiers. GPL-2.0-only is not GPL-2.0-or-later, and AND is not OR. 3. Set the policy before the release: allowed, review or denied, with exceptions that name an approver and an expiry date. 4. Run it on the pull request that adds a dependency, not at the gate. 5. Keep the inventory, policy version, findings and exceptions with the release. The inventory stops where the build system stops: the vendored C library, the board support blob, the library a vendor binary links. Not legal advice. Counsel decides what a license requires of your product. Safeguard handles the SBOM, license classification and policy gates around the release; it does not scan a raw flashed binary. Full workflow in the use case post (swipe the document for the short version): https://lnkd.in/g_ZUJ-vN #OpenSourceCompliance #SBOM #Automotive
 X
Is there GPL code in this OTA image? Answer it from an inventory with an SPDX license on every line, a policy set before the release, and exceptions with an approver and an expiry date. Not from memory. https://t.co/54GBmqvCYV https://t.co/kjuMIBWUyf
 LinkedInVideo
PostgreSQL 14 gets its final release on 12 November, per the project's versioning policy. After that, a bug found in code that 14 shares with newer versions gets fixed in 15 through 18 and stays open in 14. The copies that get missed are rarely the main cluster. They are the CI…
Read the full postHide the full post
PostgreSQL 14 gets its final release on 12 November, per the project's versioning policy. After that, a bug found in code that 14 shares with newer versions gets fixed in 15 through 18 and stays open in 14. The copies that get missed are rarely the main cluster. They are the CI service container, the migration image, the reporting replica, and the database embedded in a vendor appliance. A plan for the next eleven days: 1. Inventory every PostgreSQL 14 instance, self-hosted, in containers and managed. 2. If you hold SBOMs, search them by package and version. In Safeguard that lists every project and image that carries it. Appliances show up only when the supplier gives you an SBOM. 3. Apply the final 14 release when it ships. 4. Schedule the major upgrade to 18, which the project supports until November 2030. Our write-up has the dates, the SQL to run after pg_upgrade, and a script that finds pinned PostgreSQL versions in a repo: https://lnkd.in/gdF5WtWi Footage credit: PostgresConf South Africa 2018 opening, video by Malcolm McLean, CC BY 4.0 (https://lnkd.in/g_azHTFN). Stock: Mixkit. Dates: https://lnkd.in/gD9zZyCp. #PostgreSQL #PlatformEngineering #DevOps
- InstagramVideo
PostgreSQL 14 gets its final release on 12 November. After that, new bugs get fixed in newer versions only. Find every 14: the main cluster, CI containers, migration jobs, replicas, vendor appliances. Apply the final release, then plan the move to 18. Link in bio: http://safegua…
Read the full postHide the full post
PostgreSQL 14 gets its final release on 12 November. After that, new bugs get fixed in newer versions only. Find every 14: the main cluster, CI containers, migration jobs, replicas, vendor appliances. Apply the final release, then plan the move to 18. Link in bio: http://safeguard.sh/resources/blog Video: Malcolm McLean, PostgresConf South Africa 2018, CC BY 4.0. Stock: Mixkit. #postgresql #devops #platformengineering #database
 YouTubeVideo
PostgreSQL 14 gets its final release on 12 November 2026, per https://na2.hubs.ly/H08LcTv0. After that, new bugs found in 14 get fixed in newer versions only. Find every 14 you run: the main cluster, CI containers, migration jobs, replicas and vendor appliances. Apply the final…
Read the full postHide the full post
PostgreSQL 14 gets its final release on 12 November 2026, per https://na2.hubs.ly/H08LcTv0. After that, new bugs found in 14 get fixed in newer versions only. Find every 14 you run: the main cluster, CI containers, migration jobs, replicas and vendor appliances. Apply the final 14 release when it ships, then plan the move to 18. Footage: PostgresConf South Africa 2018 opening, video by Malcolm McLean, CC BY 4.0 (https://na2.hubs.ly/H08LcV70). Mixkit stock (free license). Local terminal recording and https://na2.hubs.ly/H08LcTw0 screen recording. Write-up: https://na2.hubs.ly/H08LcTx0 #PostgreSQL #DevOps #Shorts
- FacebookVideo
PostgreSQL 14 gets its final release on 12 November. After that, new bugs found in 14 get fixed in newer versions only. Find every 14 you run, including CI containers, migration jobs, replicas and vendor appliances, apply the final 14 release when it ships, then plan the move to…
Read the full postHide the full post
PostgreSQL 14 gets its final release on 12 November. After that, new bugs found in 14 get fixed in newer versions only. Find every 14 you run, including CI containers, migration jobs, replicas and vendor appliances, apply the final 14 release when it ships, then plan the move to 18. If you hold SBOMs, a search by package and version lists every project and image that carries it. Write-up: https://na2.hubs.ly/H08LcSW0 Video: Malcolm McLean, PostgresConf South Africa 2018, CC BY 4.0. Stock: Mixkit.
- XVideo
PostgreSQL 14 gets its final release on 12 November. After that, new bugs in 14 get fixed in newer versions only. Find every 14: CI images, migration jobs, replicas, vendor appliances. Then plan the move to 18. https://t.co/0WePzRMO1P https://t.co/KxyMmIrXbF
- TikTokVideo
PostgreSQL 14 final release is 12 November. After that, new bugs get fixed in newer versions only. Find every 14: CI containers, migration jobs, replicas, vendor appliances. Then plan the move to 18. Link in bio: https://na2.hubs.ly/H08LcTW0 #postgresql #devops #platformengineer…
Read the full postHide the full post
PostgreSQL 14 final release is 12 November. After that, new bugs get fixed in newer versions only. Find every 14: CI containers, migration jobs, replicas, vendor appliances. Then plan the move to 18. Link in bio: https://na2.hubs.ly/H08LcTW0 #postgresql #devops #platformengineering
 Instagram
Happy Kannada Rajyotsava! A lamp, jasmine and a warm wish for Karnataka Formation Day. #KannadaRajyotsava #KarnatakaFormationDay #Karnataka #Bengaluru #Kannada
Read the full postHide the full post
Happy Kannada Rajyotsava! A lamp, jasmine and a warm wish for Karnataka Formation Day. #KannadaRajyotsava #KarnatakaFormationDay #Karnataka #Bengaluru #Kannada
- Instagram
Happy Kannada Rajyotsava! A lamp, jasmine and a warm wish for Karnataka Formation Day. #KannadaRajyotsava #KarnatakaFormationDay #Karnataka #Bengaluru #Kannada
Read the full postHide the full post
Happy Kannada Rajyotsava! A lamp, jasmine and a warm wish for Karnataka Formation Day. #KannadaRajyotsava #KarnatakaFormationDay #Karnataka #Bengaluru #Kannada
 LinkedIn
Today Karnataka marks the day it came together as a state. Wishing everyone celebrating Kannada Rajyotsava a warm and happy 1 November, in Bengaluru, across Karnataka and wherever you are in the world. #KannadaRajyotsava #Karnataka #Bengaluru
Read the full postHide the full post
Today Karnataka marks the day it came together as a state. Wishing everyone celebrating Kannada Rajyotsava a warm and happy 1 November, in Bengaluru, across Karnataka and wherever you are in the world. #KannadaRajyotsava #Karnataka #Bengaluru
- LinkedIn
Today Karnataka marks the day it came together as a state. Wishing everyone celebrating Kannada Rajyotsava a warm and happy 1 November, in Bengaluru, across Karnataka and wherever you are in the world. #KannadaRajyotsava #Karnataka #Bengaluru
Read the full postHide the full post
Today Karnataka marks the day it came together as a state. Wishing everyone celebrating Kannada Rajyotsava a warm and happy 1 November, in Bengaluru, across Karnataka and wherever you are in the world. #KannadaRajyotsava #Karnataka #Bengaluru
- Facebook
Happy Kannada Rajyotsava, everyone! Warm wishes on Karnataka Formation Day to our friends and colleagues in Karnataka and around the world. Enjoy the day with family and friends.
- Facebook
Happy Kannada Rajyotsava, everyone! Warm wishes on Karnataka Formation Day to our friends and colleagues in Karnataka and around the world. Enjoy the day with family and friends.
 X
Happy Kannada Rajyotsava to everyone in Karnataka and beyond. Wishing you a bright Karnataka Formation Day. #KannadaRajyotsava #Karnataka https://t.co/EInZYMQann
- X
Happy Kannada Rajyotsava to everyone in Karnataka and beyond. Wishing you a bright Karnataka Formation Day. #KannadaRajyotsava #Karnataka https://t.co/VMRqGpY98F
- YouTubeVideo
Is there a document editing app on your file server that you installed once and forgot? CISA put one on its exploited list on 23 October, and the advisory says switching it off is not enough. This Patch Monday briefing covers four stories from 23 to 30 October 2026, each with wh…
Read the full postHide the full post
Is there a document editing app on your file server that you installed once and forgot? CISA put one on its exploited list on 23 October, and the advisory says switching it off is not enough. This Patch Monday briefing covers four stories from 23 to 30 October 2026, each with what happened, who is stuck with it right now, and one switch to flip on Monday morning: turn it off, narrow it, or set it on purpose. A vulnerability management and patch management story: CVE-2026-110447 in the Collabora Online Built-in CODE Server app for Nextcloud, on CISA's Known Exploited Vulnerabilities list since 23 October, and why Collabora's advisory says to update or remove the app. A credential theft story: Wiz Research's 25 October report on Gheist, a campaign that uses stolen GitHub tokens to plant workflows that print repository secrets, and how to narrow the tokens that can reach your repositories. A compliance story: the Department of Homeland Security notice of 30 October on an order to remove Acronis products from federal civilian systems, and the question it raises about every tool that runs with privileged access. And an AI agent security story: Anthropic's 26 October advisory for CVE-2026-88968, a race condition in the Claude Code Edit tool that could let a file be written outside the workspace on macOS. About eight minutes, for security engineers, AppSec leads, platform teams, compliance leads and CISOs. Topics: CVE-2026-110447, CVE-2026-88968, Collabora Online, Nextcloud, CISA KEV, Known Exploited Vulnerabilities, Gheist, GitHub tokens, GitHub Actions secrets, Wiz Research, Acronis, Federal Acquisition Supply Chain Security Act, Department of Homeland Security, Claude Code, Anthropic, vulnerability management, patch management, least privilege, software supply chain attack, compliance, AI agent security, security podcast, cybersecurity podcast, AppSec podcast, DevSecOps podcast, security engineer, CISO, Safeguard Chapters: 00:00 Cold open 00:15 Intro 00:41 Story 1: Collabora Built-in CODE Server for Nextcloud, CVE-2026-110447 on KEV 02:06 Story 2: Gheist and stolen GitHub tokens 03:40 Story 3: the DHS order on Acronis products 05:13 Story 4: the Claude Code Edit tool advisory, CVE-2026-88968 06:44 What to do Monday 07:12 Outro Links: Safeguard: https://safeguard.sh/?utm_source=podcast&utm_medium=video&utm_campaign=patch-monday&utm_content=ep02 Safeguard blog: https://safeguard.sh/blog?utm_source=podcast&utm_medium=video&utm_campaign=patch-monday&utm_content=ep02 Your copied workflow has no permissions block: what should you do: https://safeguard.sh/resources/blog/a-starter-workflow-has-no-permissions-block-add-one?utm_source=podcast&utm_medium=video&utm_campaign=patch-monday&utm_content=ep02 How do you apply least privilege to AI agents: https://safeguard.sh/resources/blog/ai-agents-and-least-privilege-checklist?utm_source=podcast&utm_medium=video&utm_campaign=patch-monday&utm_content=ep02 More episodes: https://safeguard.sh/podcast?utm_source=podcast&utm_medium=video&utm_campaign=patch-monday&utm_content=ep02 Listen on Spotify: https://open.spotify.com/show/1m9VhuuSqCzDKxH03E97fn?utm_source=podcast&utm_medium=video&utm_campaign=patch-monday&utm_content=ep02
- YouTubeVideo
A quick answer from Ask Safeguard, Ep 5: nobody has to read every fix, because only the exceptions need a person. Full episode: https://youtu.be/pkGLATpfbDQ #Shorts
Read the full postHide the full post
A quick answer from Ask Safeguard, Ep 5: nobody has to read every fix, because only the exceptions need a person. Full episode: https://youtu.be/pkGLATpfbDQ #Shorts
Follow Safeguard

Self-healing security runs on Safeguard.
Your first fix PR is minutes away.
No sales call required, even your agent can complete the purchase over MCP.