

Safeguard on social
Every post we have published on our social profiles, newest first, with the copy exactly as posted. Each card links to the original post.
Latest posts
RSS feed YouTubeVideo
No CVE means no patch, no advisory, and nothing for a scanner to match against. That’s a zero-day, and it’s already sitting in your dependencies. So we built Safeguard to find the flaw before the CVE exists, prove it’s actually reachable in your code so you’re not chasing noise,…
Read the full postHide the full post
No CVE means no patch, no advisory, and nothing for a scanner to match against. That’s a zero-day, and it’s already sitting in your dependencies. So we built Safeguard to find the flaw before the CVE exists, prove it’s actually reachable in your code so you’re not chasing noise, then hand your team the fix as a pull request they can review. 30-second version below. Want it pointed at your code? Book a demo: https://na2.hubs.ly/H080NK80 vulnerability that gets you won’t have a CVE yet.
 XVideo
The vulnerability that gets you won’t have a CVE yet. No CVE means no patch, no advisory, and nothing for a scanner to match against. That’s a zero-day, and it’s already sitting in your dependencies. So we built Safeguard to find the flaw before the CVE exists, prove it’s https:…
Read the full postHide the full post
The vulnerability that gets you won’t have a CVE yet. No CVE means no patch, no advisory, and nothing for a scanner to match against. That’s a zero-day, and it’s already sitting in your dependencies. So we built Safeguard to find the flaw before the CVE exists, prove it’s https://t.co/AW4IbRZ0Ss
- TikTokVideo
The vulnerability that gets you won’t have a CVE yet. No CVE means no patch, no advisory, and nothing for a scanner to match against. That’s a zero-day, and it’s already sitting in your dependencies. So we built Safeguard to find the flaw before the CVE exists, prove it’s actual…
Read the full postHide the full post
The vulnerability that gets you won’t have a CVE yet. No CVE means no patch, no advisory, and nothing for a scanner to match against. That’s a zero-day, and it’s already sitting in your dependencies. So we built Safeguard to find the flaw before the CVE exists, prove it’s actually reachable in your code so you’re not chasing noise, then hand your team the fix as a pull request they can review. 30-second version below. Want it pointed at your code? Book a demo: https://na2.hubs.ly/H080NK90
 LinkedInVideo
A CVE is a lagging indicator. By the time a flaw has a name, it’s public, and you’re patching in hindsight. Short video on the part that actually matters: finding the vulnerability before it’s named. Proving it’s reachable, so you fix what counts, not noise. Then shipping the fi…
Read the full postHide the full post
A CVE is a lagging indicator. By the time a flaw has a name, it’s public, and you’re patching in hindsight. Short video on the part that actually matters: finding the vulnerability before it’s named. Proving it’s reachable, so you fix what counts, not noise. Then shipping the fix as a pull request your team can review, not one more ticket. Same for the code your models write and the MCP servers they call. Want it pointed at your code? Book a demo.
 InstagramVideo
A CVE is a lagging indicator. By the time a flaw has a name, it’s public, and you’re patching in hindsight. Short video on the part that actually matters: finding the vulnerability before it’s named. Proving it’s reachable, so you fix what counts, not noise. Then shipping the fi…
Read the full postHide the full post
A CVE is a lagging indicator. By the time a flaw has a name, it’s public, and you’re patching in hindsight. Short video on the part that actually matters: finding the vulnerability before it’s named. Proving it’s reachable, so you fix what counts, not noise. Then shipping the fix as a pull request your team can review, not one more ticket. Same for the code your models write and the MCP servers they call. Want it pointed at your code? Book a demo.
 YouTubeVideo
A CVE is a lagging indicator. By the time a flaw has a name, it’s public, and you’re patching in hindsight. Short video on the part that actually matters: finding the vulnerability before it’s named. Proving it’s reachable, so you fix what counts, not noise. Then shipping the fi…
Read the full postHide the full post
A CVE is a lagging indicator. By the time a flaw has a name, it’s public, and you’re patching in hindsight. Short video on the part that actually matters: finding the vulnerability before it’s named. Proving it’s reachable, so you fix what counts, not noise. Then shipping the fix as a pull request your team can review, not one more ticket. Same for the code your models write and the MCP servers they call. Want it pointed at your code? Book a demo.
- FacebookVideo
A CVE is a lagging indicator. By the time a flaw has a name, it’s public, and you’re patching in hindsight. Short video on the part that actually matters: finding the vulnerability before it’s named. Proving it’s reachable, so you fix what counts, not noise. Then shipping the fi…
Read the full postHide the full post
A CVE is a lagging indicator. By the time a flaw has a name, it’s public, and you’re patching in hindsight. Short video on the part that actually matters: finding the vulnerability before it’s named. Proving it’s reachable, so you fix what counts, not noise. Then shipping the fix as a pull request your team can review, not one more ticket. Same for the code your models write and the MCP servers they call. Want it pointed at your code? Book a demo.
- TikTokVideo
A CVE is a lagging indicator. By the time a flaw has a name, it’s public, and you’re patching in hindsight. Short video on the part that actually matters: finding the vulnerability before it’s named. Proving it’s reachable, so you fix what counts, not noise. Then shipping the fi…
Read the full postHide the full post
A CVE is a lagging indicator. By the time a flaw has a name, it’s public, and you’re patching in hindsight. Short video on the part that actually matters: finding the vulnerability before it’s named. Proving it’s reachable, so you fix what counts, not noise. Then shipping the fix as a pull request your team can review, not one more ticket. Same for the code your models write and the MCP servers they call. Want it pointed at your code? Book a demo.
 LinkedIn
CAPTION: Found something before it even has a CVE number? It still gets a name, an advisory, and a suggested fix attached to it. Comment "ADVISORY" and we'll show you what one looks like.
Read the full postHide the full post
CAPTION: Found something before it even has a CVE number? It still gets a name, an advisory, and a suggested fix attached to it. Comment "ADVISORY" and we'll show you what one looks like.
- X
CAPTION: Found something before it even has a CVE number? It still gets a name, an advisory, and a suggested fix attached to it. Comment "ADVISORY" and we'll show you what one looks like. https://t.co/uLcJ0yeoTu
Read the full postHide the full post
CAPTION: Found something before it even has a CVE number? It still gets a name, an advisory, and a suggested fix attached to it. Comment "ADVISORY" and we'll show you what one looks like. https://t.co/uLcJ0yeoTu
- X
Finding it is only step one. After that, it gets checked, tagged, and disclosed the responsible way before it ever hits a public feed. Because discovering a vulnerability means nothing if the process after discovery puts more people at risk. Safeguard can help your team identify
Read the full postHide the full post
Finding it is only step one. After that, it gets checked, tagged, and disclosed the responsible way before it ever hits a public feed. Because discovering a vulnerability means nothing if the process after discovery puts more people at risk. Safeguard can help your team identify
- LinkedIn
Finding it is only step one. After that, it gets checked, tagged, and disclosed the responsible way before it ever hits a public feed. Because discovering a vulnerability means nothing if the process after discovery puts more people at risk. Safeguard can help your team identify…
Read the full postHide the full post
Finding it is only step one. After that, it gets checked, tagged, and disclosed the responsible way before it ever hits a public feed. Because discovering a vulnerability means nothing if the process after discovery puts more people at risk. Safeguard can help your team identify and manage security findings with a process built for responsible disclosure. #safeguard
- TikTokVideo
Safeguard is now a connector in Claude. You can ask what's open, which findings are actually reachable, and have it open a fix PR, all without leaving the chat. Takes about two minutes to connect. https://na2.hubs.ly/H07Tb8b0
 LinkedInVideo
A long list of findings can look impressive, but what really matters is knowing which ones are actually worth fixing. Safeguard challenges findings and proposed fixes before they move forward, helping cut through the noise and give your team more confidence in what needs attenti…
Read the full postHide the full post
A long list of findings can look impressive, but what really matters is knowing which ones are actually worth fixing. Safeguard challenges findings and proposed fixes before they move forward, helping cut through the noise and give your team more confidence in what needs attention. Less noise, more actionable work. #safeguard
 YouTubeVideo
A long list of findings can look impressive, but what really matters is knowing which ones are actually worth fixing. Safeguard challenges findings and proposed fixes before they move forward, helping cut through the noise and give your team more confidence in what needs attenti…
Read the full postHide the full post
A long list of findings can look impressive, but what really matters is knowing which ones are actually worth fixing. Safeguard challenges findings and proposed fixes before they move forward, helping cut through the noise and give your team more confidence in what needs attention. Less noise, more actionable work. #safeguard
- XVideo
A long list of findings can look impressive, but what really matters is knowing which ones are actually worth fixing. Safeguard challenges findings and proposed fixes before they move forward, helping cut through the noise and give your team more confidence in what needs https:/…
Read the full postHide the full post
A long list of findings can look impressive, but what really matters is knowing which ones are actually worth fixing. Safeguard challenges findings and proposed fixes before they move forward, helping cut through the noise and give your team more confidence in what needs https://t.co/EHV535RlVA
 LinkedInVideo
Some vulnerabilities don’t look dangerous at first. They can sit quietly in perfectly normal-looking code until the right conditions turn them into something exploitable. That’s why finding the unusual paths matters, not just checking for what we already know. #safeguard
 YouTubeVideo
Some vulnerabilities don’t look dangerous at first. They can sit quietly in perfectly normal-looking code until the right conditions turn them into something exploitable. That’s why finding the unusual paths matters, not just checking for what we already know. #safeguard
- XVideo
Some vulnerabilities don’t look dangerous at first. They can sit quietly in perfectly normal-looking code until the right conditions turn them into something exploitable. That’s why finding the unusual paths matters, not just checking for what we already know. #safeguard https:/…
Read the full postHide the full post
Some vulnerabilities don’t look dangerous at first. They can sit quietly in perfectly normal-looking code until the right conditions turn them into something exploitable. That’s why finding the unusual paths matters, not just checking for what we already know. #safeguard https://t.co/PASPxRxwIN
 InstagramVideo
A long list of findings can look impressive, but what really matters is knowing which ones are actually worth fixing. Safeguard challenges findings and proposed fixes before they move forward, helping cut through the noise and give your team more confidence in what needs attenti…
Read the full postHide the full post
A long list of findings can look impressive, but what really matters is knowing which ones are actually worth fixing. Safeguard challenges findings and proposed fixes before they move forward, helping cut through the noise and give your team more confidence in what needs attention. Less noise, more actionable work. #safeguard
 InstagramVideo
Some vulnerabilities don’t look dangerous at first. They can sit quietly in perfectly normal-looking code until the right conditions turn them into something exploitable. That’s why finding the unusual paths matters, not just checking for what we already know. #safeguard
 Instagram
Some vulnerabilities don’t look dangerous at first. They can sit quietly in perfectly normal-looking code until the right conditions turn them into something exploitable. That’s why finding the unusual paths matters, not just checking for what we already know. #safeguard
 Instagram
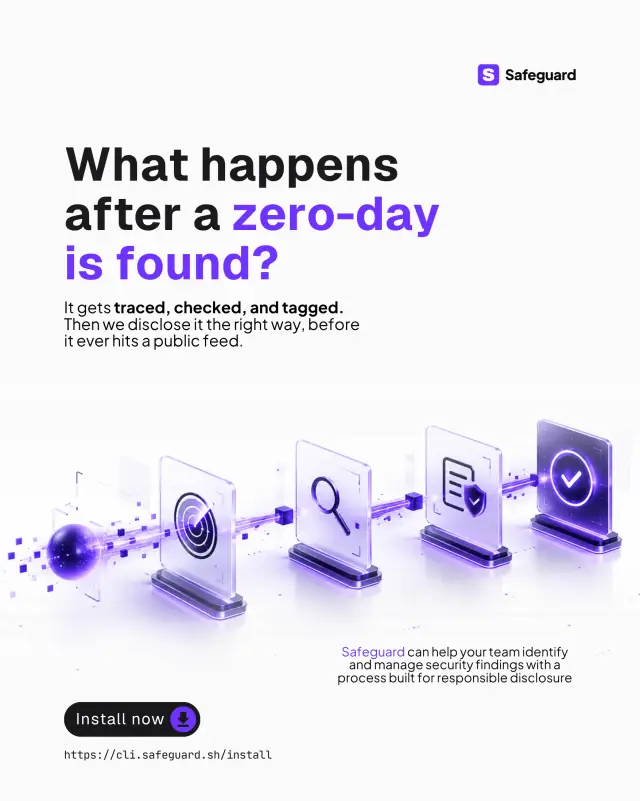
Finding it is only step one. After that, it gets checked, tagged, and disclosed the responsible way before it ever hits a public feed. Because discovering a vulnerability means nothing if the process after discovery puts more people at risk. Safeguard can help your team identify…
Read the full postHide the full post
Finding it is only step one. After that, it gets checked, tagged, and disclosed the responsible way before it ever hits a public feed. Because discovering a vulnerability means nothing if the process after discovery puts more people at risk. Safeguard can help your team identify and manage security findings with a process built for responsible disclosure. #safeguard
- Instagram
Found something before it even has a CVE number? It still gets a name, an advisory, and a suggested fix attached to it. Comment "ADVISORY" and we'll show you what one looks like.
Read the full postHide the full post
Found something before it even has a CVE number? It still gets a name, an advisory, and a suggested fix attached to it. Comment "ADVISORY" and we'll show you what one looks like.
Follow Safeguard

Self-healing security runs on Safeguard.
Your first fix PR is minutes away.
No sales call required, even your agent can complete the purchase over MCP.