

Safeguard on social
Every post we have published on our social profiles, newest first, with the copy exactly as posted. Each card links to the original post.
Posts on TikTok
RSS feed TikTokVideo
Your CVE dashboard is all green. That’s the part that should worry you. Closing every known CVE proves you handled the vulnerabilities that already have a name. A zero-day is the one that doesn’t, so it never shows up on the board you hand the auditor. When a customer’s security…
Read the full postHide the full post
Your CVE dashboard is all green. That’s the part that should worry you. Closing every known CVE proves you handled the vulnerabilities that already have a name. A zero-day is the one that doesn’t, so it never shows up on the board you hand the auditor. When a customer’s security review or a regulator asks how you handle the unknown, “we scan for CVEs” isn’t an answer. Safeguard finds zero-days before they’re public, proves which ones are actually reachable, and gives you both the fix and the evidence. Coverage complete, before the CVE exists. 30-second version below. See where you’re exposed. Book a demo.
 TikTokVideo
Your team ships more code every week. Your scanner only knows last year’s CVEs. A scanner matches known vulnerabilities. But the one that actually hurts, the flaw an AI just wrote into your codebase, doesn’t have a CVE yet. No advisory, no signature, nothing to match. So we buil…
Read the full postHide the full post
Your team ships more code every week. Your scanner only knows last year’s CVEs. A scanner matches known vulnerabilities. But the one that actually hurts, the flaw an AI just wrote into your codebase, doesn’t have a CVE yet. No advisory, no signature, nothing to match. So we built Safeguard to find the zero-day in your own code and dependencies, prove it’s actually reachable so you’re not chasing noise, then open the tested fix as a pull request your team can review. Review it, merge it, keep shipping. 30-second version below. Want it pointed at your repo? Book a demo.
 TikTokVideo
That notification badge you’ve been ignoring for three weeks is doing more work than you think. The scariest bugs in your software aren’t the ones with a CVE and a patch waiting. They’re the ones nobody’s named yet, quietly worth more on the open market than most engineers make…
Read the full postHide the full post
That notification badge you’ve been ignoring for three weeks is doing more work than you think. The scariest bugs in your software aren’t the ones with a CVE and a patch waiting. They’re the ones nobody’s named yet, quietly worth more on the open market than most engineers make in a decade, sitting in code someone shipped and forgot.
 TikTokVideo
The vulnerability that gets you won’t have a CVE yet. No CVE means no patch, no advisory, and nothing for a scanner to match against. That’s a zero-day, and it’s already sitting in your dependencies. So we built Safeguard to find the flaw before the CVE exists, prove it’s actual…
Read the full postHide the full post
The vulnerability that gets you won’t have a CVE yet. No CVE means no patch, no advisory, and nothing for a scanner to match against. That’s a zero-day, and it’s already sitting in your dependencies. So we built Safeguard to find the flaw before the CVE exists, prove it’s actually reachable in your code so you’re not chasing noise, then hand your team the fix as a pull request they can review. 30-second version below. Want it pointed at your code? Book a demo: https://na2.hubs.ly/H080NK90
 TikTokVideo
A CVE is a lagging indicator. By the time a flaw has a name, it’s public, and you’re patching in hindsight. Short video on the part that actually matters: finding the vulnerability before it’s named. Proving it’s reachable, so you fix what counts, not noise. Then shipping the fi…
Read the full postHide the full post
A CVE is a lagging indicator. By the time a flaw has a name, it’s public, and you’re patching in hindsight. Short video on the part that actually matters: finding the vulnerability before it’s named. Proving it’s reachable, so you fix what counts, not noise. Then shipping the fix as a pull request your team can review, not one more ticket. Same for the code your models write and the MCP servers they call. Want it pointed at your code? Book a demo.
- TikTokVideo
Safeguard is now a connector in Claude. You can ask what's open, which findings are actually reachable, and have it open a fix PR, all without leaving the chat. Takes about two minutes to connect. https://na2.hubs.ly/H07Tb8b0
 TikTokVideo
Some vulnerabilities don’t look dangerous at first. They can sit quietly in perfectly normal-looking code until the right conditions turn them into something exploitable. That’s why finding the unusual paths matters, not just checking for what we already know. #safeguard
 TikTokVideo
A long list of findings can look impressive, but what really matters is knowing which ones are actually worth fixing. Safeguard challenges findings and proposed fixes before they move forward, helping cut through the noise and give your team more confidence in what needs attenti…
Read the full postHide the full post
A long list of findings can look impressive, but what really matters is knowing which ones are actually worth fixing. Safeguard challenges findings and proposed fixes before they move forward, helping cut through the noise and give your team more confidence in what needs attention. Less noise, more actionable work. #safeguard
 TikTokVideo
Your vulnerability database can tell you what’s already known—but what about the things nobody has found yet? Zero-days don’t come with a CVE or advisory, so Safeguard looks beyond known vulnerabilities to help uncover weaknesses hiding in your code. Because not every threat is…
Read the full postHide the full post
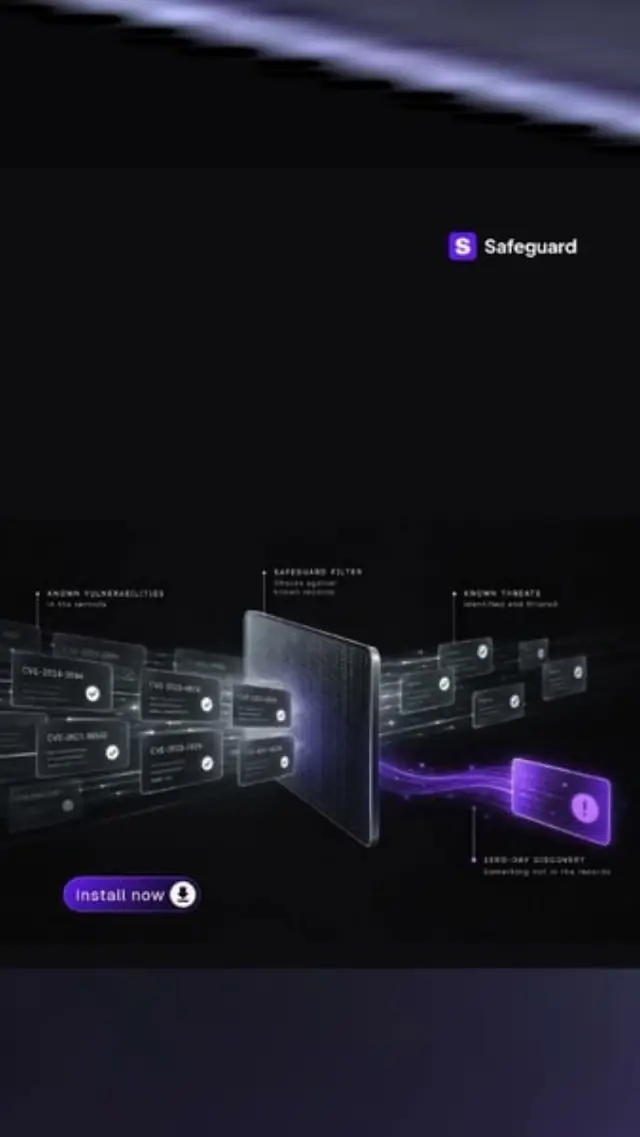
Your vulnerability database can tell you what’s already known—but what about the things nobody has found yet? Zero-days don’t come with a CVE or advisory, so Safeguard looks beyond known vulnerabilities to help uncover weaknesses hiding in your code. Because not every threat is already in the database. #safeguard
 TikTokVideo
Vulnerability feeds tell you what’s already known. Zero-day discovery starts with what isn’t. Safeguard Research looks beyond published threats—investigating package behavior, maintainers, tampering, and provenance. Because real security starts before the alert.
 TikTokVideo
A Zero Day nobody’s found yet is a gift — to whoever finds it first. Left hidden, it’s an open door. Found and fixed first, it’s the reason your software holds. Zero Days aren’t only threats. Found first, they’re your best defense. Safeguard & self-heal your software supply chai…
Read the full postHide the full post
A Zero Day nobody’s found yet is a gift — to whoever finds it first. Left hidden, it’s an open door. Found and fixed first, it’s the reason your software holds. Zero Days aren’t only threats. Found first, they’re your best defense. Safeguard & self-heal your software supply chain → https://na2.hubs.ly/H07H2MC0 #cybersecurity #appsec #zeroday #devsecops #softwaresecurity #vulnerabilitymanagement #infosec #supplychainsecurity
 TikTokVideo
Not every team can run AI on their code, and we get that. So Zero-Day Discovery works two ways. One powered by AI, one that isn't. Same protection, either way. Comment "MODES" and we'll walk you through both.
 TikTokVideo
Ask your scanner one question: where does my code go when you run it? If the answer bugs you, that’s why Safeguard CLI exists. Book a demo on your own repo: https://na2.hubs.ly/H07CL_10 #AppSec #DevSecOps
Follow Safeguard

Self-healing security runs on Safeguard.
Your first fix PR is minutes away.
No sales call required, even your agent can complete the purchase over MCP.