

Safeguard on social
Every post we have published on our social profiles, newest first, with the copy exactly as posted. Each card links to the original post.
Posts on Facebook
RSS feed Facebook
SOC 2 Type II for a startup under 10 people: the checklist. Cover written policies, access control and reviews, change management with code review, vendor review, vulnerability management, evidence collection, security training and incident response. Safeguard's SOC 2 Type II au…
Read the full postHide the full post
SOC 2 Type II for a startup under 10 people: the checklist. Cover written policies, access control and reviews, change management with code review, vendor review, vulnerability management, evidence collection, security training and incident response. Safeguard's SOC 2 Type II automation also covers app and supply chain security. See https://na2.hubs.ly/H08HZmS0 for current plans. Audit fees are separate. See the plan: https://na2.hubs.ly/H08HZmT0
 Facebook
Jit orchestrates open source scanners through security plans as code. Safeguard runs its own engines and opens fix pull requests. We are a competitor, so we say where Jit is strong and when to pick it. Compared as of 28 October 2026. The full comparison: https://na2.hubs.ly/H08K…
Read the full postHide the full post
Jit orchestrates open source scanners through security plans as code. Safeguard runs its own engines and opens fix pull requests. We are a competitor, so we say where Jit is strong and when to pick it. Compared as of 28 October 2026. The full comparison: https://na2.hubs.ly/H08K-zF0
 FacebookVideo
US clocks go back this Sunday, 1 November, at 2:00 local time. The rule reaches your servers, phones and code through the IANA time zone database, and one host often holds several copies of that data (OS, Java, Node, Python, Go). Before the weekend: run zdump on a few zones, kee…
Read the full postHide the full post
US clocks go back this Sunday, 1 November, at 2:00 local time. The rule reaches your servers, phones and code through the IANA time zone database, and one host often holds several copies of that data (OS, Java, Node, Python, Go). Before the weekend: run zdump on a few zones, keep logs in UTC, review jobs scheduled in local time, and list the tzdata version in every image. An SBOM can show you which images carry an older copy. Walkthrough with commands: https://na2.hubs.ly/H08JFD10
 Facebook
106 malicious npm and PyPI packages were published between 26 and 28 October 2026, per GitHub's advisory database. 96 on npm, 10 on PyPI. The post lists what they did, gives you a script to check your lockfiles, and shows how an install-time block in front of npm and pip, like S…
Read the full postHide the full post
106 malicious npm and PyPI packages were published between 26 and 28 October 2026, per GitHub's advisory database. 96 on npm, 10 on PyPI. The post lists what they did, gives you a script to check your lockfiles, and shows how an install-time block in front of npm and pip, like Safeguard's Package Firewall, refuses the next batch before it runs. https://na2.hubs.ly/H08K-7q0
 Facebook
CISA added CVE-2026-110447 to its Known Exploited Vulnerabilities catalog on 23 October: an unauthenticated command injection in the Nextcloud "Collabora Online - Built-in CODE Server" app (richdocumentscode). Attackers have used it to drop web shells since at least 10 September…
Read the full postHide the full post
CISA added CVE-2026-110447 to its Known Exploited Vulnerabilities catalog on 23 October: an unauthenticated command injection in the Nextcloud "Collabora Online - Built-in CODE Server" app (richdocumentscode). Attackers have used it to drop web shells since at least 10 September. Fixed in richdocumentscode 26.4.303; 26.4.402 is the current release. Standalone Collabora Online servers are not affected, only the built-in app. If you run Nextcloud, check the installed apps, update, then look for web shells. How the bug works and how to check a server: https://na2.hubs.ly/H08CFpC0
 FacebookVideo
Before you add a dependency, look it up. Gold Open Source (https://na2.hubs.ly/H08CDG-0) is free and needs no login. A package page shows the version Gold indexed, the known vulnerability count, a verification panel and an OpenSSF Scorecard grade. Then check the version against…
Read the full postHide the full post
Before you add a dependency, look it up. Gold Open Source (https://na2.hubs.ly/H08CDG-0) is free and needs no login. A package page shows the version Gold indexed, the known vulnerability count, a verification panel and an OpenSSF Scorecard grade. Then check the version against your pull request, read the license, and look at the install scripts yourself. https://na2.hubs.ly/H08CDH00
 Facebook
A CISO needs one page to watch every week and one short pack to send the board every month. In Safeguard that page is the Program Overview dashboard. The two tiles that matter most: KEV listed findings in production (the docs say it should read zero) and time to remediate. Sched…
Read the full postHide the full post
A CISO needs one page to watch every week and one short pack to send the board every month. In Safeguard that page is the Program Overview dashboard. The two tiles that matter most: KEV listed findings in production (the docs say it should read zero) and time to remediate. Scheduled reports send a daily digest, a Monday executive summary and a monthly board pack as PDF plus JSON. What to watch weekly and what to show the board: https://na2.hubs.ly/H08JgQ10
 Facebook
Revocation alone does not fix a CA compromise. A stolen CA key can sign its own "good" answers, so the plan is to replace certificates and remove trust, not just revoke. Apps that ship their own CA bundle or pin a key ignore operating system trust store changes. Safeguard's SBOM…
Read the full postHide the full post
Revocation alone does not fix a CA compromise. A stolen CA key can sign its own "good" answers, so the plan is to replace certificates and remove trust, not just revoke. Apps that ship their own CA bundle or pin a key ignore operating system trust store changes. Safeguard's SBOMs help you find them. Inventory, revoke, reissue runbook: https://na2.hubs.ly/H08J5c30
 FacebookVideo
Your coding agents already emit telemetry. Send it to Safeguard and see what they actually did, as detections your SOC can act on. OpenAI Codex and Claude Code export OpenTelemetry. Safeguard turns it into sessions, tool decisions and results, model calls, tokens and cost, and A…
Read the full postHide the full post
Your coding agents already emit telemetry. Send it to Safeguard and see what they actually did, as detections your SOC can act on. OpenAI Codex and Claude Code export OpenTelemetry. Safeguard turns it into sessions, tool decisions and results, model calls, tokens and cost, and AI detections in Detection & Response. The ingest token is send-only, prompt content is off by default and credentials are redacted on arrival. Setup guide: https://na2.hubs.ly/H08FpzX0
 FacebookVideo
The software you buy ships open source too. Atlassian's October security bulletin lists 75 unique CVEs, all in bundled third-party libraries such as Tomcat, Netty and Bouncy Castle. Several were public in August, and the fixed builds are dated 20 October. Know what is inside eac…
Read the full postHide the full post
The software you buy ships open source too. Atlassian's October security bulletin lists 75 unique CVEs, all in bundled third-party libraries such as Tomcat, Netty and Bouncy Castle. Several were public in August, and the fixed builds are dated 20 October. Know what is inside each vendor product and which version you run. If a supplier gives you an SBOM, Safeguard can import it and match its components to known vulnerabilities. Details: https://na2.hubs.ly/H08JhBV0
 Facebook
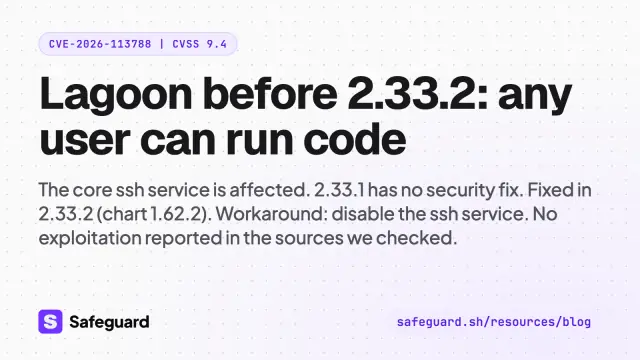
CVE-2026-113788 lets any Lagoon user run code through the core ssh service. Every release before 2.33.2 is affected, and 2.33.1 has no security fix. The fix is Lagoon 2.33.2 (lagoon-core chart 1.62.2, 25 August 2026). No exploitation reported in the sources we checked. Safeguard…
Read the full postHide the full post
CVE-2026-113788 lets any Lagoon user run code through the core ssh service. Every release before 2.33.2 is affected, and 2.33.1 has no security fix. The fix is Lagoon 2.33.2 (lagoon-core chart 1.62.2, 25 August 2026). No exploitation reported in the sources we checked. Safeguard's SBOM scan flags vulnerable components in your estate. What to patch and check: https://na2.hubs.ly/H08J3Jb0
 Facebook
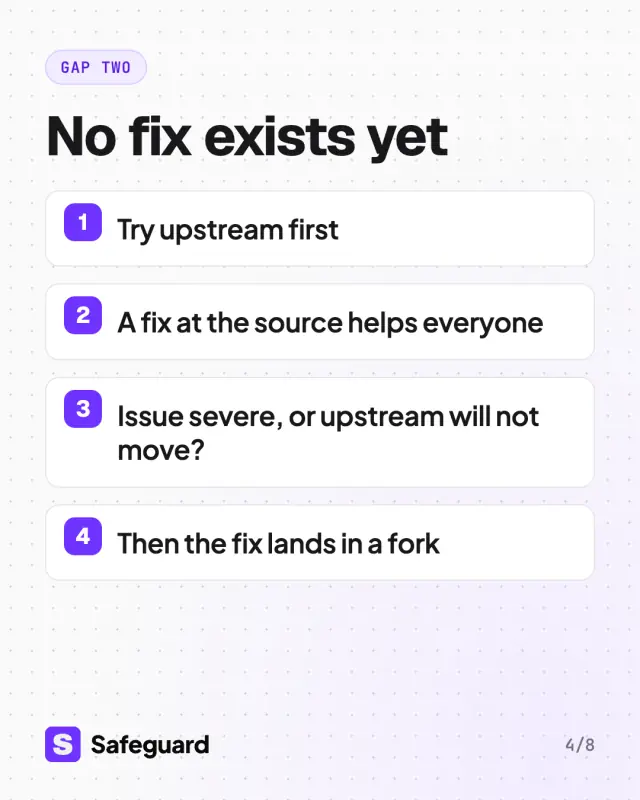
The maintainer has not shipped a fix for the dependency you use. There are two gaps: a fix that exists but has not reached your builds, and no fix at all. For the first, an SBOM per build turns an advisory into a lookup, and tested remediation pull requests move you to the fixed…
Read the full postHide the full post
The maintainer has not shipped a fix for the dependency you use. There are two gaps: a fix that exists but has not reached your builds, and no fix at all. For the first, an SBOM per build turns an advisory into a lookup, and tested remediation pull requests move you to the fixed version (it ships switched off, so you set how much runs on its own). For the second, we first work to get the fix accepted upstream. If the issue is severe or upstream will not move, we fork, fix it there and publish a hardened Gold build. One honest limit: vendor appliances, hosted services and operating systems you do not build still need the fix from the vendor. Full brief: https://na2.hubs.ly/H08CD_t0
 FacebookVideo
ASUS fixed three High rated router flaws on 23 October: an authentication bypass (CVE-2026-93489) and two root command injections (CVE-2026-75775, CVE-2026-75779). The CVE records list a firmware series and no fixed version, and none is in CISA's KEV catalog as of 26 October. Ho…
Read the full postHide the full post
ASUS fixed three High rated router flaws on 23 October: an authentication bypass (CVE-2026-93489) and two root command injections (CVE-2026-75775, CVE-2026-75779). The CVE records list a firmware series and no fixed version, and none is in CISA's KEV catalog as of 26 October. How many routers do you own? The branch office, the home office, the one in the closet. Check the firmware on every one. What to check and how: https://na2.hubs.ly/H08Jhj80
 Facebook
Two separate exposures at Amadeus, the airline booking technology provider, surfaced in October 2026. Korean Air and Asiana say booking data leaked through misuse of a login for an Amadeus system account. Separately, heise online found passenger records behind an unauthenticated…
Read the full postHide the full post
Two separate exposures at Amadeus, the airline booking technology provider, surfaced in October 2026. Korean Air and Asiana say booking data leaked through misuse of a login for an Amadeus system account. Separately, heise online found passenger records behind an unauthenticated Spring Boot heap dump, including Lufthansa and Condor flights; Amadeus says it is fixed. No source links the two. If you buy from a booking or SaaS vendor, ask which of their system accounts can read your data, how credentials rotate, and how many hours until they tell you after unauthorized access. https://na2.hubs.ly/H08CDSQ0
 FacebookVideo
The Fix Window, Ep 5 is live: Three days: how fast to patch a bug that is already being used. How CISA's BOD 26-04 turned one patch deadline into four facts, and how a private team can borrow the idea: a fast lane for exploited flaws on exposed assets, a CI gate on known exploit…
Read the full postHide the full post
The Fix Window, Ep 5 is live: Three days: how fast to patch a bug that is already being used. How CISA's BOD 26-04 turned one patch deadline into four facts, and how a private team can borrow the idea: a fast lane for exploited flaws on exposed assets, a CI gate on known exploited CVEs, and honest risk acceptance. Mira, Cal and Theo are AI voices; the script is written by the Safeguard team. Listen: https://na2.hubs.ly/H08Jbb_0
 FacebookVideo
One mistyped package name, stopped before it lands. Safeguard's Package Firewall sits between your developers, your CI and the public registries for npm and pip, and blocks malicious, typosquatted and dependency confusion packages at install time. Start in audit mode, then enfor…
Read the full postHide the full post
One mistyped package name, stopped before it lands. Safeguard's Package Firewall sits between your developers, your CI and the public registries for npm and pip, and blocks malicious, typosquatted and dependency confusion packages at install time. Start in audit mode, then enforce. Walkthrough and CLI commands: https://na2.hubs.ly/H08Cv4m0
 Facebook
Running Adobe Commerce or Magento Open Source? Apply the fix for CVE-2026-48356 (unrestricted file upload, CVSS 9.3) from Adobe bulletin APSB26-73, then check pub/media/custom_options/ for uploaded files, review admin users and rotate credentials if you find anything. Patching d…
Read the full postHide the full post
Running Adobe Commerce or Magento Open Source? Apply the fix for CVE-2026-48356 (unrestricted file upload, CVSS 9.3) from Adobe bulletin APSB26-73, then check pub/media/custom_options/ for uploaded files, review admin users and rotate credentials if you find anything. Patching does not remove what an attacker already left behind. Safeguard inventories each store from its lock file and puts KEV listed findings first. The full checklist: https://na2.hubs.ly/H08J3KV0
 FacebookVideo
Whether your team standardised on Anthropic's Claude or OpenAI's ChatGPT, the risk is depending on any single provider. In Safeguard you pick the model per task: one OpenAI-compatible endpoint, provider/model ids, and you change the id, not the integration. Routes for Anthropic,…
Read the full postHide the full post
Whether your team standardised on Anthropic's Claude or OpenAI's ChatGPT, the risk is depending on any single provider. In Safeguard you pick the model per task: one OpenAI-compatible endpoint, provider/model ids, and you change the id, not the integration. Routes for Anthropic, OpenAI, Google, xAI, Mistral, Cohere and open-weight hosts. Bring your own model for Safeguard's AI features such as search and chat, or run Zero AI with no LLM anywhere. Your model, your call (1/3): https://na2.hubs.ly/H08FyrB0 Claude is a product of Anthropic. ChatGPT is a product of OpenAI.
 FacebookVideo
OpenSSL 3.4 lost upstream support on 22 October, and 3.6 follows this Sunday, 1 November. The copies to worry about are the ones you build, bundle or brew yourself, plus base images nobody rebuilt. Find every copy and its version, then move to a supported line (3.5 LTS, 4.0 or 4…
Read the full postHide the full post
OpenSSL 3.4 lost upstream support on 22 October, and 3.6 follows this Sunday, 1 November. The copies to worry about are the ones you build, bundle or brew yourself, plus base images nobody rebuilt. Find every copy and its version, then move to a supported line (3.5 LTS, 4.0 or 4.1). Guide and checker script: https://na2.hubs.ly/H08Cy6-0
 Facebook
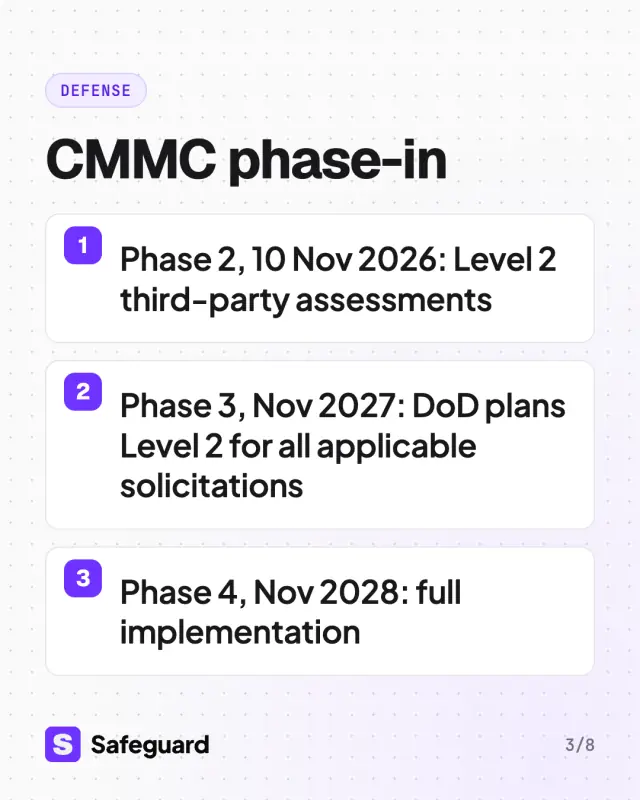
Three US software security dates are coming up: CMMC Phase 2 on 10 November 2026, CISA BOD 26-04 remediation timelines for federal agencies on 7 December 2026, and Colorado's AI developer duties on 1 January 2027. Our guide covers each rule from its primary text and ends with a…
Read the full postHide the full post
Three US software security dates are coming up: CMMC Phase 2 on 10 November 2026, CISA BOD 26-04 remediation timelines for federal agencies on 7 December 2026, and Colorado's AI developer duties on 1 January 2027. Our guide covers each rule from its primary text and ends with a 90-day plan in three phases. Swipe through the dates and the plan. https://na2.hubs.ly/H08CDRZ0
 FacebookVideo
One vendor breach, two universities. NEC says a company it outsources to was attacked in late September and valid accounts were misused against its customers. Osaka University says a third party downloaded files shared on cloud storage outside the contract: 77,851 people, duplic…
Read the full postHide the full post
One vendor breach, two universities. NEC says a company it outsources to was attacked in late September and valid accounts were misused against its customers. Osaka University says a third party downloaded files shared on cloud storage outside the contract: 77,851 people, duplicates removed. Your risk includes your vendors' vendors. Can you name every company that touches your systems or your data? Timeline from the official notices and questions to ask your vendors: https://na2.hubs.ly/H08C19j0
 Facebook
Anthropic filed a Form S-1 on 26 October. For teams that already run on Claude, the risk factors are a vendor security review answered in public: model weights named as a state-sponsored target, "known limitations or gaps" in defenses at times, agent hijack paths, and dated outa…
Read the full postHide the full post
Anthropic filed a Form S-1 on 26 October. For teams that already run on Claude, the risk factors are a vendor security review answered in public: model weights named as a state-sponsored target, "known limitations or gaps" in defenses at times, agent hijack paths, and dated outages and export restrictions. Your side of the work: an AI-BOM, an MCP connector inventory and least-privilege agent permissions. Not investment advice.
 Facebook
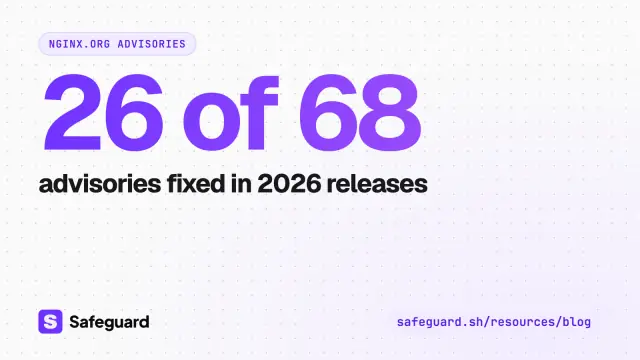
26 of the 68 advisories on the nginx project's security advisories page were fixed in releases shipped in 2026. Stable is now 1.30.6 and mainline 1.31.8 (26 October 2026), and the 1.28 branch ended with 1.28.3 on 24 March. If a distribution, container image or ingress controller…
Read the full postHide the full post
26 of the 68 advisories on the nginx project's security advisories page were fixed in releases shipped in 2026. Stable is now 1.30.6 and mainline 1.31.8 (26 October 2026), and the 1.28 branch ended with 1.28.3 on 24 March. If a distribution, container image or ingress controller ships your nginx, that packager sets your patch timing. An SBOM that records the build in every image and host turns an advisory into a lookup. Release history, advisory process and upgrade checklist: https://na2.hubs.ly/H08CDrJ0
- Facebook
Taking a security platform to twenty teams is an identity problem before it is a scanning problem. Our new post covers SSO (SAML 2.0, OIDC), SCIM, roles, the org hierarchy, staged gates and the audit log, with a phased rollout plan.
Follow Safeguard

Self-healing security runs on Safeguard.
Your first fix PR is minutes away.
No sales call required, even your agent can complete the purchase over MCP.